

AIDebug
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
ai-securitybinary-analysisdebuggers+7
13
anpa1200/aidebugEvidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
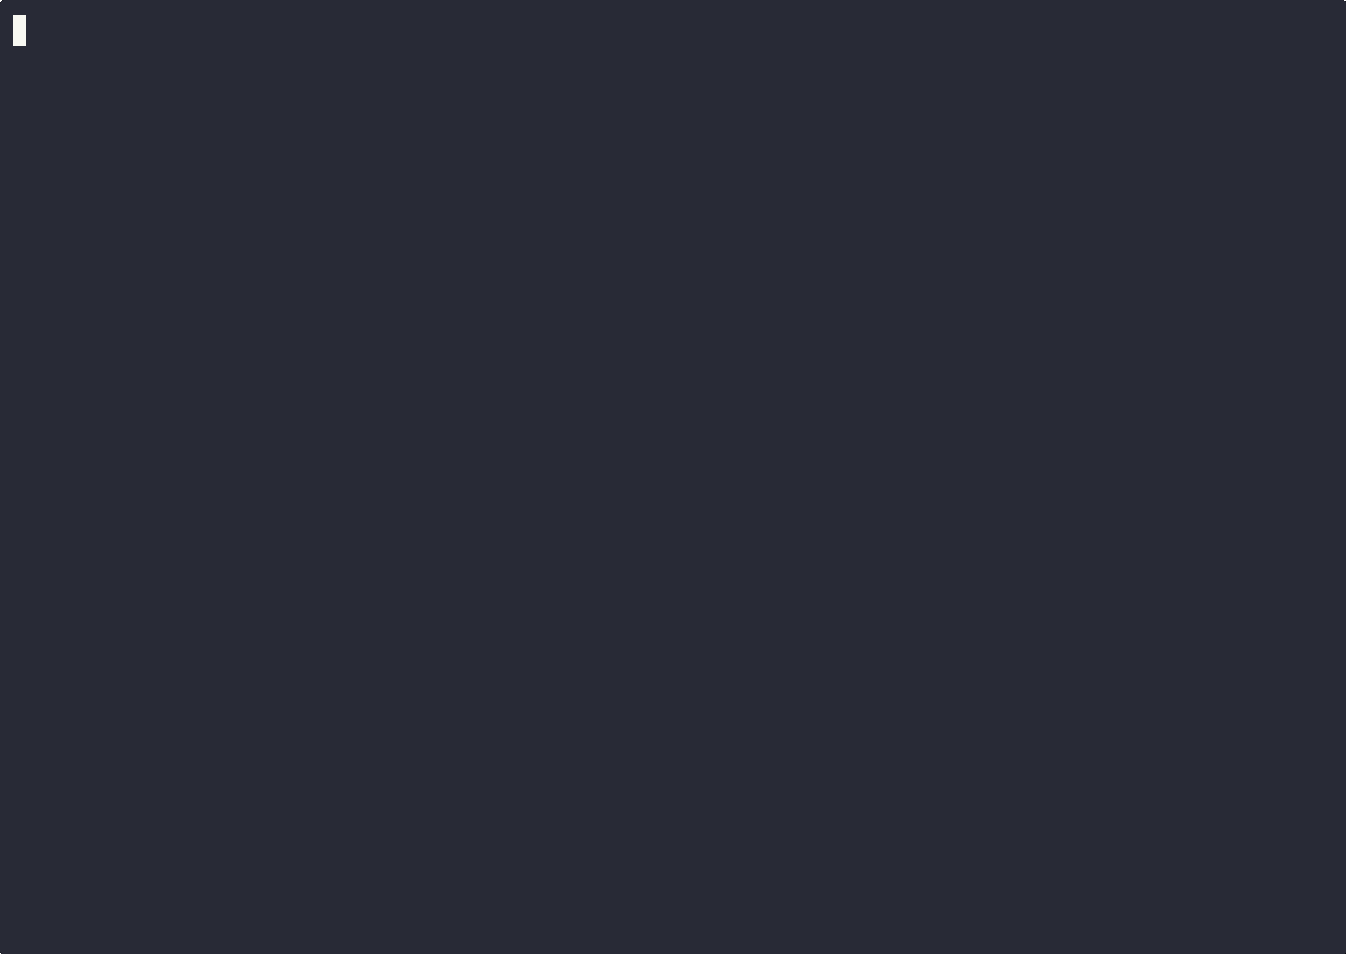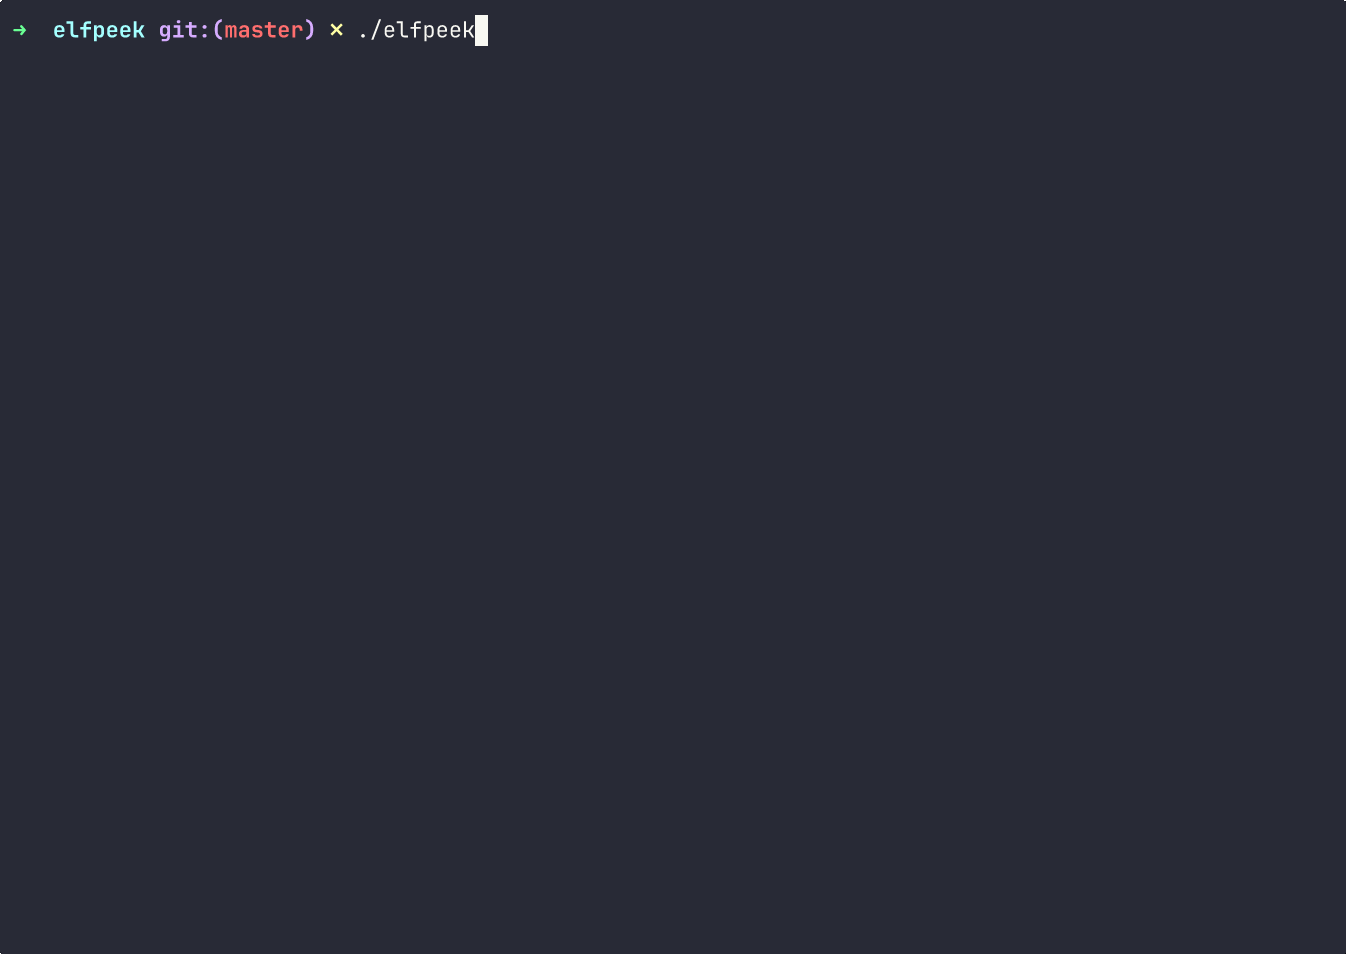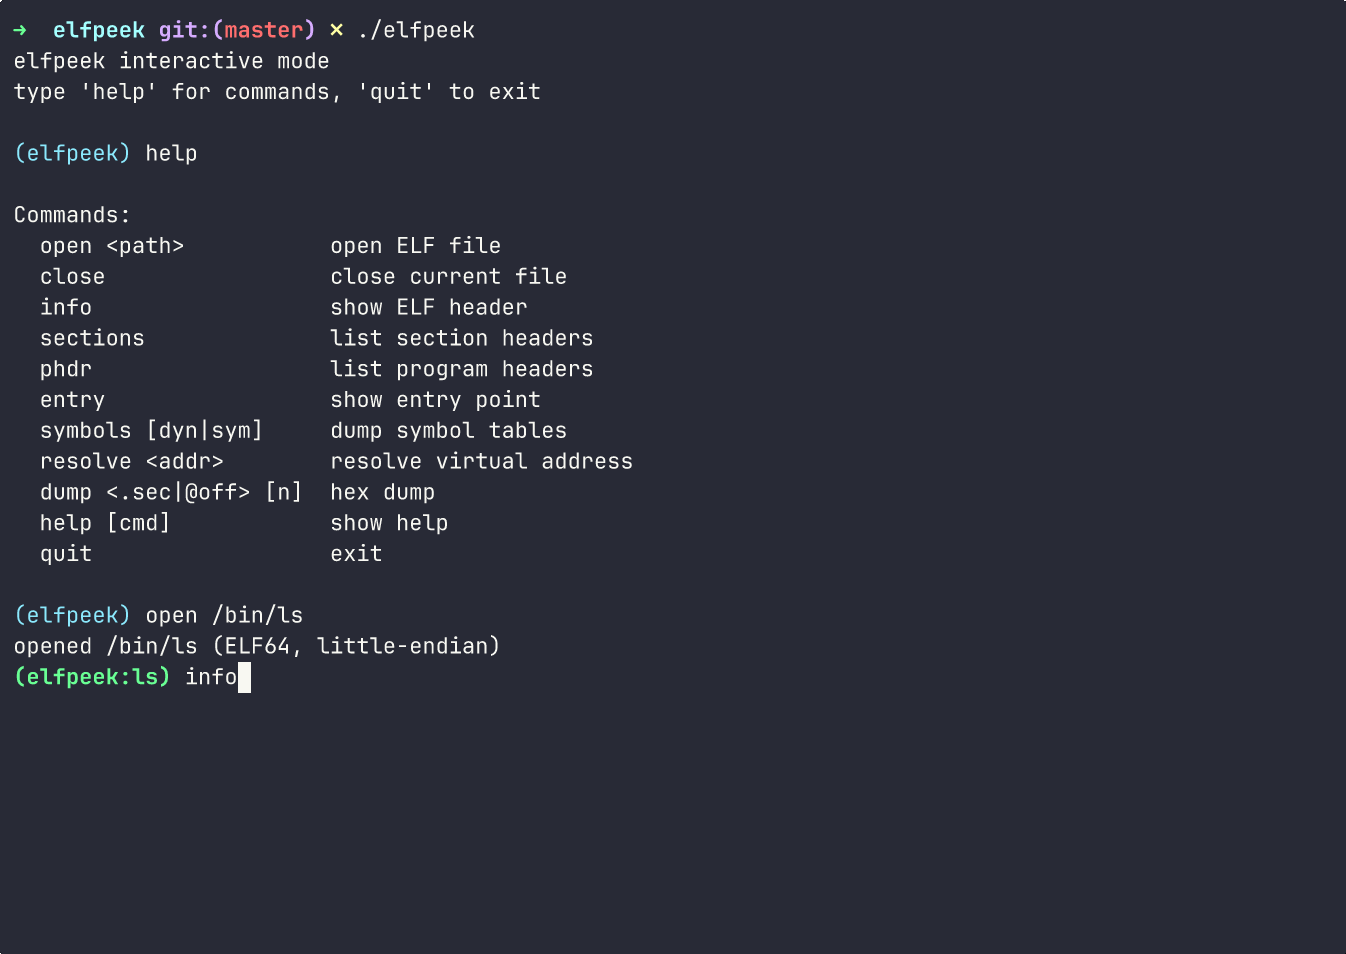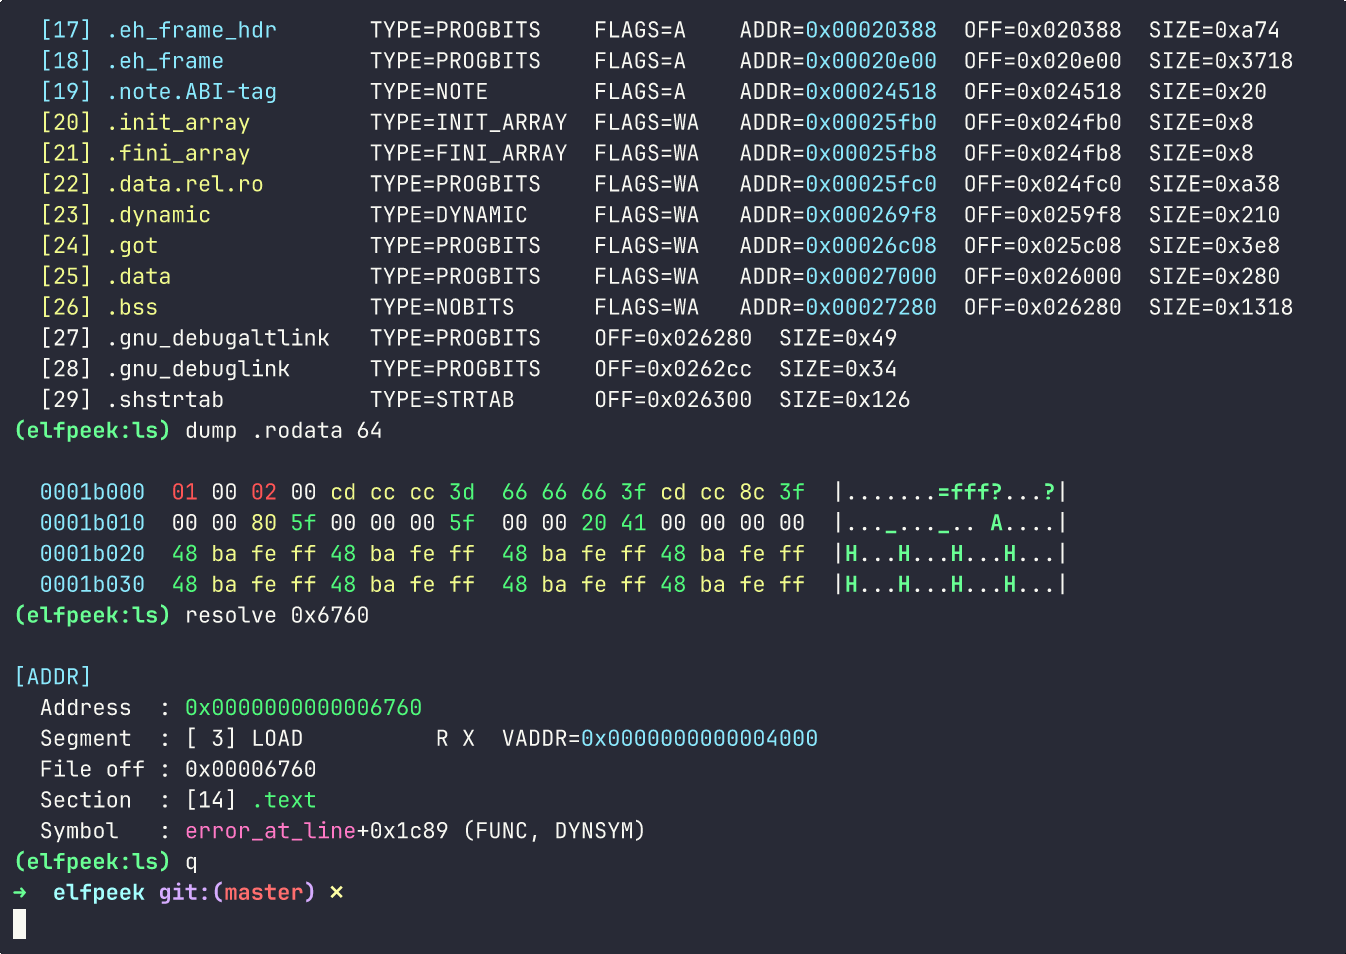 oblivionsage/elfpeek
Minimal ELF inspector written in C for quick binary layout inspection
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 ehabhussein/ollydbg-binary-execution-visualizer
reverse engineering, visual binary analysis
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 spiralbl0ck/blacklotus-analysis-stage2-bootkit-rootkit-stage
Z2A-BlackLotus Challenge stage 2 bootkit-rootkit analysis
 velteyn/unbattletech
BattleTech: The Crescent Hawk's Inception reverse engeneering
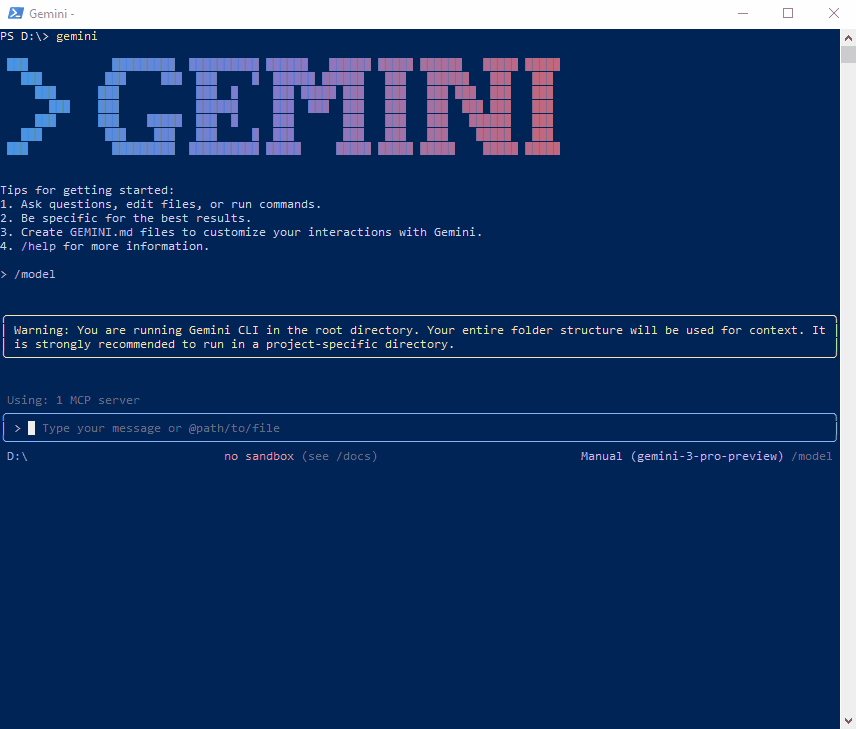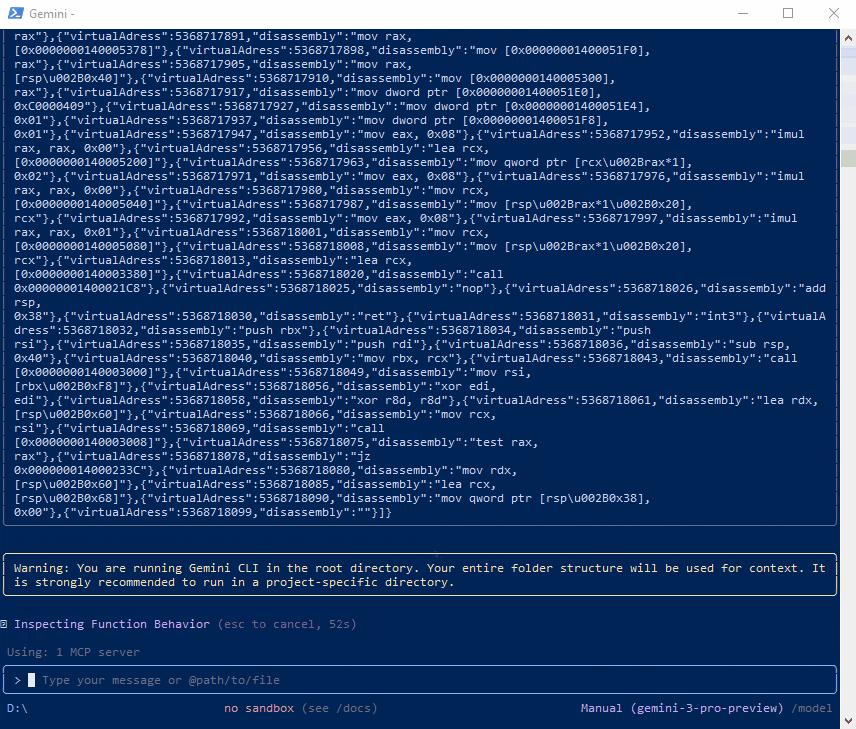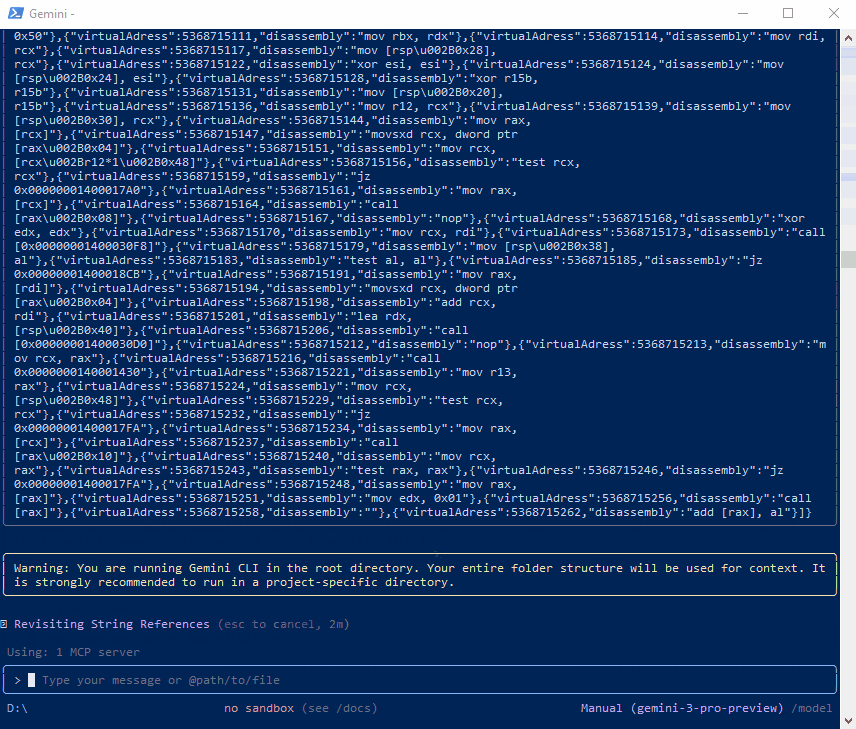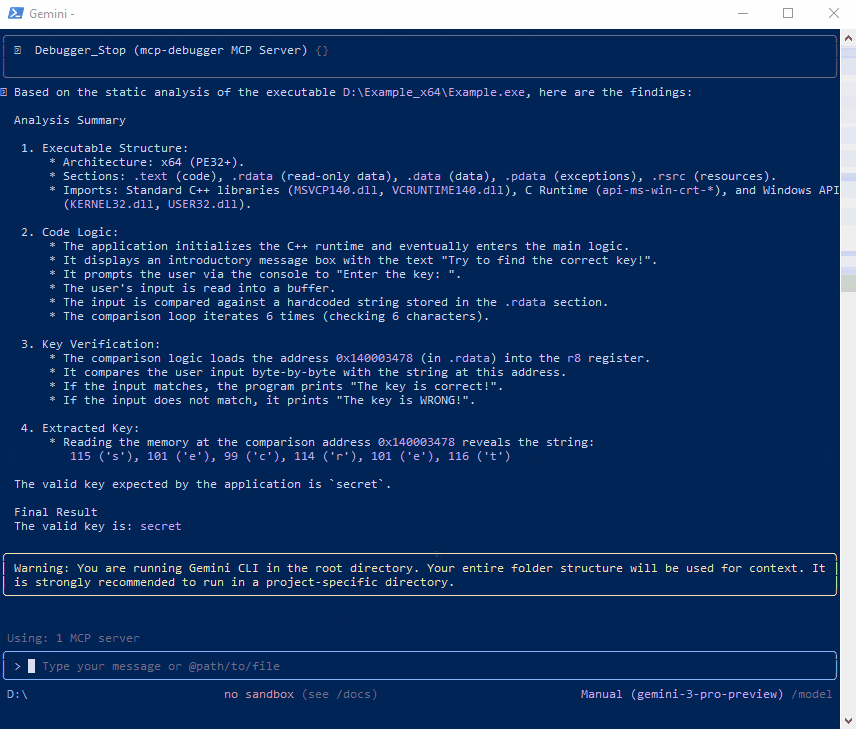 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
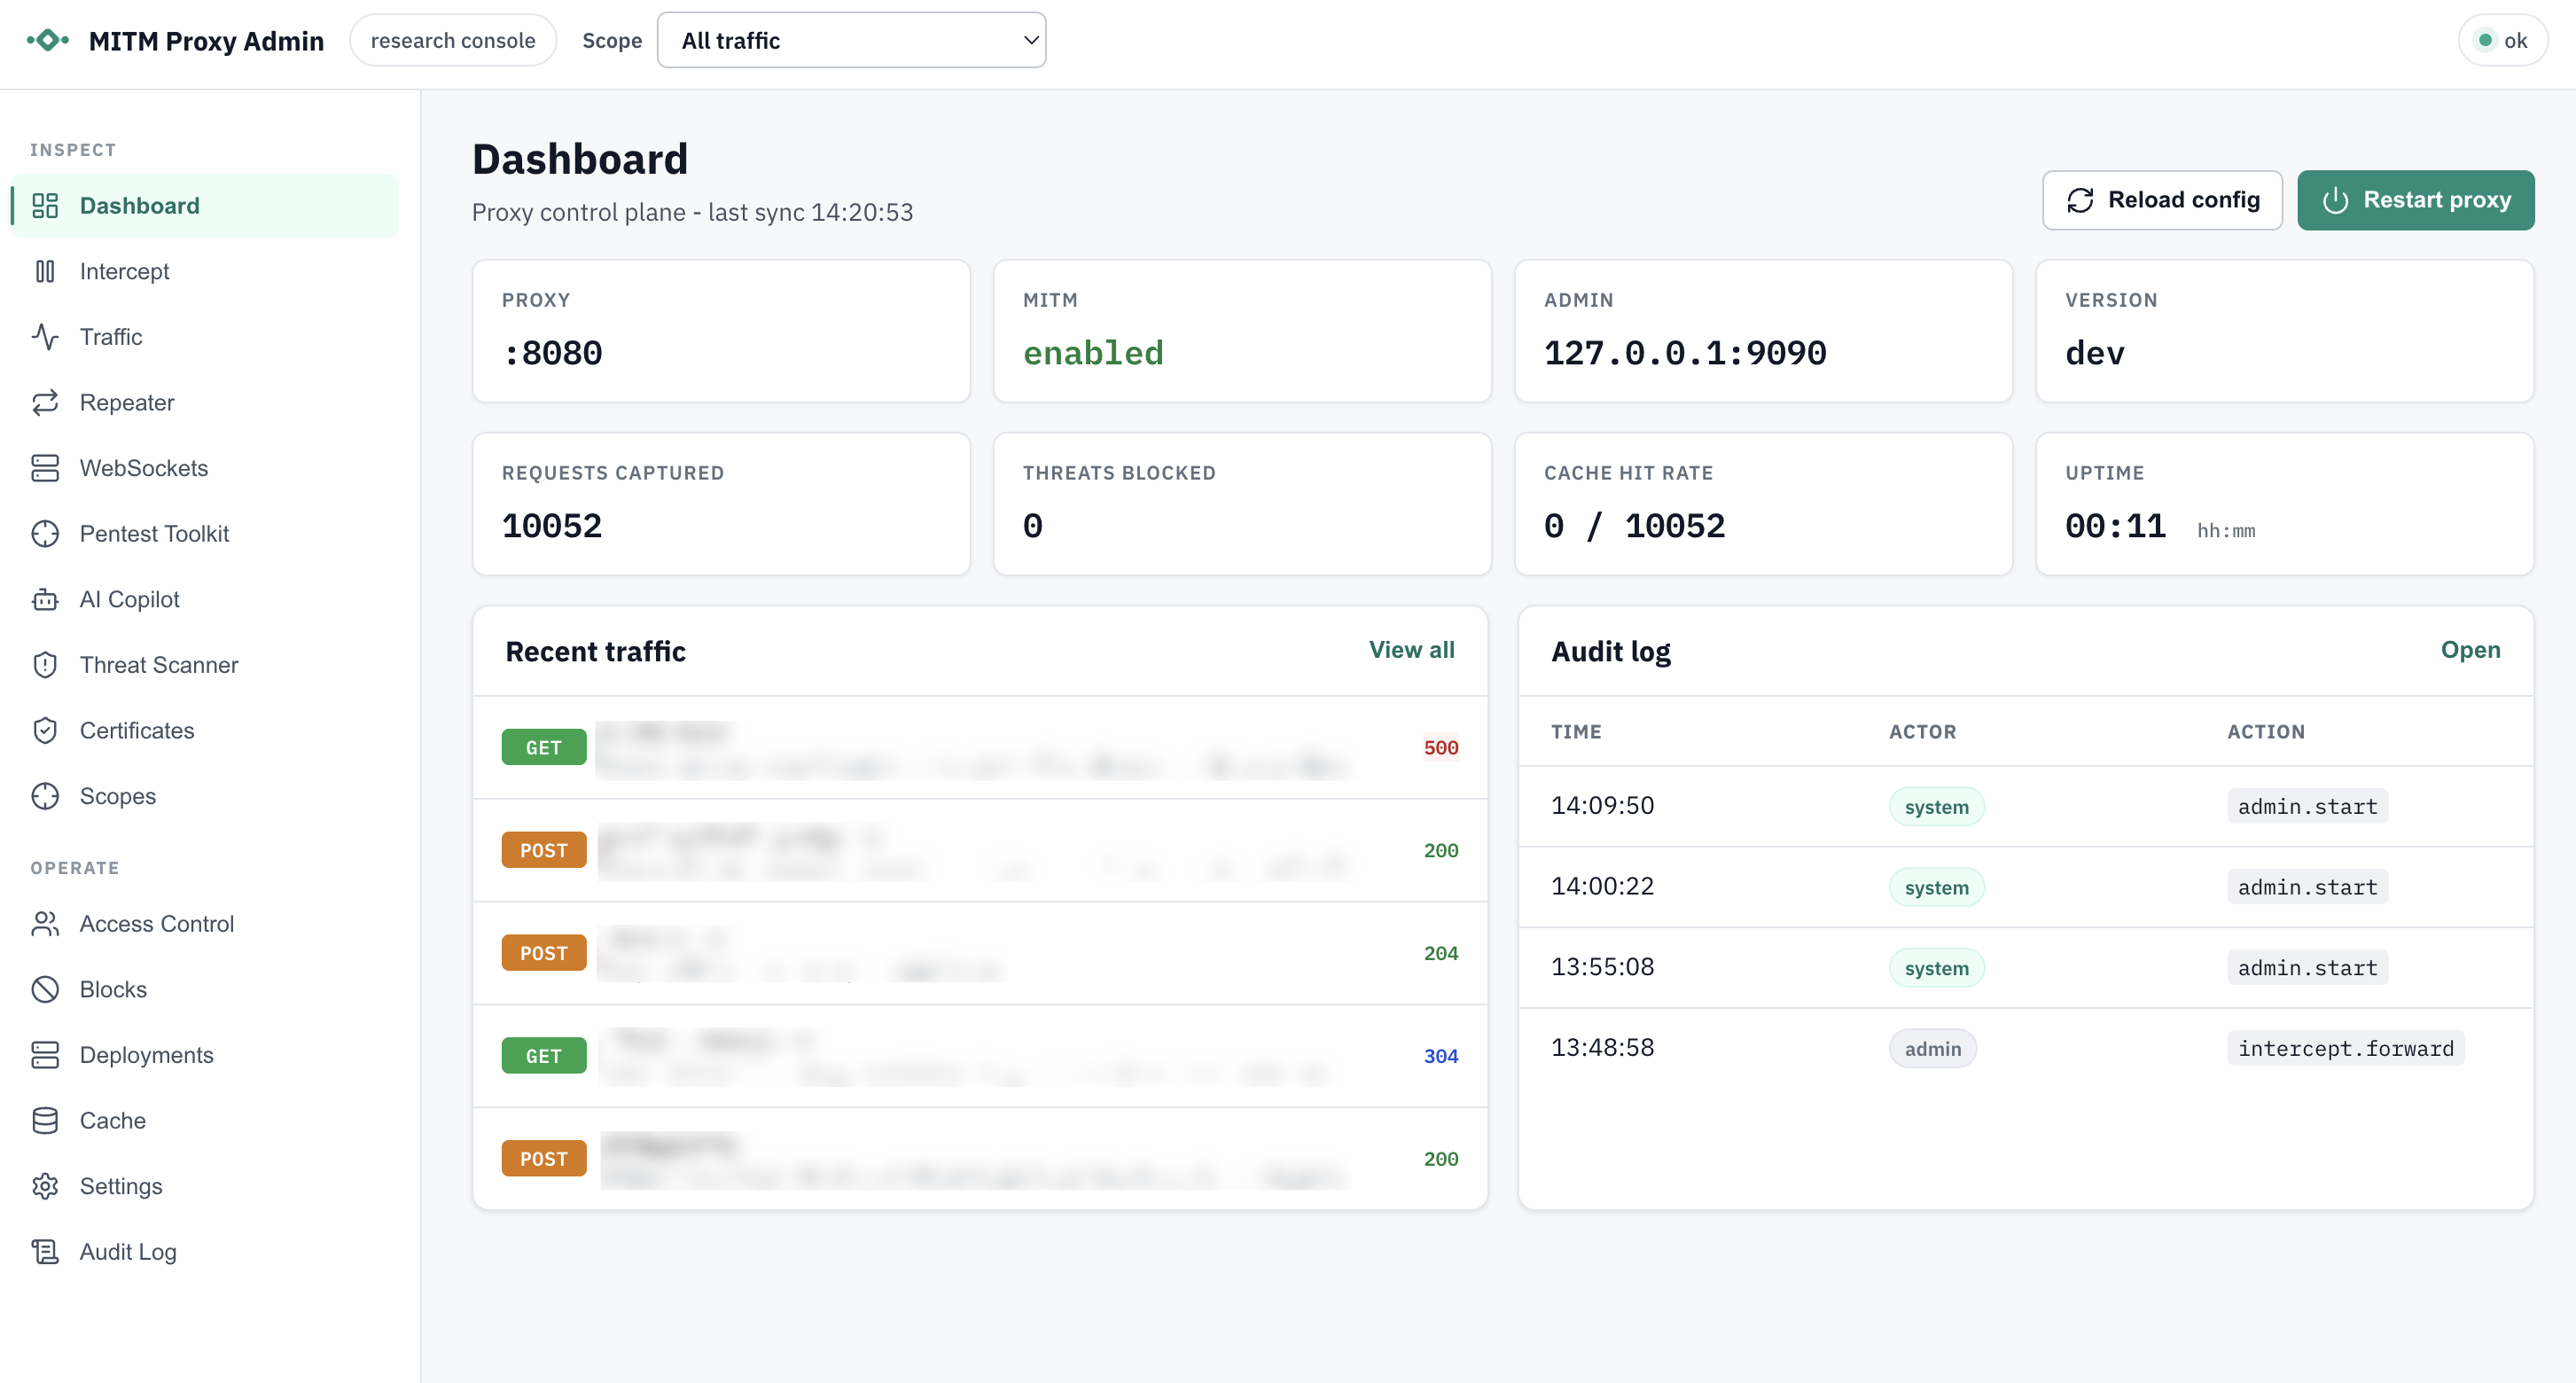 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)