

dynamorio
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
dynamorio/dynamorioRuntime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
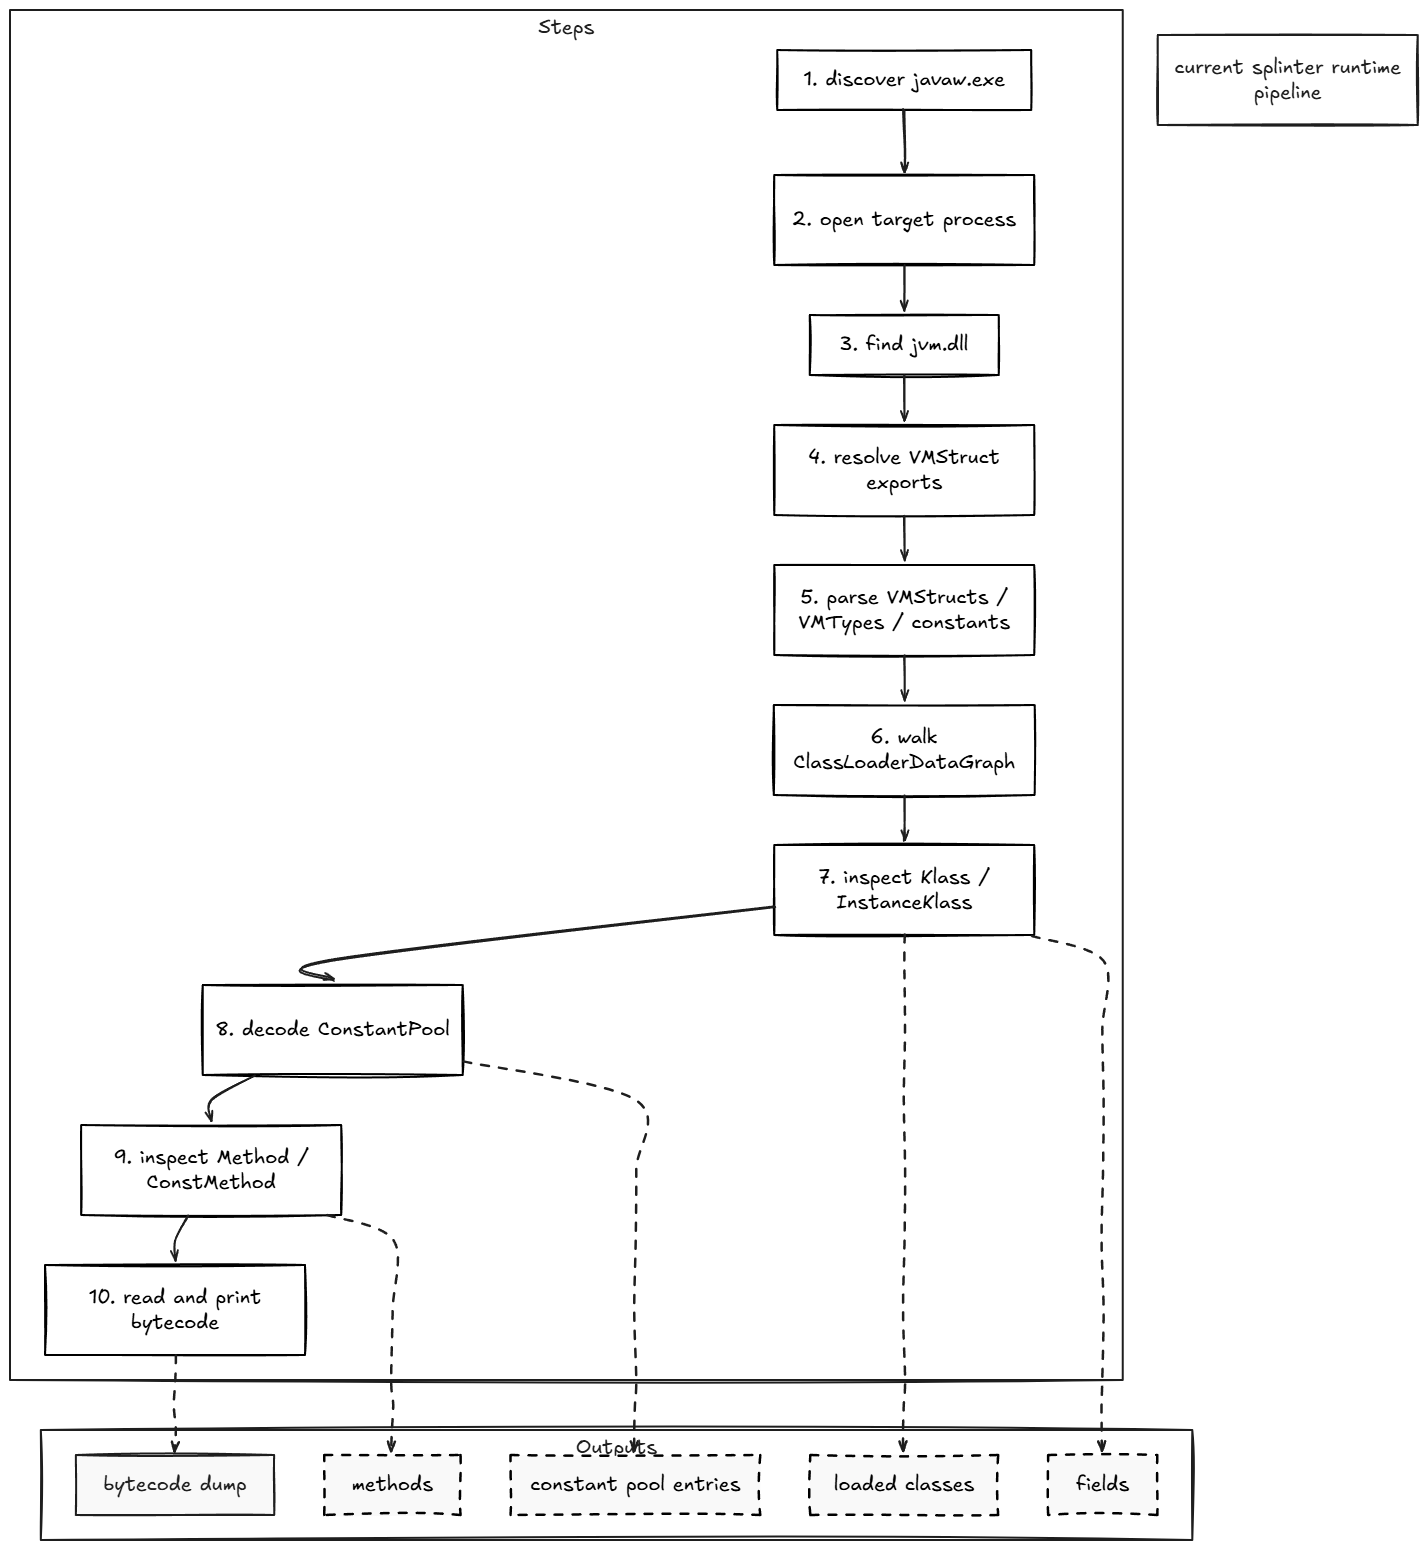 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
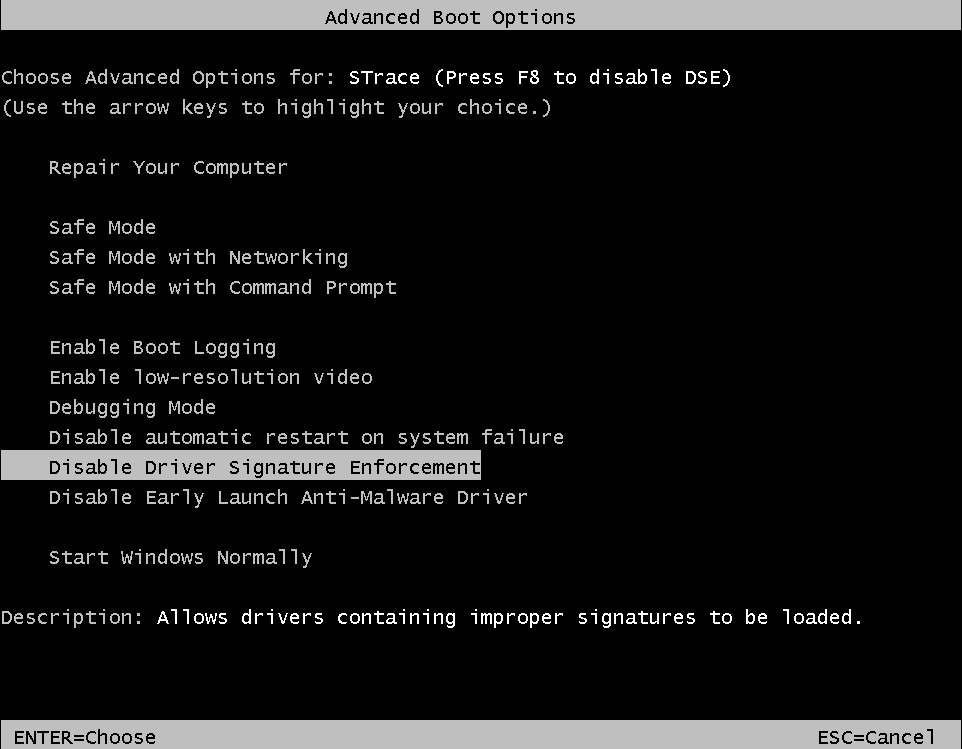 mandiant/strace
A DTrace on Windows Reimplementation