

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.1k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
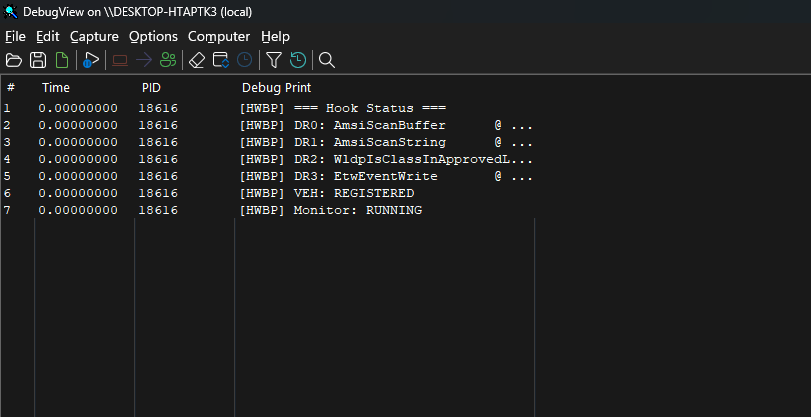 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
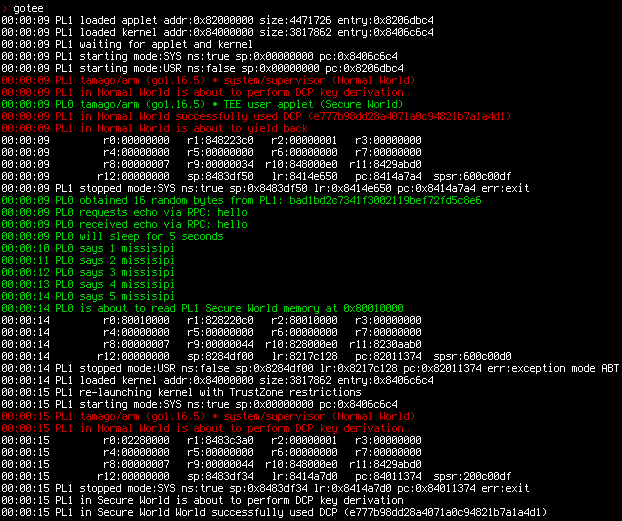 usbarmory/gotee-example
GoTEE - example application
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
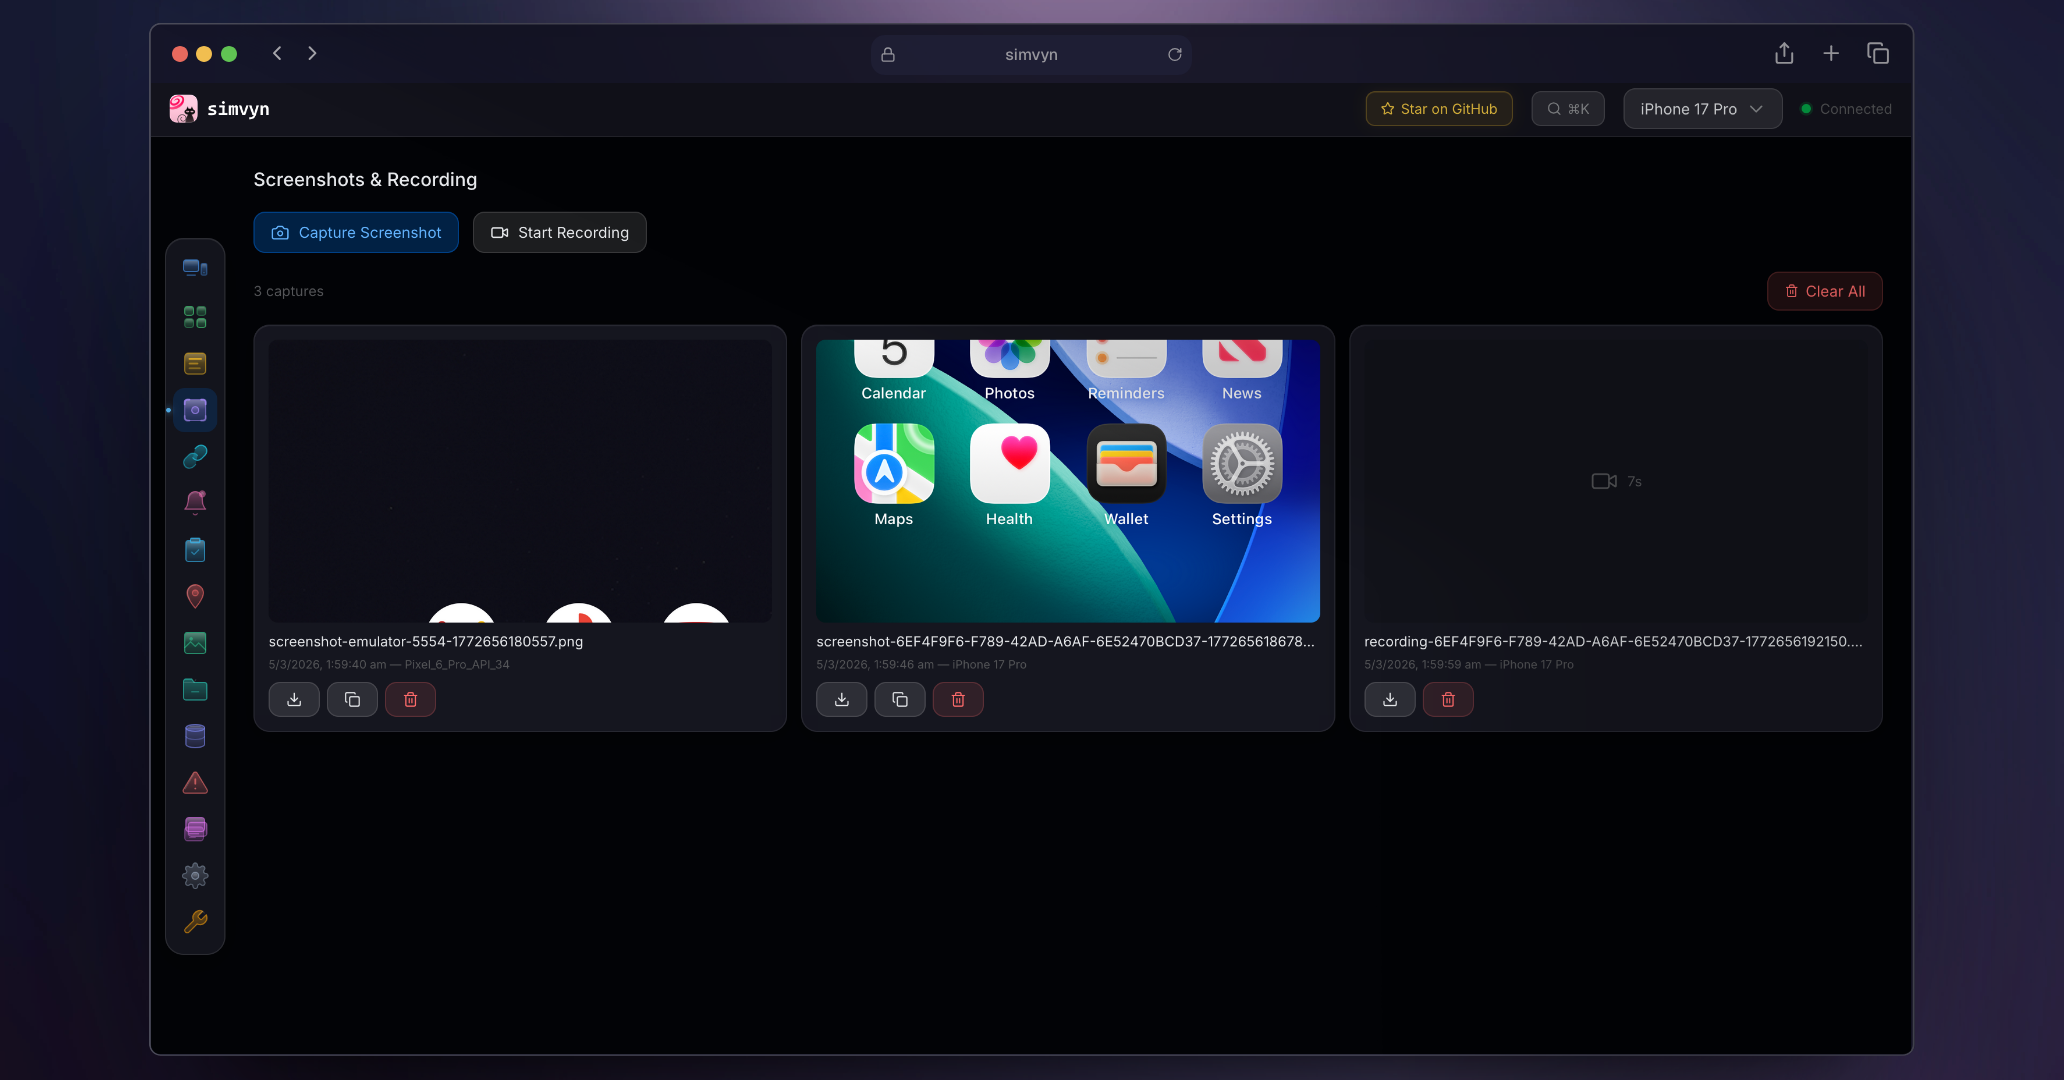 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 baiyibai/pico-usb-wifi
Firmware for Raspberry Pi Pico W that creates a driverless USB Wi-Fi adapter with transparent layer-2 bridging, WPA2/WPA3 authentication, and…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 zodiacon/alltools
All reasonably stable tools
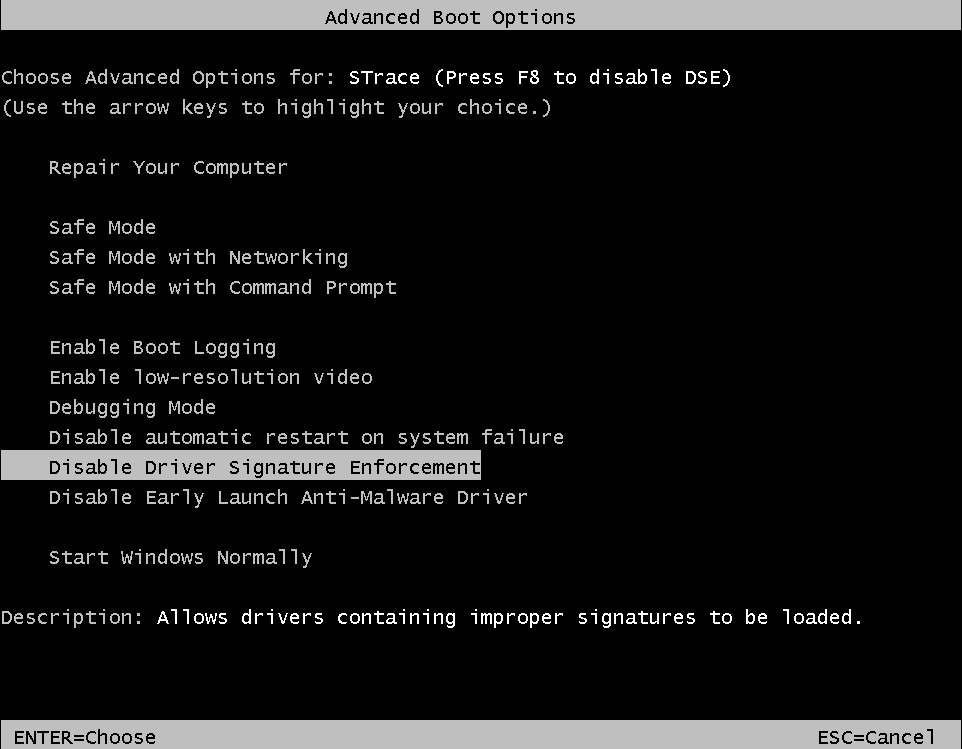 mandiant/strace
A DTrace on Windows Reimplementation
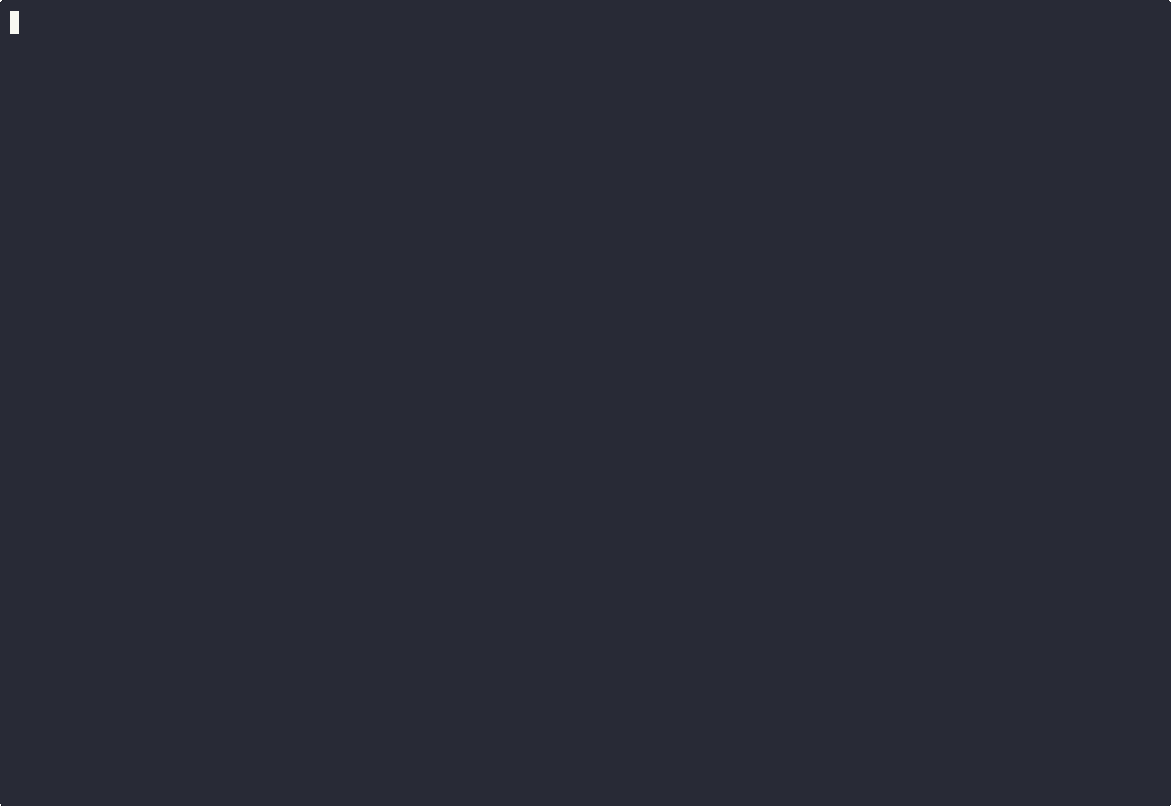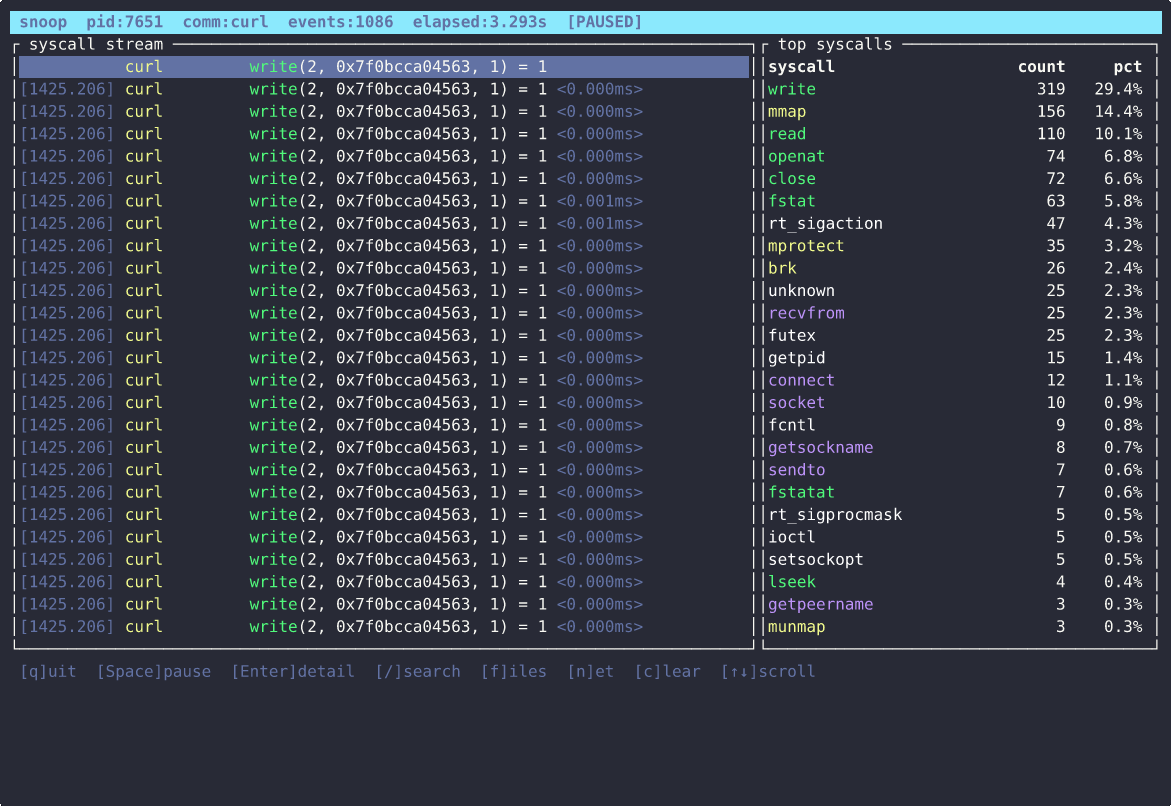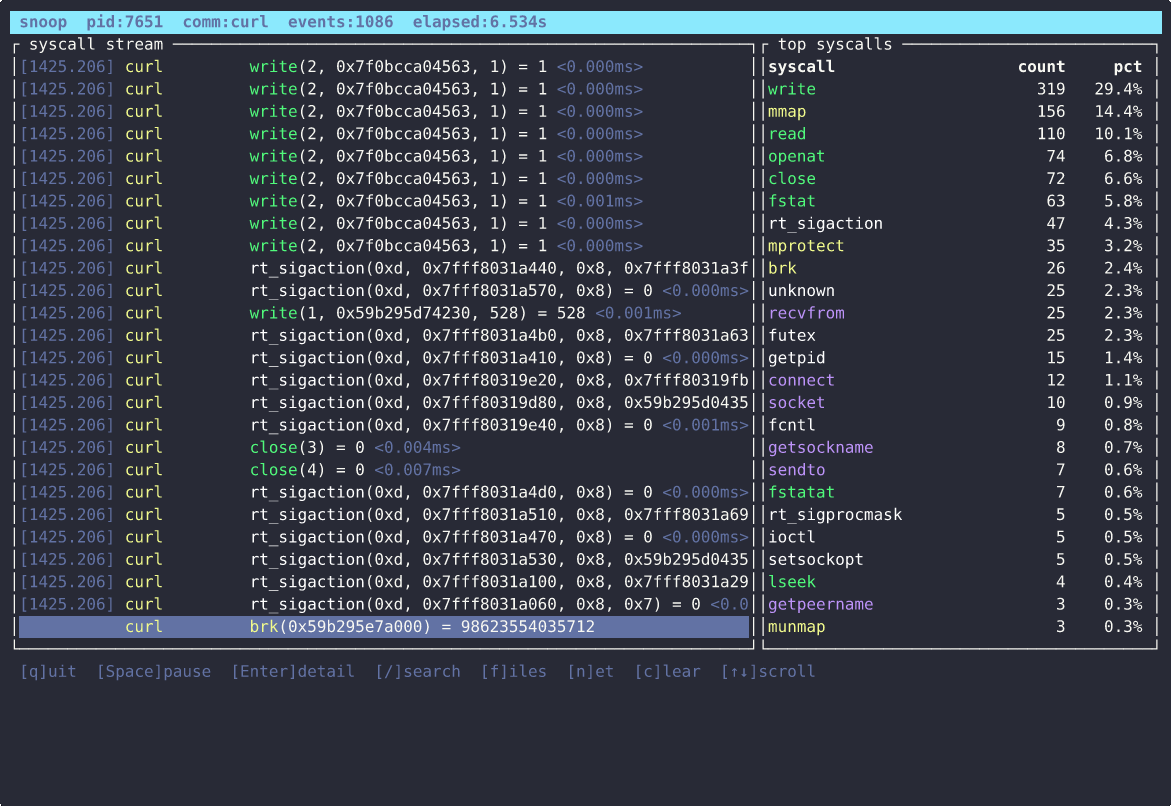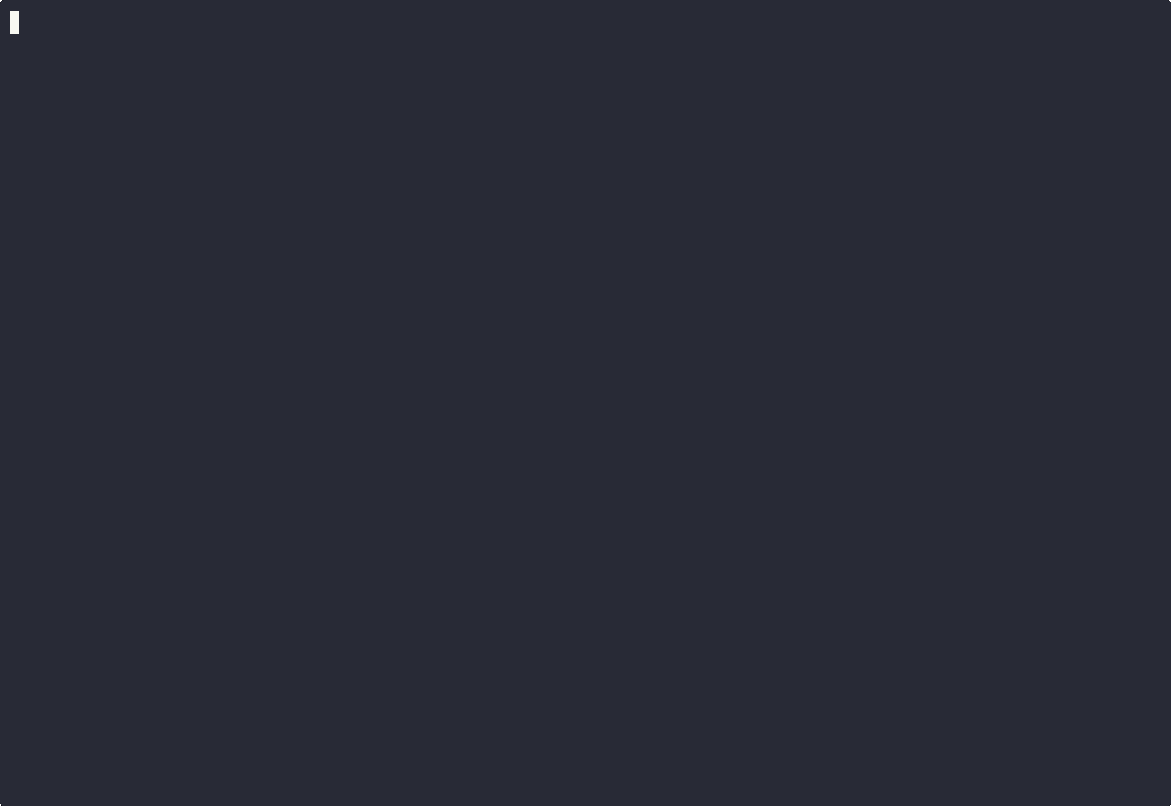 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
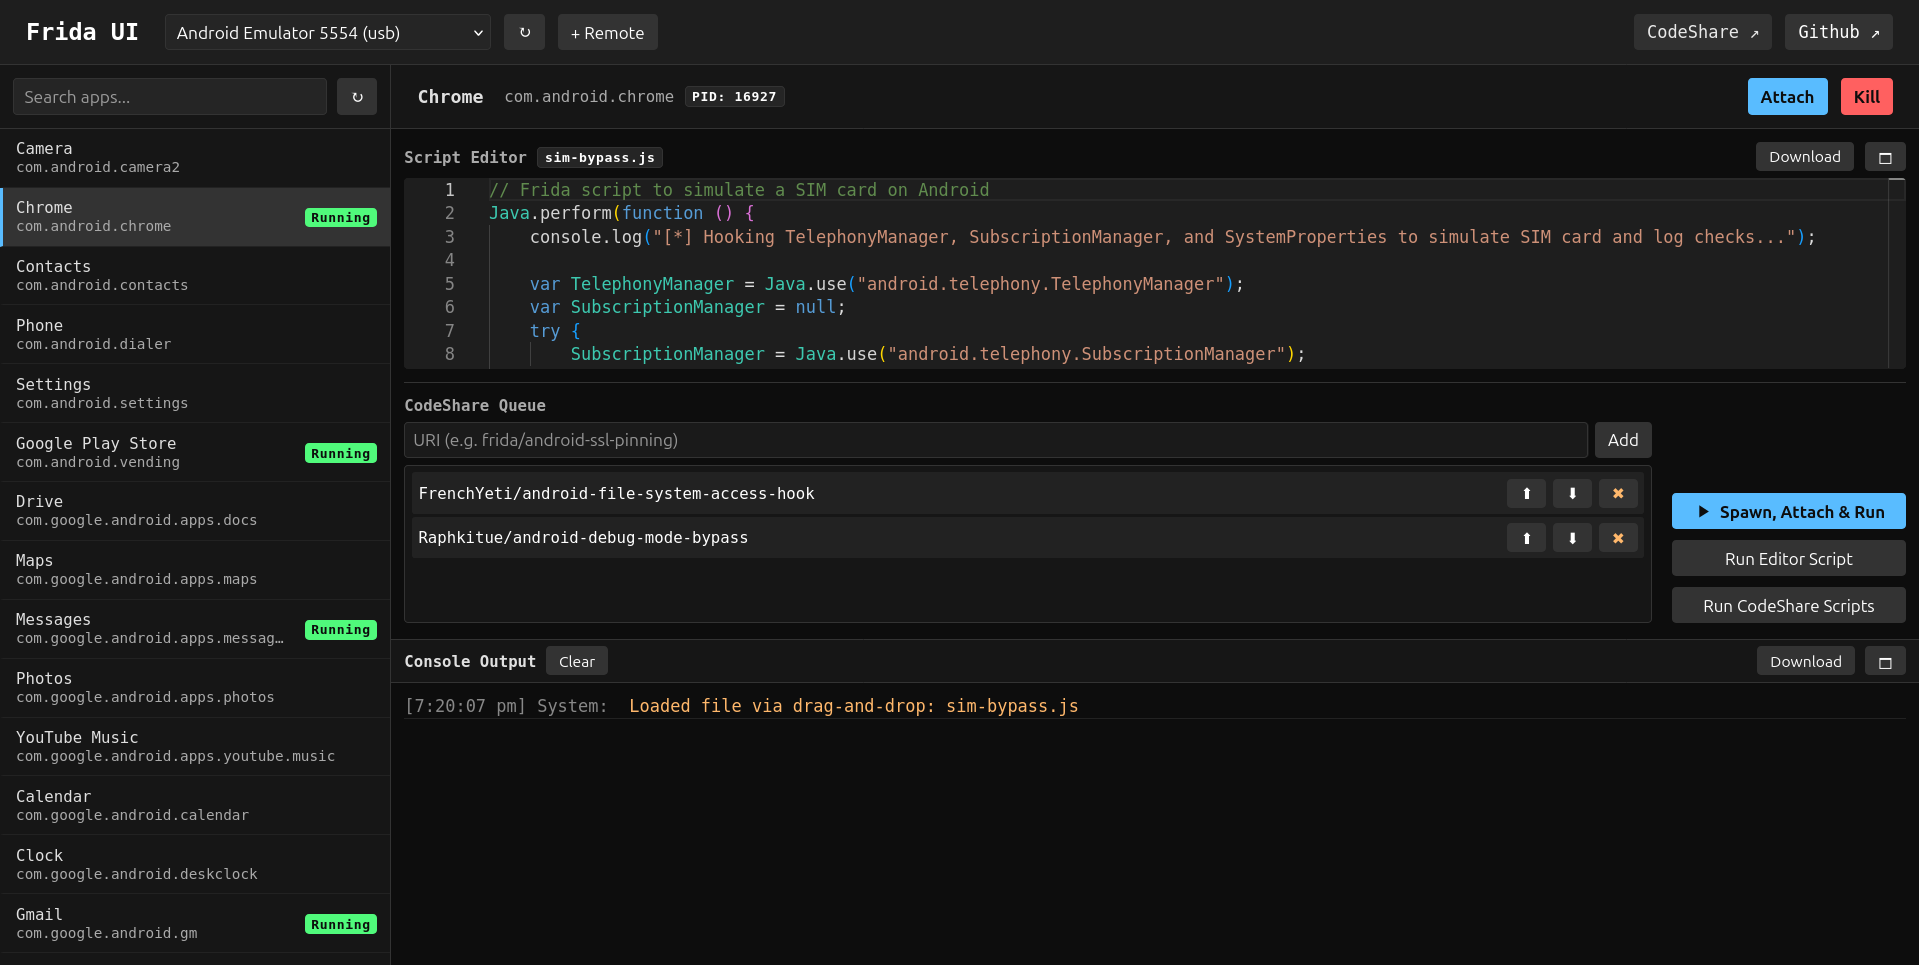 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
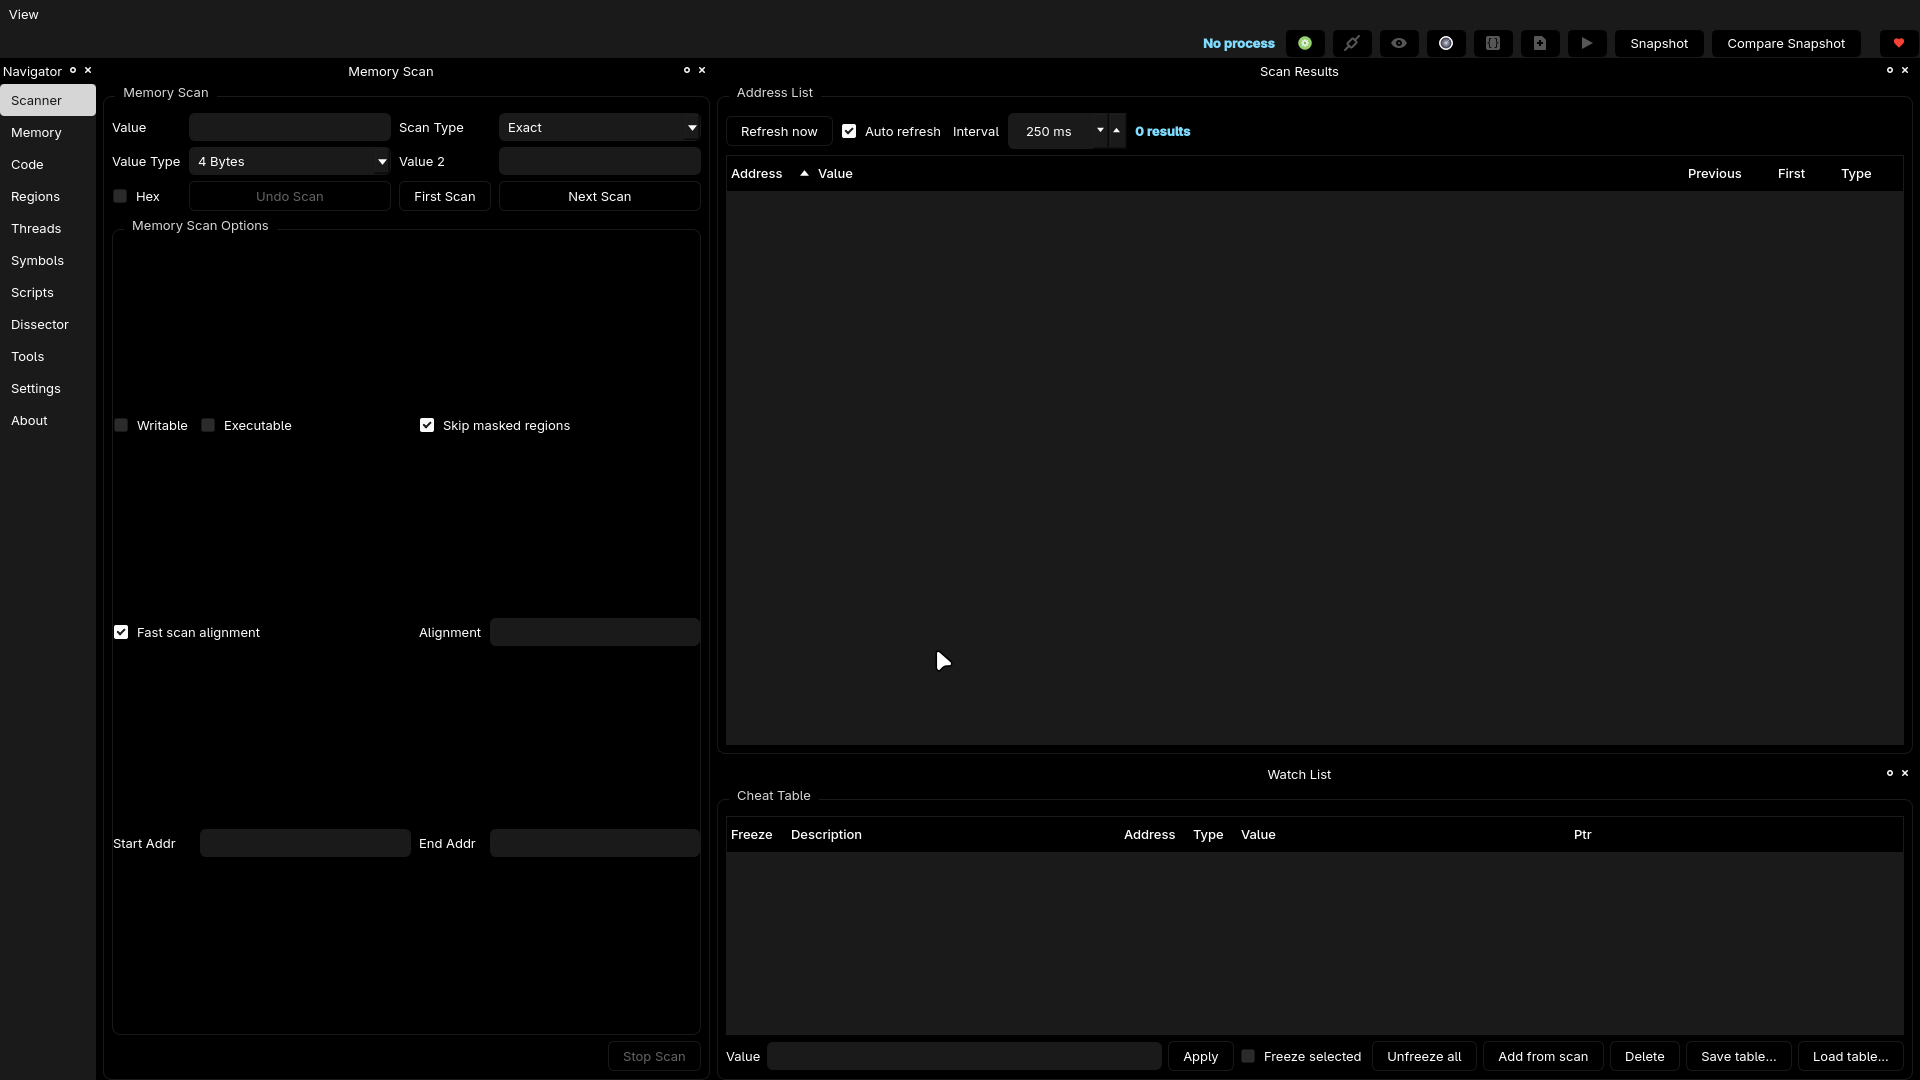 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android