
UnBattletech
 velteyn/unbattletech
BattleTech: The Crescent Hawk's Inception reverse engeneering
binary-analysisdebuggerseducation+3
velteyn/unbattletechBattleTech: The Crescent Hawk's Inception reverse engeneering
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
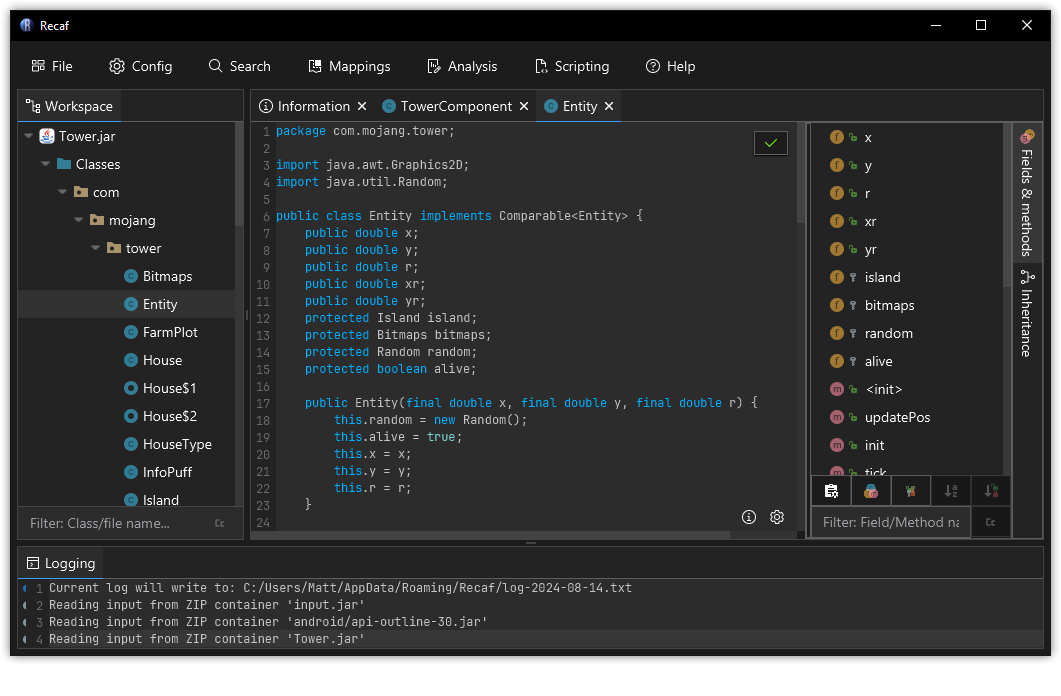
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
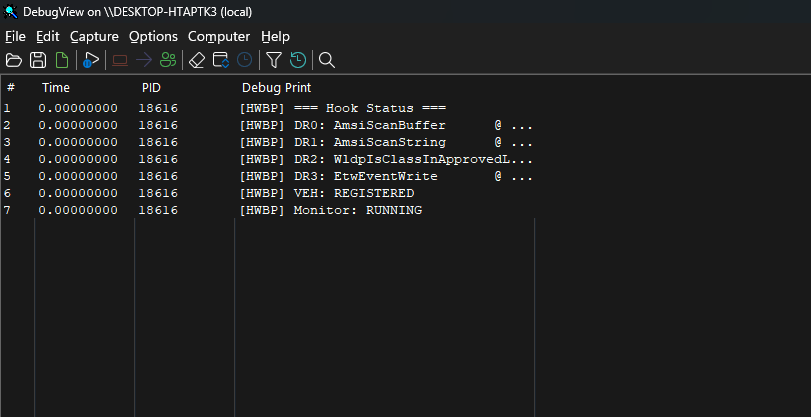 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 usbarmory/gotee-example
GoTEE - example application
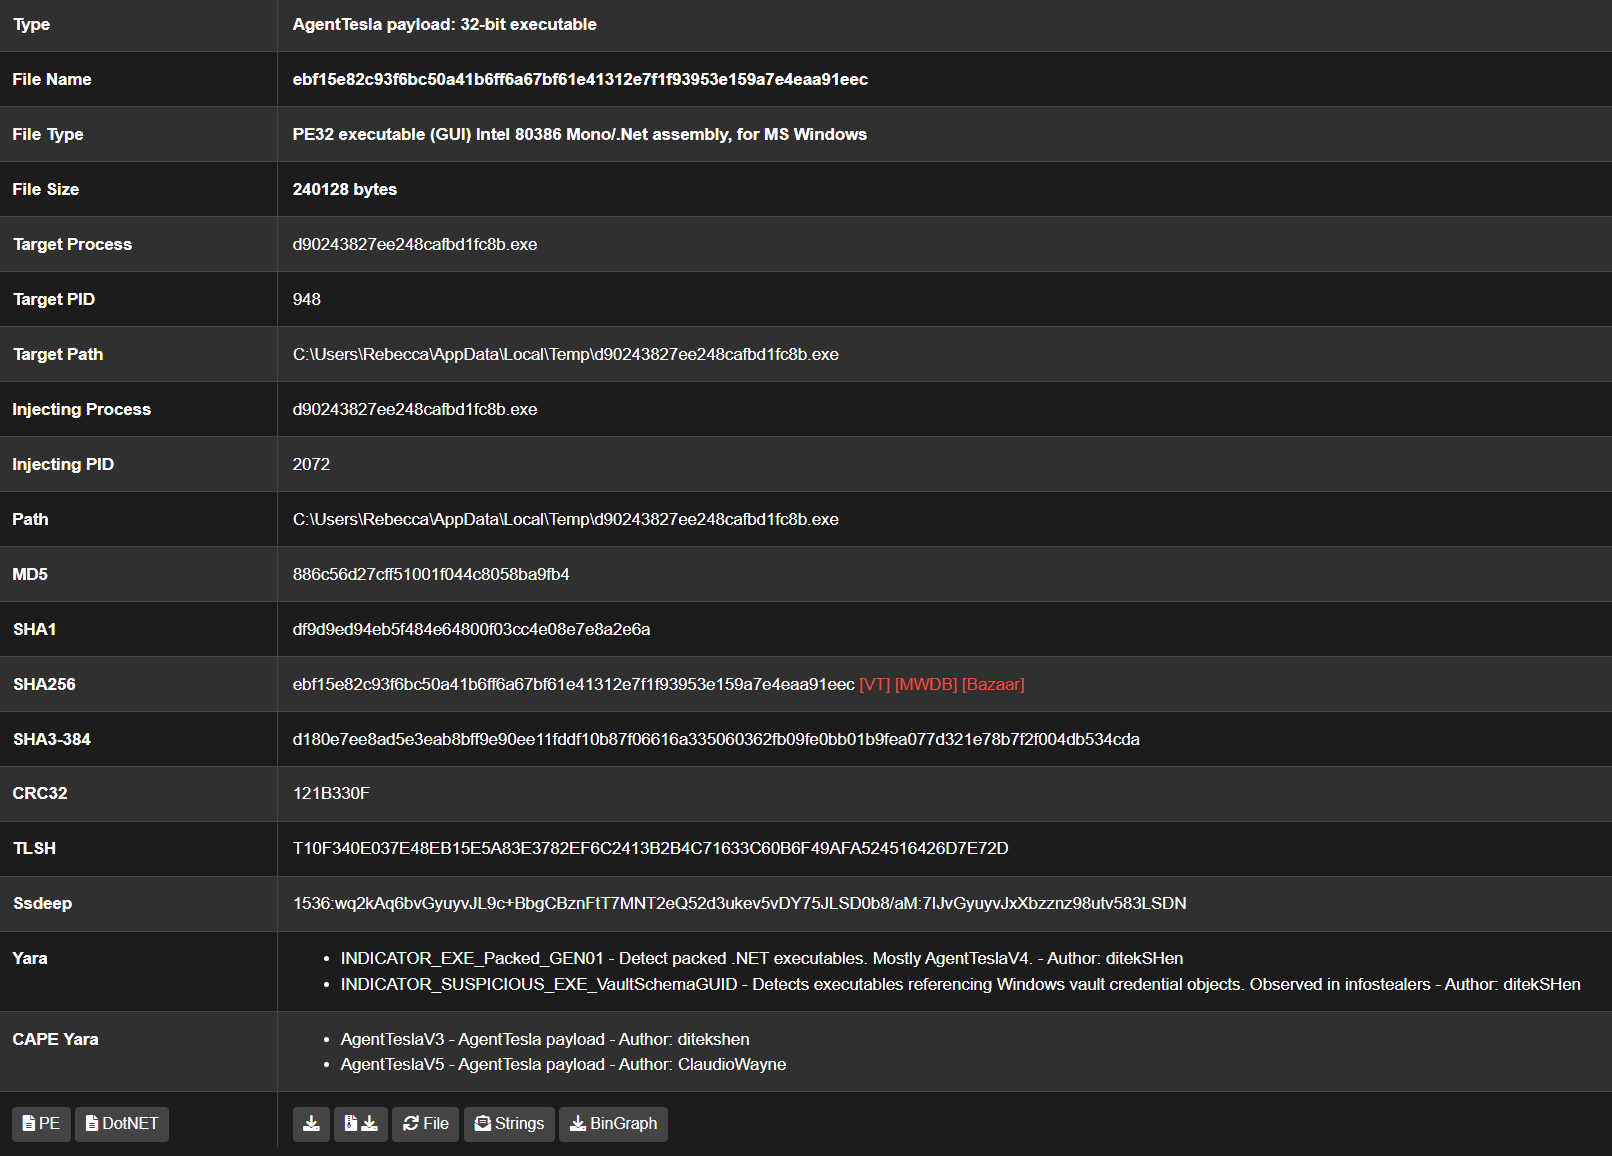 kevoreilly/capev2
Malware Configuration And Payload Extraction
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
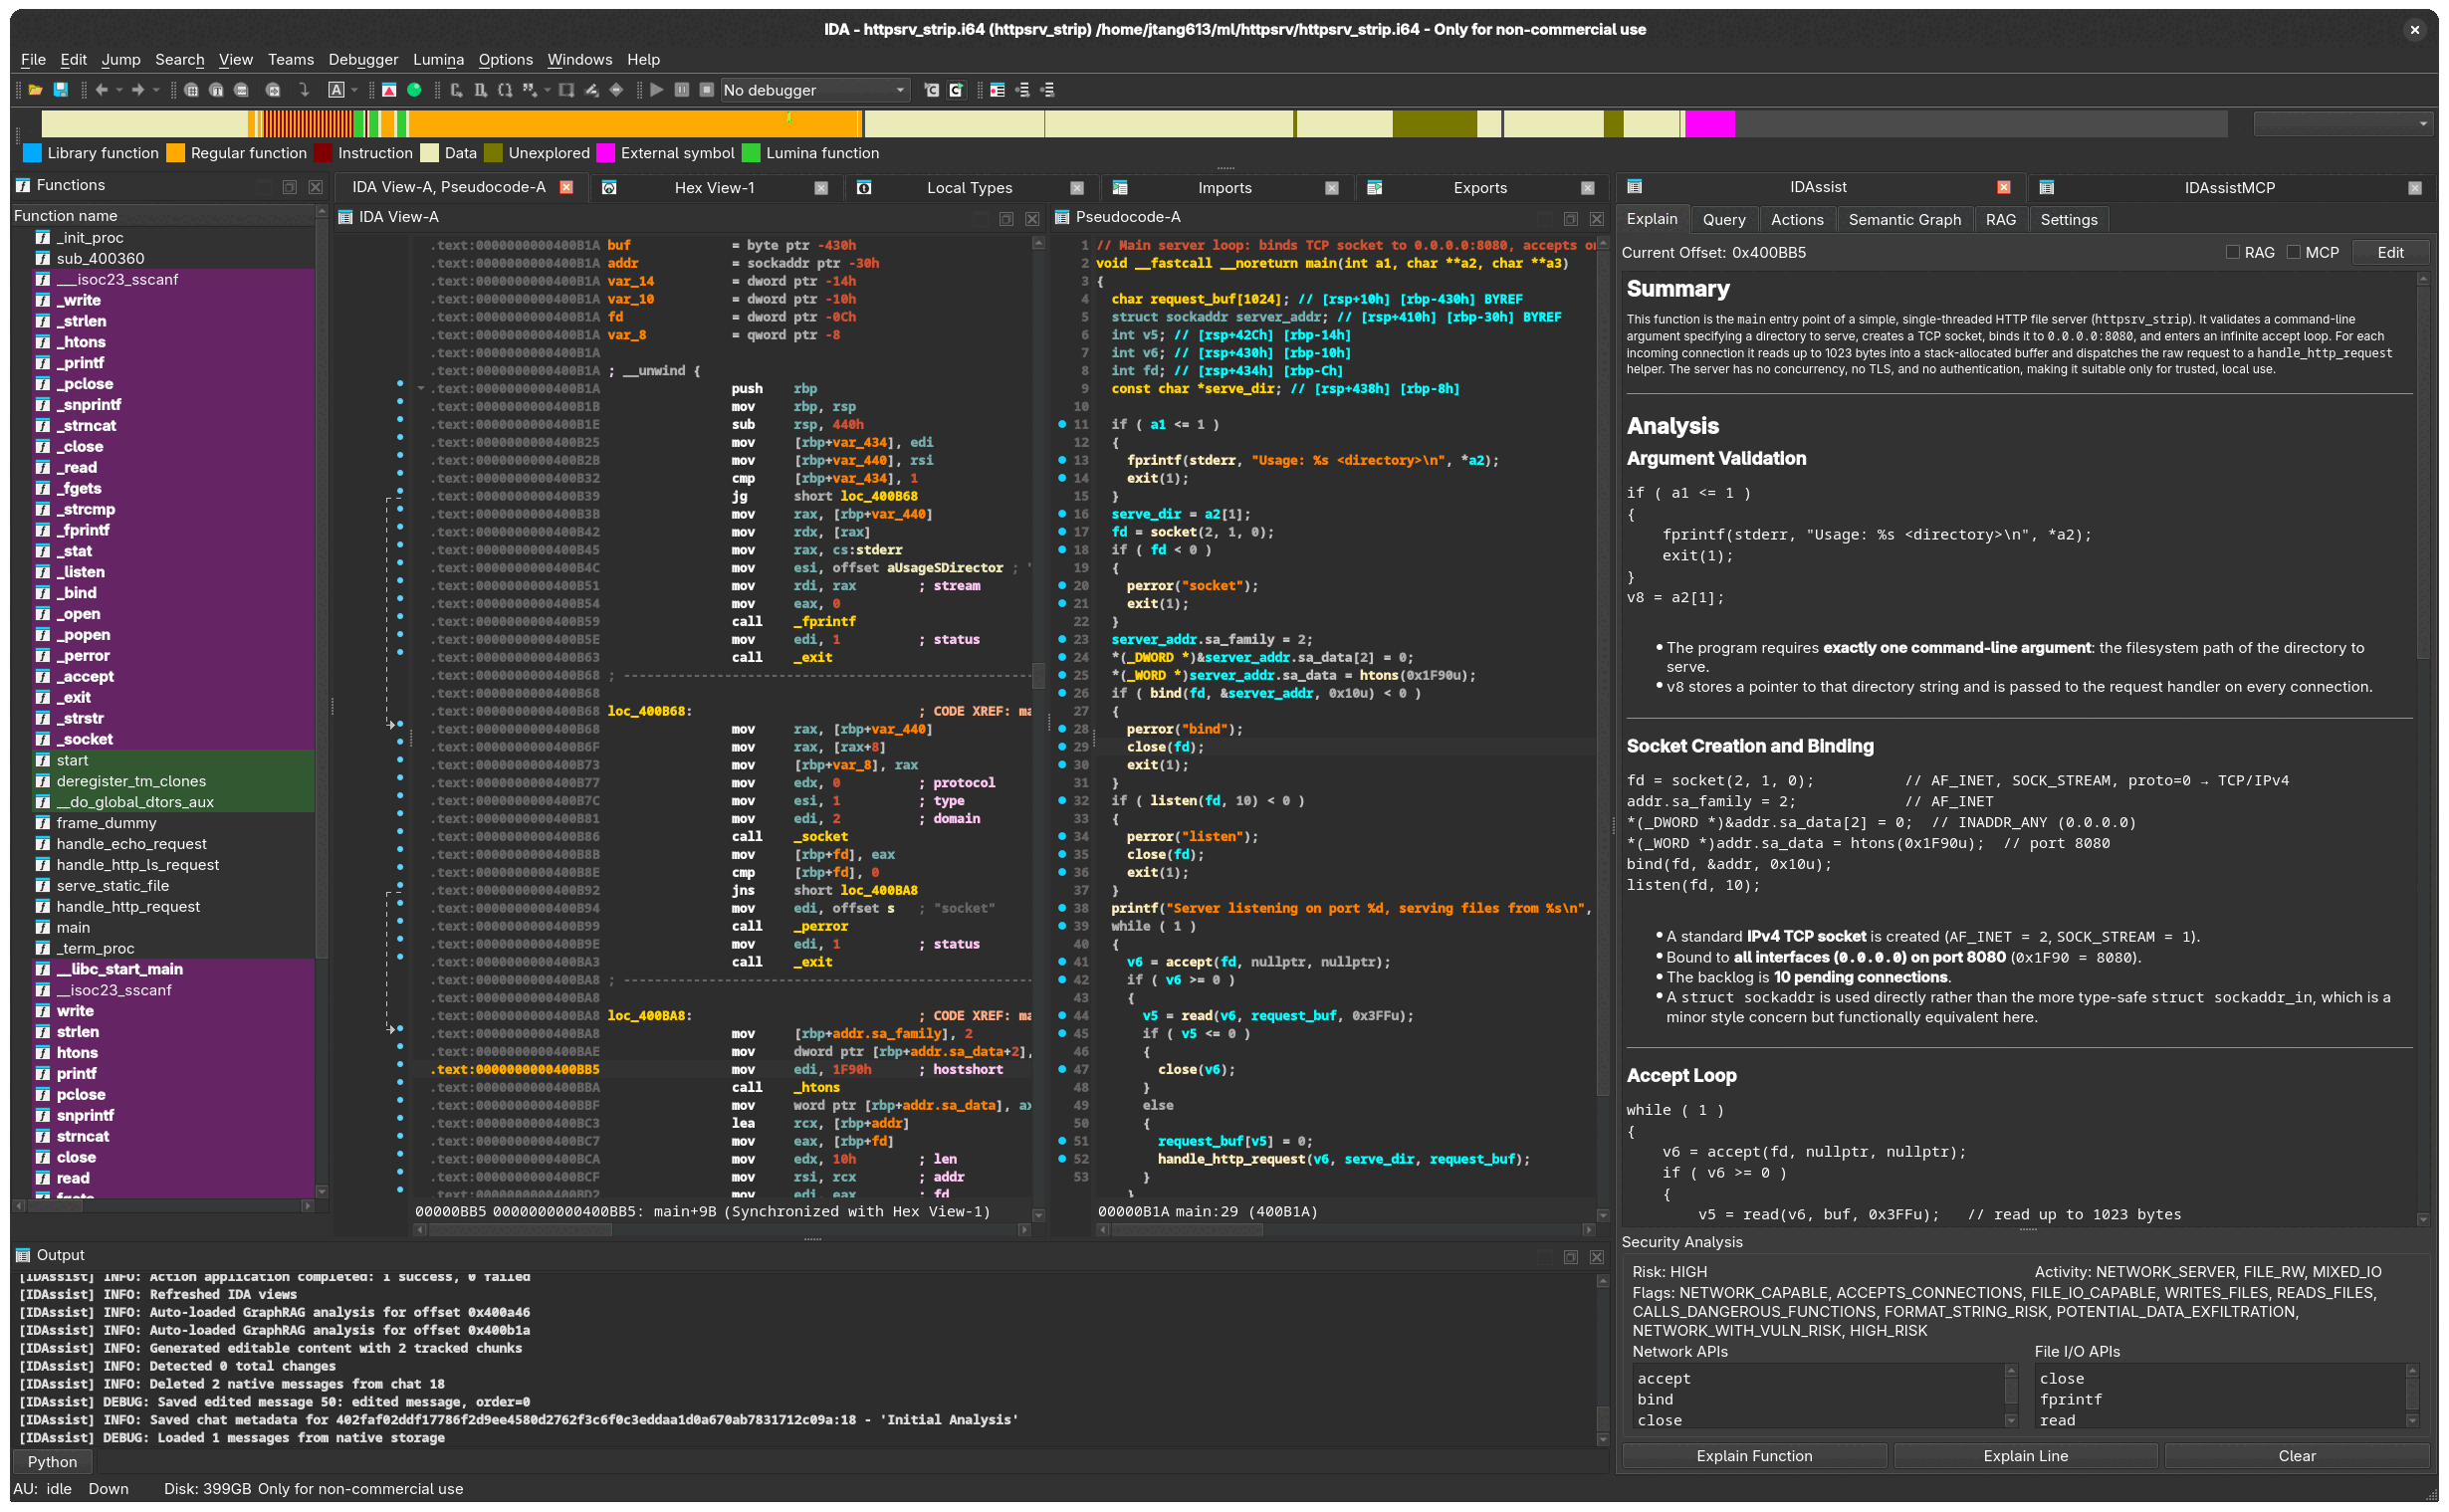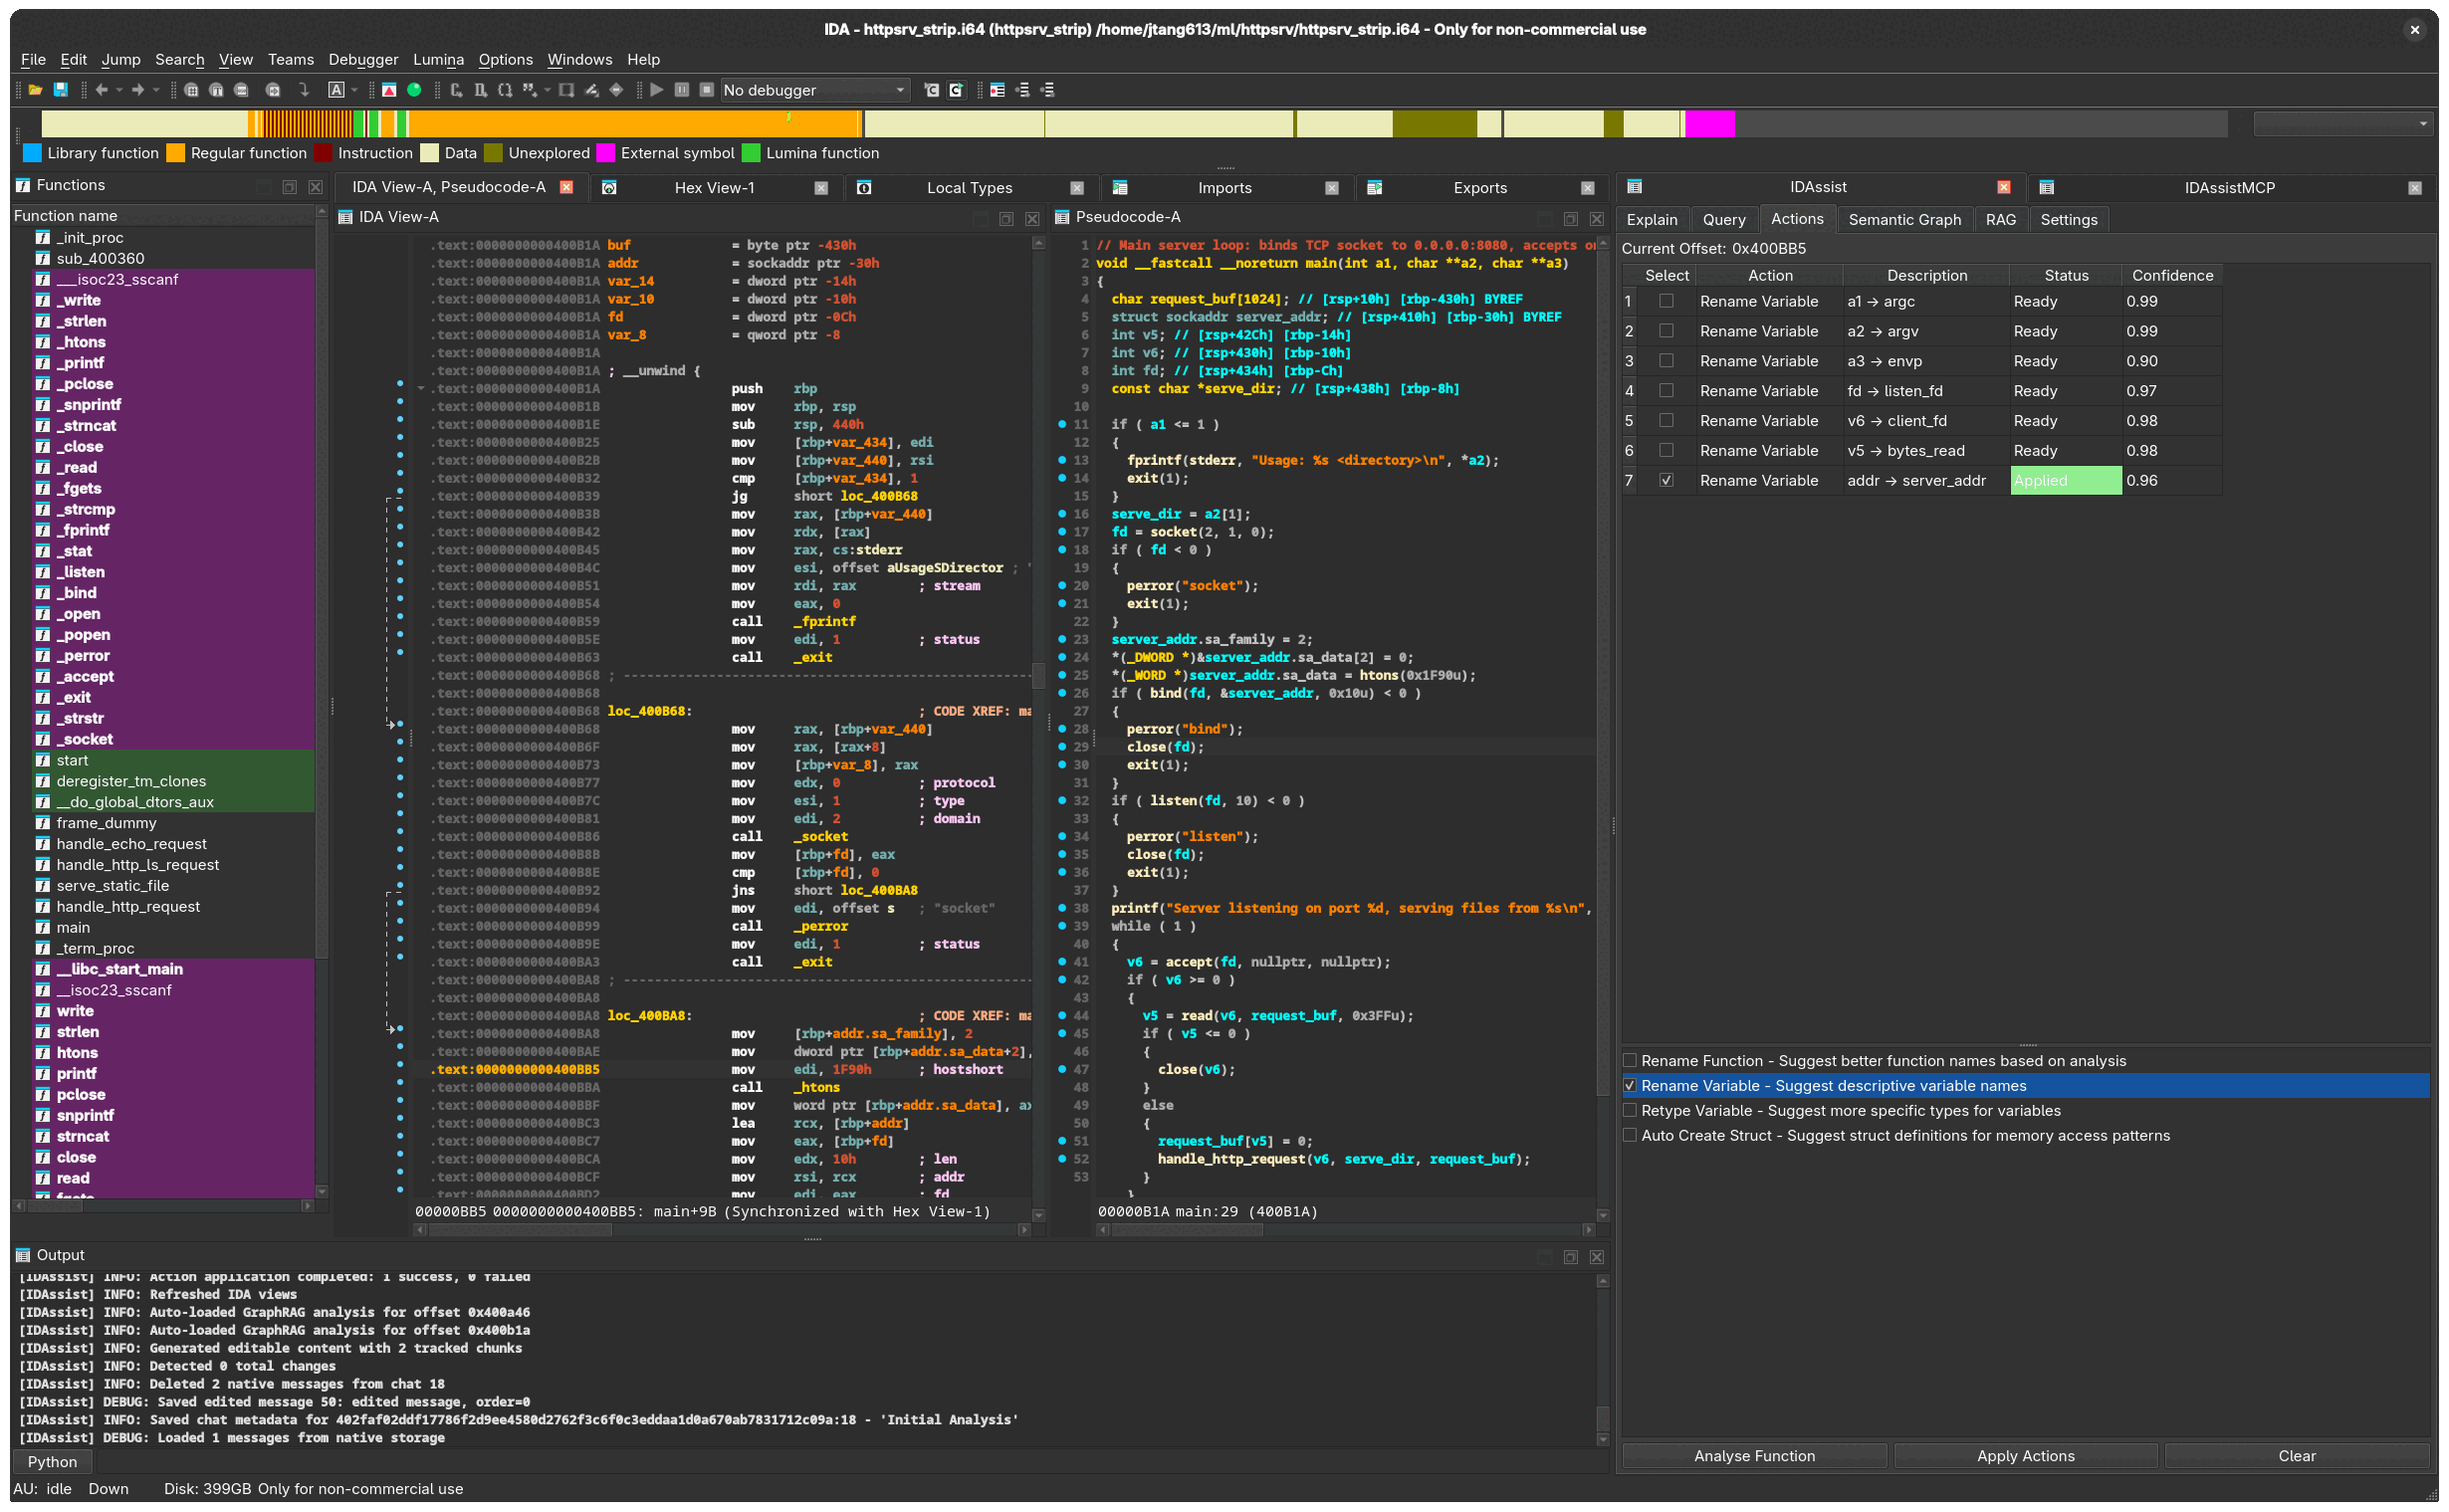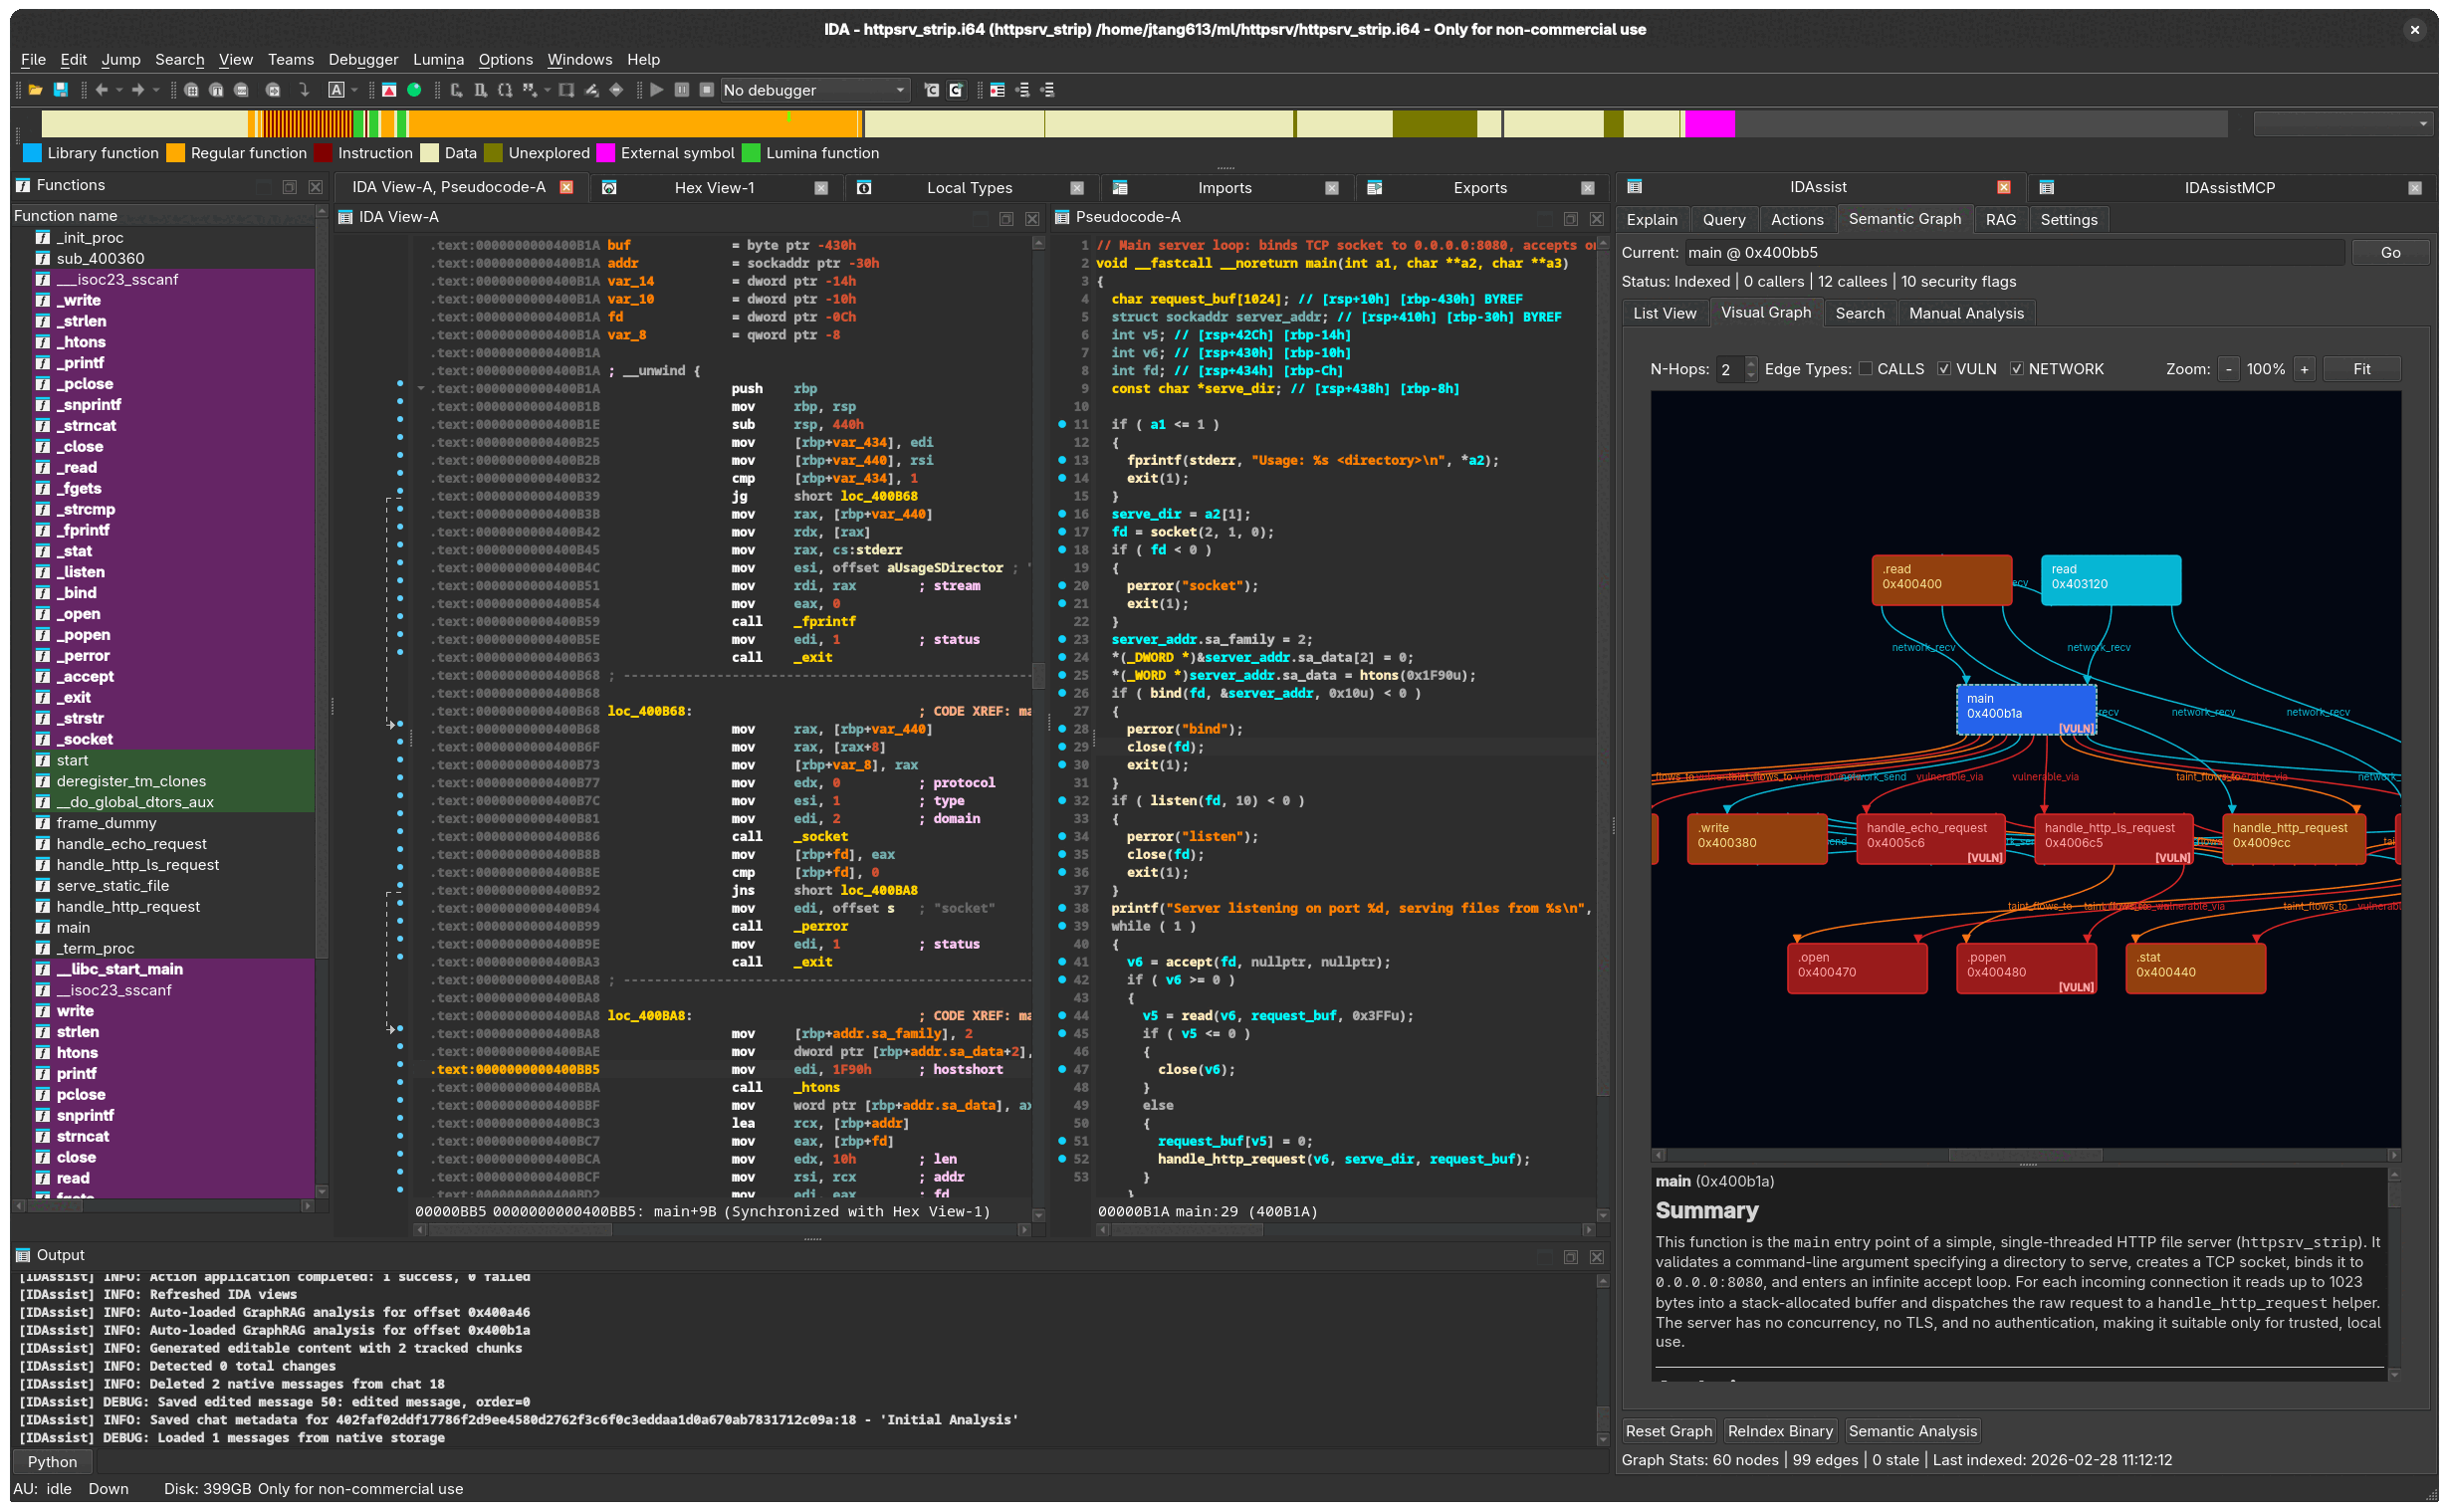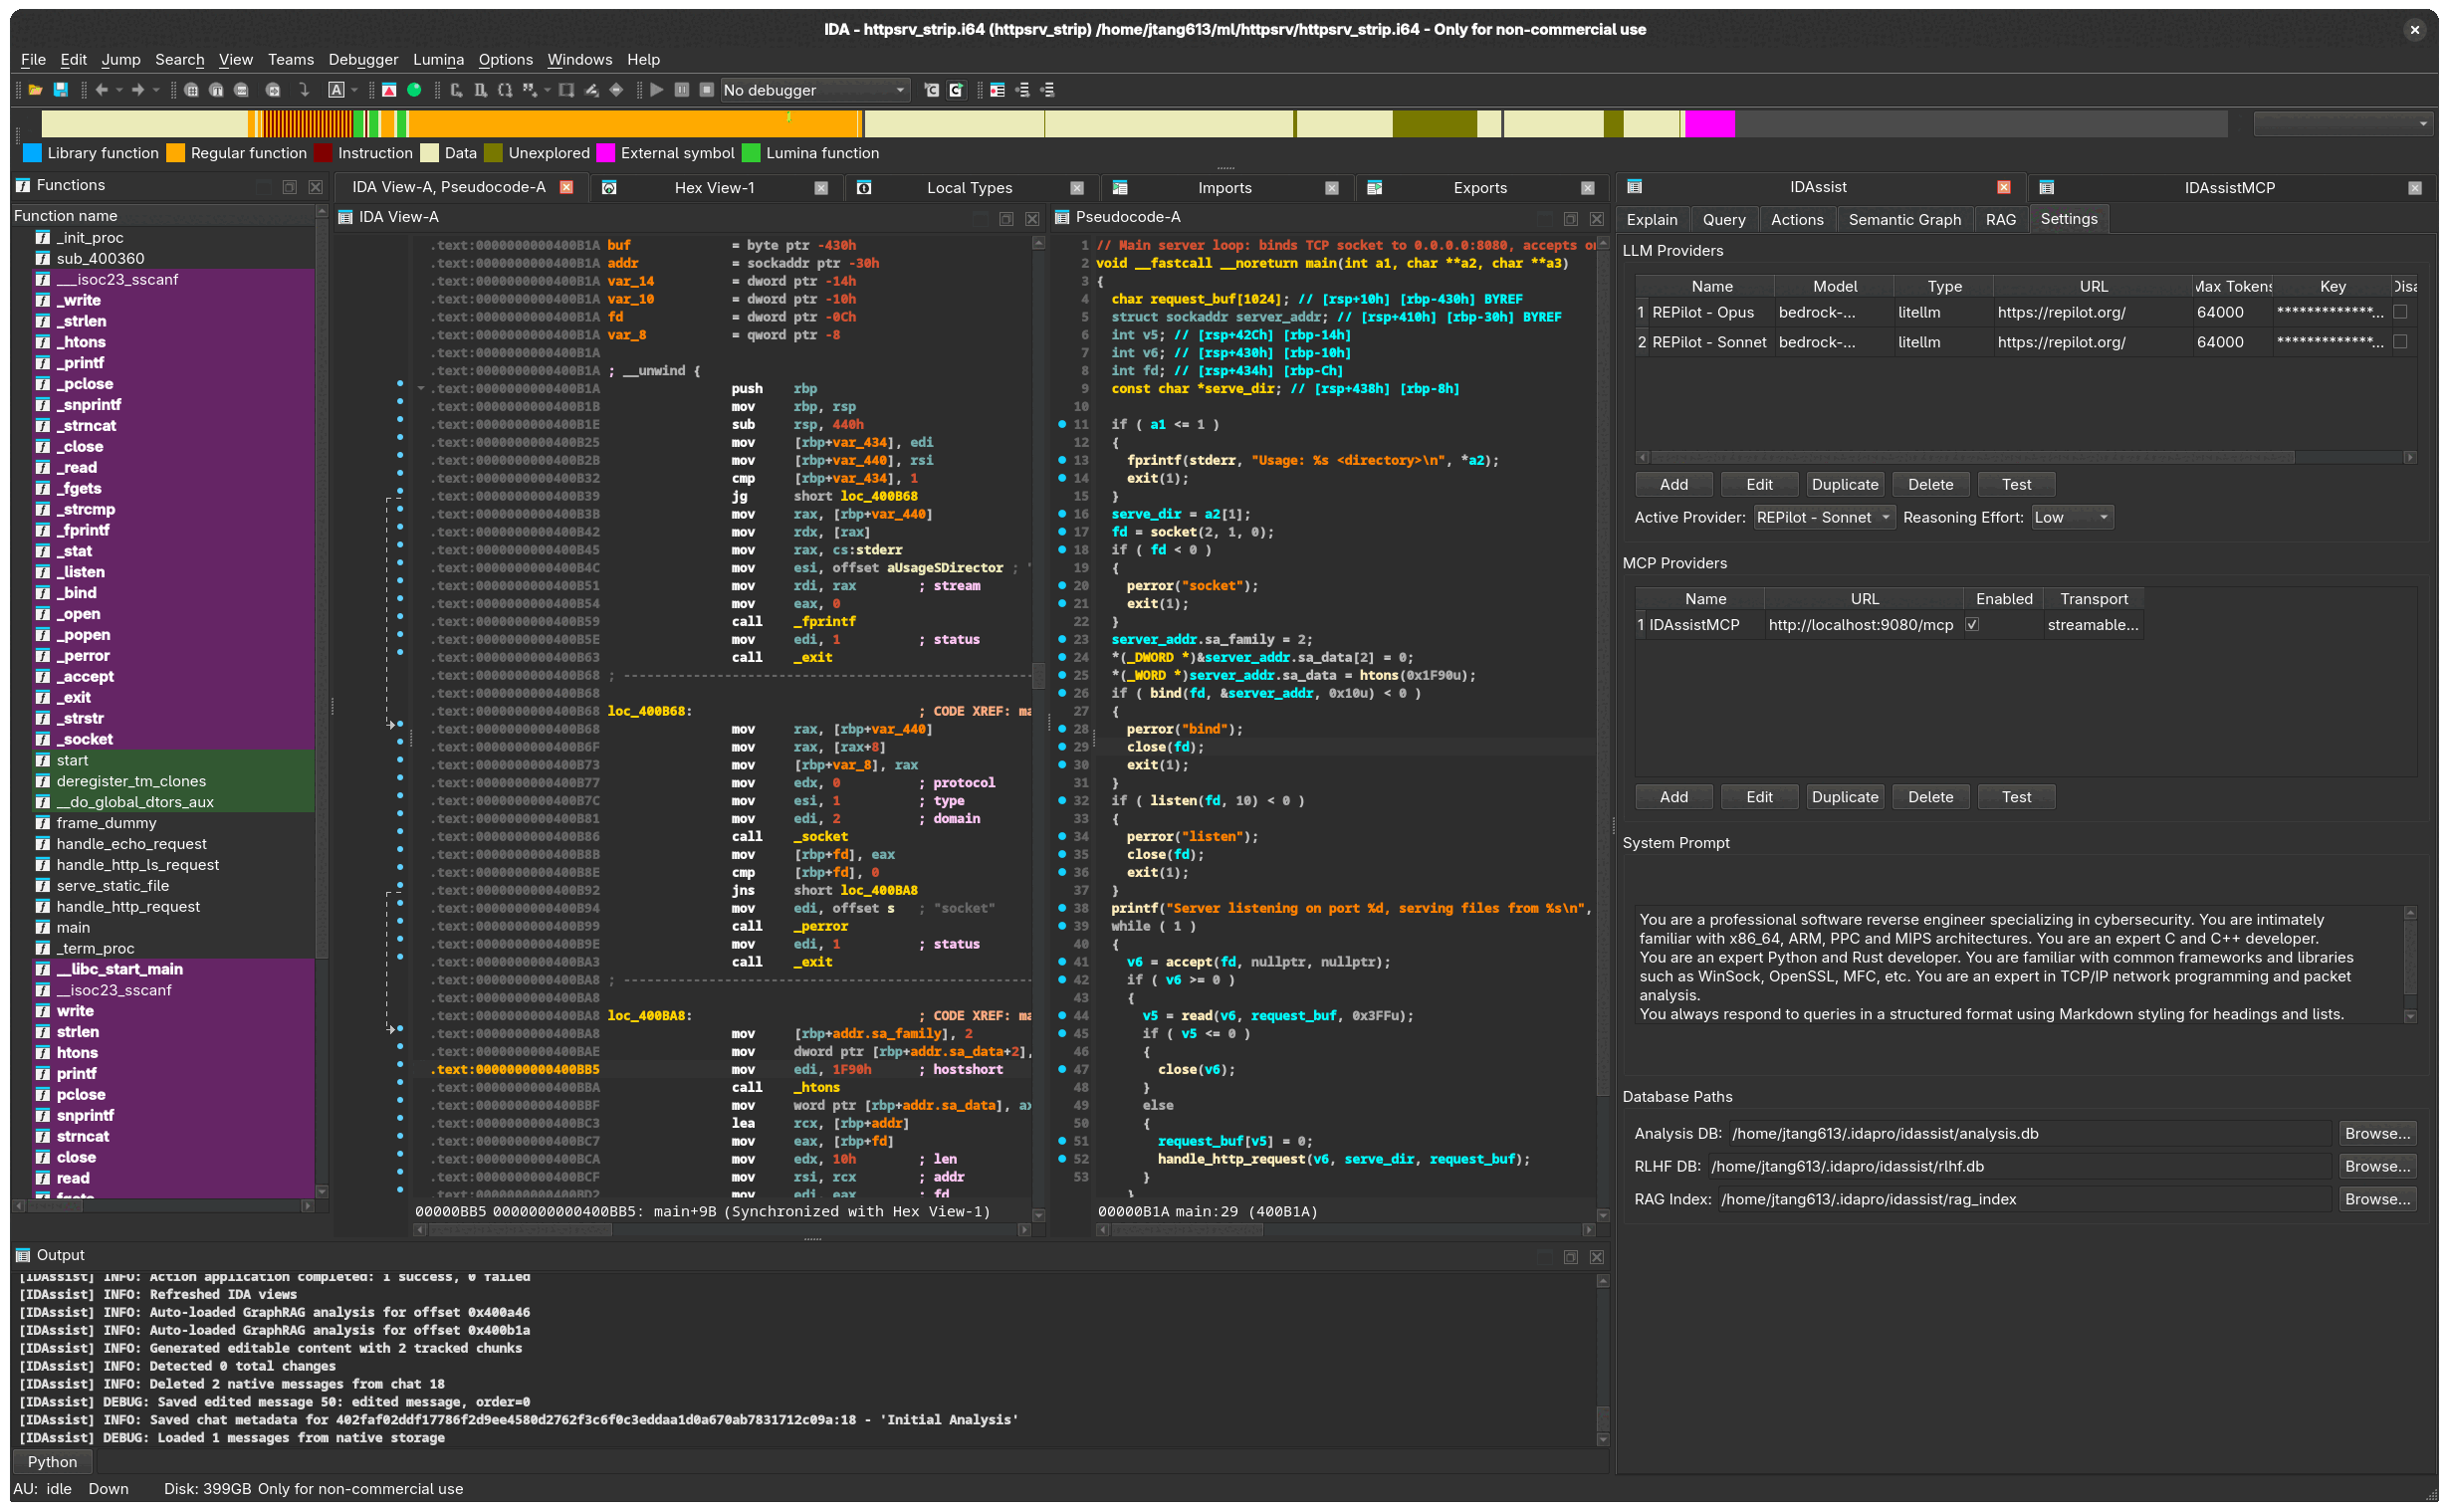 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro

 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool