IDA-Ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…

TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…

Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…

Lightweight fuzzing of a memory snapshot using KVM

A lightweight dynamic instrumentation library

Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.

A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…

Interact with Frida devices, processes, and scripts directly from your browser.

A lightweight hex editor and decompiler to solve your binary file analysis problems.

A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…

A lightweight test harness designed to speed up shellcode development by providing an execution environment with integrated crash diagnostics and…

A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks

Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)

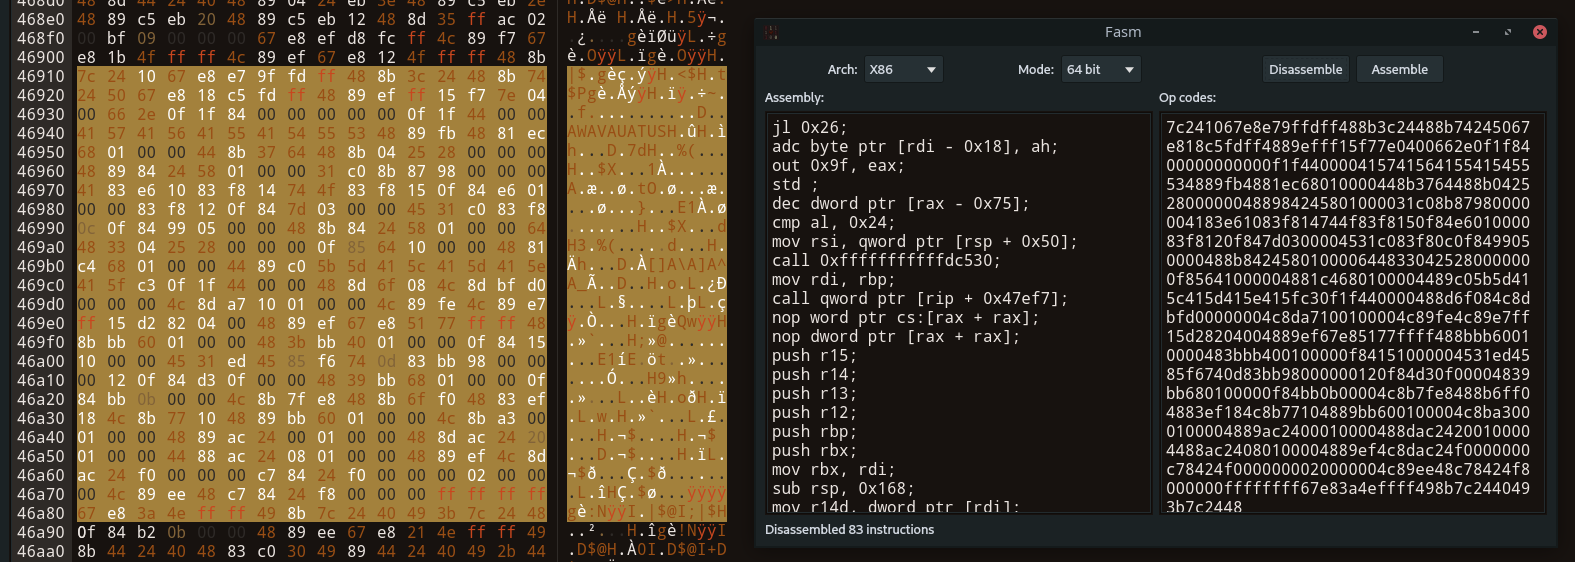
A Full-Featured HexEditor compatible with Linux/Windows/MacOS