

ceasta
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
169
ngwg/ceastadisassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 fail0verflow/ps5-umtxdbg
C++ exploit reliability experimentation for a PlayStation 5 FreeBSD kernel vulnerability, with VM kernel builds and GDB remote-debugging setup.
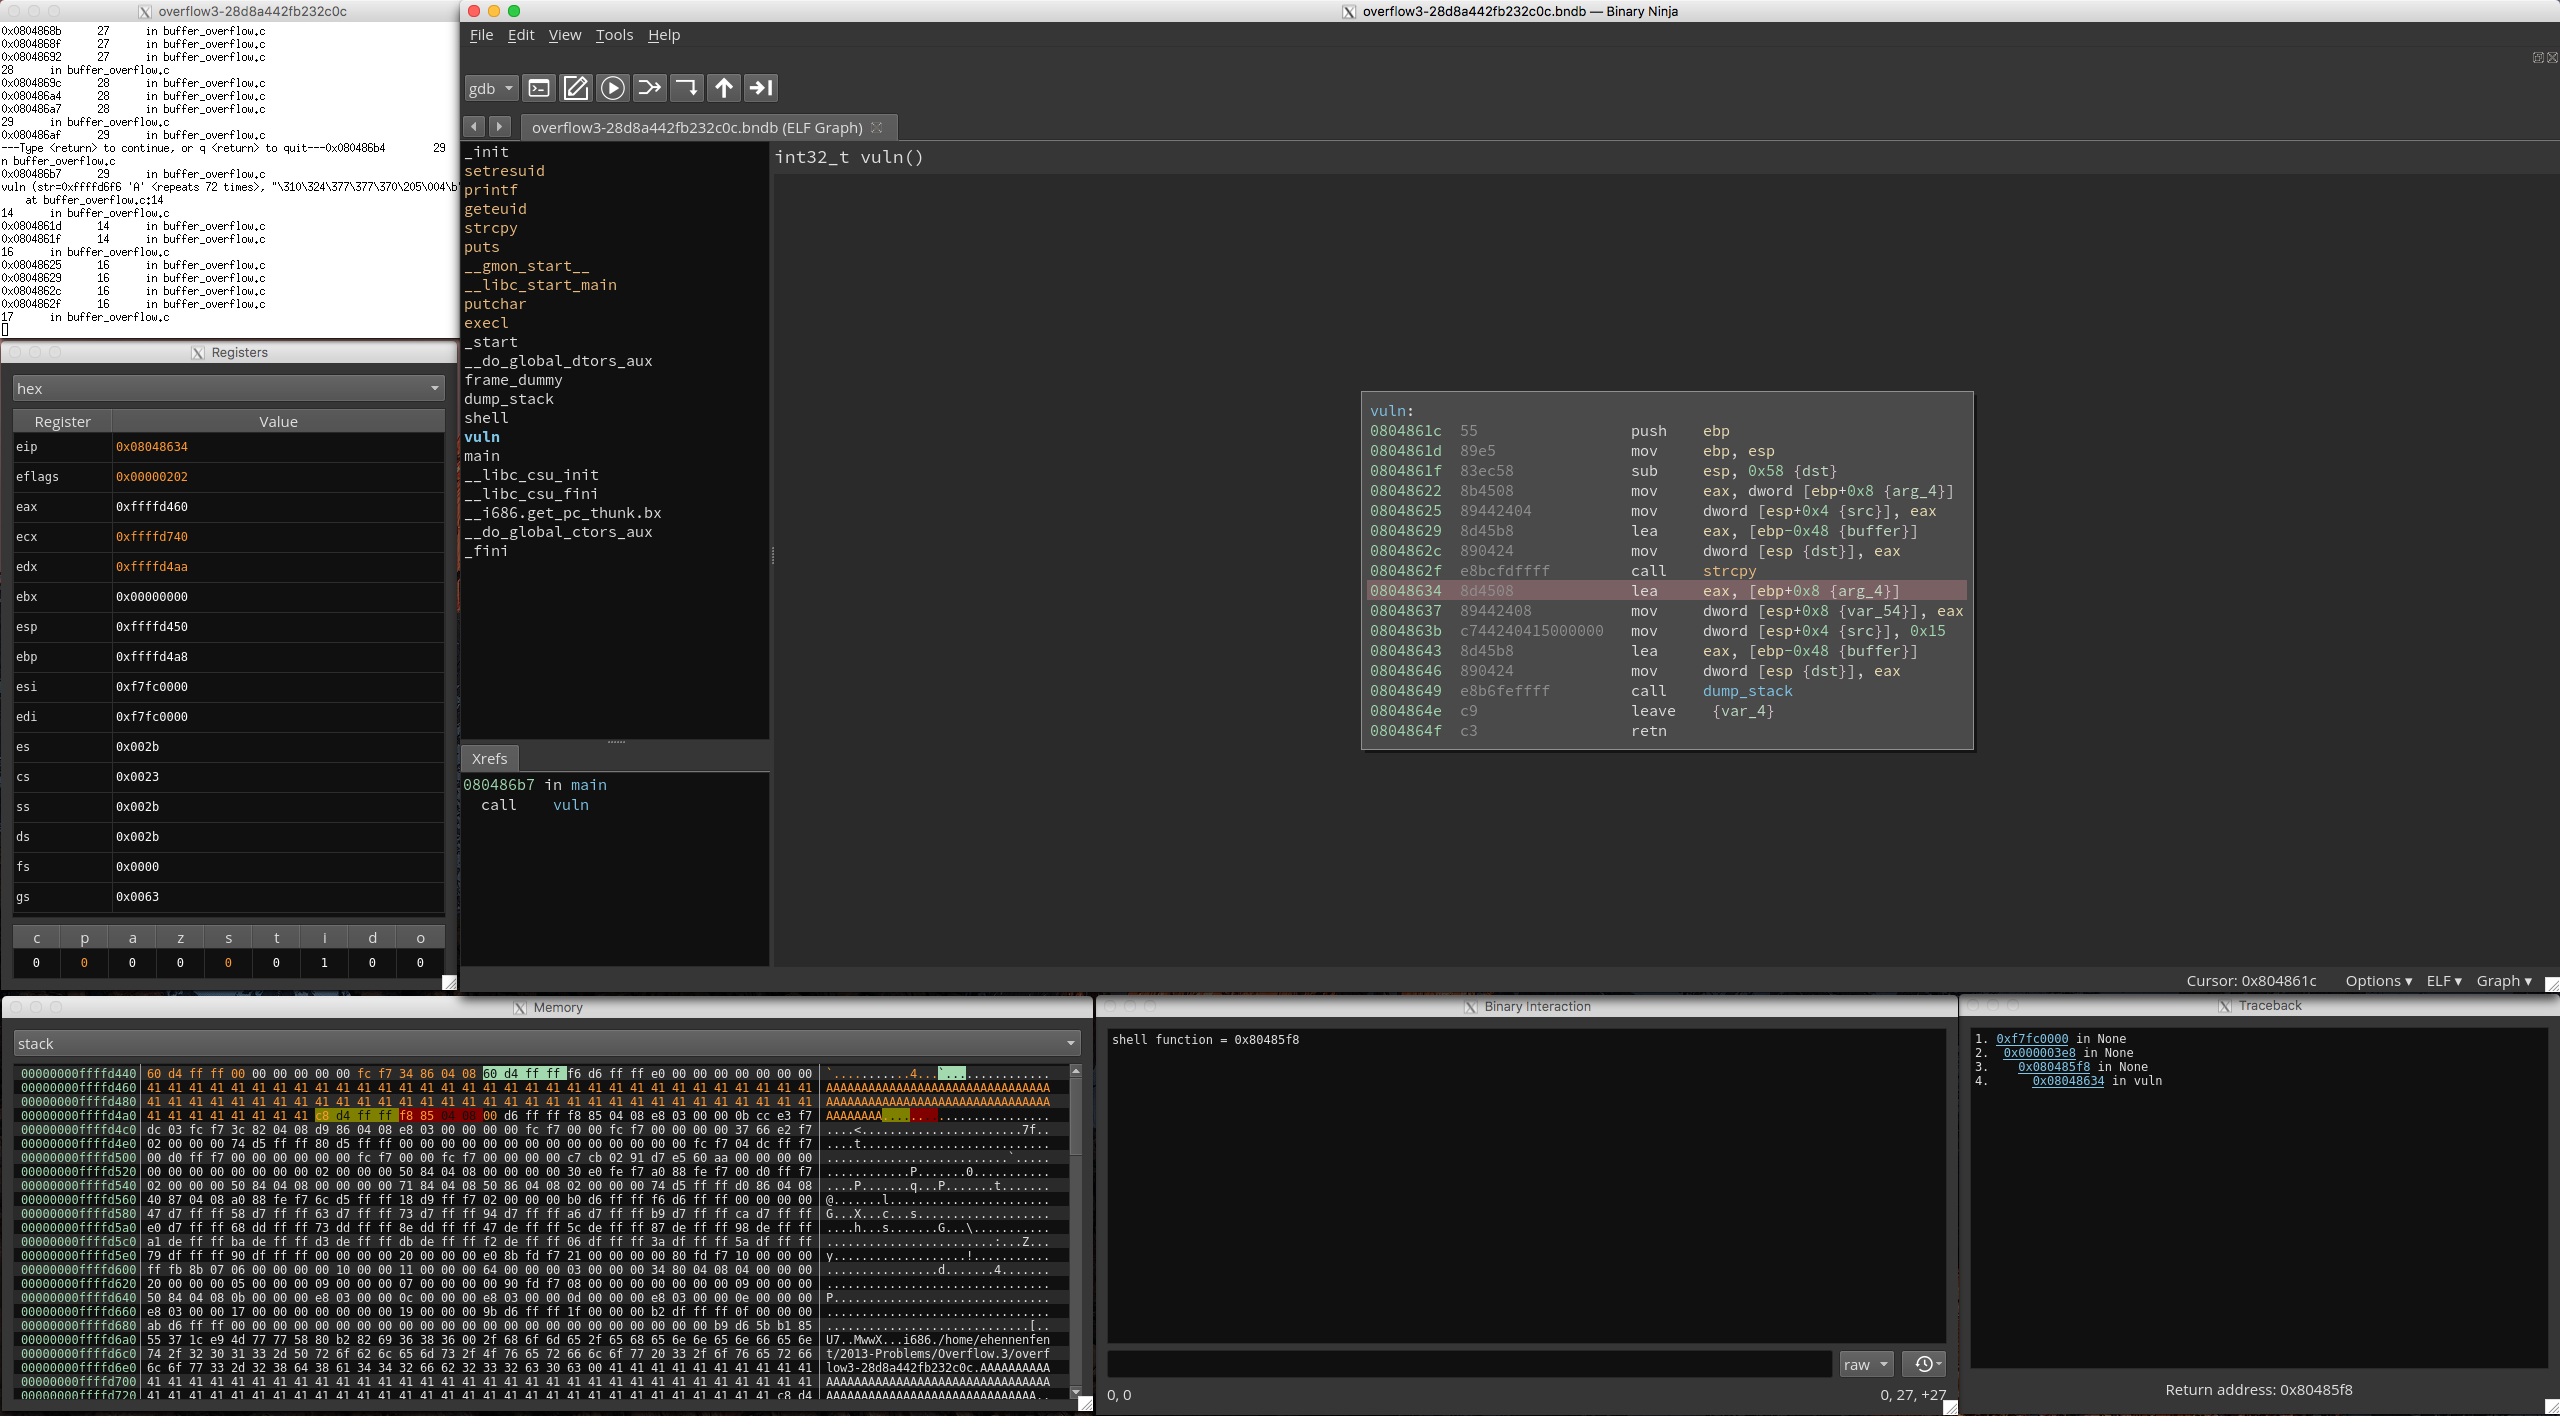 nccgroup/binja_dynamics
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
 nccgroup/iodide
The Cisco IOS Debugger and Integrated Disassembler Environment
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 halcy0nic/cve-2022-44311
Proof of concept for CVE-2022-44311
 halcy0nic/cve-2022-43343
Proof of concept for (CVE-2022-43343)
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 calysteon/cve-2025-43504
Technical deep-dive into CVE-2025-43504, a remote pre-authentication global buffer overflow in LLDB's debugserver for iOS, with PoC code and…
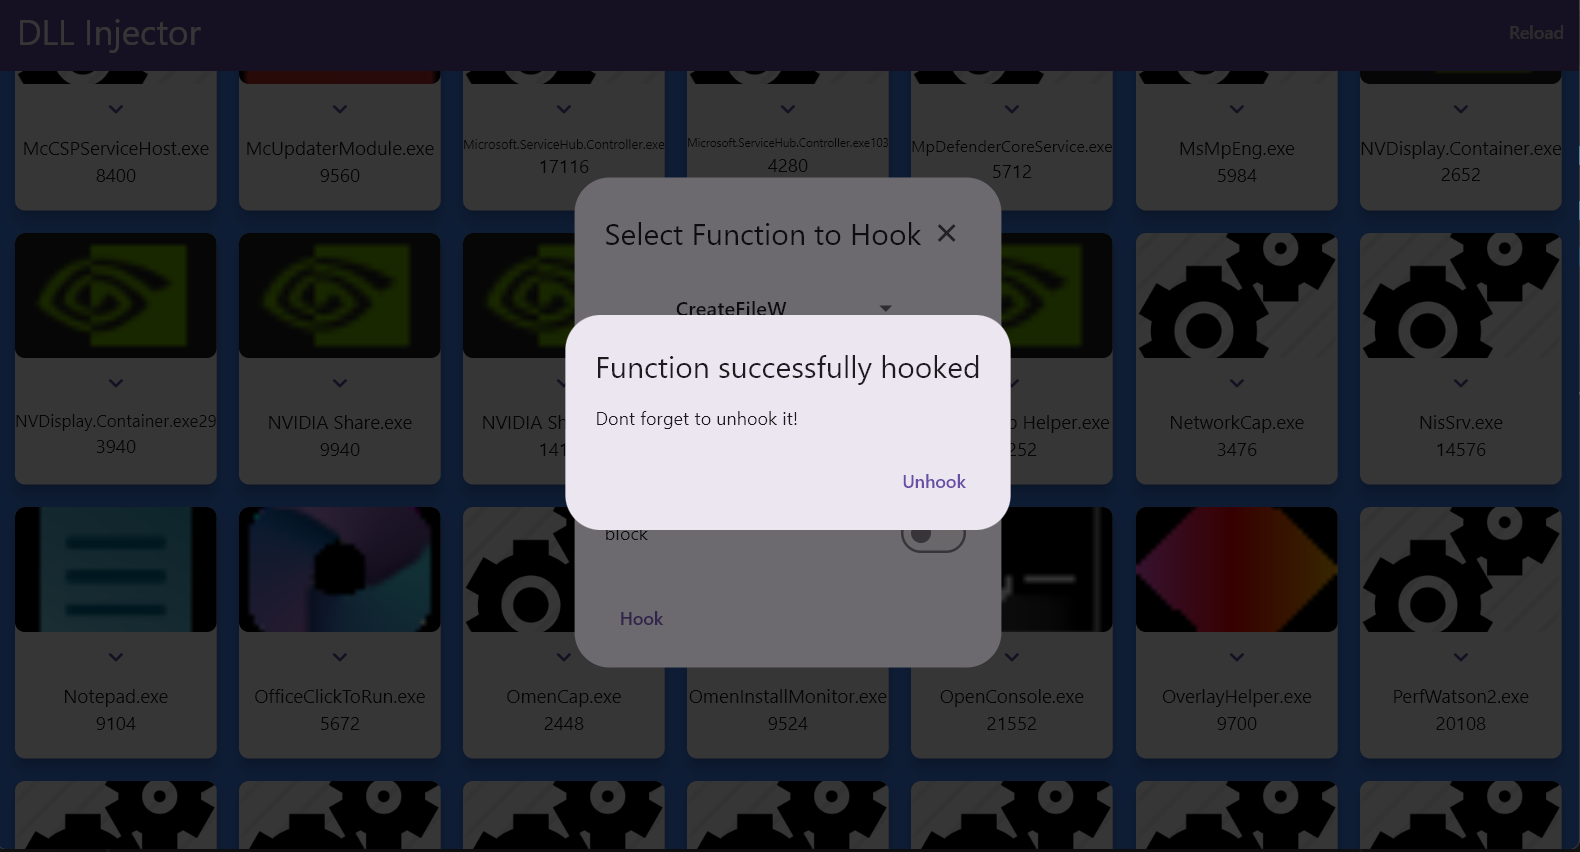 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime