
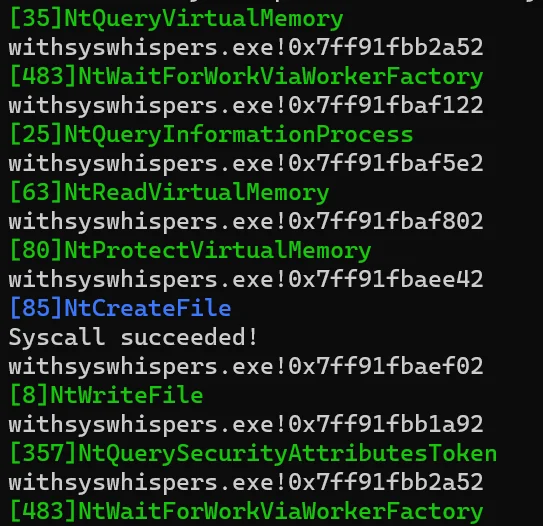
NtStrace
 gmh5225/ntstrace
frida-stalker based system call tracer on windows(x64).
binary-analysisdebuggersdynamic-analysis-sandboxing+2
gmh5225/ntstracefrida-stalker based system call tracer on windows(x64).
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
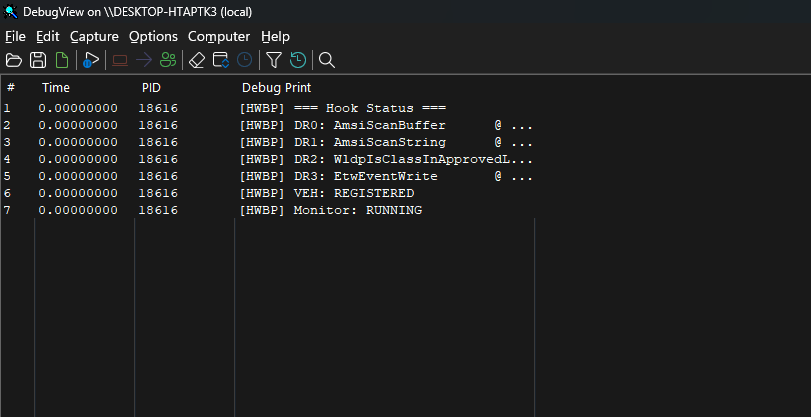 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
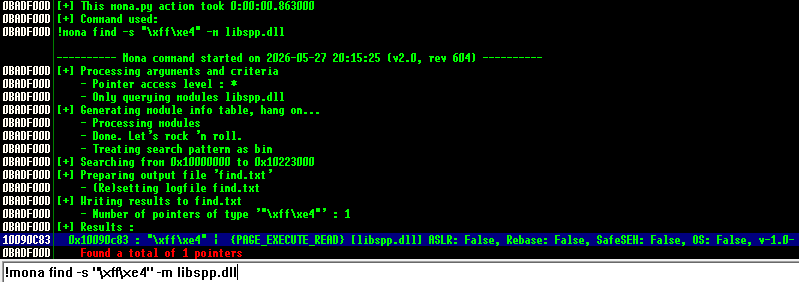 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 usbarmory/gotee-example
GoTEE - example application
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 nccgroup/libmempool
Heap analysis tooling for mempool
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
 colton1skees/dna
LLVM based static binary analysis framework
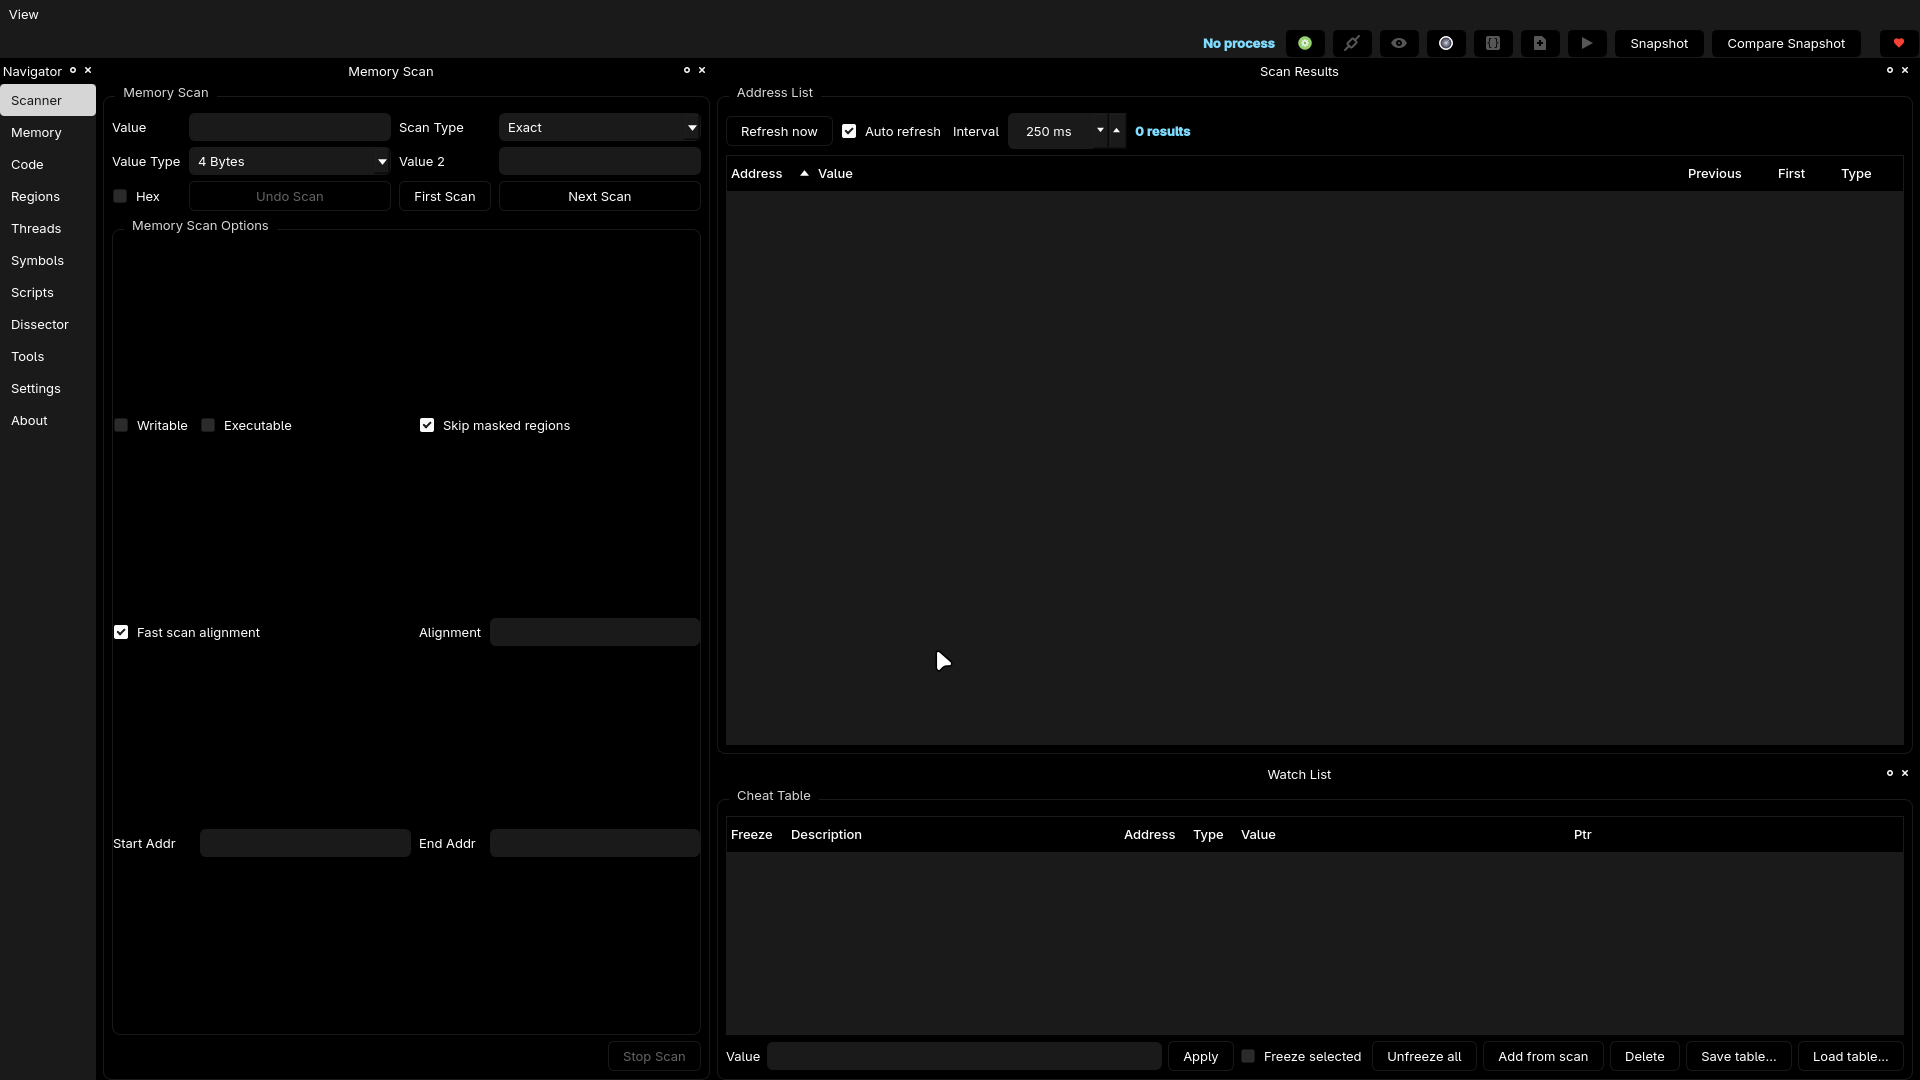 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 kitctf/nginxpwn
Exploitation Training -- CVE-2013-2028: Nginx Stack Based Buffer Overflow
 iamescri/cve-2025-5548-freefloat-ftp-buffer-overflow
Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0