

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.1k3 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 pingcap/failpoint
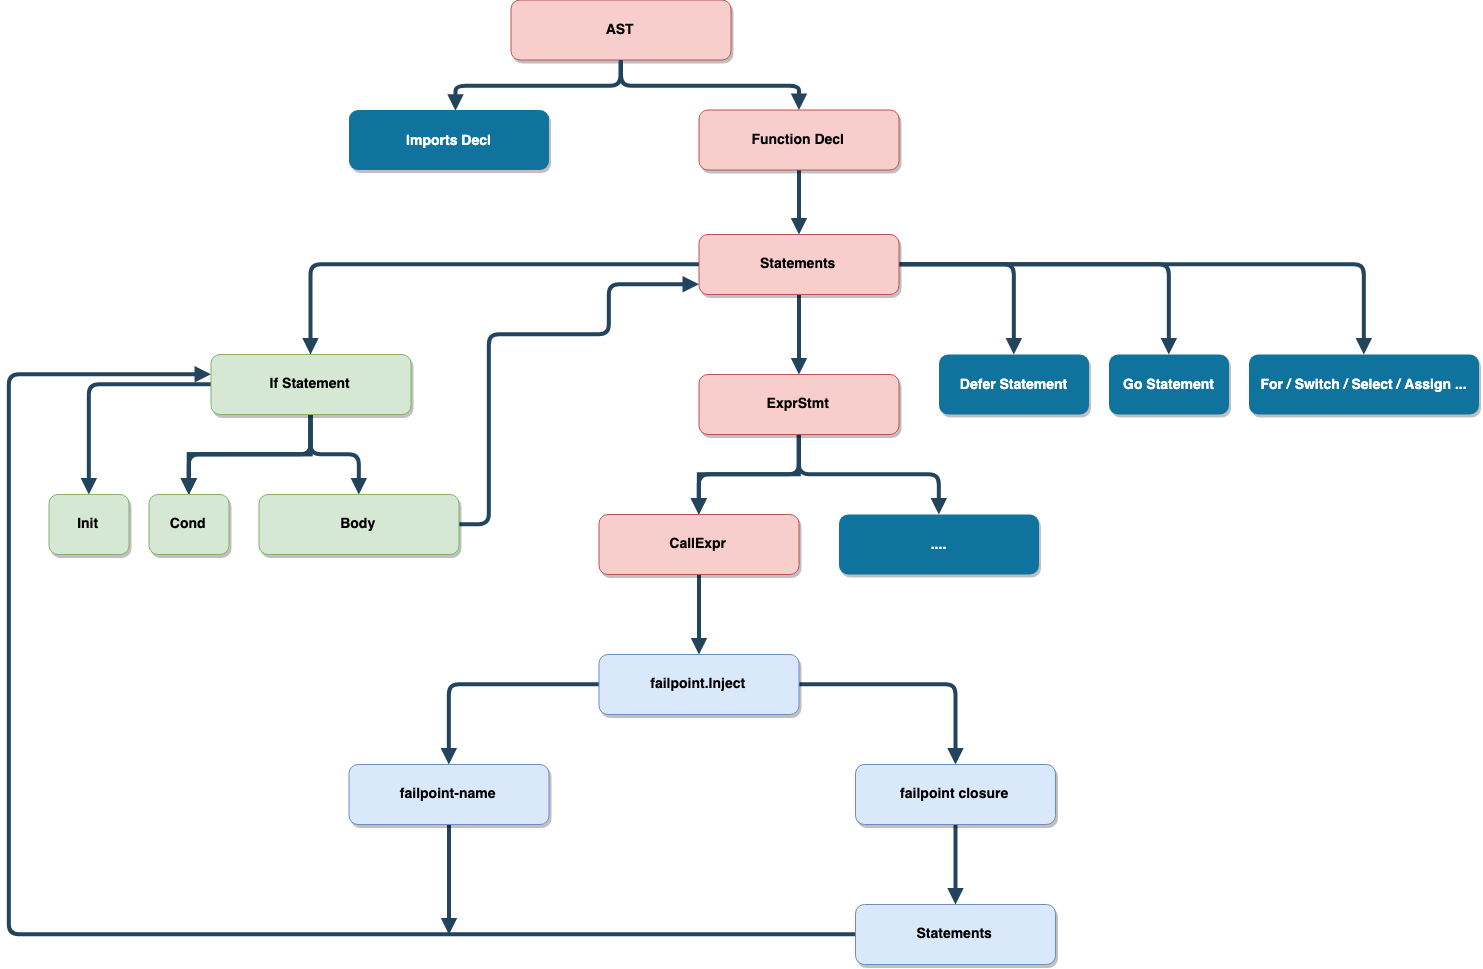
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
 biniamf/ai-reverse-engineering
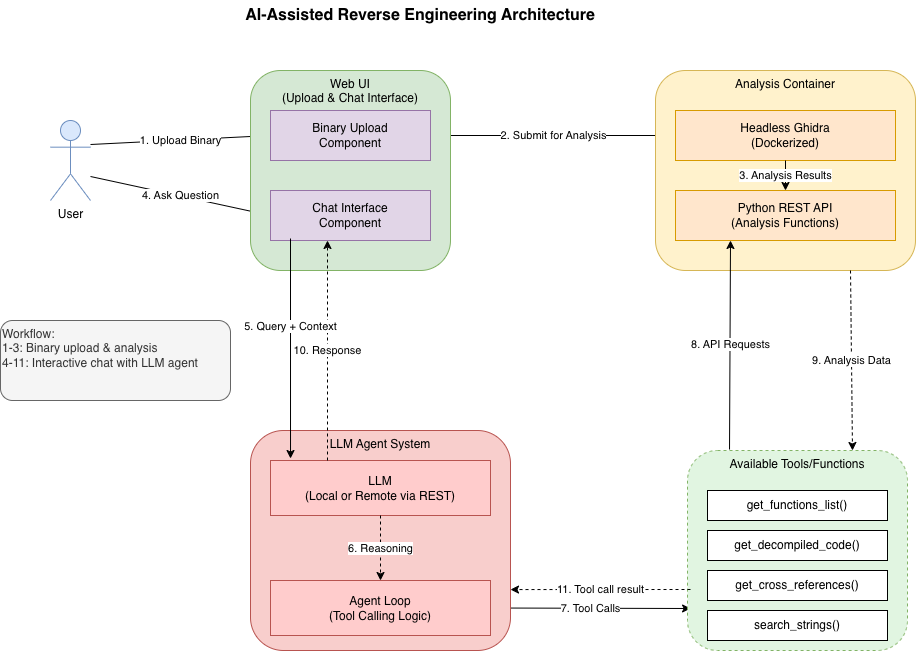
AI-Assisted Reverse Engineering with Ghidra
 thalium/icebox
Virtual Machine Introspection, Tracing & Debugging
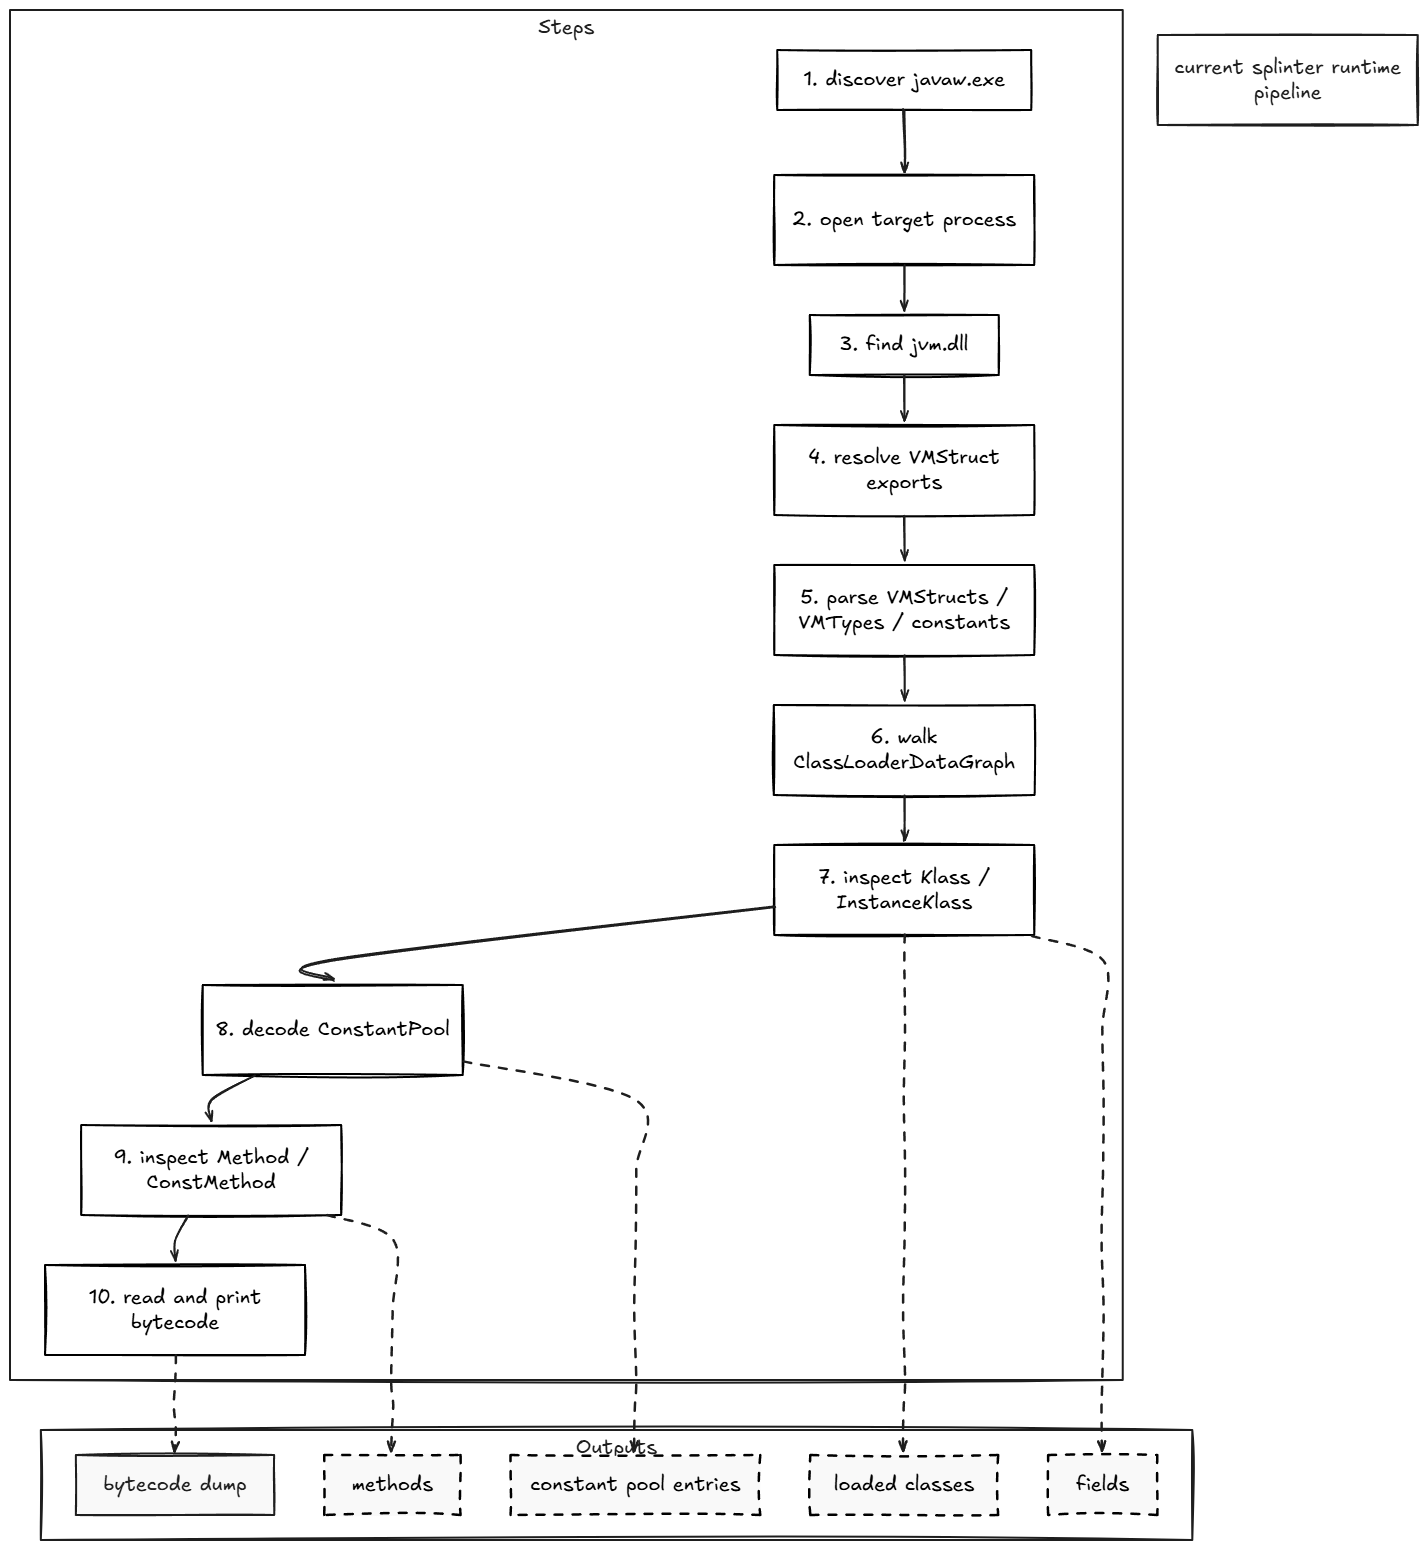 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 hugsy/recon_2024_windbg_workshop
Workshop materials for mastering WinDbg debugging in kernel and user mode, with KdNet setup, demos, and a Time Travel Debugging challenge for binary…
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 trailofbits/manticoreui
The Manticore User Interface with plugins for Binary Ninja and Ghidra