lighthouse
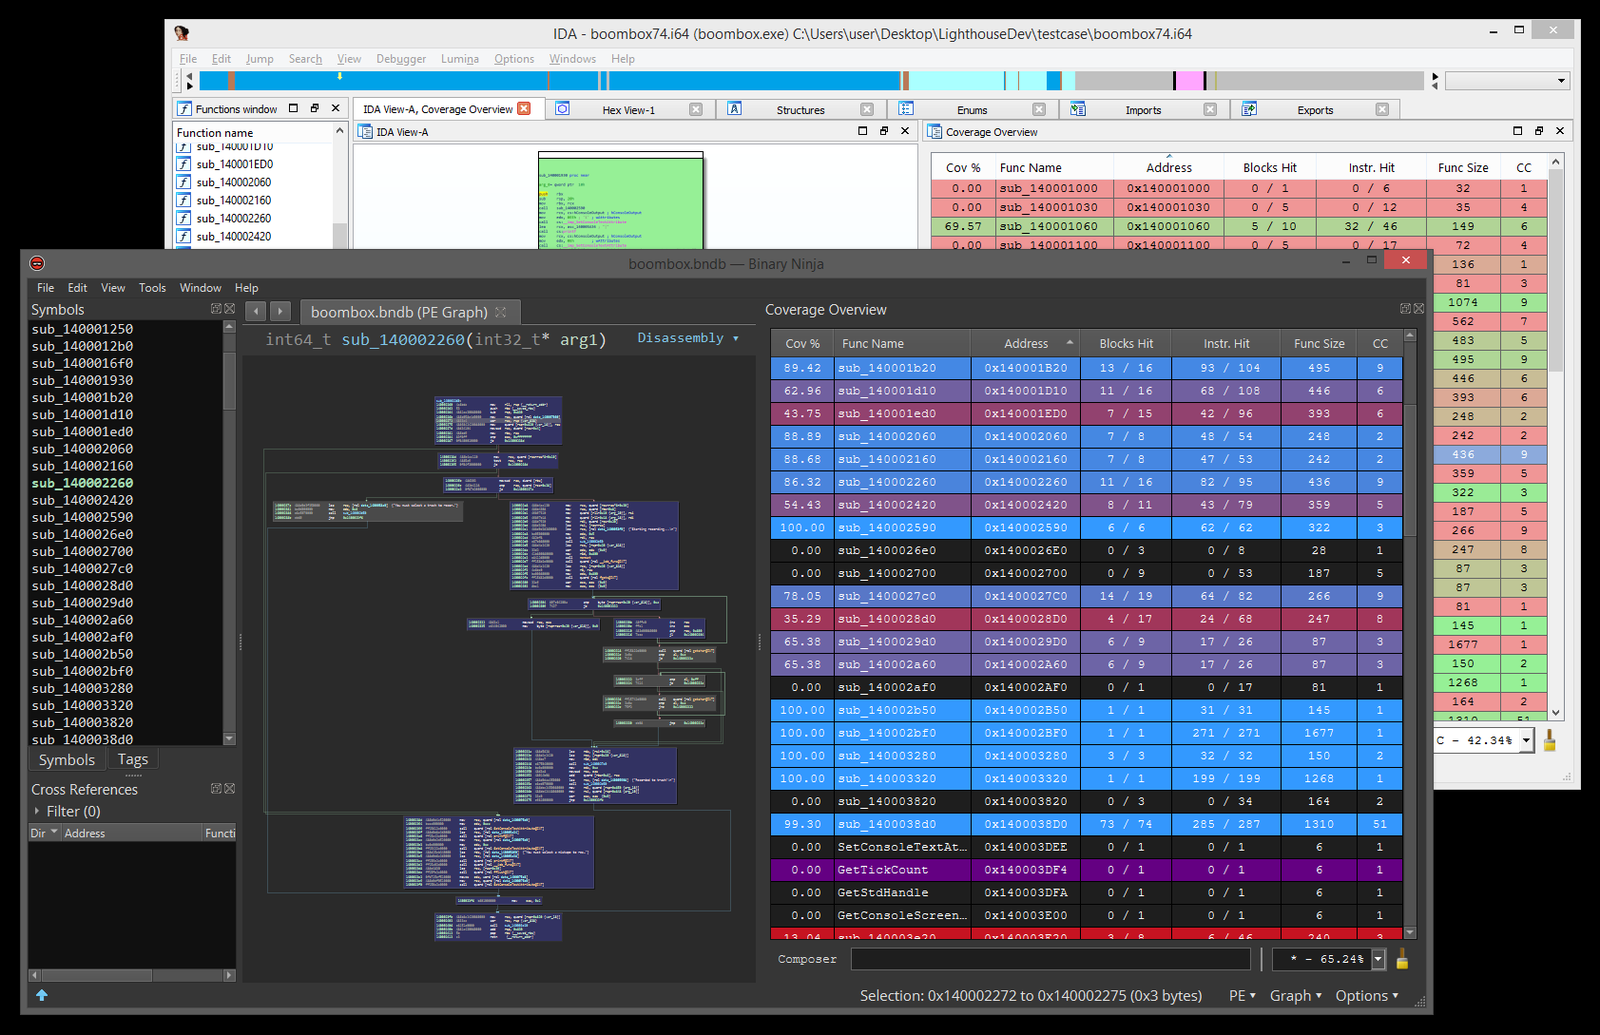
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
binary-analysiscode-analysisdebuggers+6
gaasedelen/lighthouseA Coverage Explorer for Reverse Engineers
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
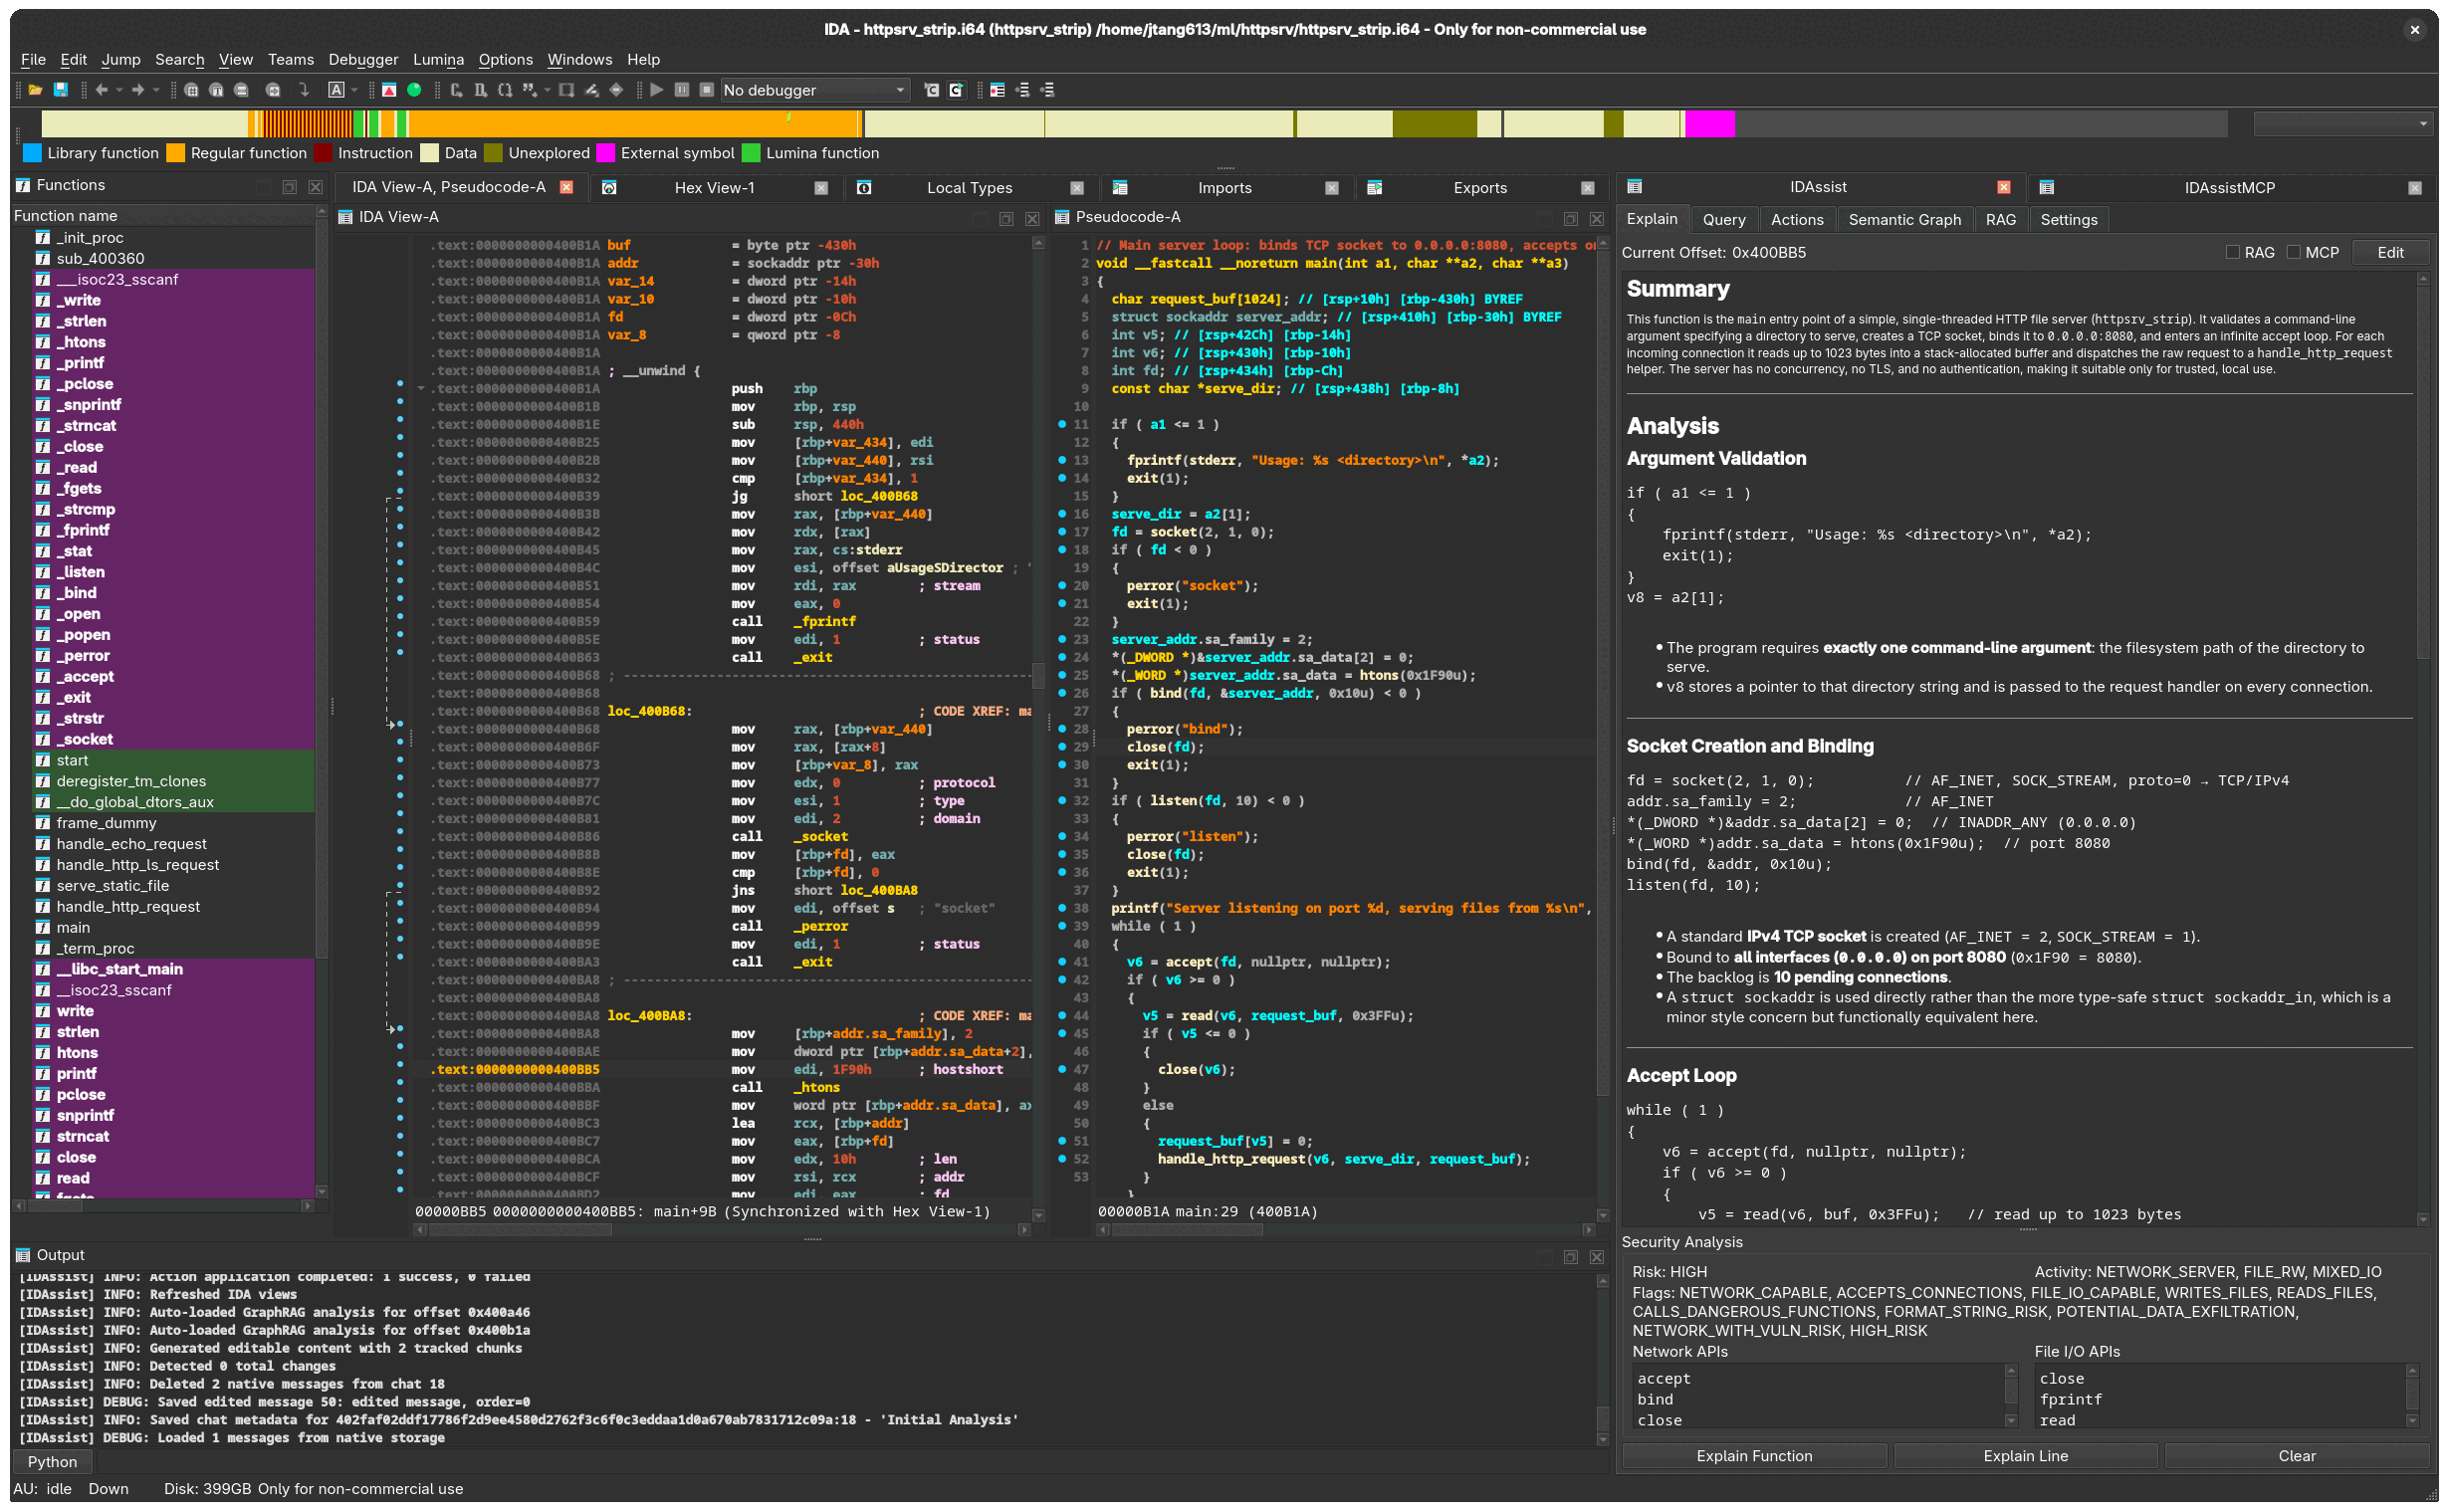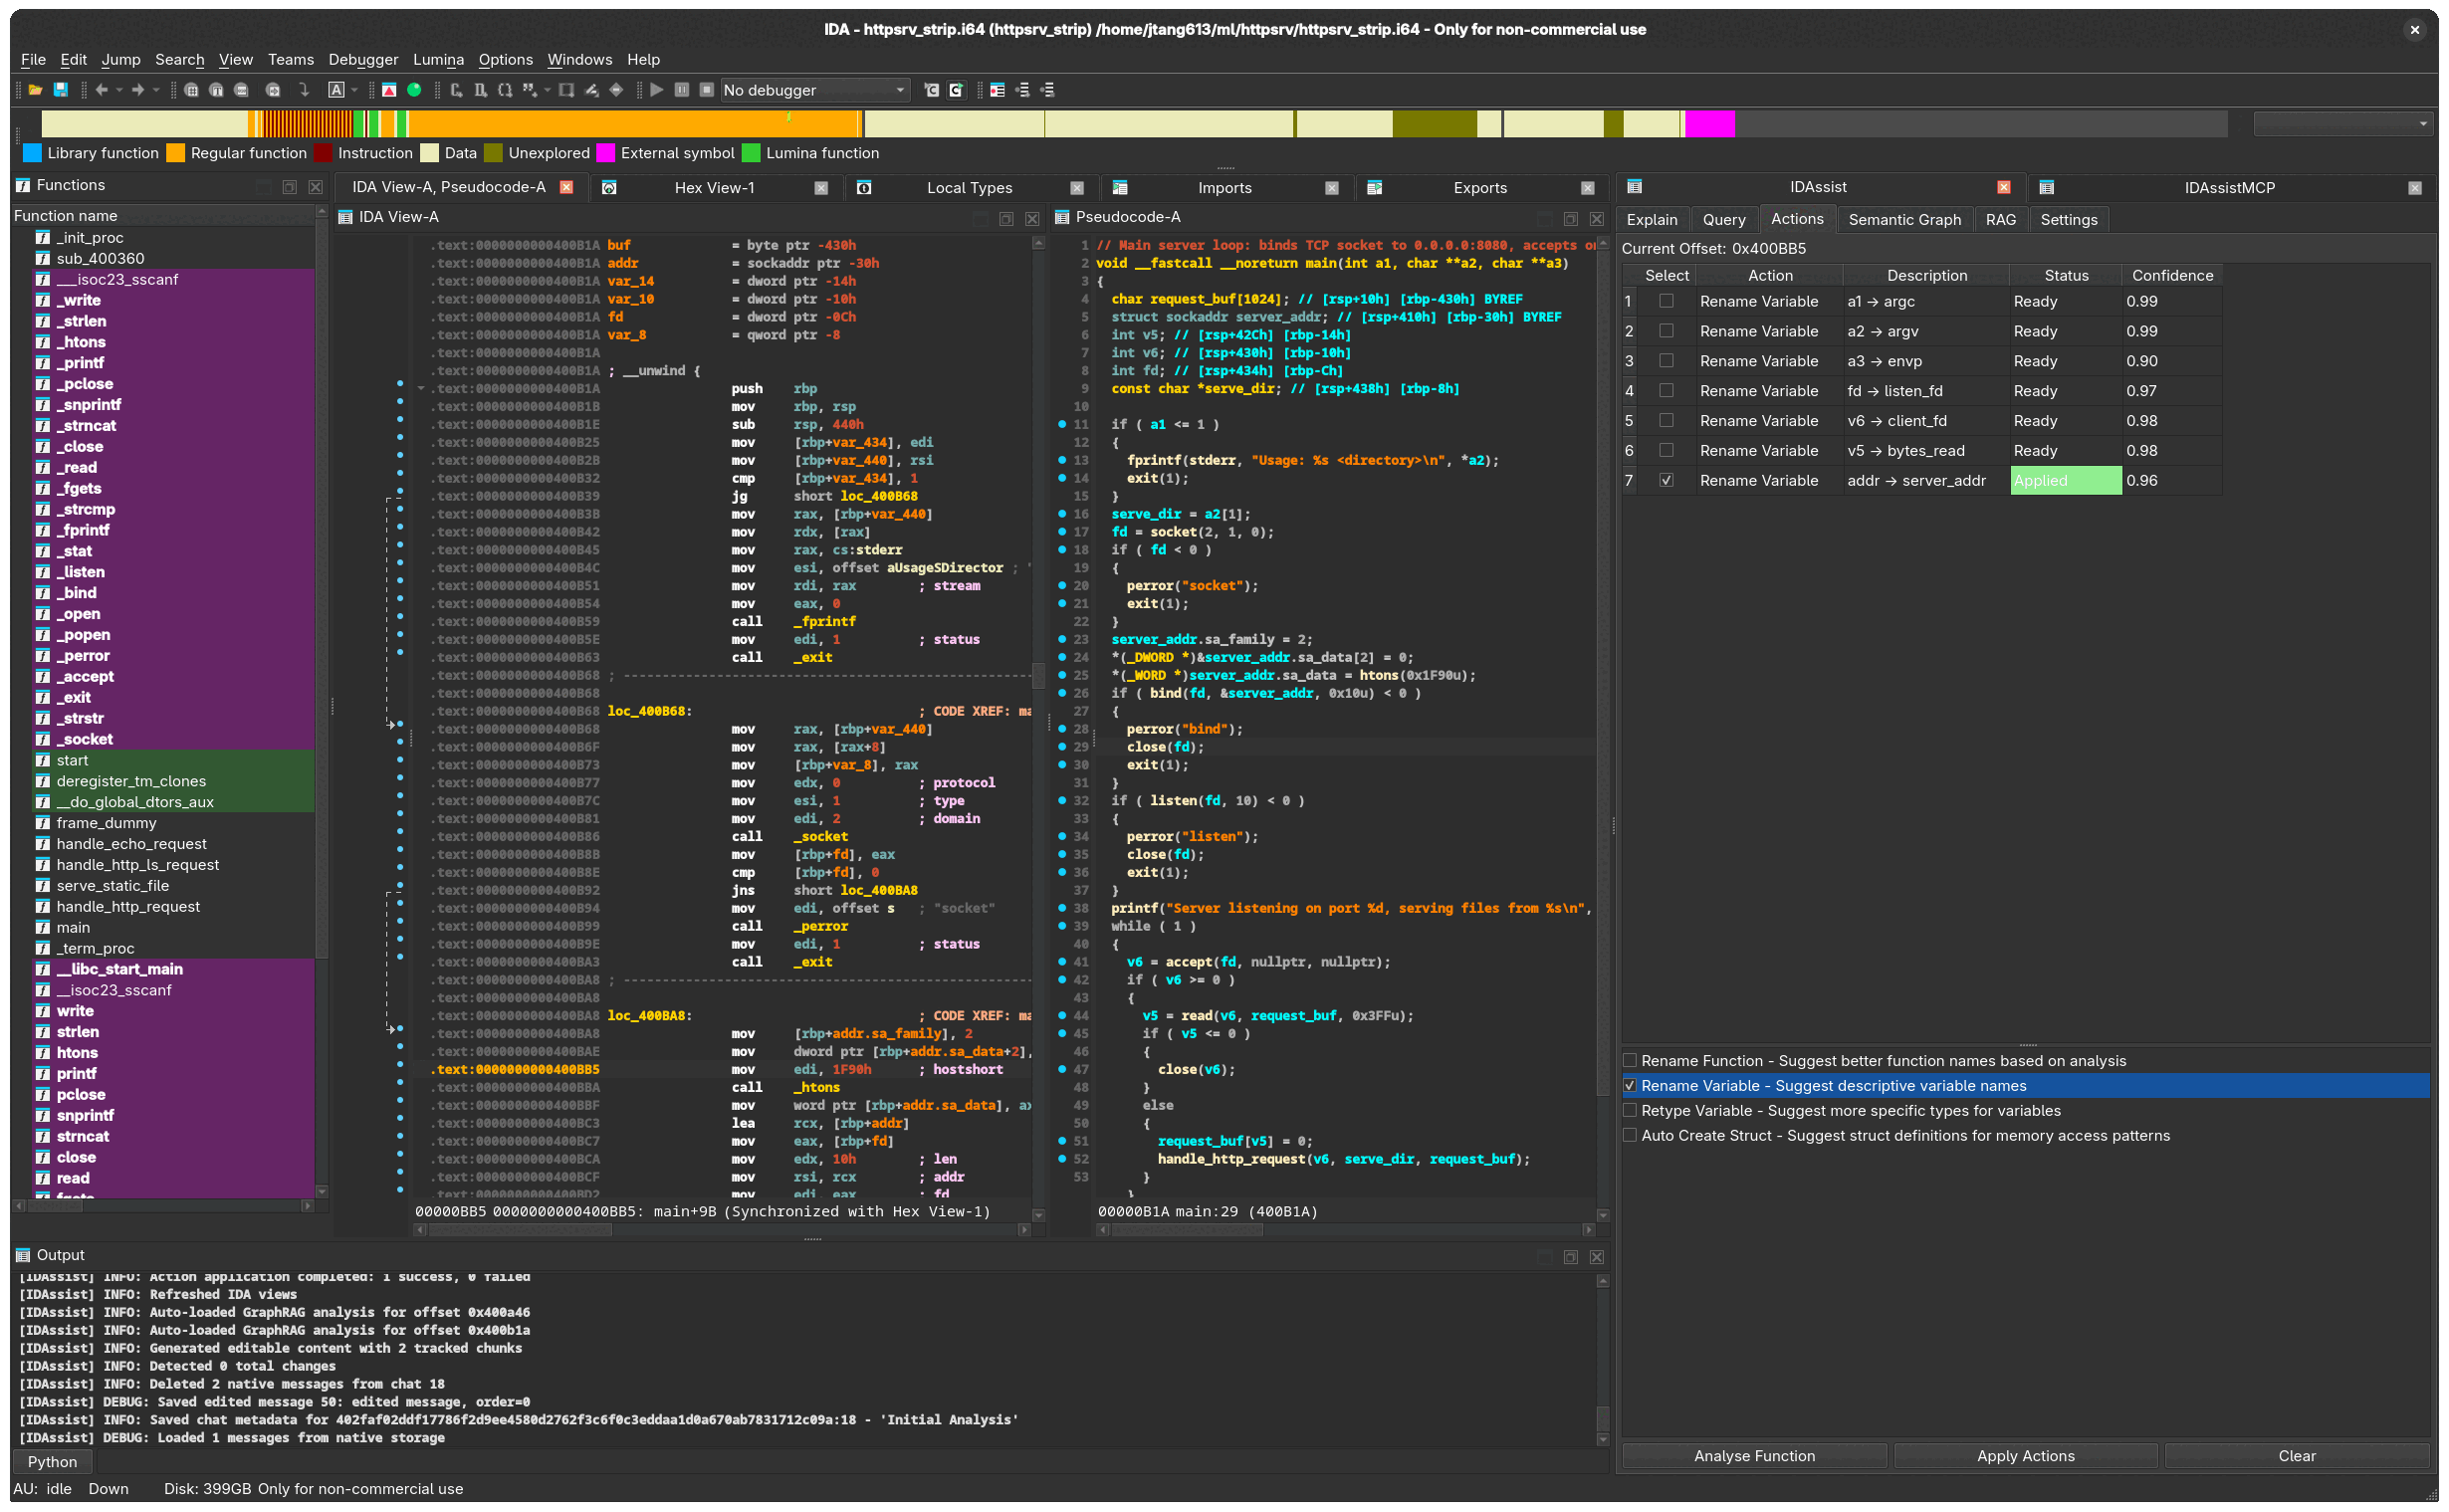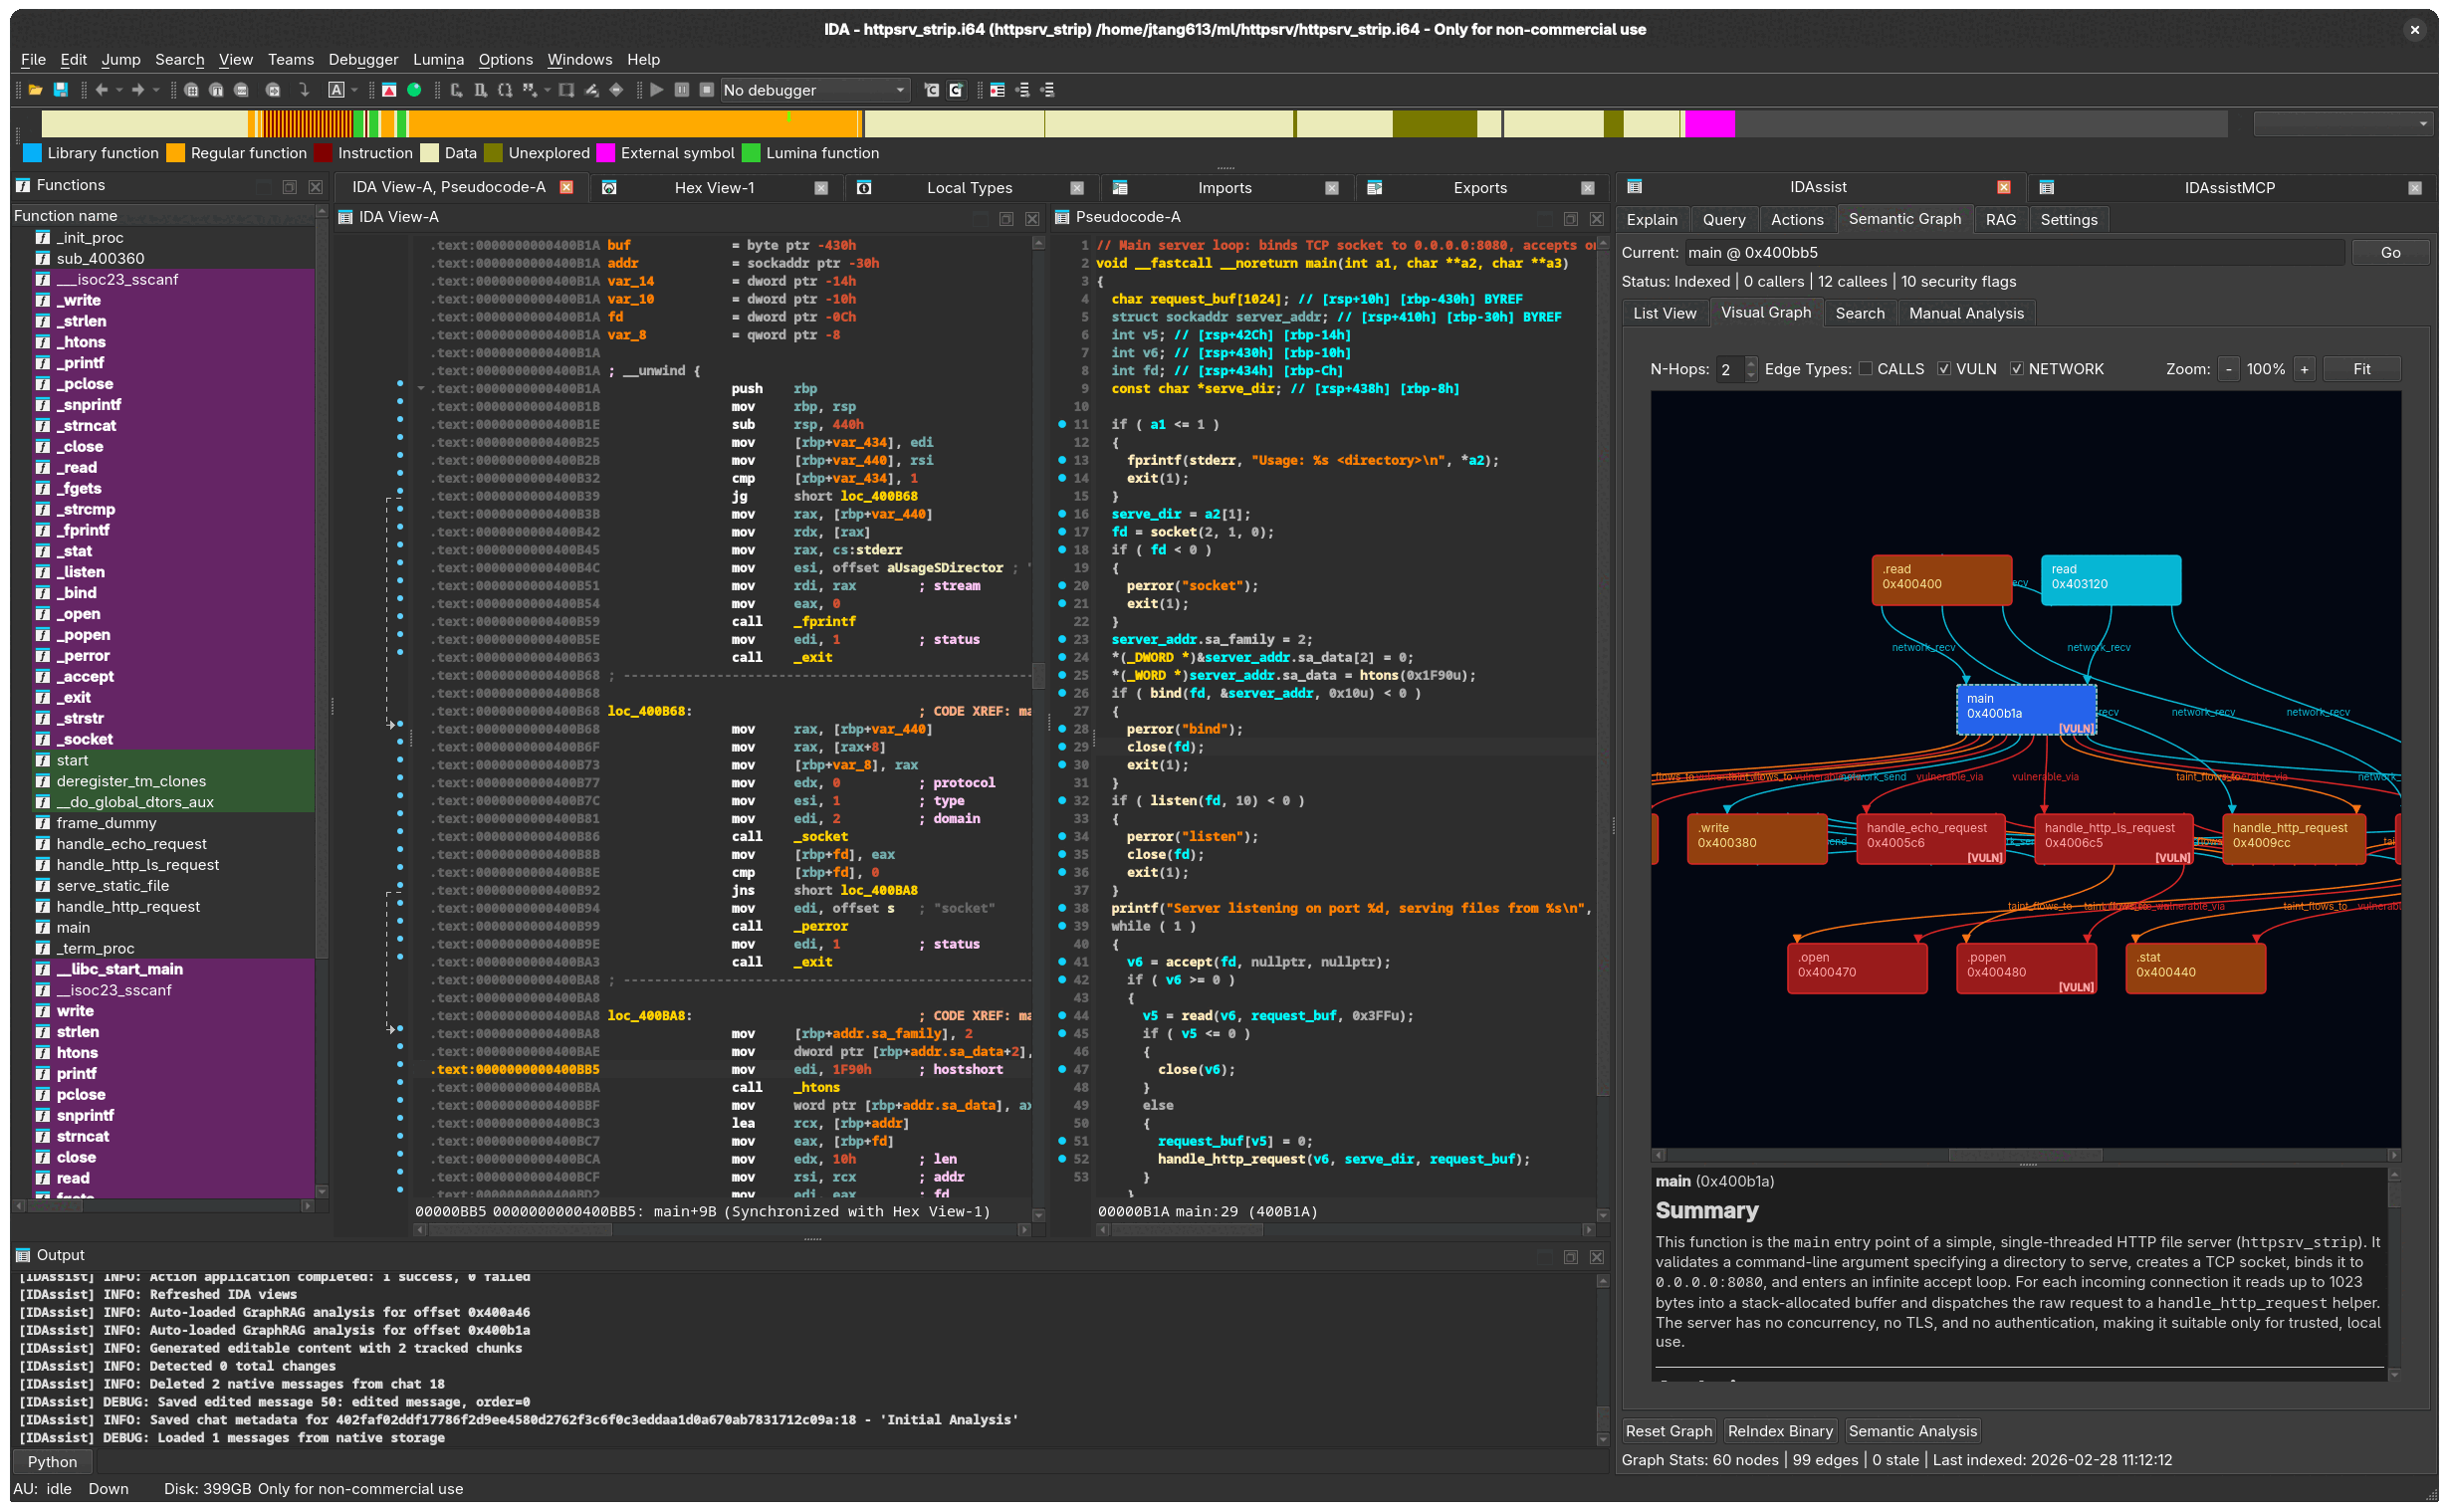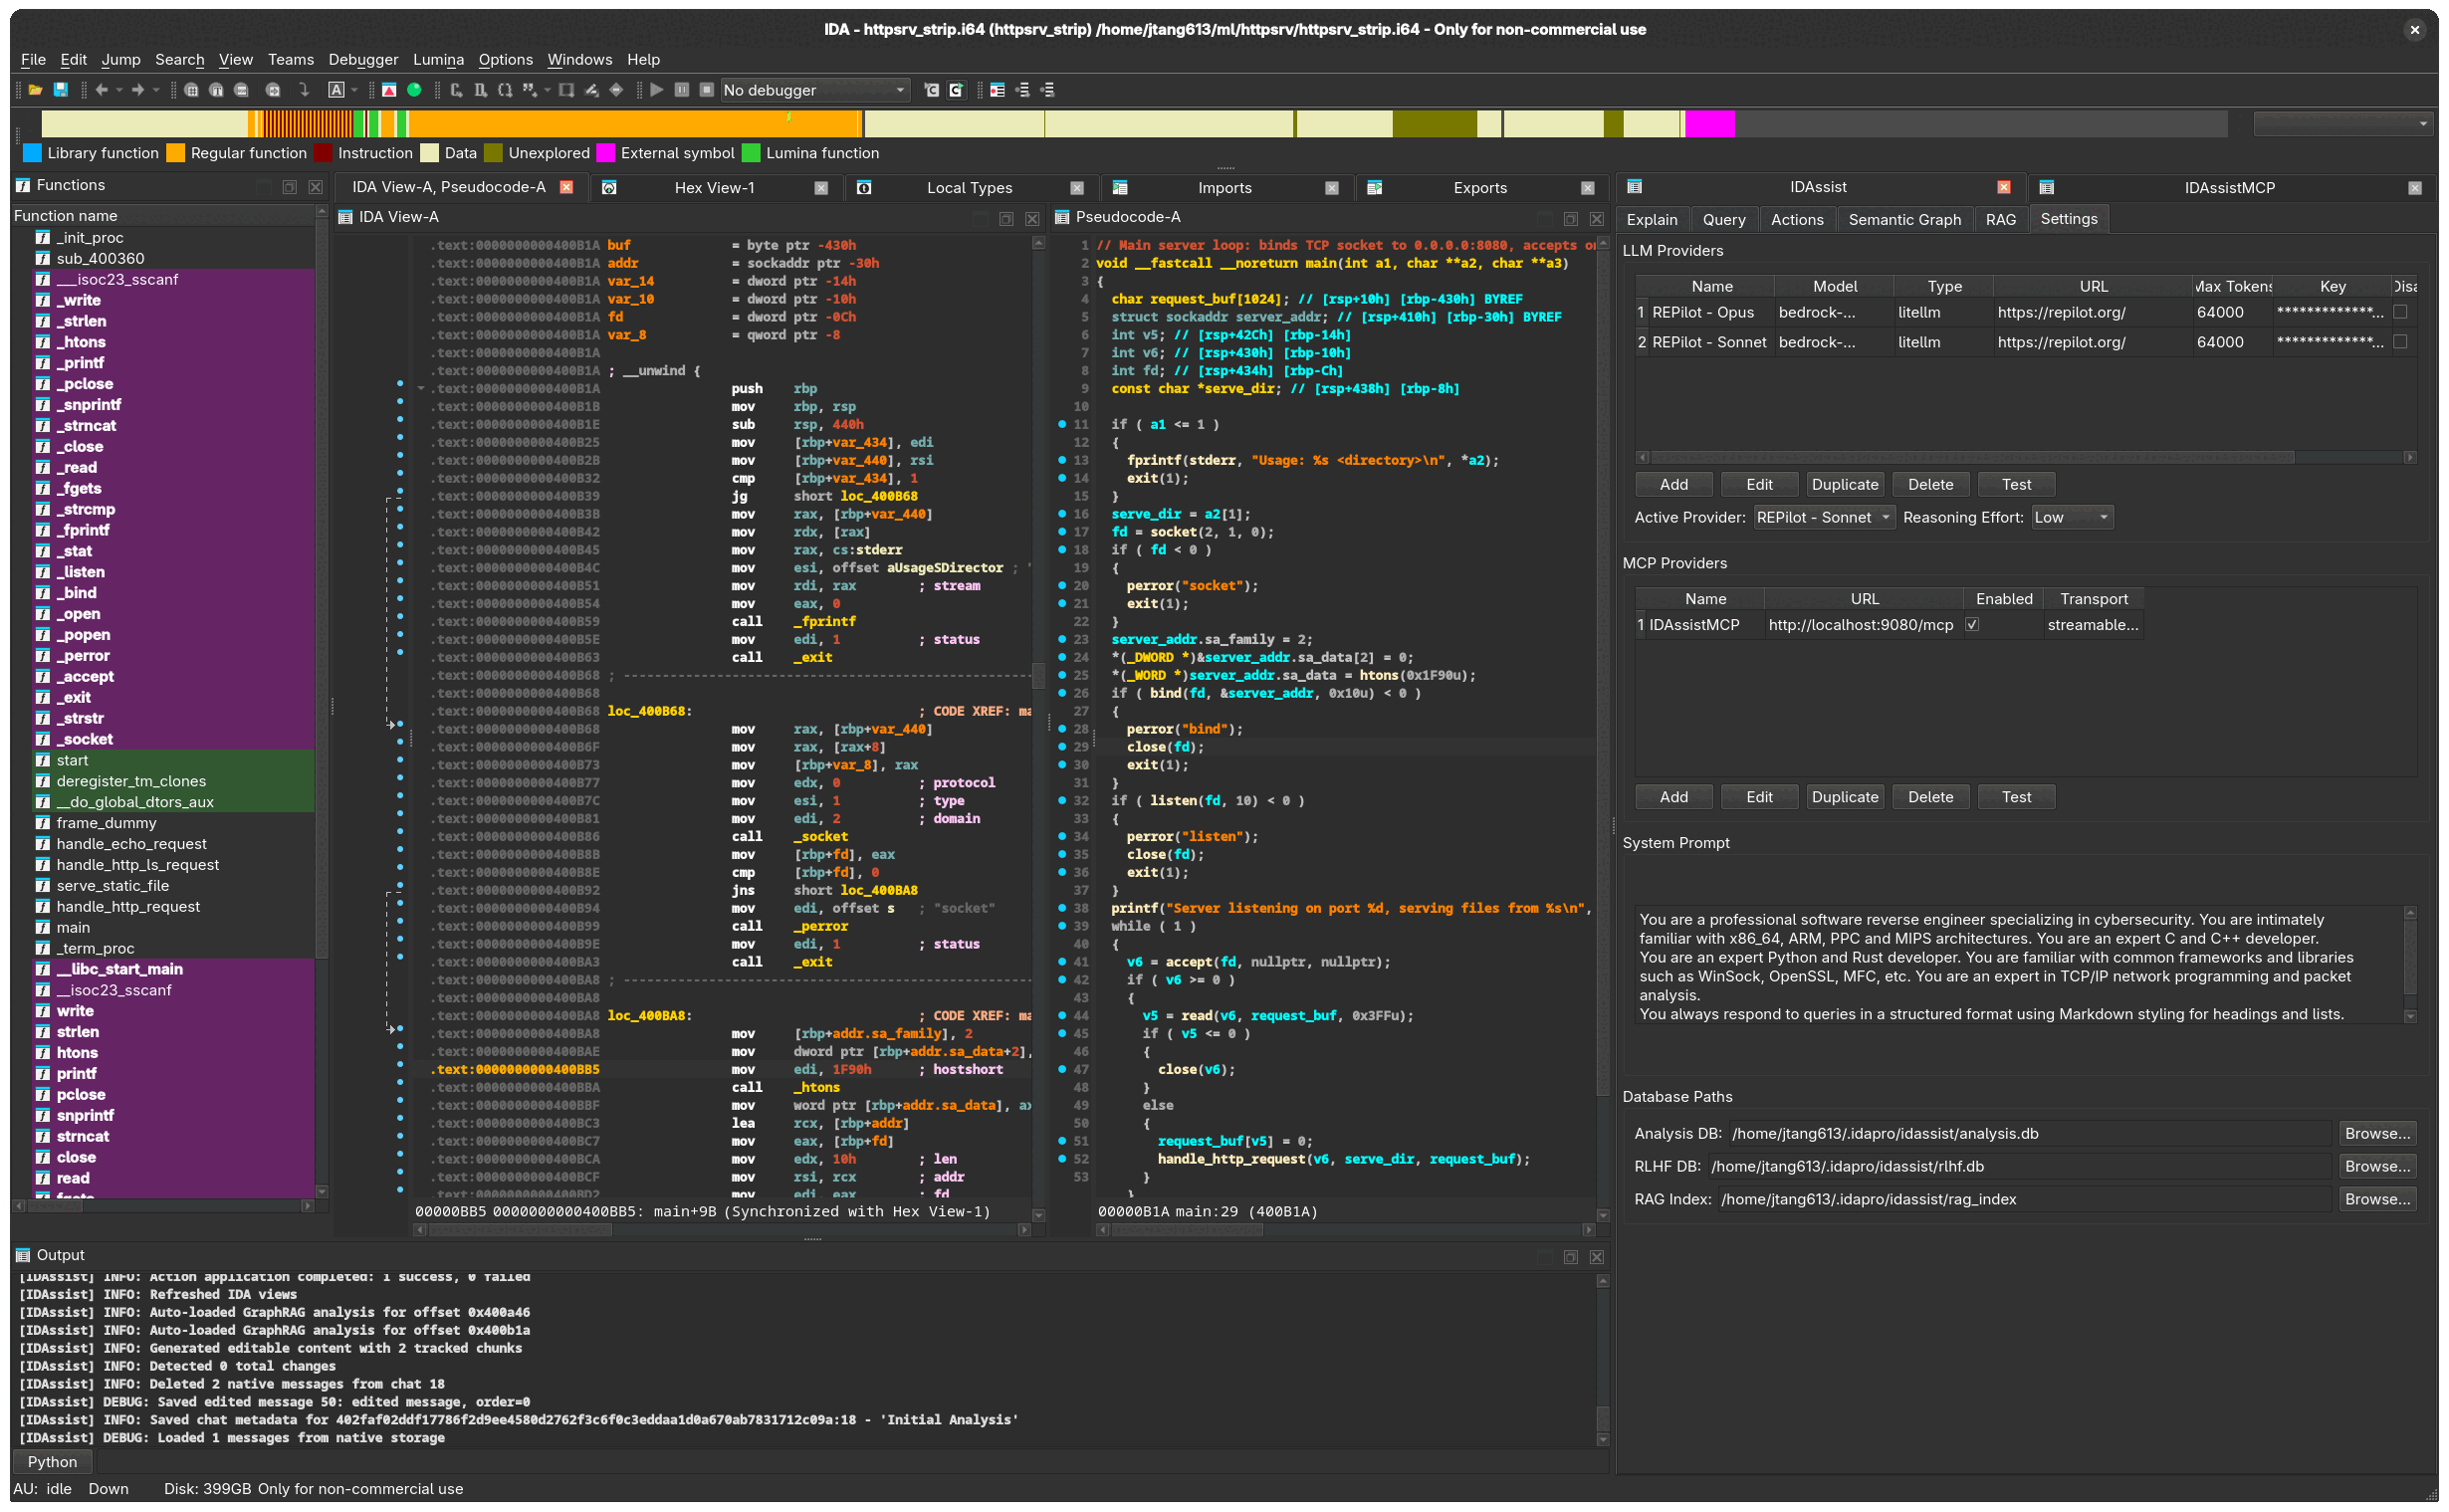 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
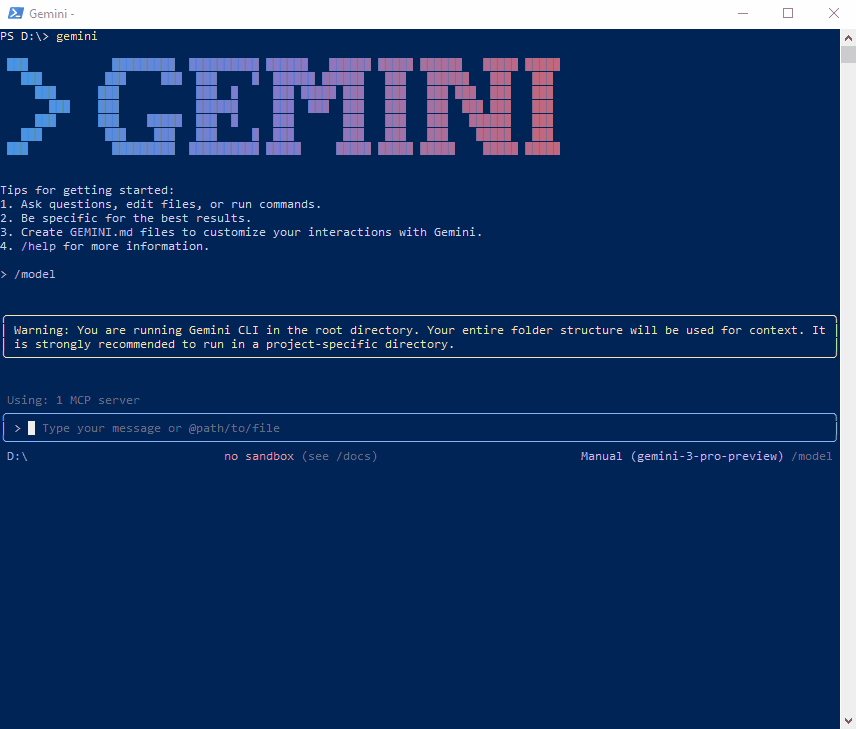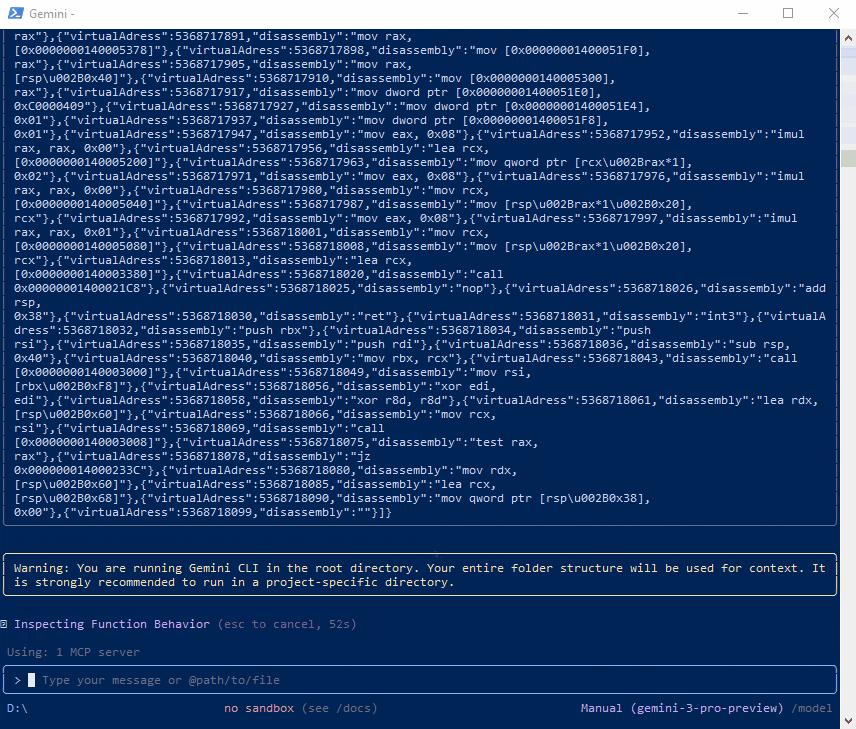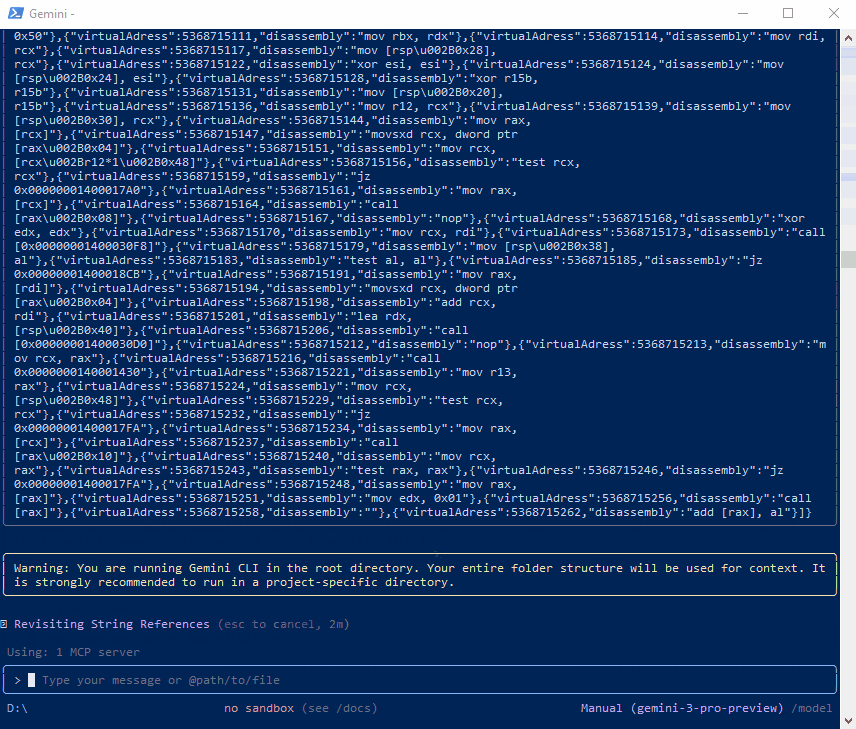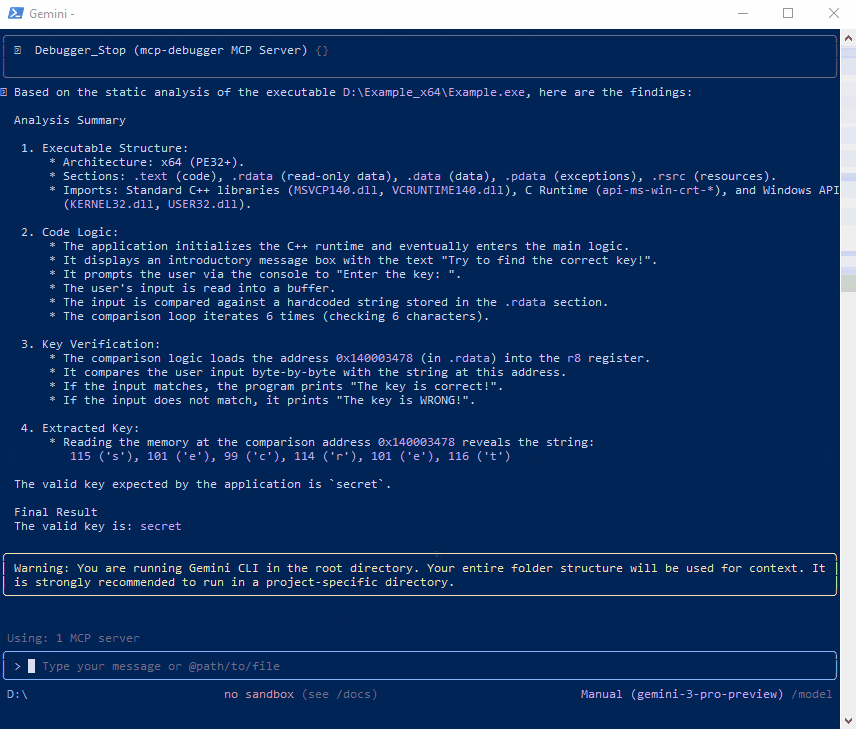 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
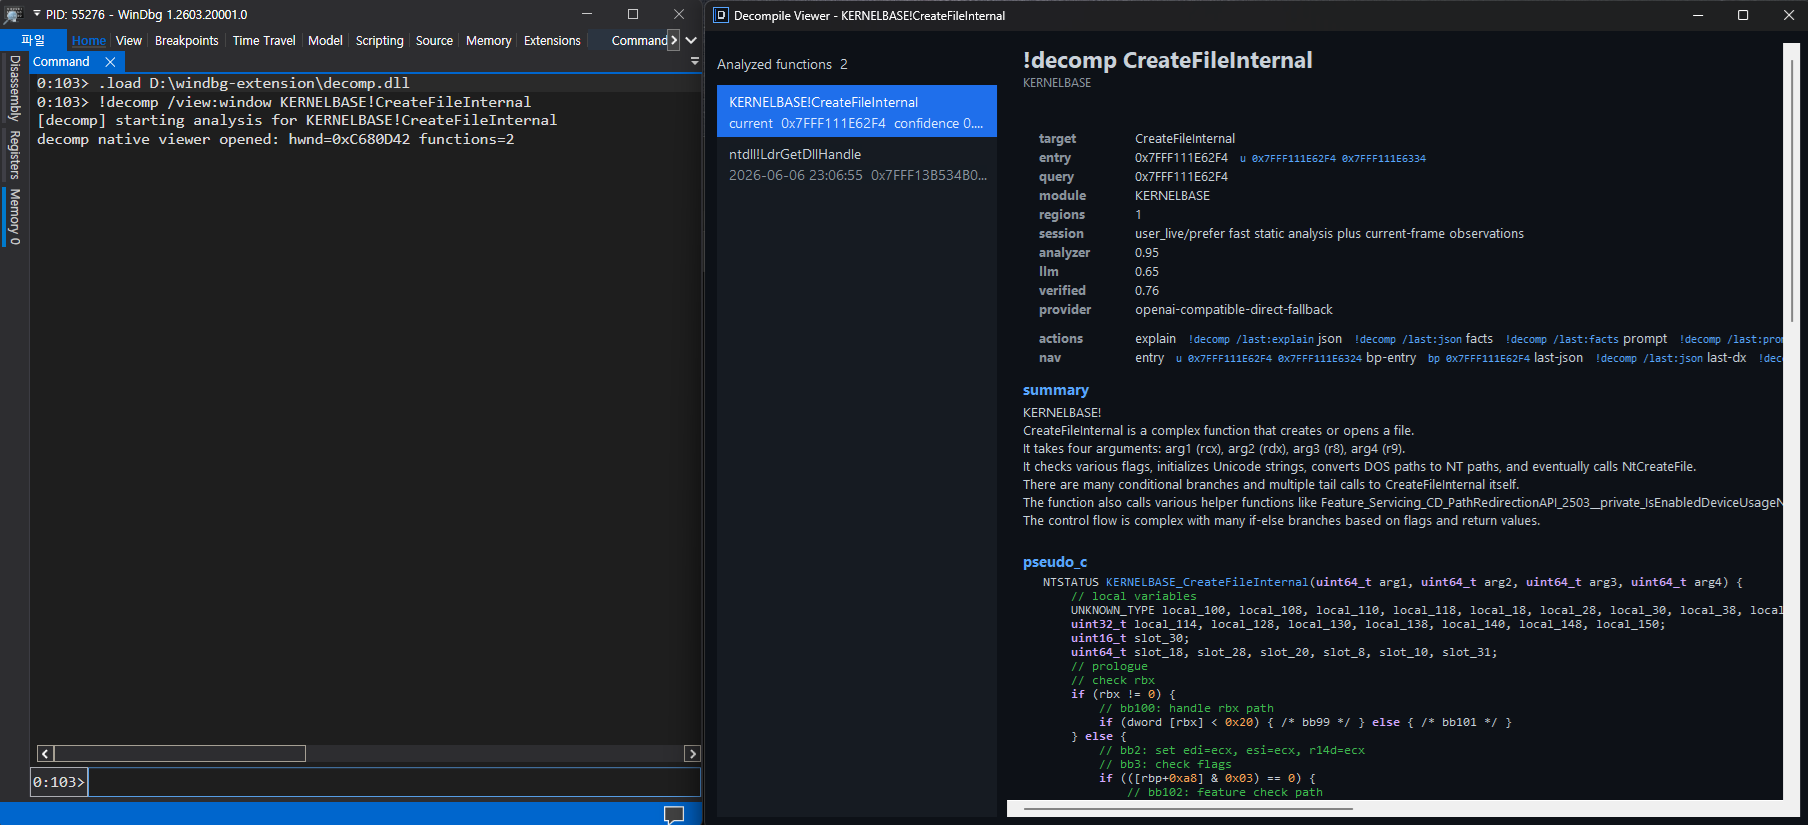 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
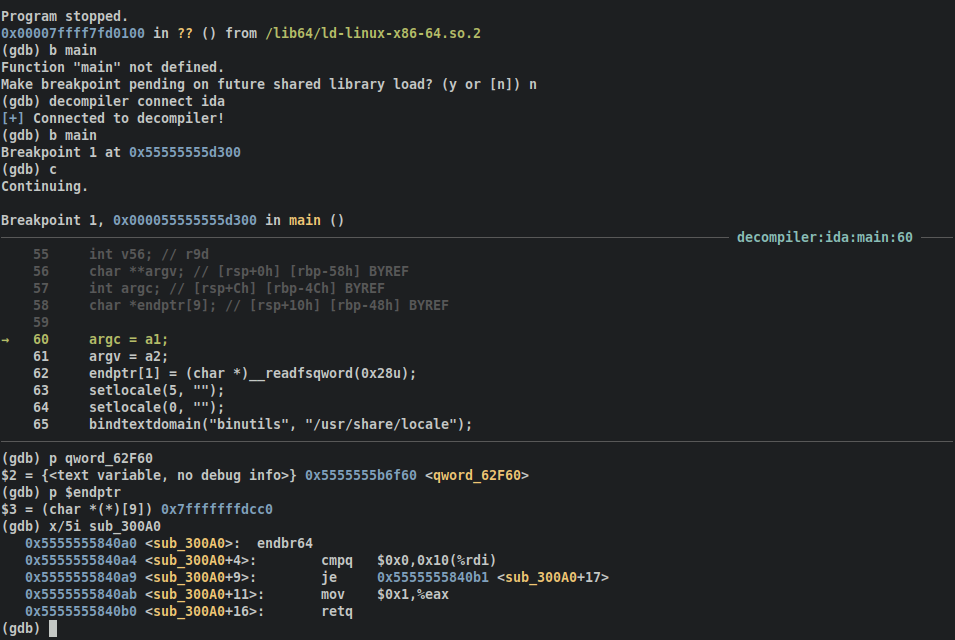 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…