
ptrace
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
binary-analysisdebuggersdynamic-code-analysis+2
whatswrongandwhy/ptraceLinux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
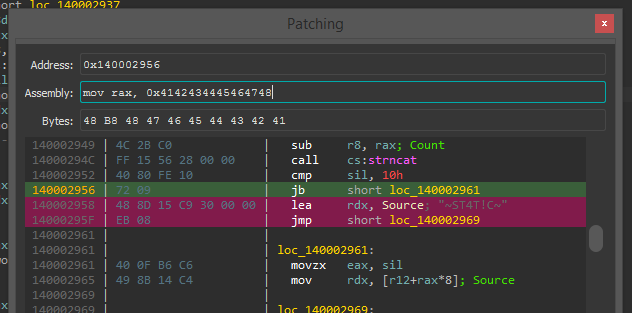 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
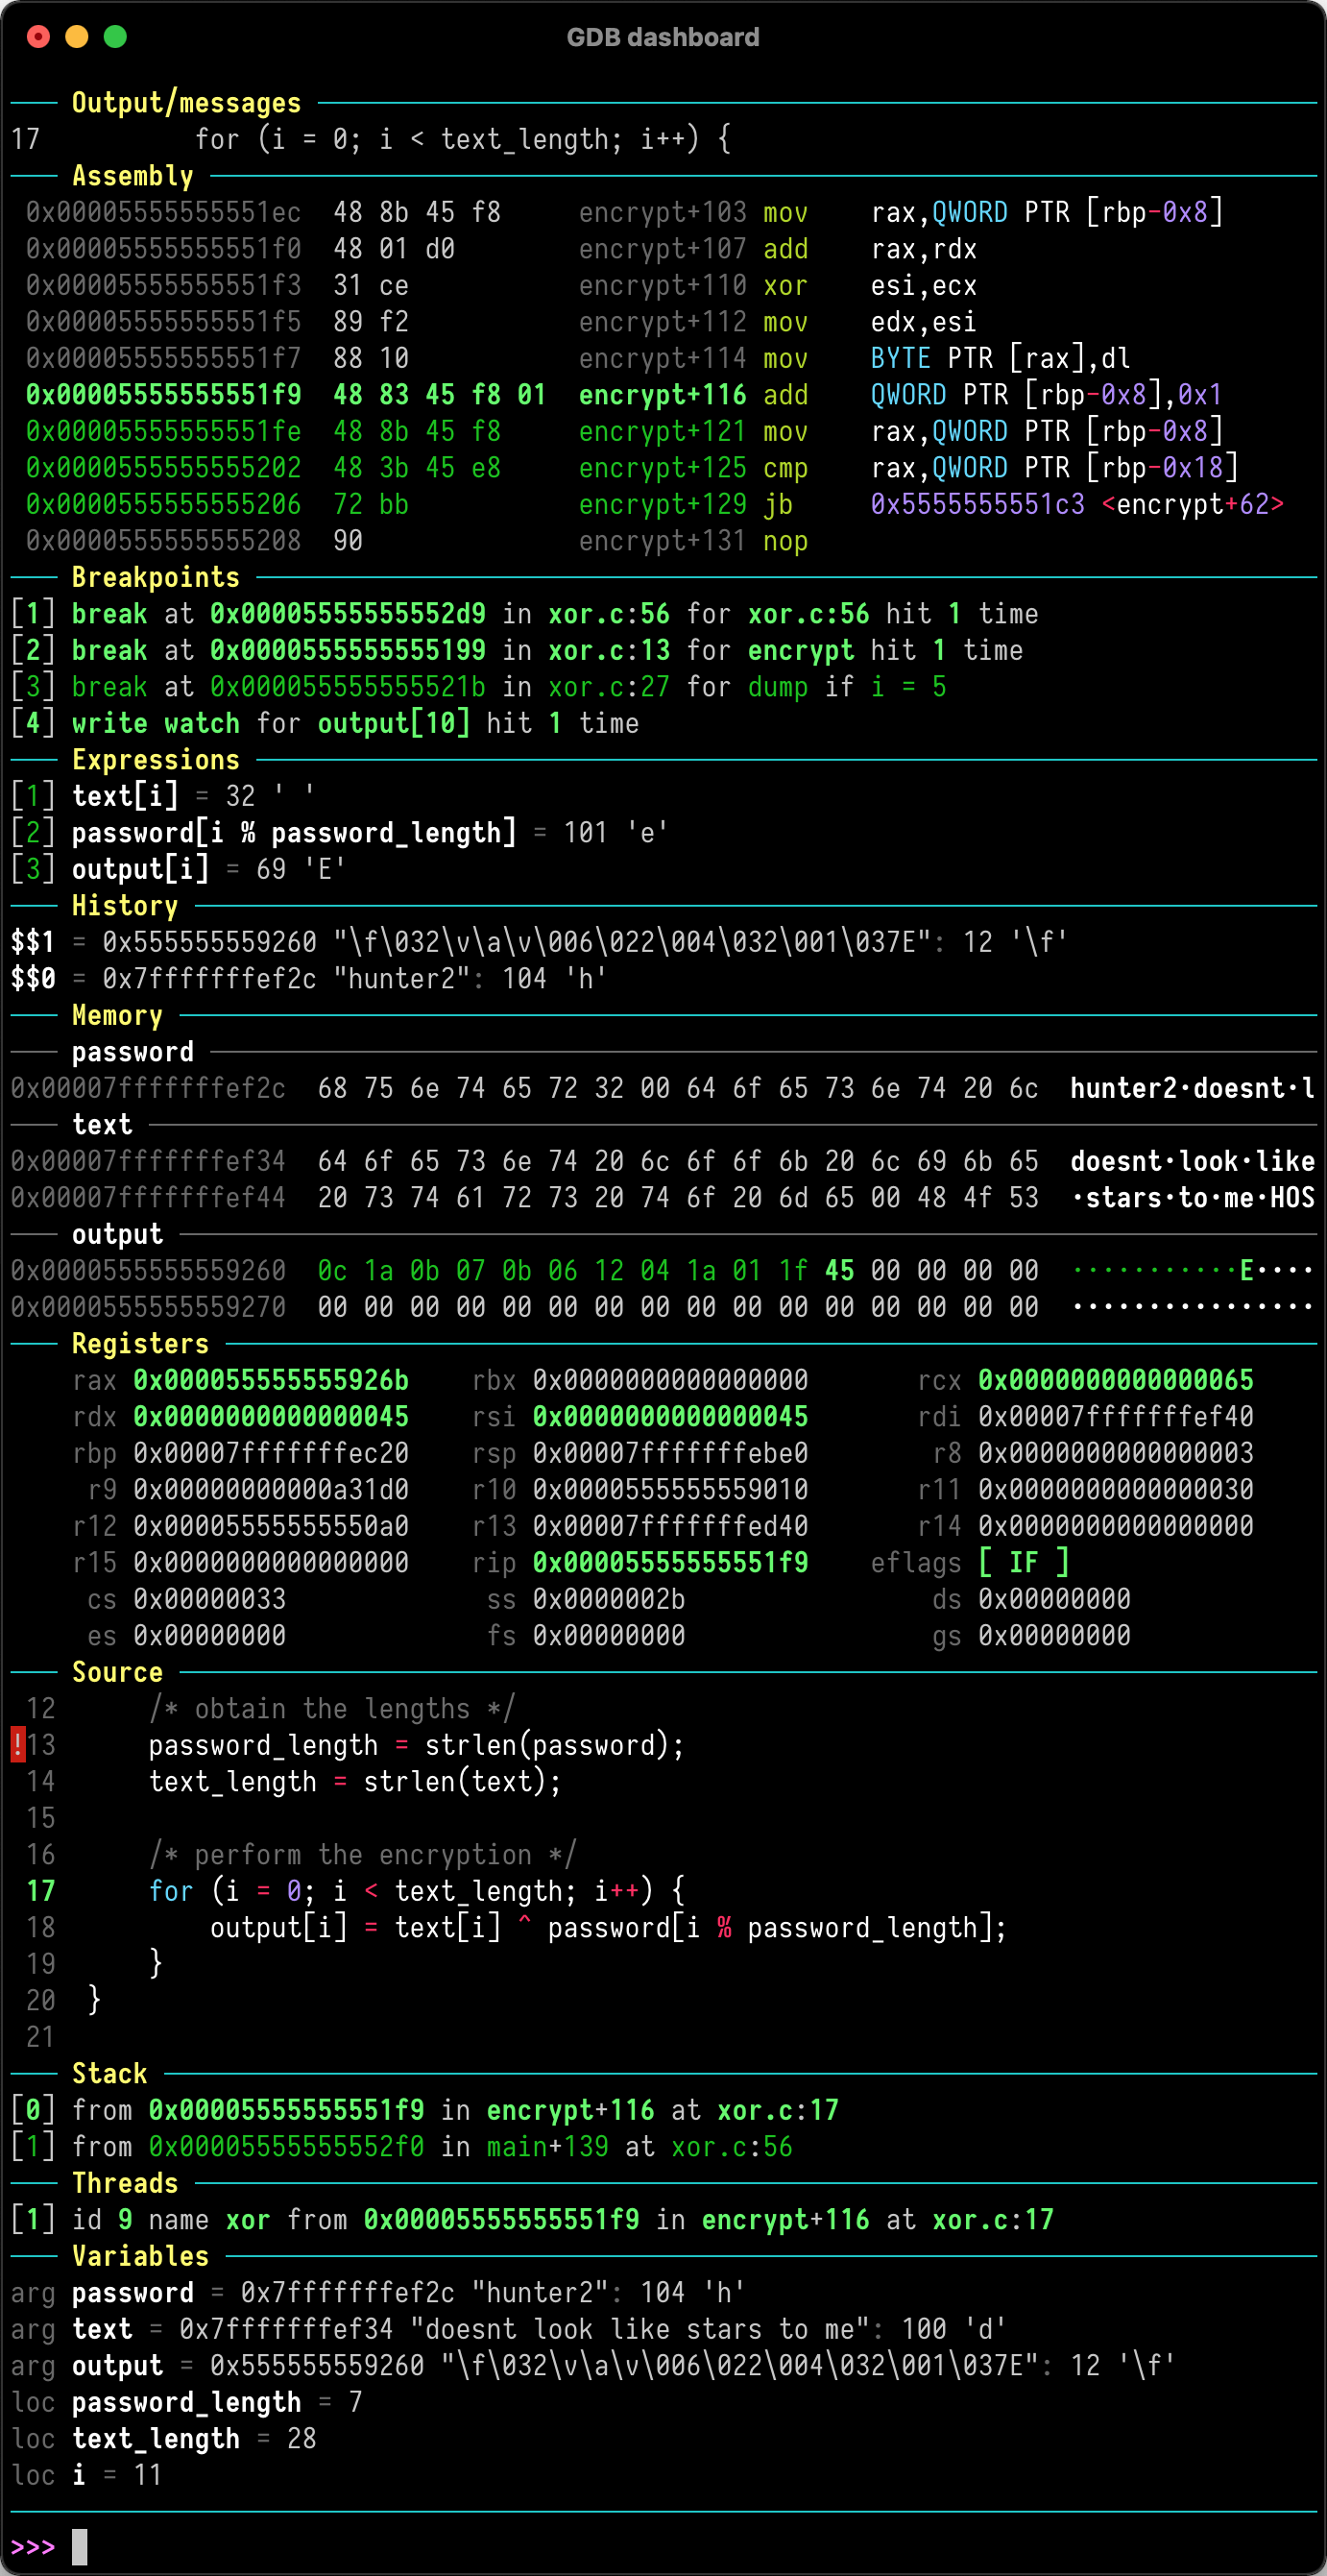 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
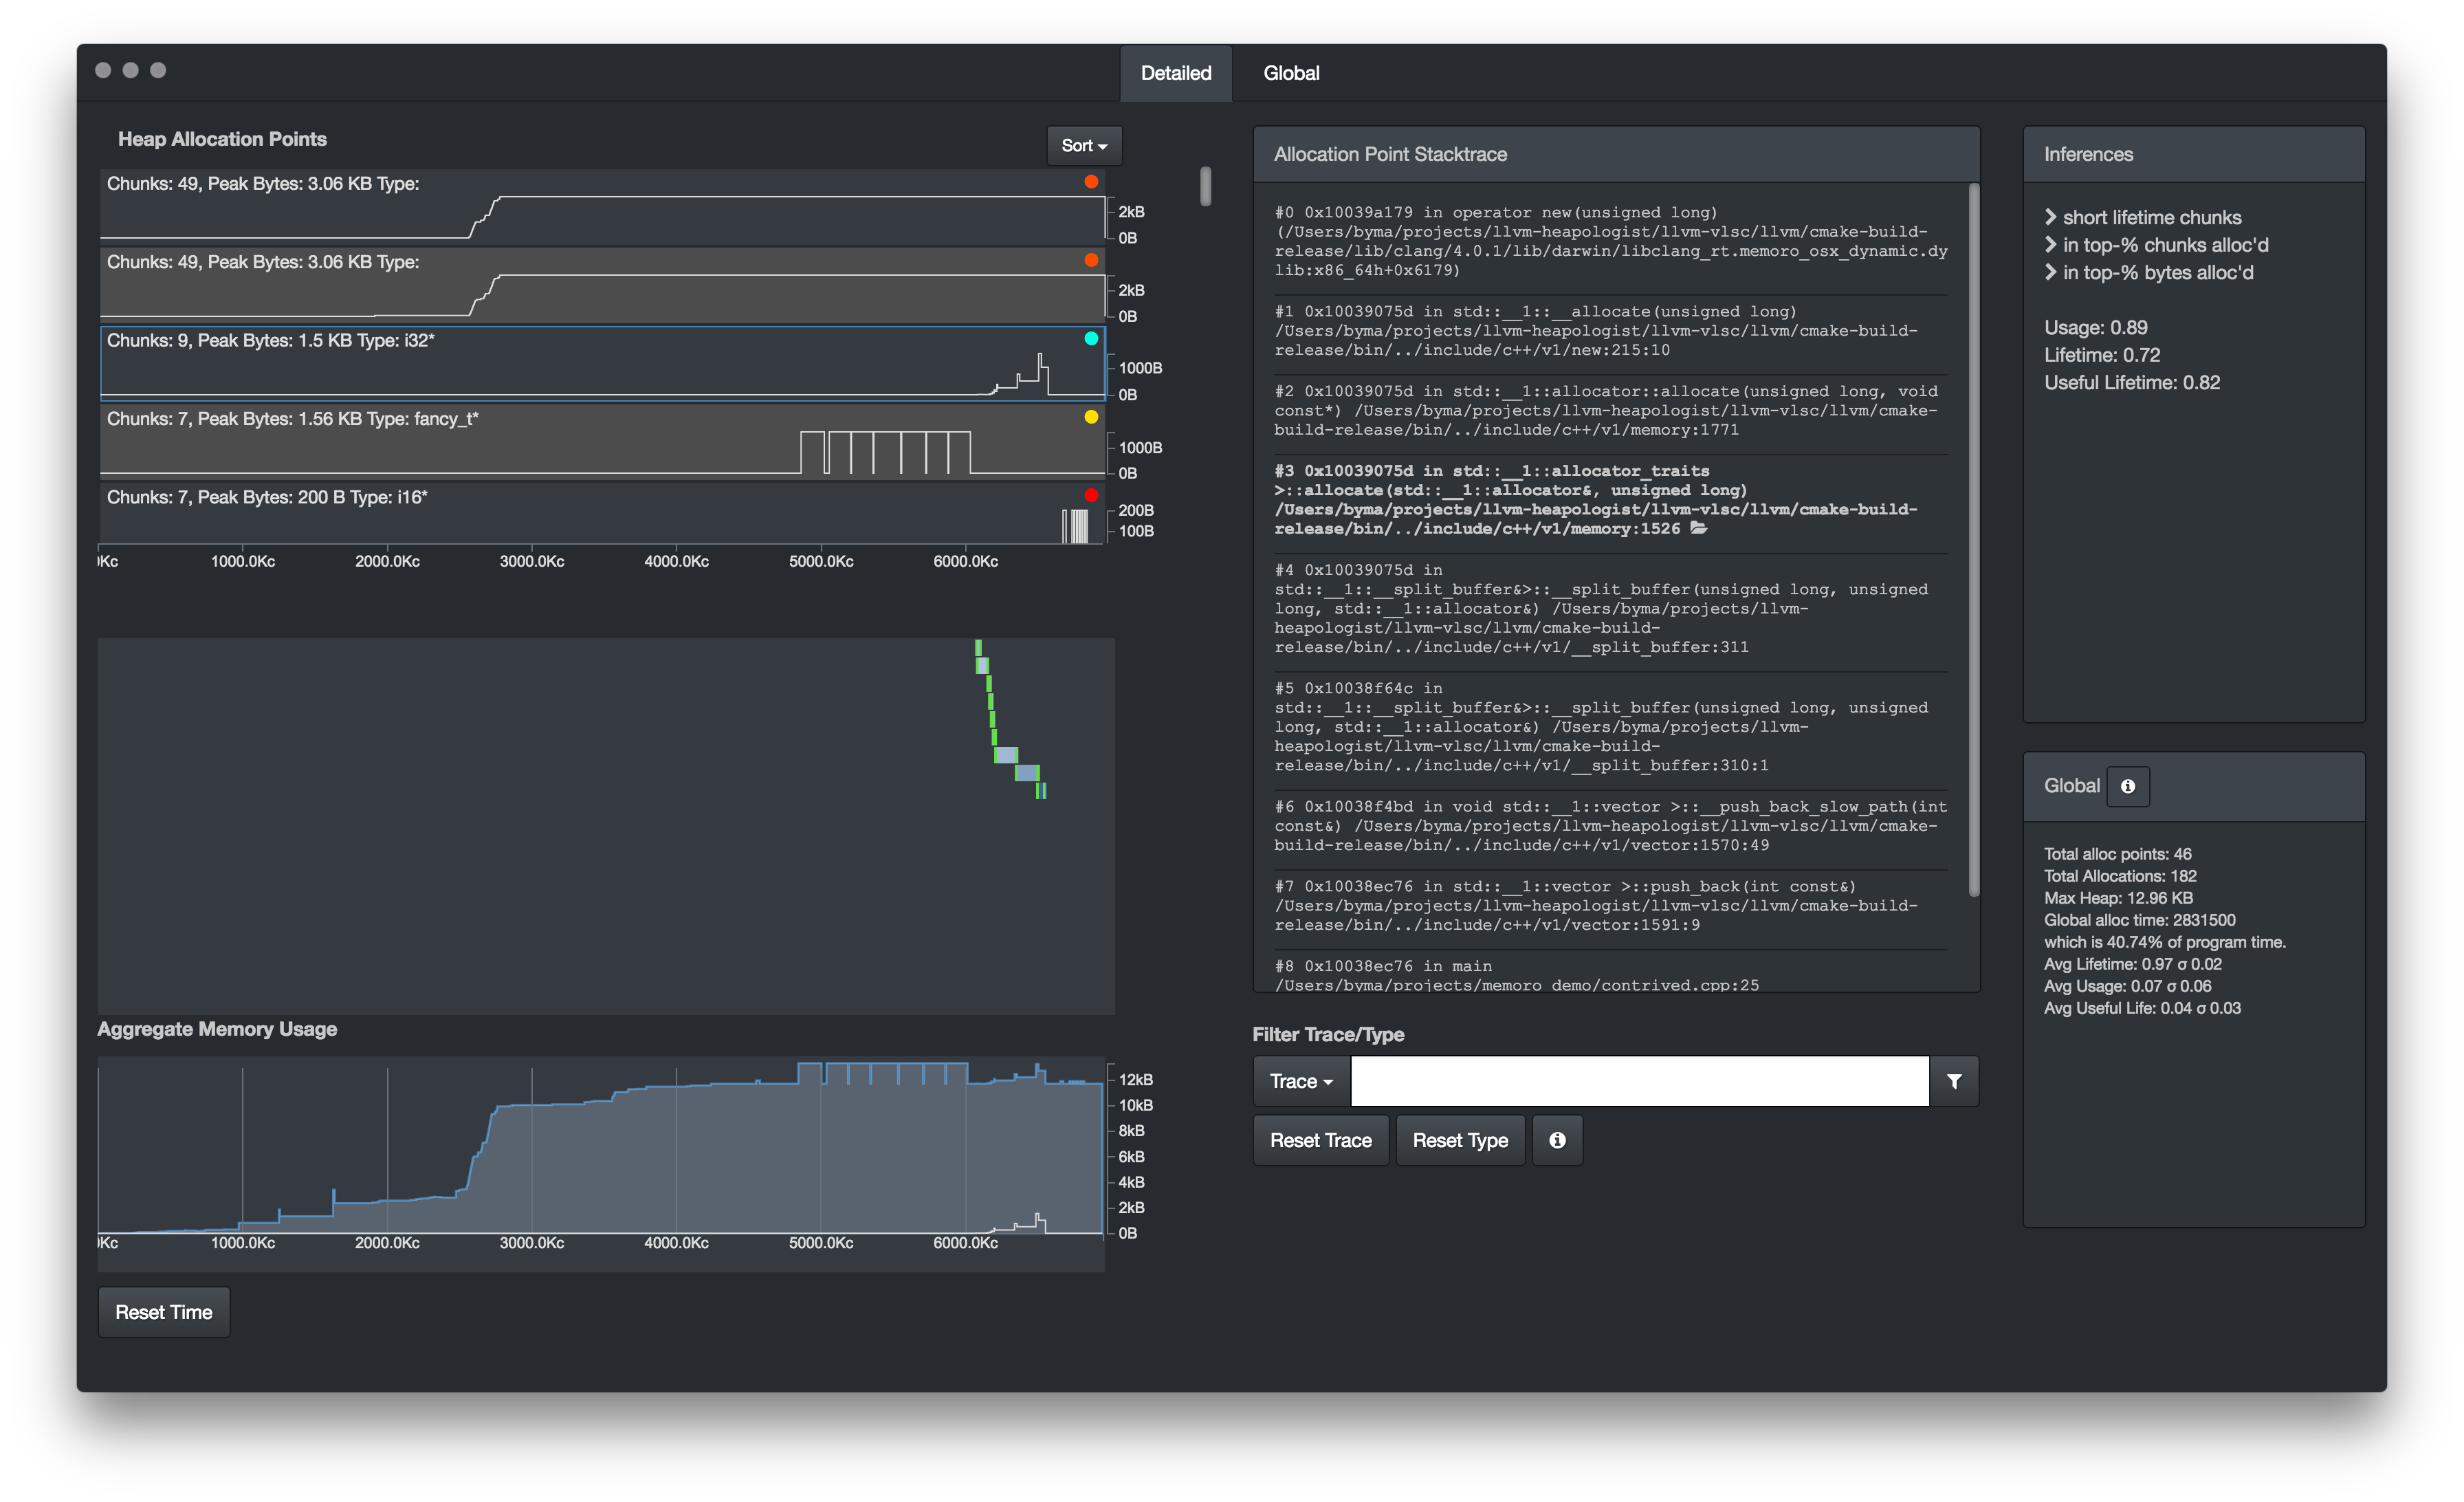 epfl-vlsc/memoro
Memoro: A Detailed Heap Profiler
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
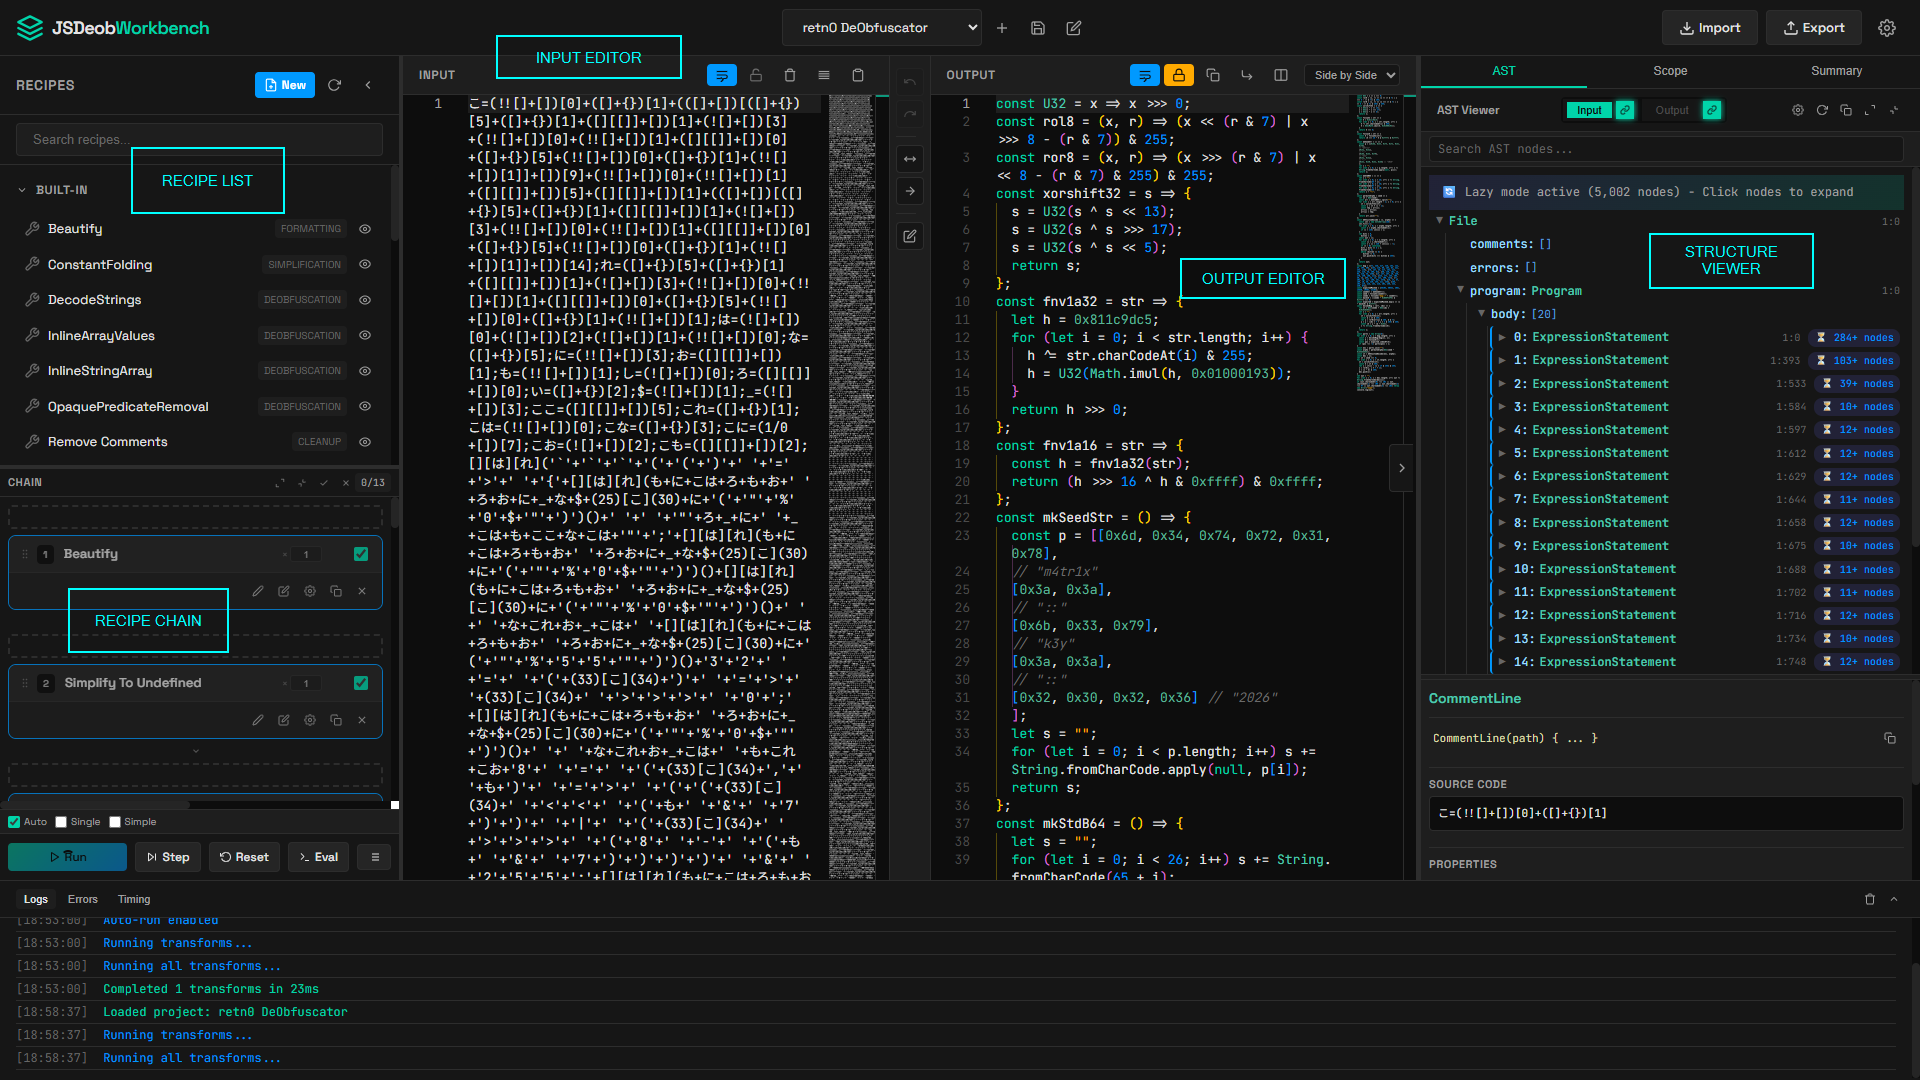 owl4444/jsdeob-workbench
Reverse engineer obfuscated JavaScript visually. Chain transforms, inspect AST changes, write reusable deobfuscation plugins.
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…