

mora-hwbp
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
adversarial-attackdebuggersdefensive-tools+3
18
dovughs/mora-hwbpHardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 vaibhavpandeyvpz/apkstudio
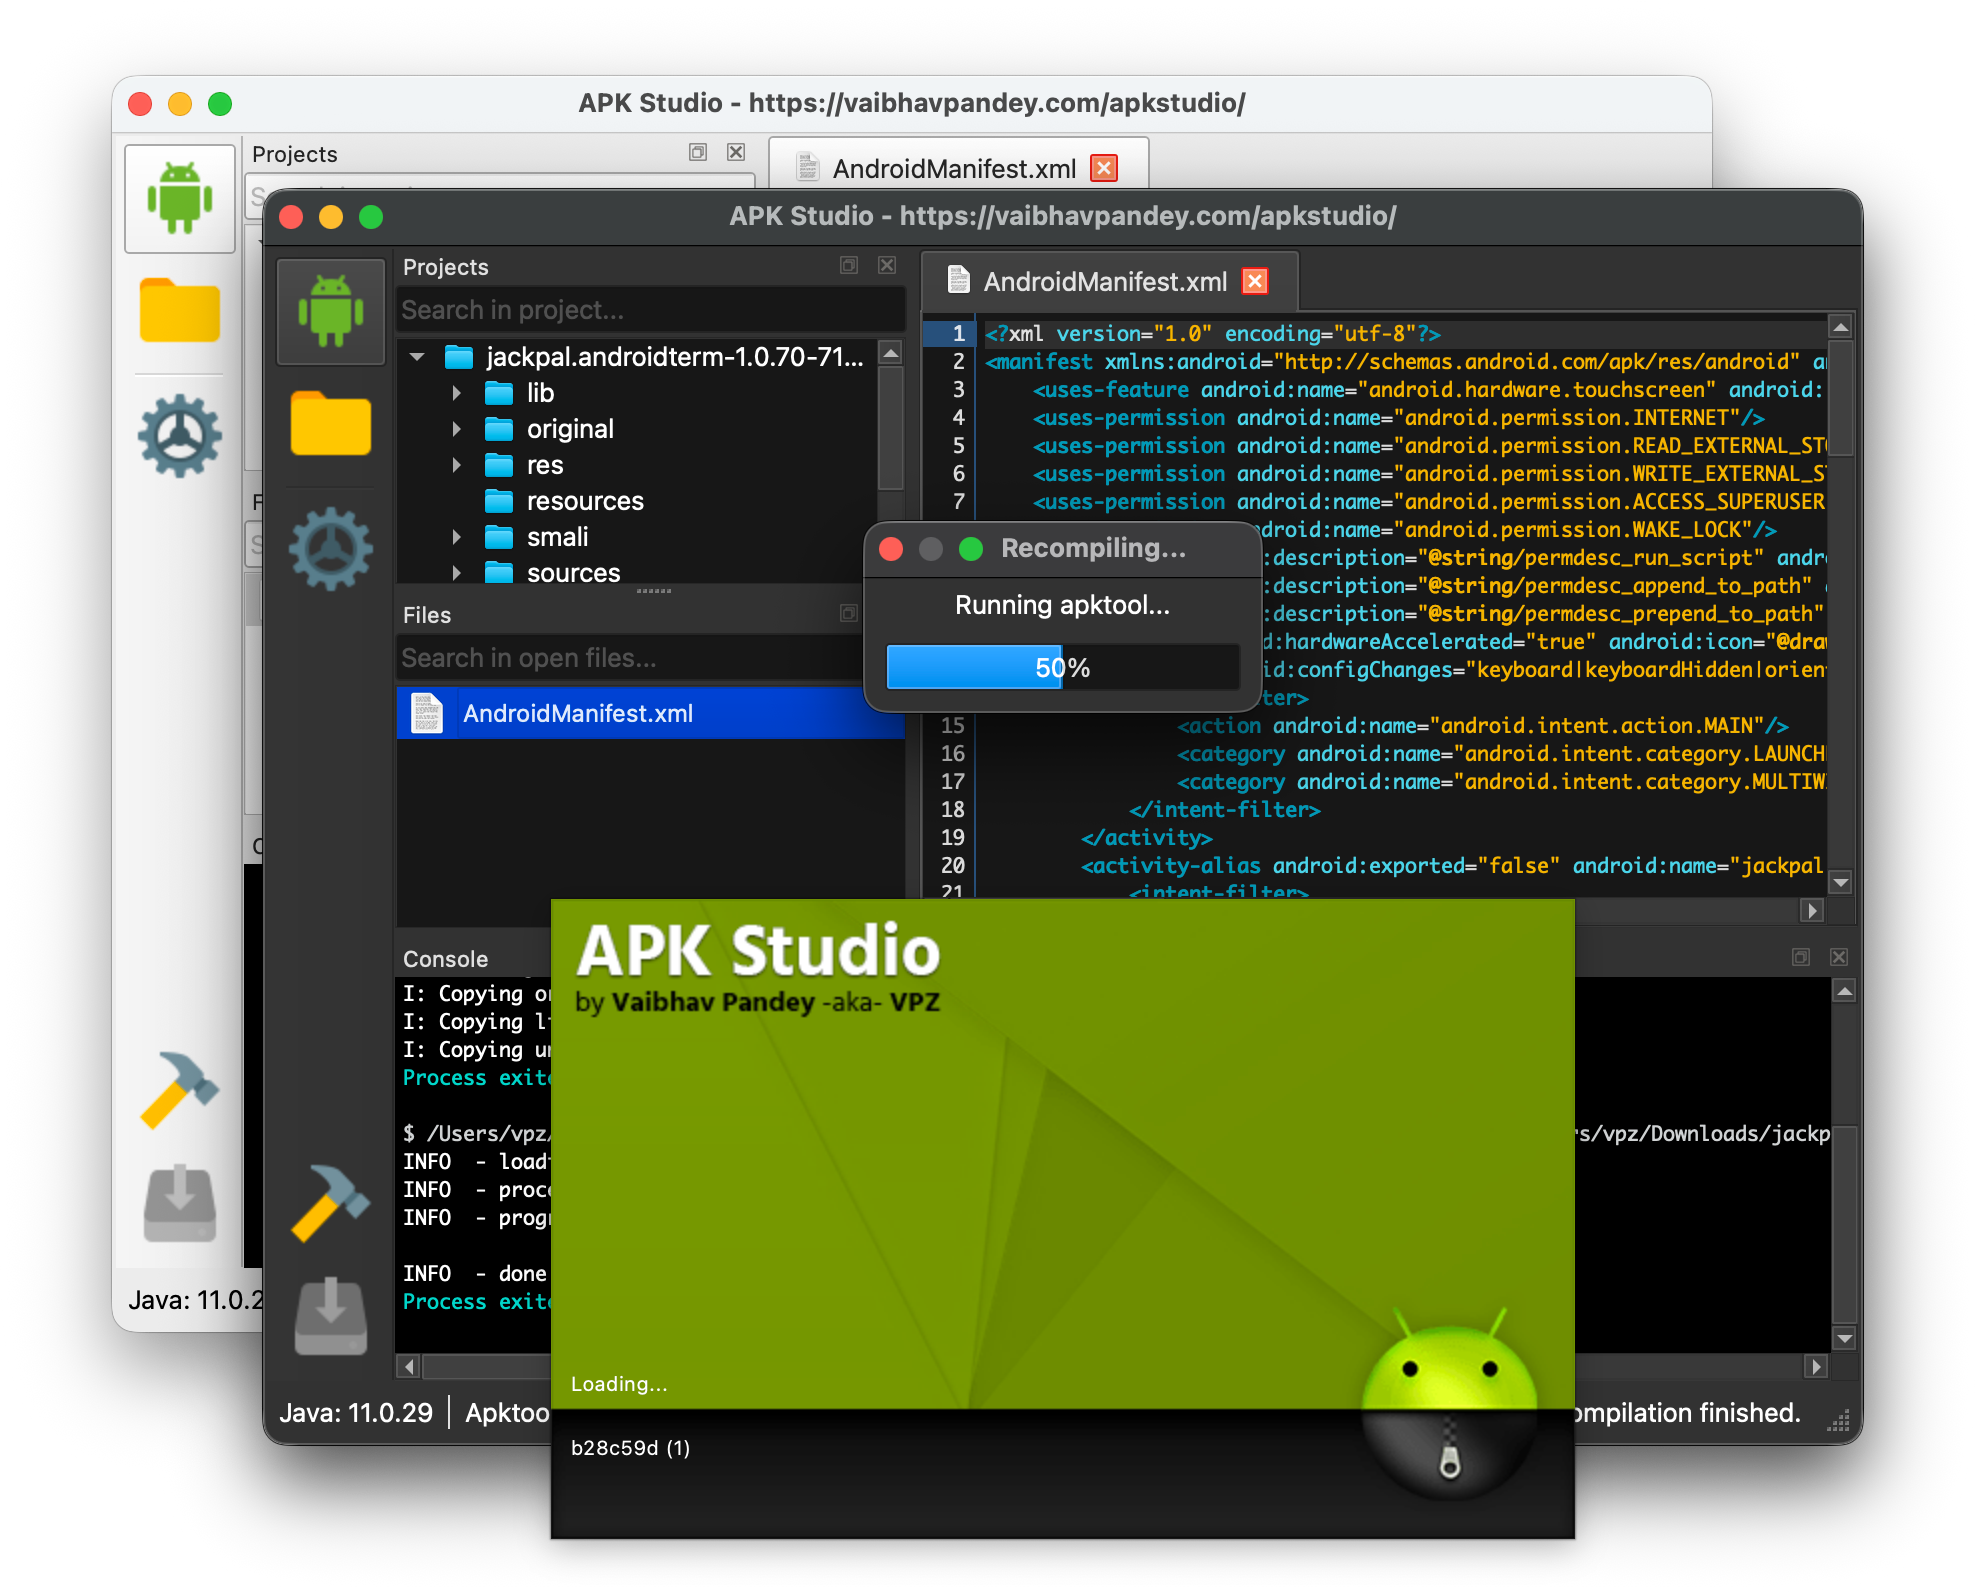
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 kdzwinel/betwixt
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.
 usbarmory/gotee-example
GoTEE - example application
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
 kitctf/nginxpwn
Exploitation Training -- CVE-2013-2028: Nginx Stack Based Buffer Overflow
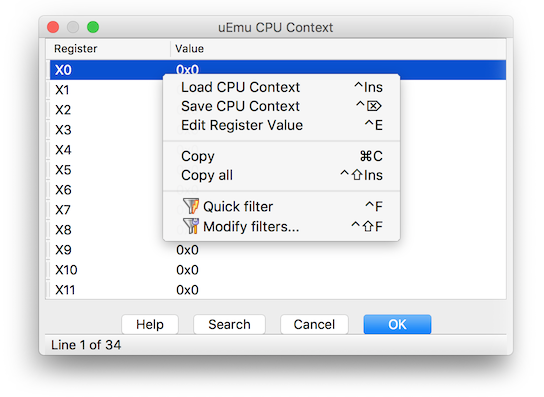 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
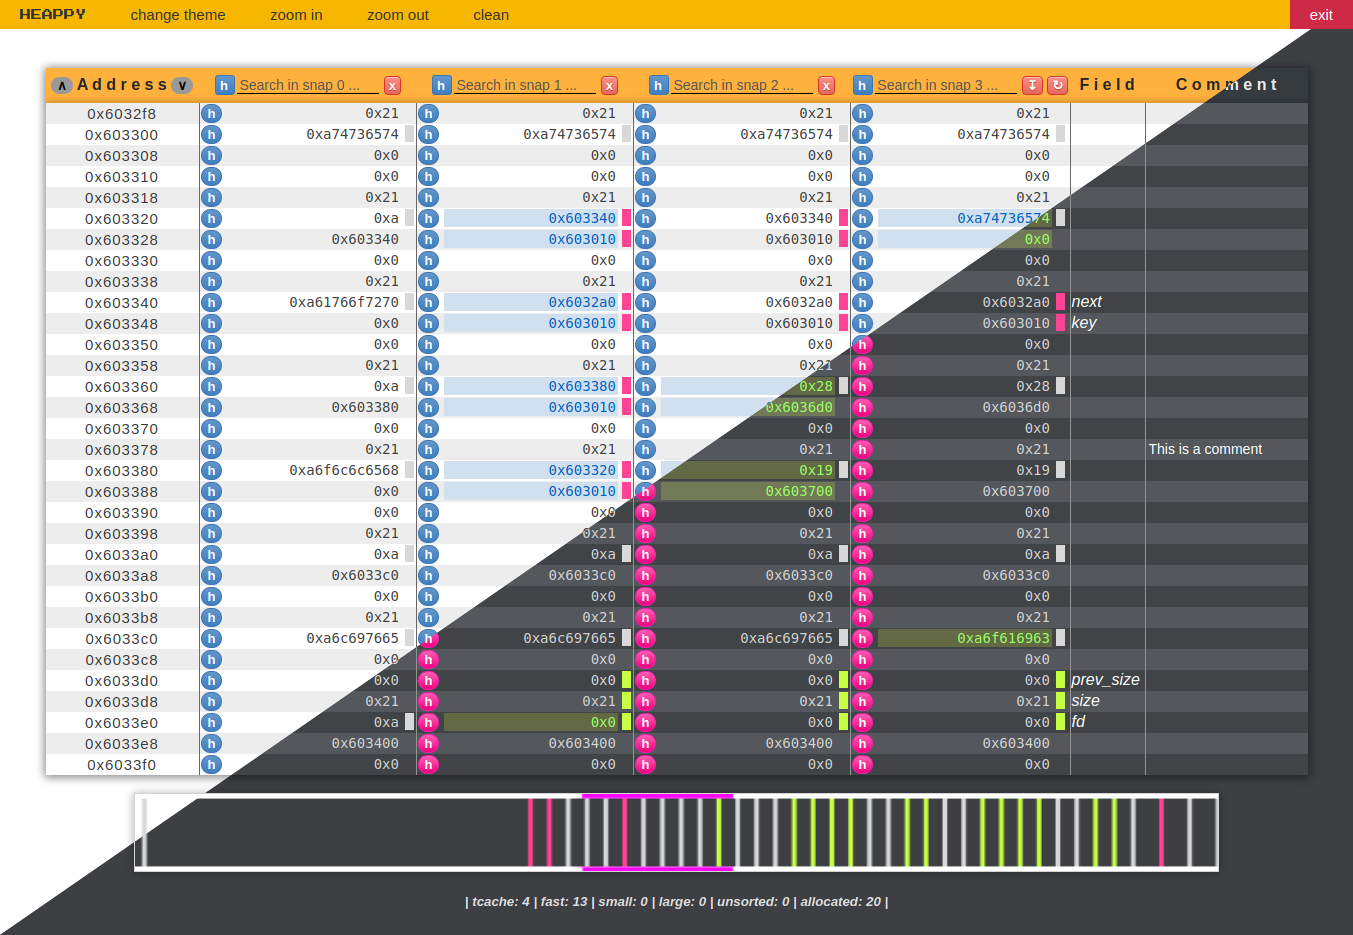 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory