
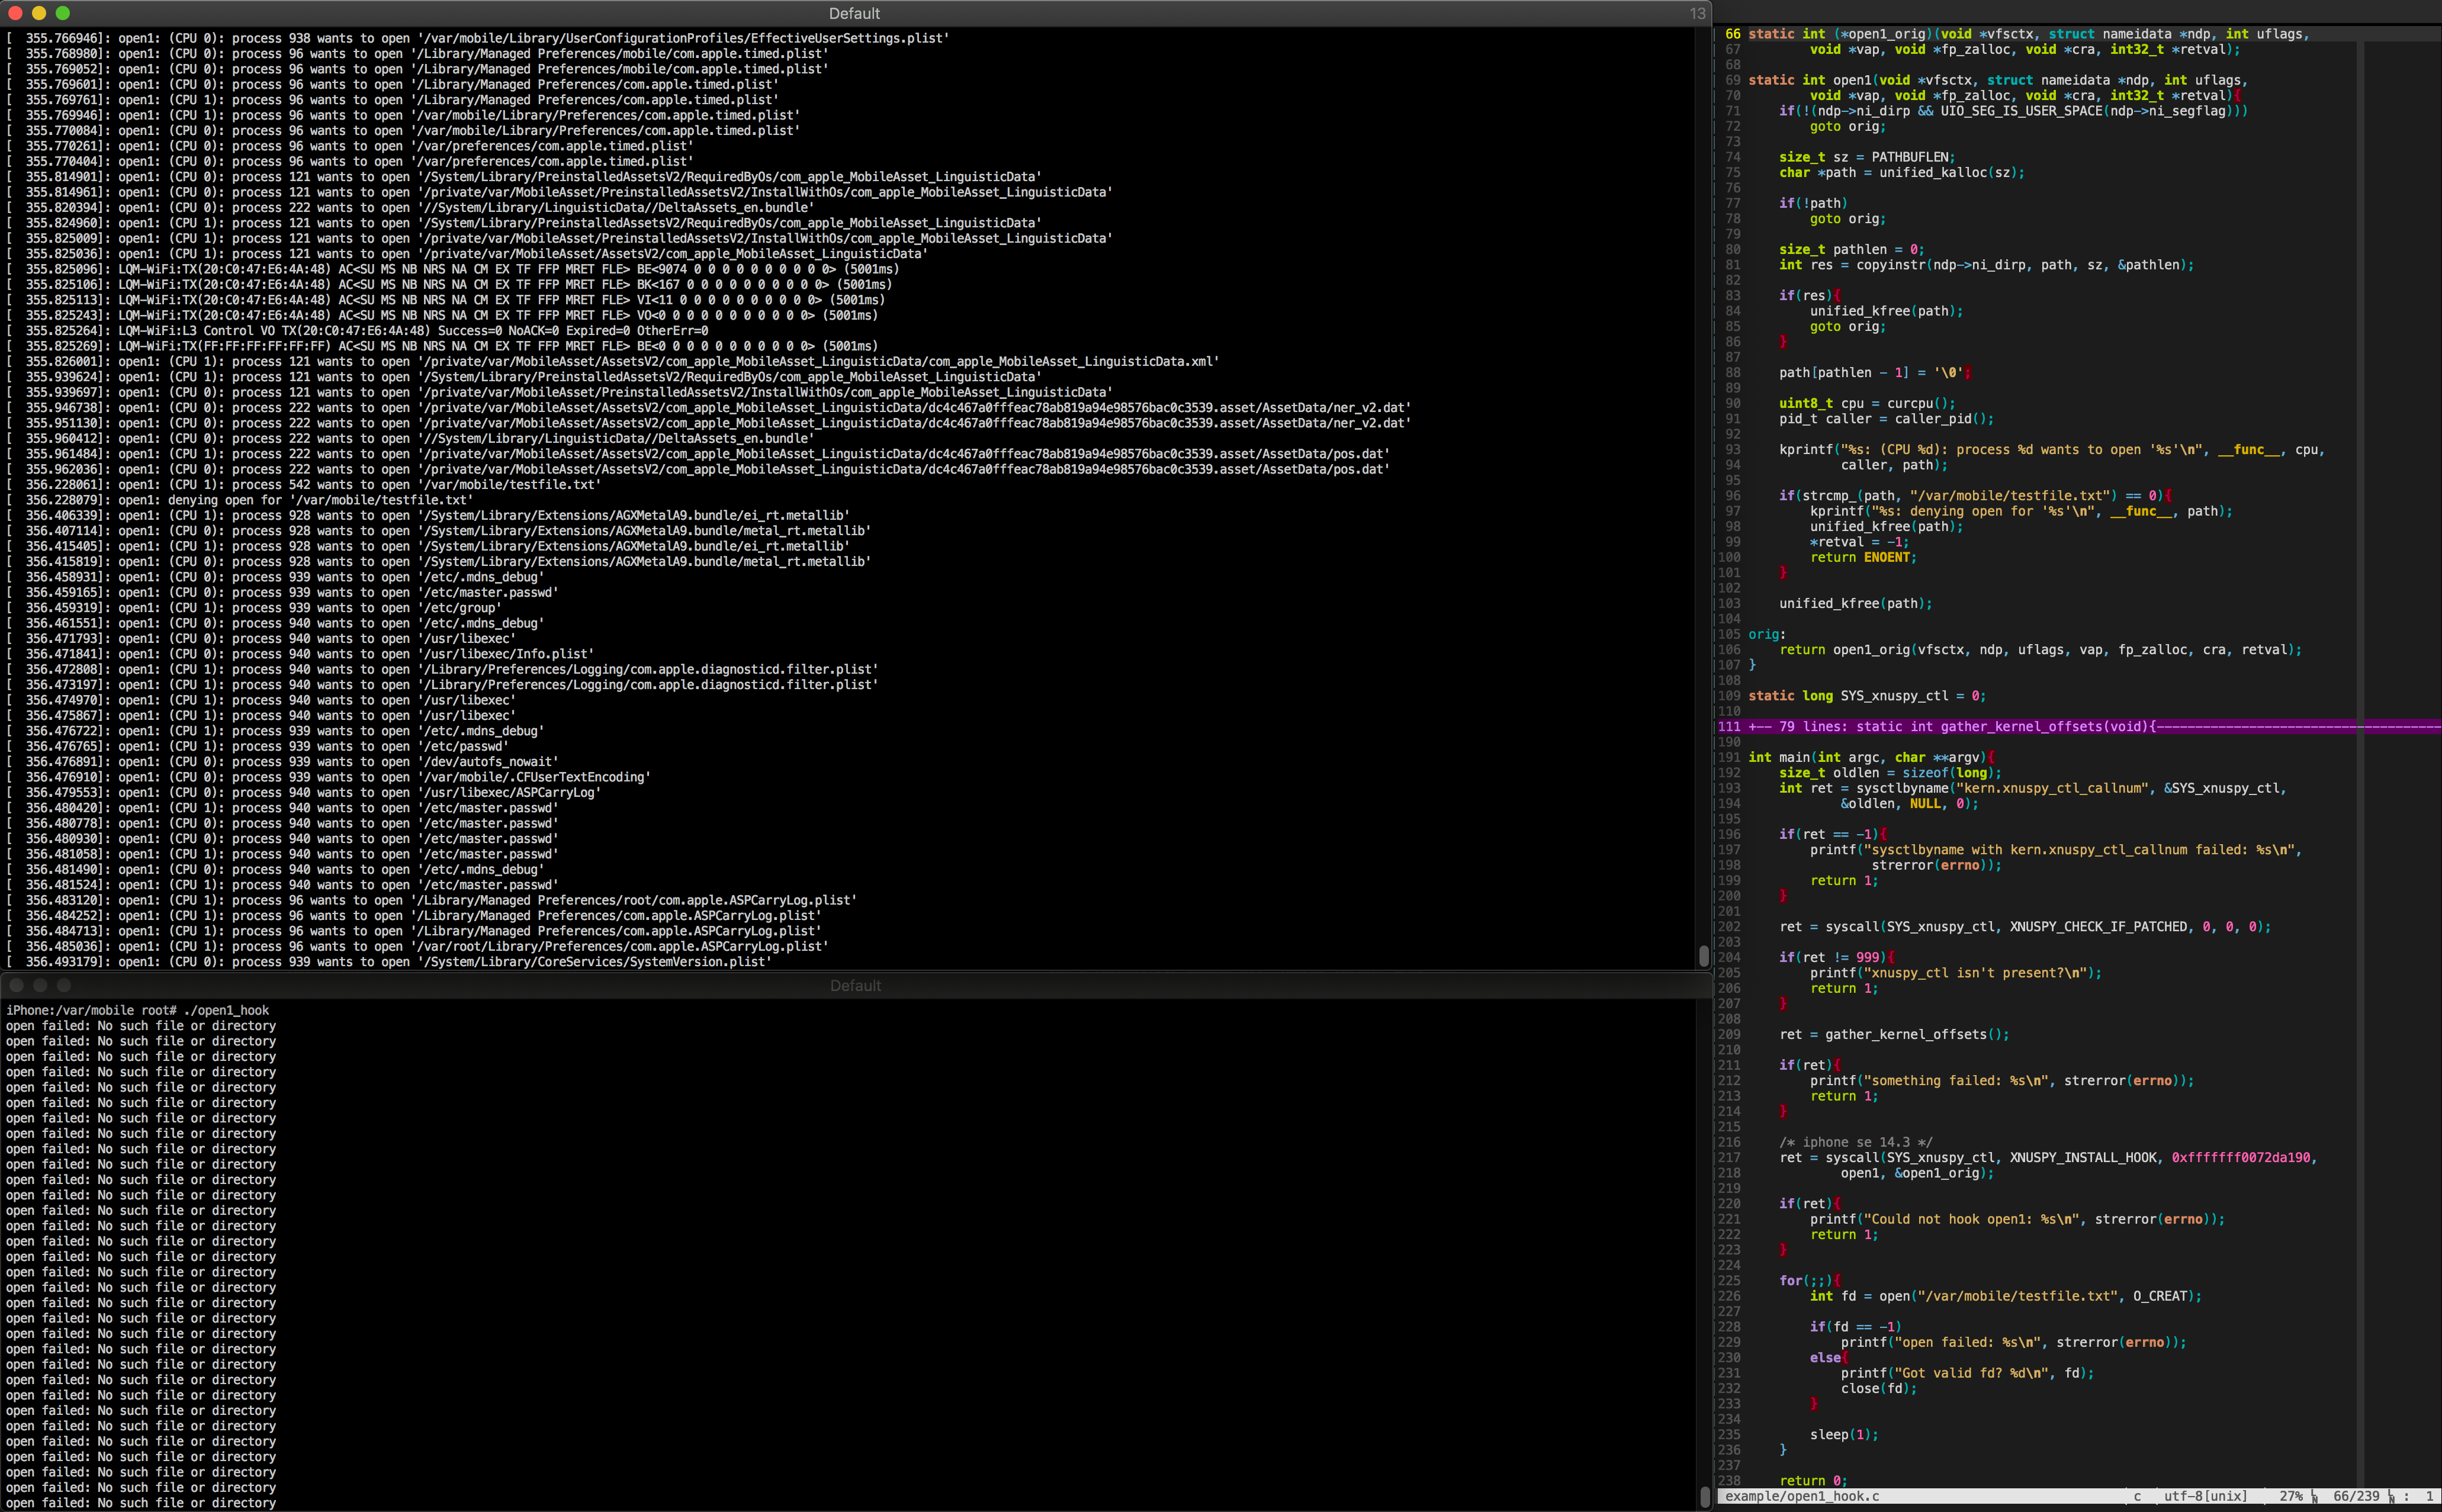
xnuspy
 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
binary-analysisdebuggersexploitation+1
jsherman212/xnuspyan iOS kernel function hooking framework for checkra1n'able devices
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
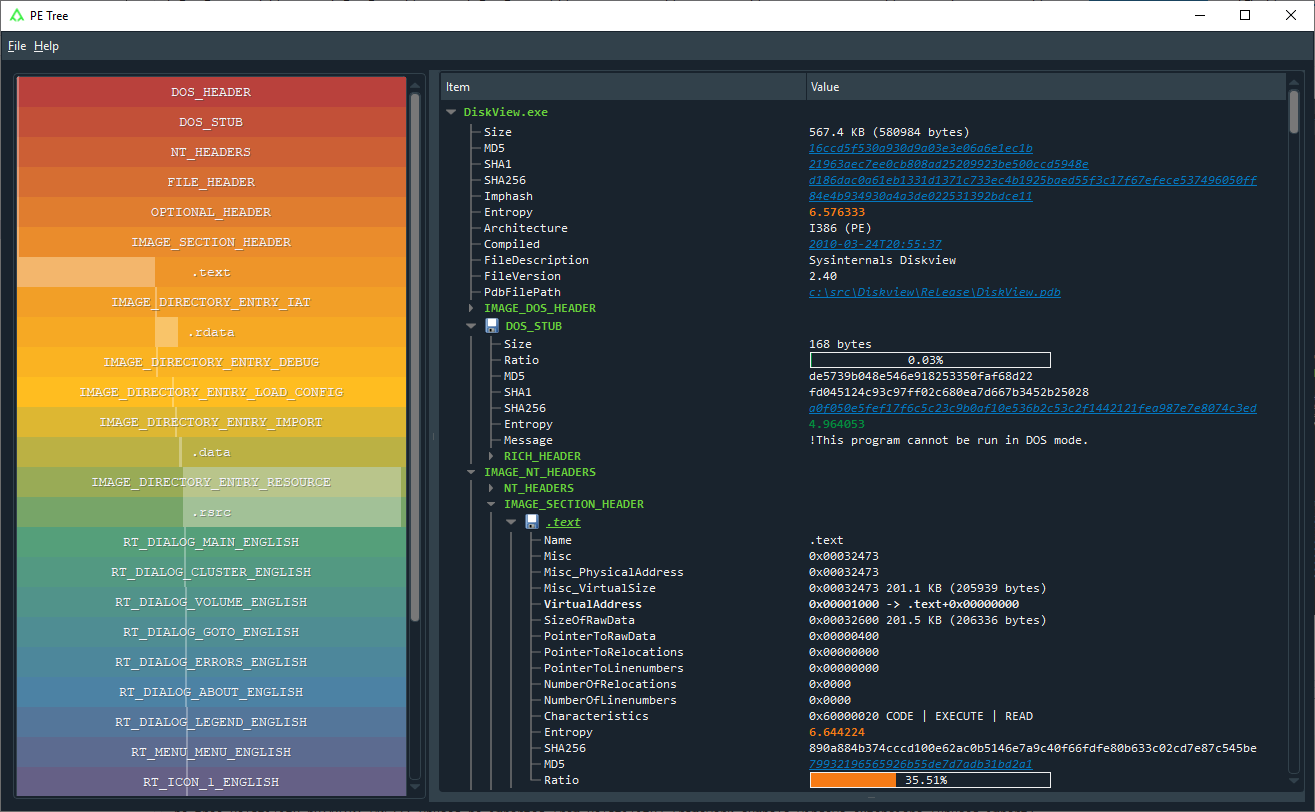 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
 gmh5225/linux-kernel-debugger
Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.