
kernel-research
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
binary-exploitationdebuggersexploit-frameworks+6
97
google/kernel-researchLinux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
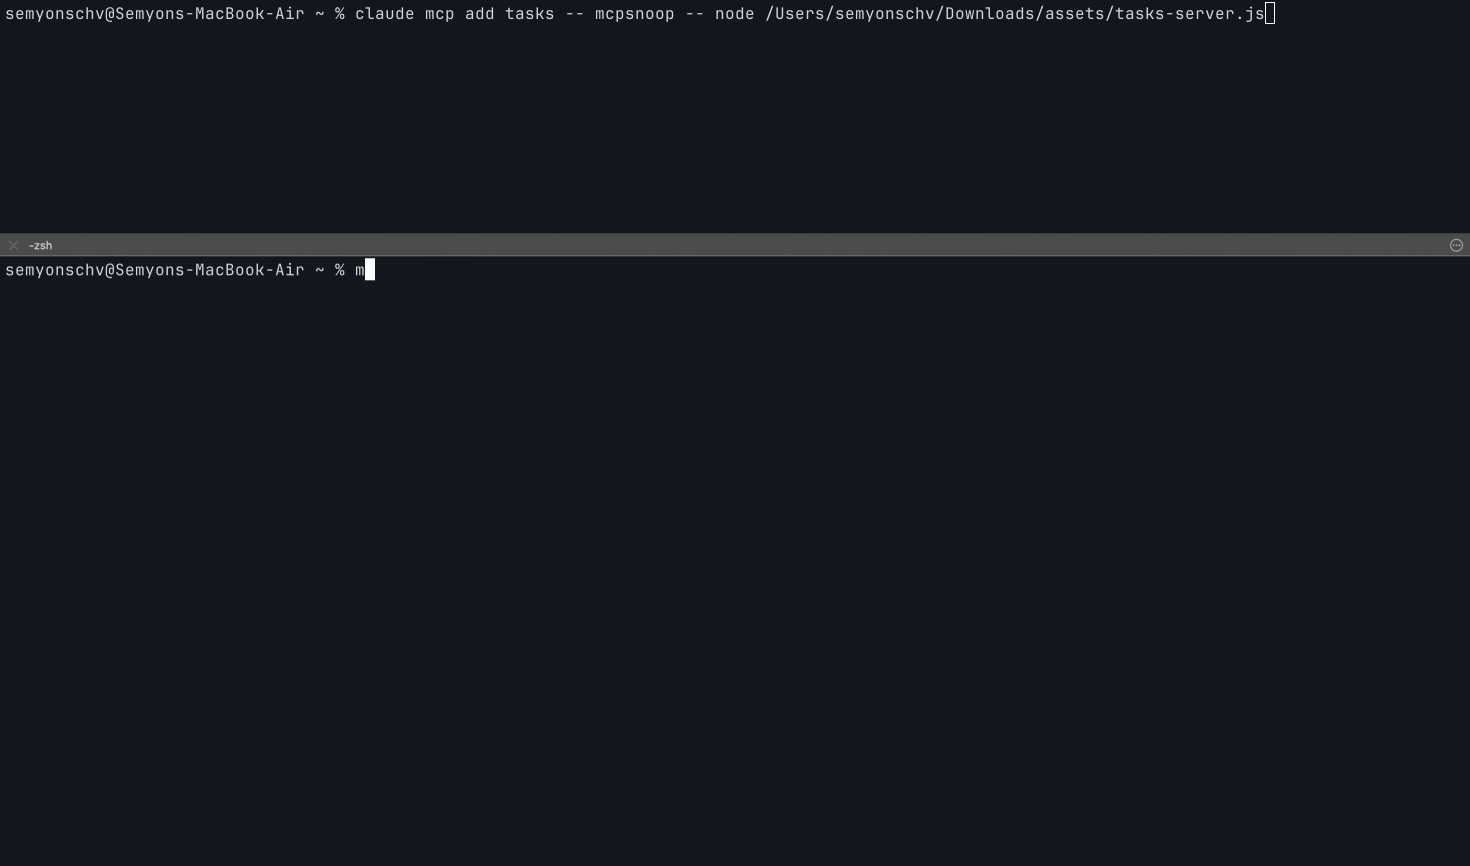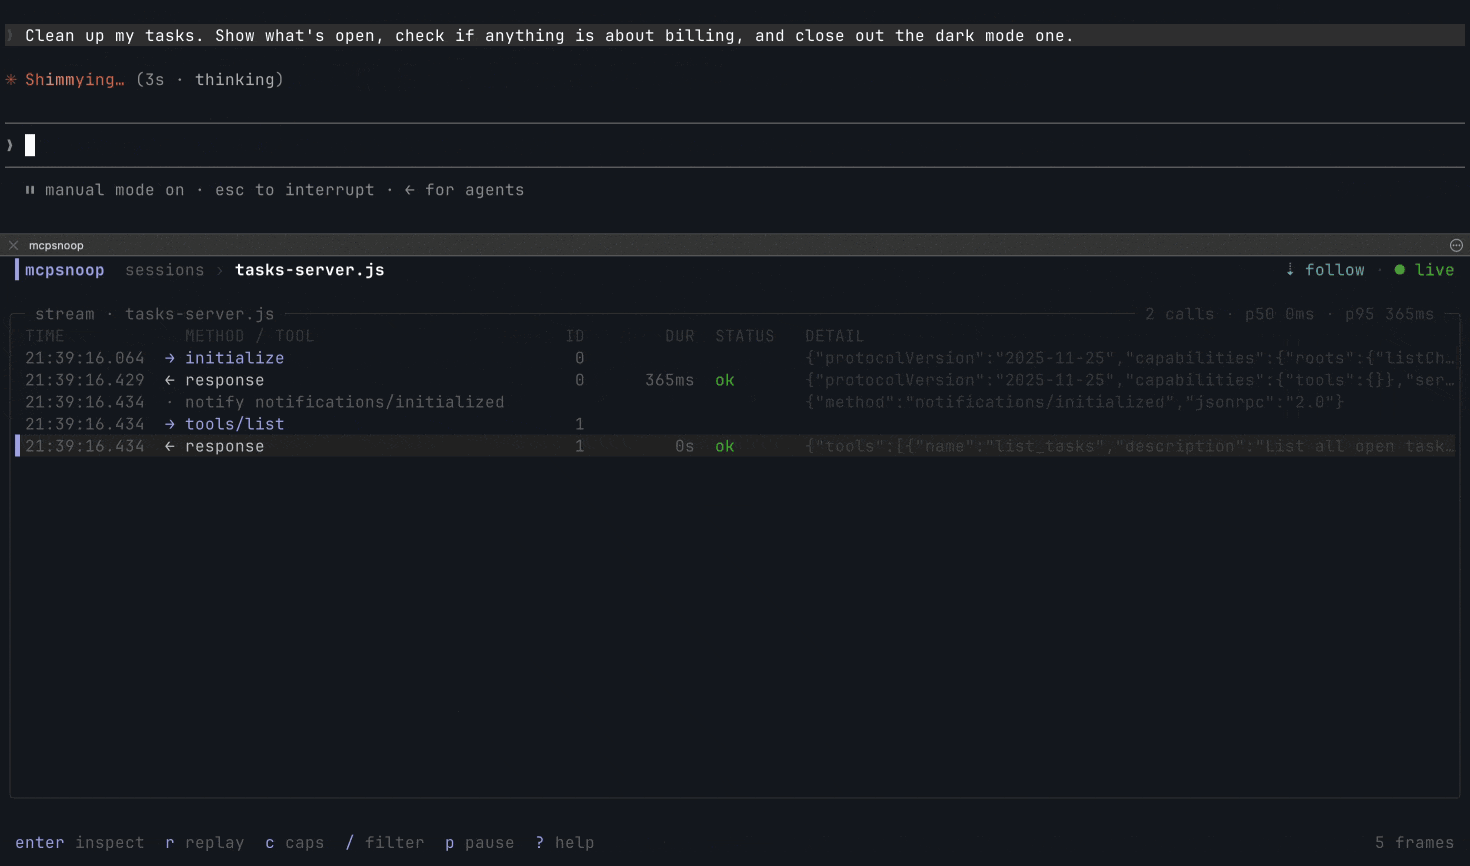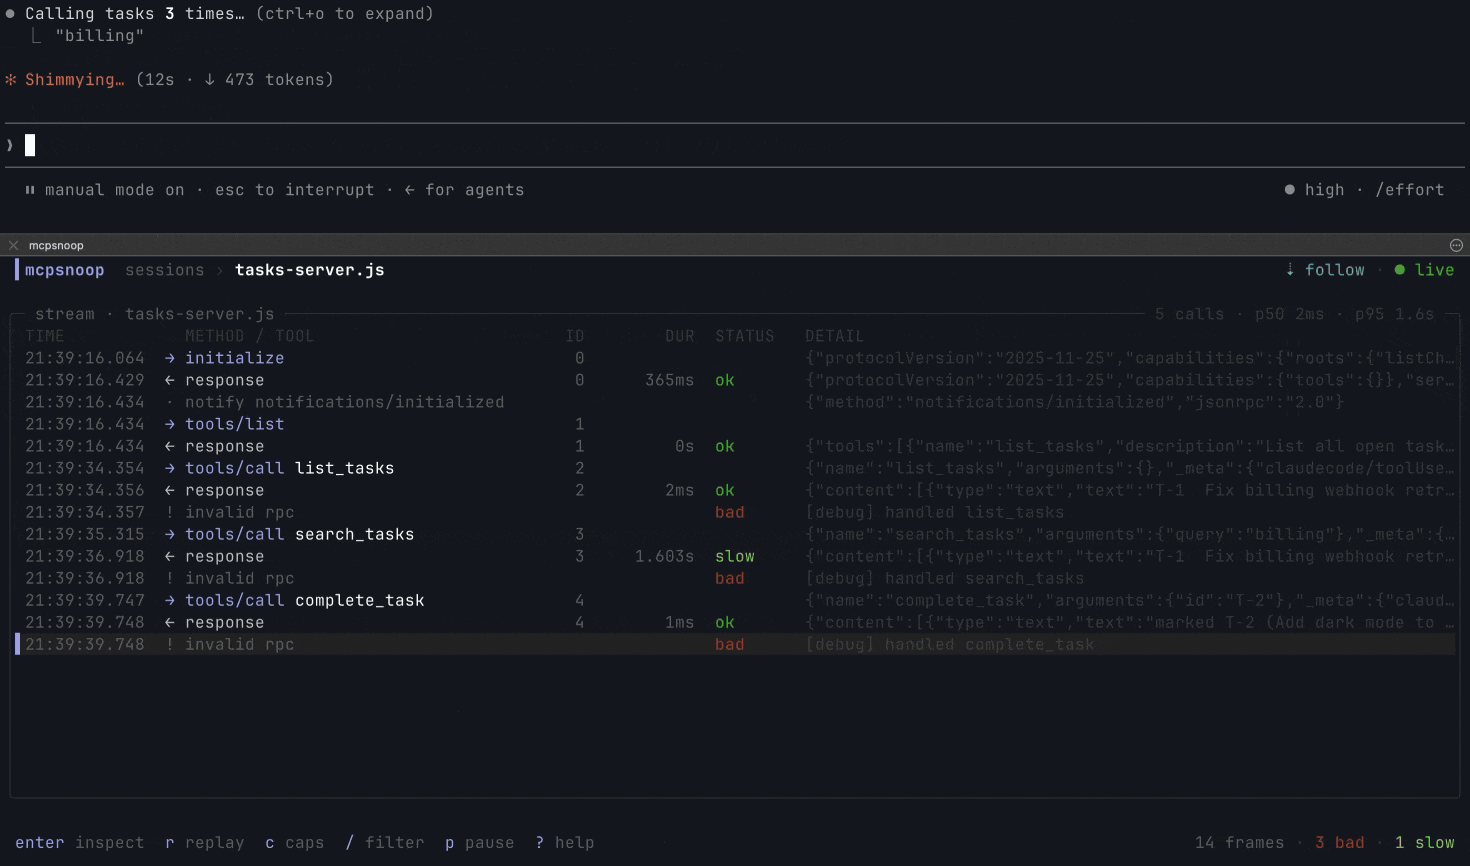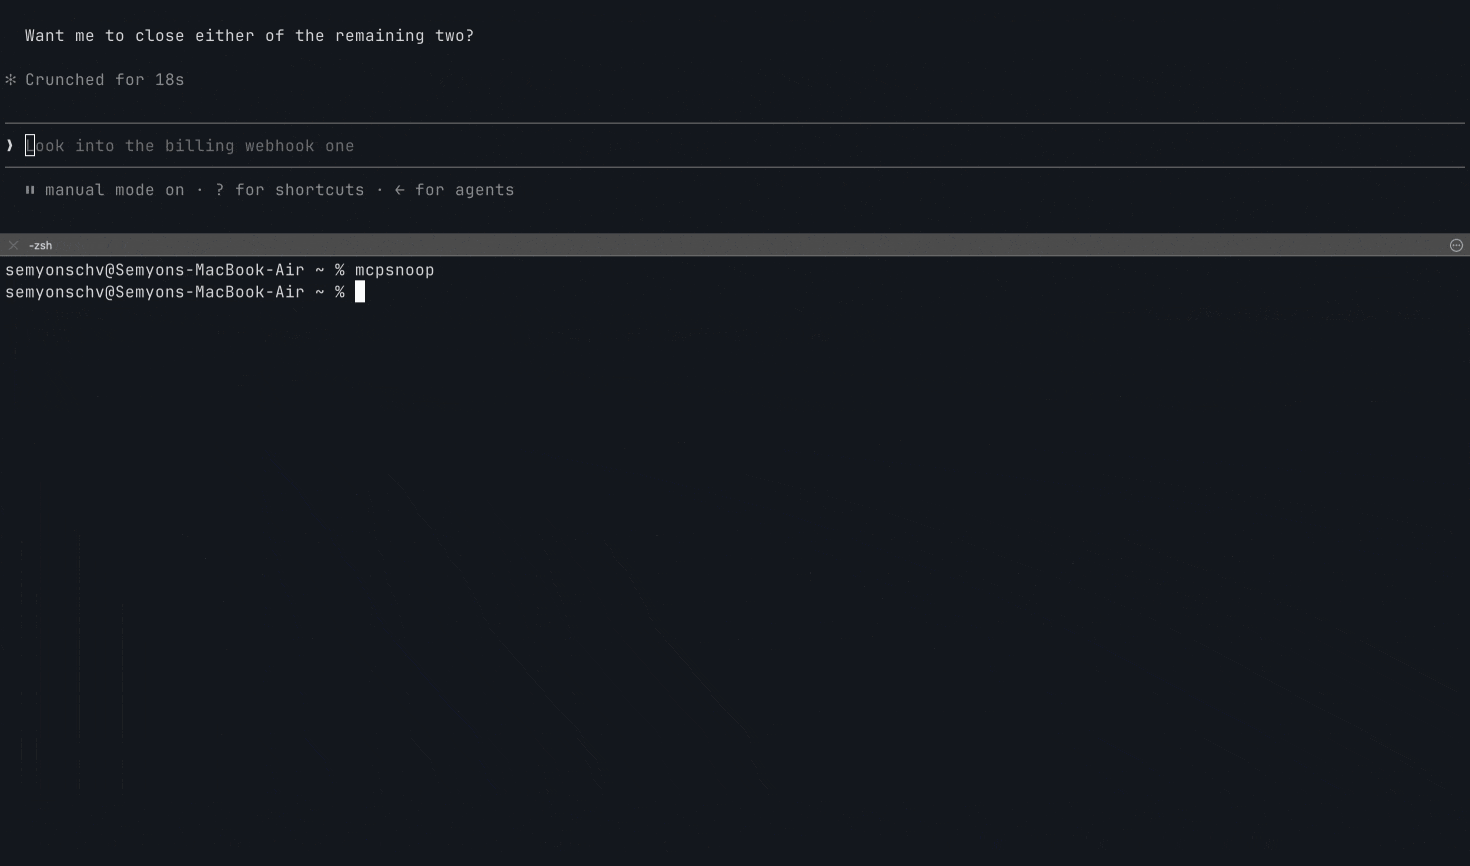 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 zardus/ctf-tools
Some setup scripts for security research tools.
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
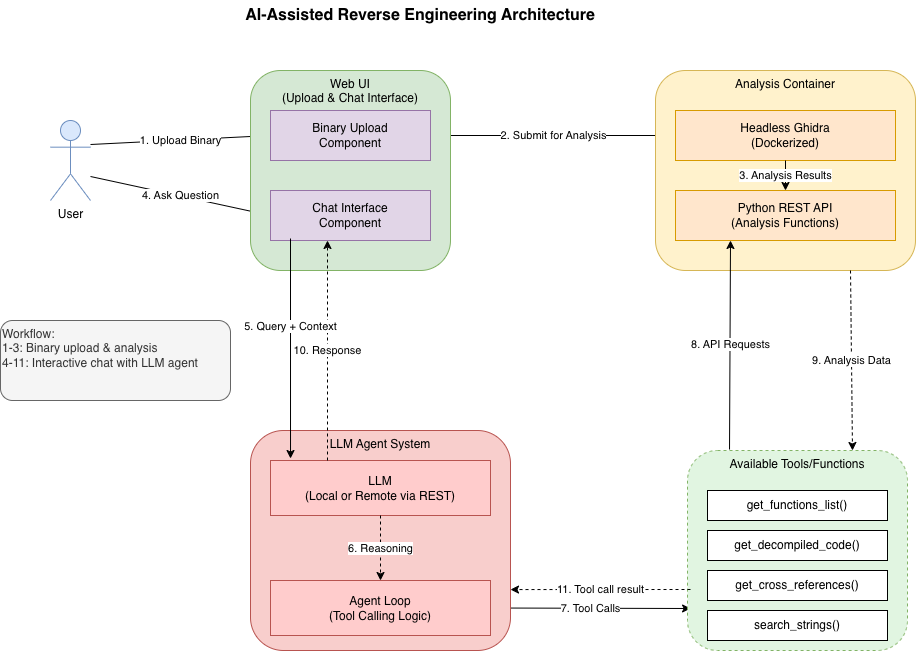 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
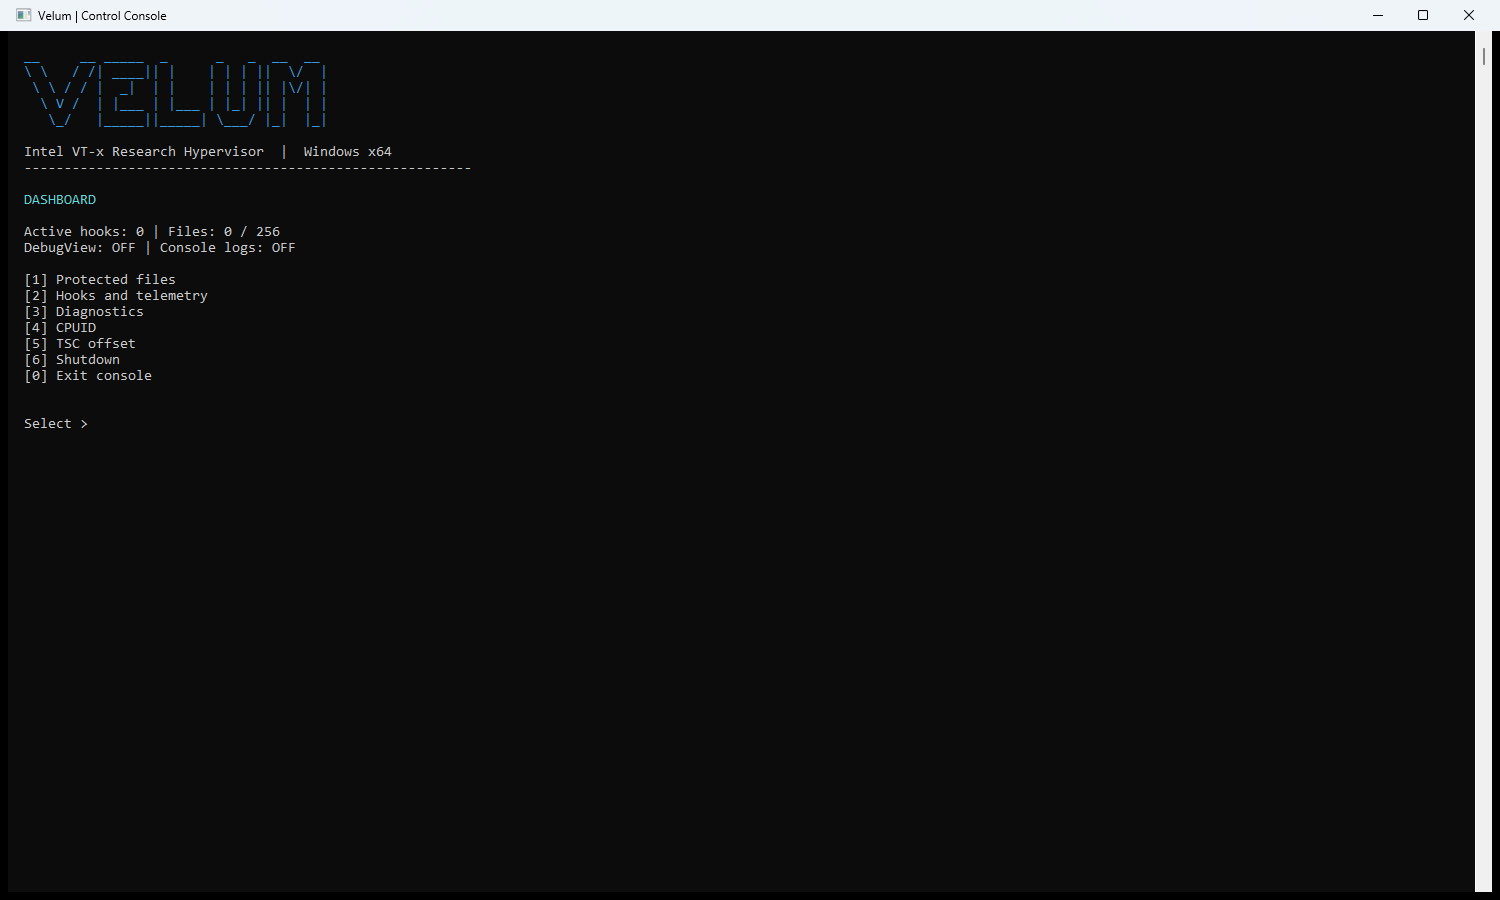 dovughs/velum-vmm
Windows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
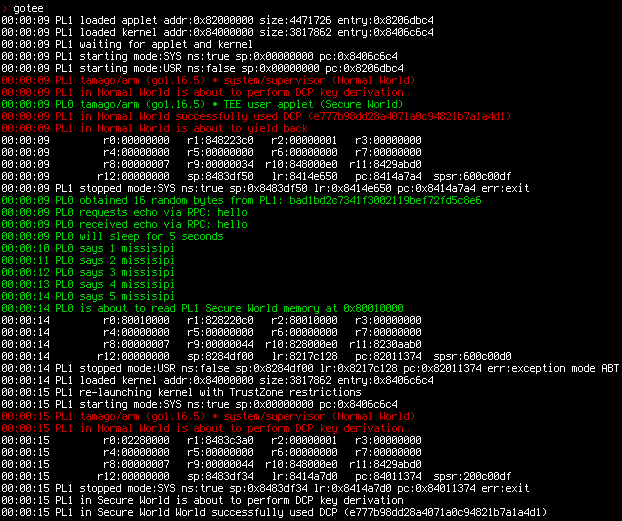 usbarmory/gotee-example
GoTEE - example application
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.