

lighthouse
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
binary-analysiscode-analysisdebuggers+6
gaasedelen/lighthouseA Coverage Explorer for Reverse Engineers
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
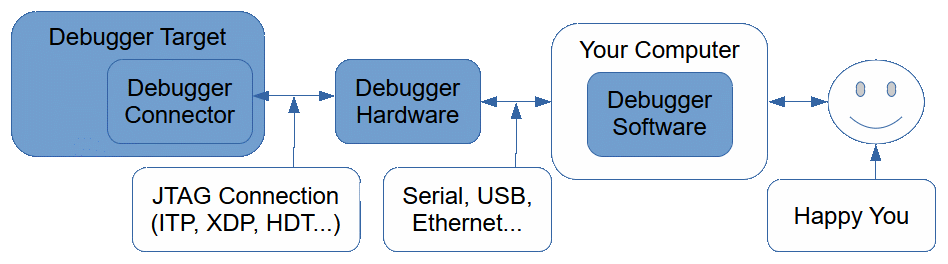 x86-jtag-open-research/x86-jtag-information
Documents Intel and AMD x86 JTAG debugger hardware, connectors, probe software, and target platforms for low-level system debugging and firmware…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 mfthomps/resim
Reverse engineering software using a full system simulator
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
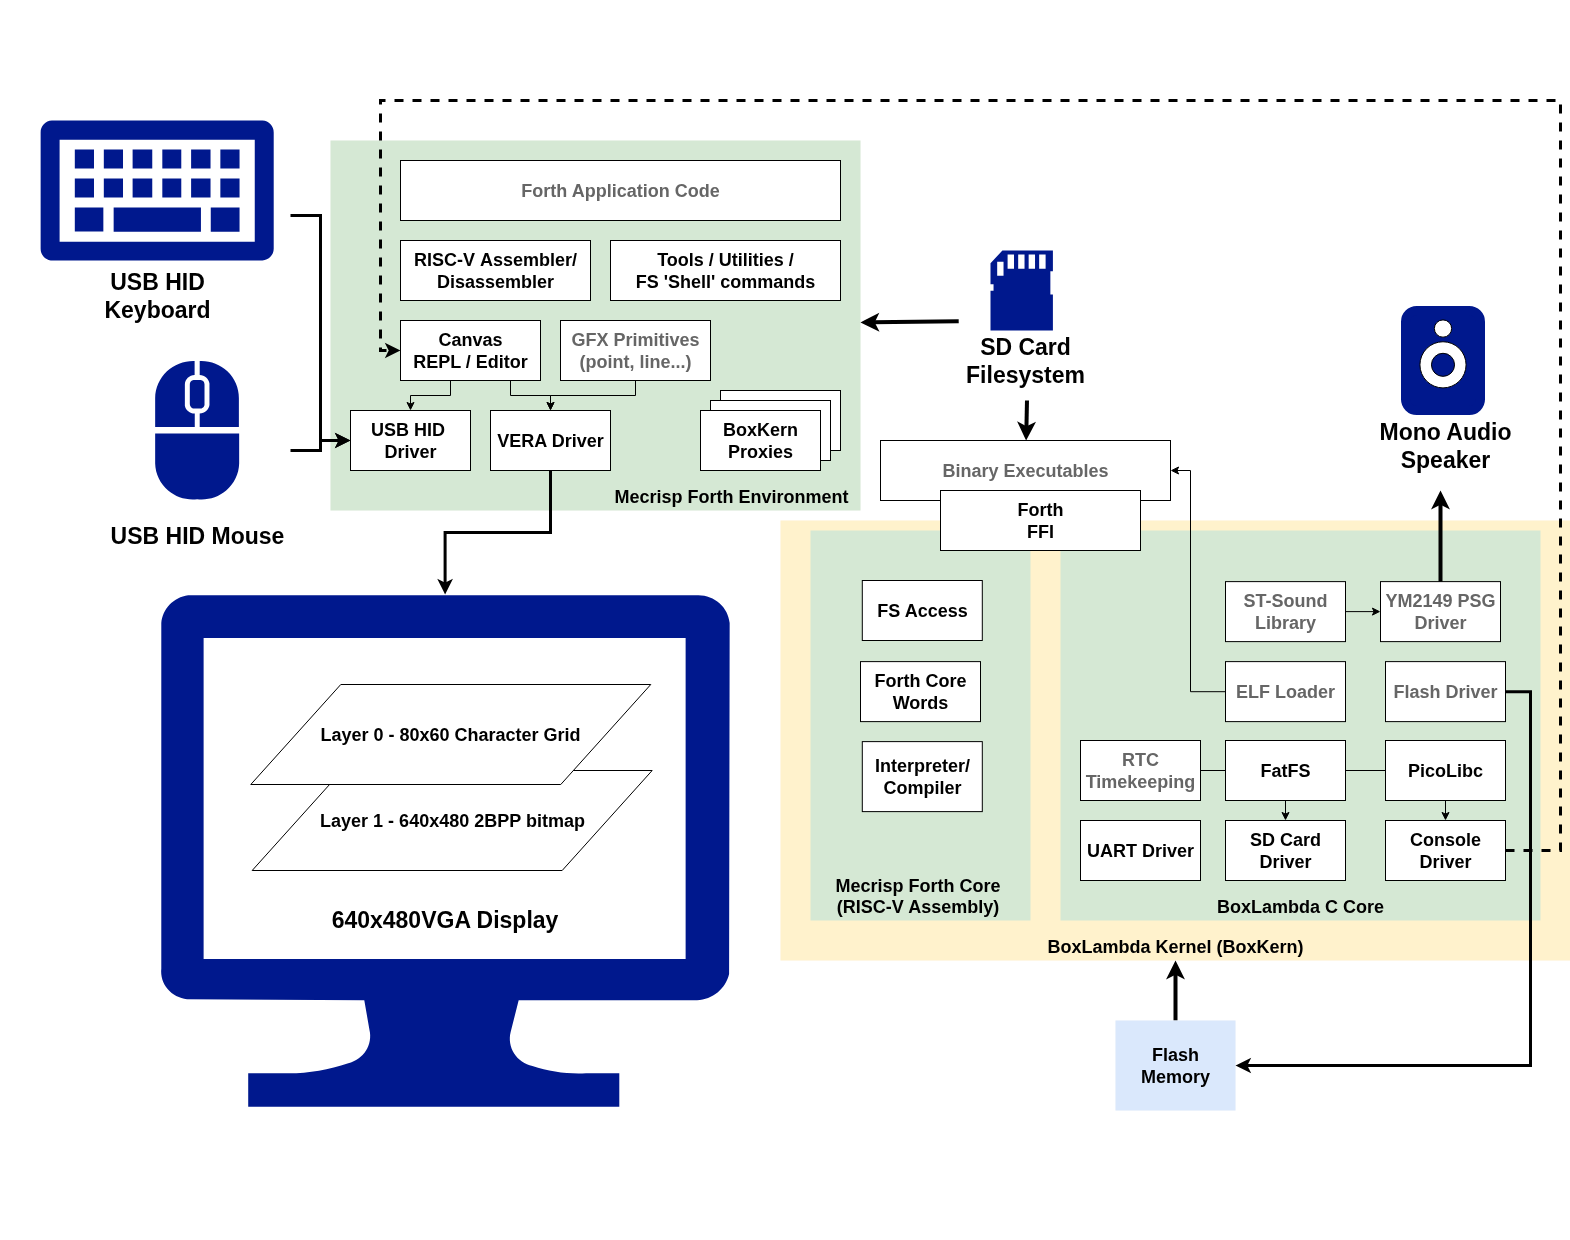 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#