

recurse
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
ai-assisted-reversingai-securitybinary-analysis+7
284
recurse-labs/recurseAgentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 zardus/ctf-tools
Some setup scripts for security research tools.
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 illera88/ponce
IDA 2016 plugin contest winner! Symbolic Execution just one-click away!
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
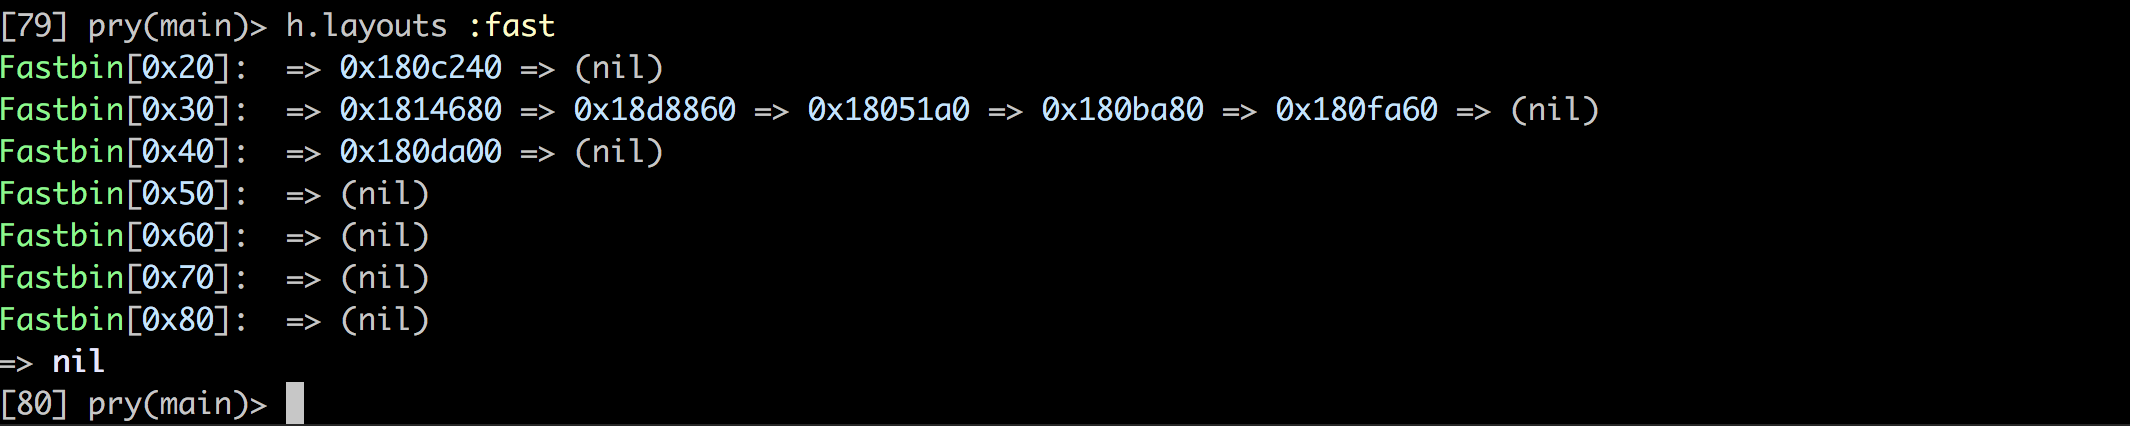 david942j/heapinfo
An interactive memory info for pwning / exploiting
 angr/angr
A powerful and user-friendly binary analysis platform!
 gallopsled/pwntools
CTF framework and exploit development library
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
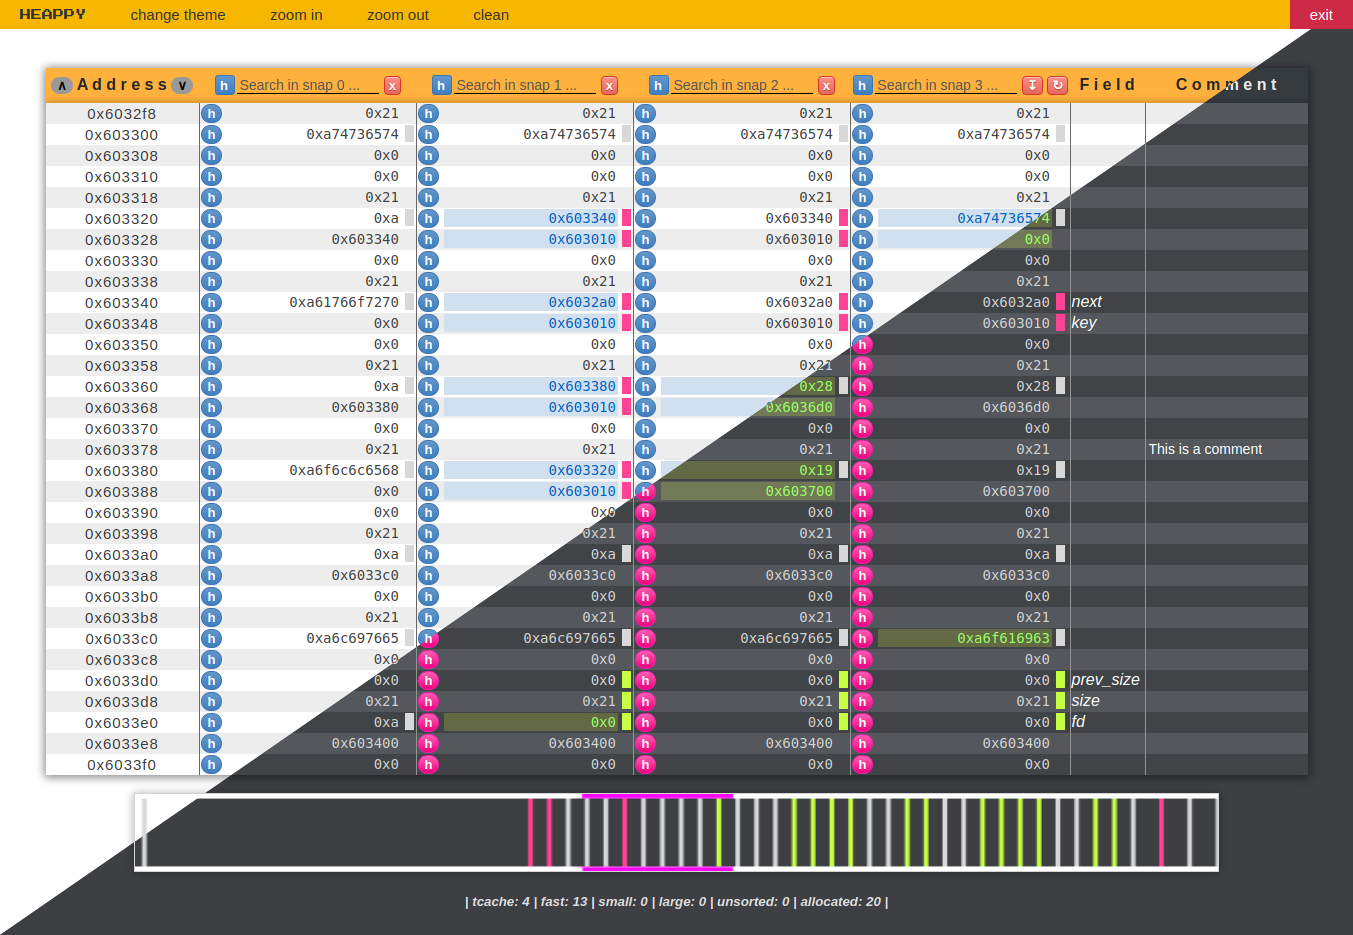 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.