capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 angr/angr
A powerful and user-friendly binary analysis platform!
 gallopsled/pwntools
CTF framework and exploit development library
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
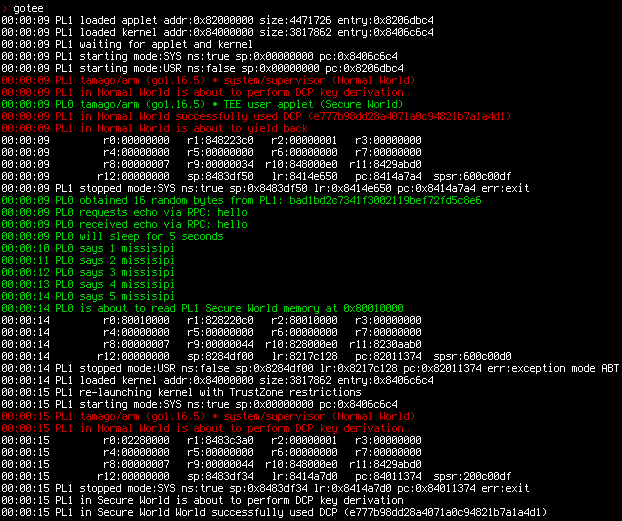 usbarmory/gotee-example
GoTEE - example application