

duckdb
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
anomaly-detectiondatabase-securityeducation+2
5
jepsen-io/duckdbJepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
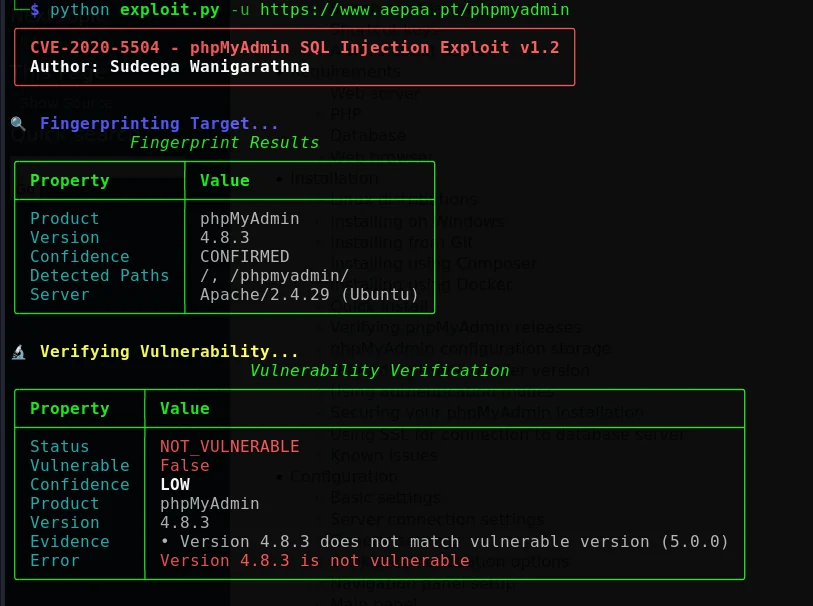 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 sysdream/pysqli
Python SQL injection framework
 torque59/nosql-exploitation-framework
A Python Framework For NoSQL Scanning and Exploitation
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 torque59/nosqlpot
The NoSQL Honeypot Framework
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 ivansmc/cve-2025-10351-poc
Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework
 initroot/wodat
Windows Oracle Database Attack Toolkit
 eqstlab/cve-2026-34220
SQL Injection vulnerability in MikroORM
 eqstlab/cve-2026-0603
Hibernate ORM Second-Order SQL Injection
 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference