

wapiti
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
api-security-testingconfiguration-auditingcrawler+11
wapiti-scanner/wapitiWeb vulnerability scanner written in Python3
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…
 0xsu3ks/cve-2025-45346
Proof-of-concept exploit for time-based blind SQL injection in Bacula-Web's jobfiles endpoint, using pg_sleep() delays to extract PostgreSQL version…
 geraldoalcantara/cve-2023-49968
Customer Support System 1.0 - SQL Injection Vulnerability in manage_department.php via "id" URL Parameter
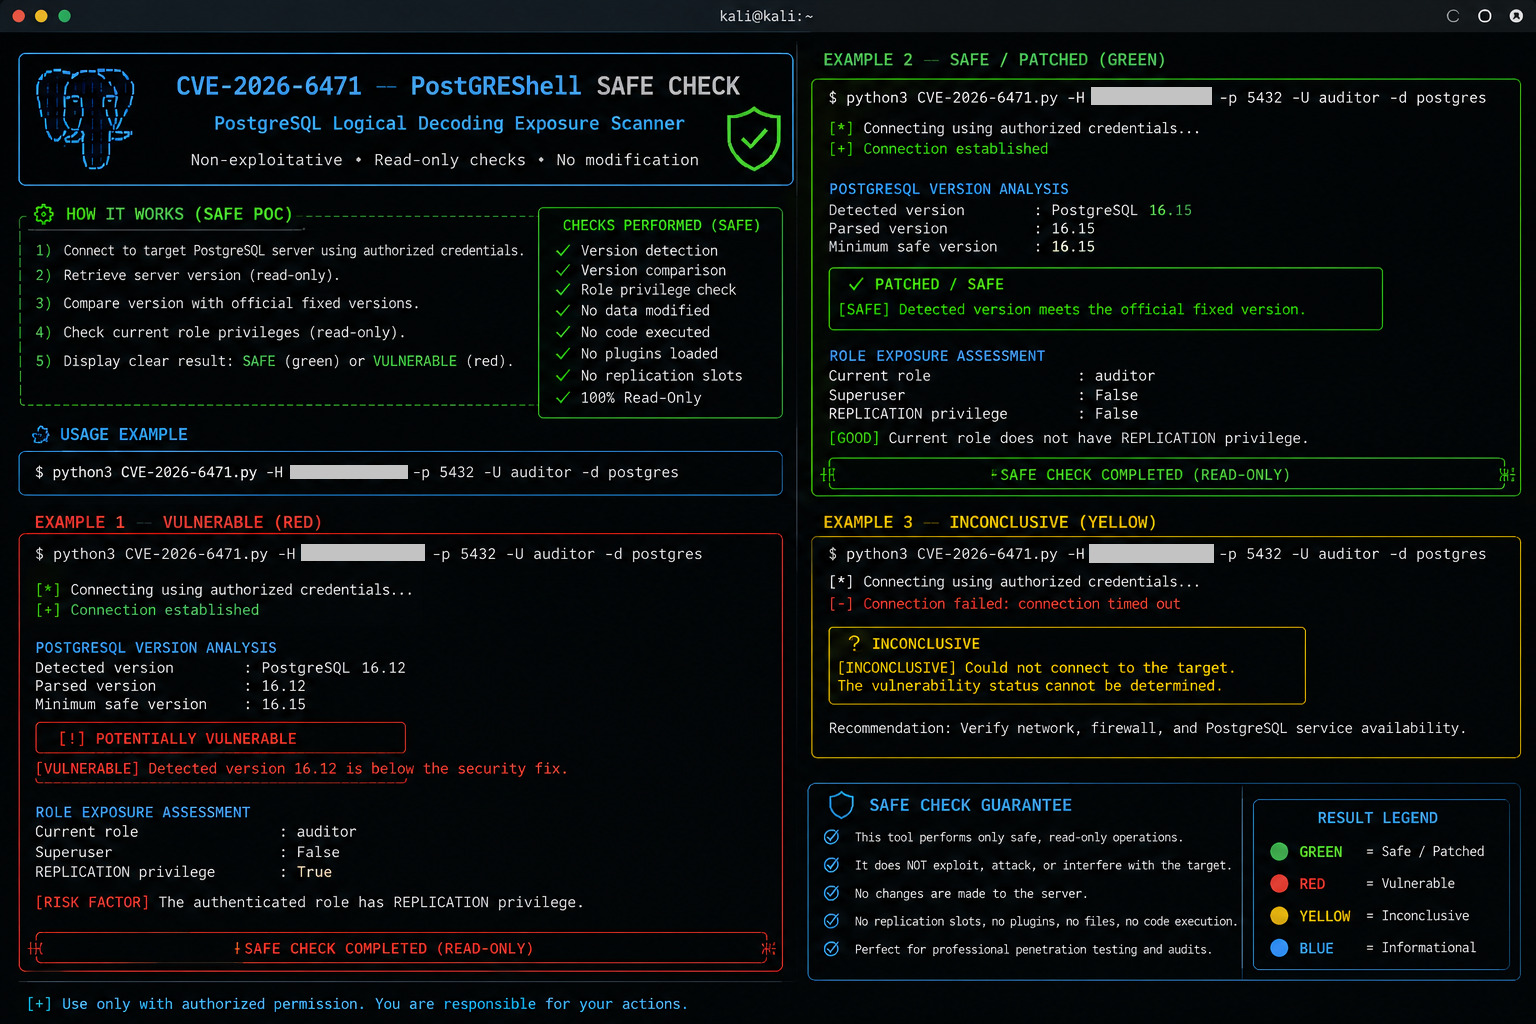 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 maliktawfiq/cve-2025-22953
EPICOR HCM Unauthenticated Blind SQL Injection CVE-2025-22953
 amaansiddd787/cve-2025-65354
Technical disclosure and proof-of-concept for SQL injection in PuneethReddyHC event-management v1.0, detailing affected endpoint, payloads, and…
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
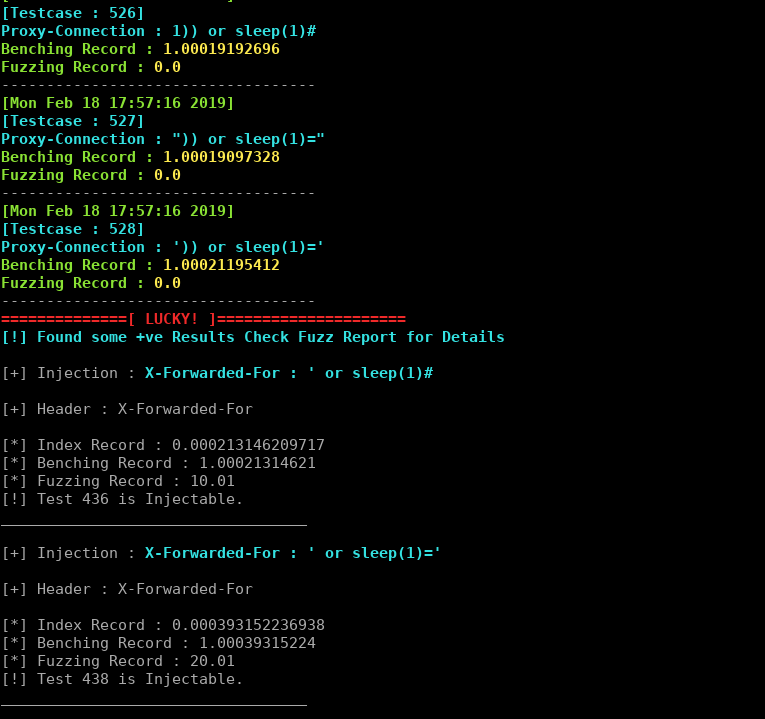 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 wezery/cve-2019-14529
OpenEMR Security issue
 shanika04/cp30_xxe_partial_fix
version between CVE-2018-20433 and CVE-2019-5427