

MongoDeepDive
 tunahantekeoglu/mongodeepdive
Context-Aware Memory Leak Scanner & Exploit for CVE-2025-14847.
database-securityexploitationinformation-gathering+3
tunahantekeoglu/mongodeepdiveContext-Aware Memory Leak Scanner & Exploit for CVE-2025-14847.
 chrissub08/cve-2026-32127_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-32127: SQL Injection Vulnerability in OpenEMR <8.0.0.1
 chrissub08/cve-2026-29187_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-29187: SQL Injection Vulnerability in OpenEMR <8.0.0.3
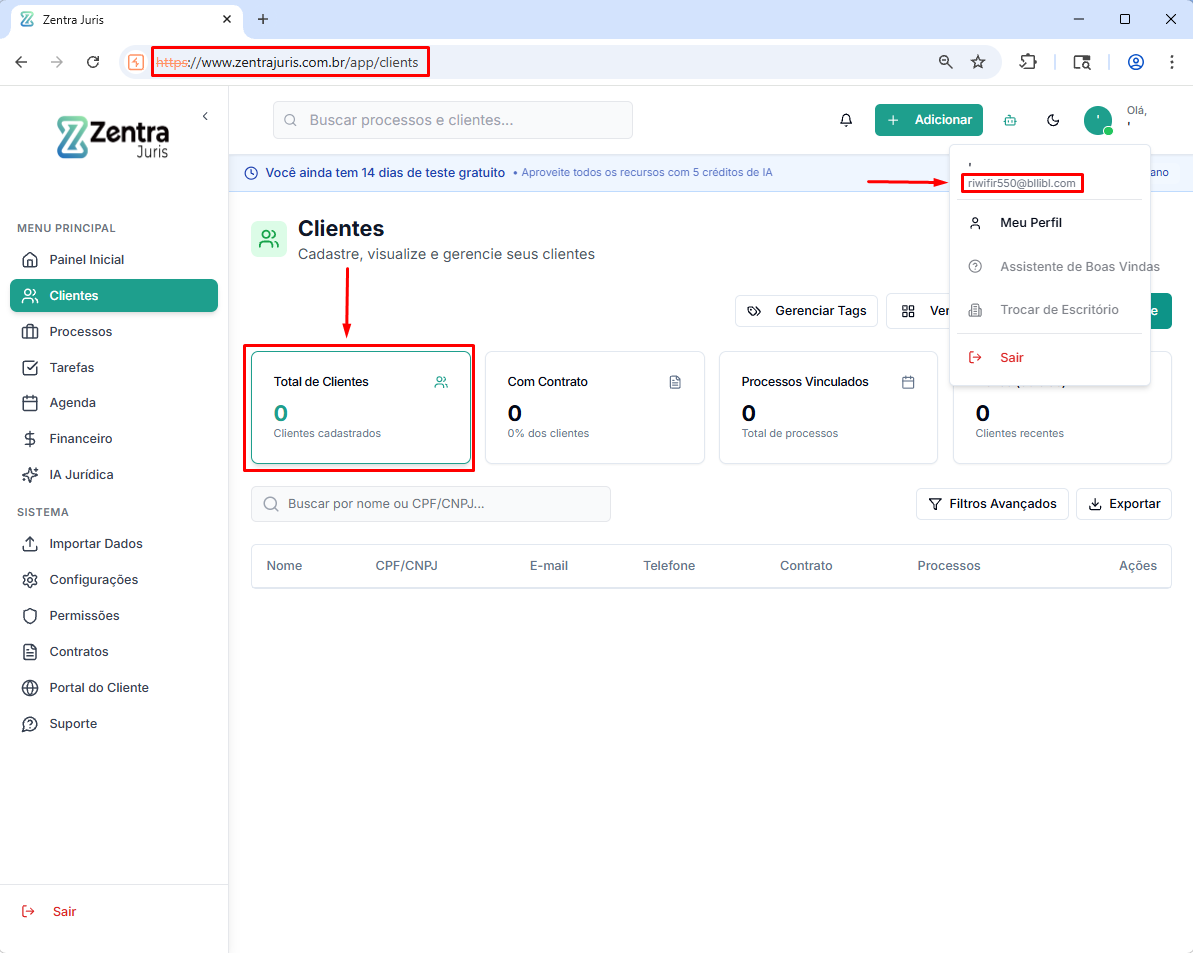 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 petergabaldon/cve-2025-40677
Summar Employee Portal Prior to 3.98.0 Authenticated SQL Injection - CVE-2025-40677
 sohelyousef/cve-2024-58290-xhibiter-sqli
Proof of Concept (PoC) for SQL Injection in Xhibiter NFT Marketplace 1.10.2 (Collections Endpoint). Discovered by Sohel Yousef.
 chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0
 brynax/cve-2026-30655
Security advisory for CVE-2026-30655: unauthenticated SQL injection in esiclivre (/reset/index.php).
 14mb1v45h/cyberdudebivash-mongodb-detector-v2026
Detect exposed MongoDB instances and CVE-2025-14847 "MongoBleed" risks — Zero-Trust Python scanner
 systemhaus-schulz/mongobleed-cve-2025-14847
MongoBleed CVE-2025-14847 Vulnerability Checker
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 0xsu3ks/cve-2025-45346
Proof-of-concept exploit for time-based blind SQL injection in Bacula-Web's jobfiles endpoint, using pg_sleep() delays to extract PostgreSQL version…
 amnnrth/cve-2025-14847
This script is used to identify MongoDB services that are network-exposed and allow unauthenticated protocol handshakes.
 areaventuno/exploit-joomla
Un semplice exploit che sfrutta CVE-2015-7297, CVE-2015-7857 and CVE-2015-7858 per elencare gli utenti con la psw del db
 wezery/cve-2019-14529
OpenEMR Security issue
 emad-almousa/cve-2021-2173
Proof-of-concept exploit for CVE-2021-2173, demonstrating Oracle Database metadata exposure via broken PDB isolation. Includes technical details and…
 m4xiq/cve-2025-51970
SQL Injection in Online Shopping System Advanced (CVE-2025-51970)
 randomrobbiebf/redis-checker
Checks for exposed Redis servers