
CVE-2021-42667
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
database-securityexploitationinformation-gathering+3
2
0xdeku/cve-2021-42667CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
 xbz0n/cve-2024-33911
Proof-of-concept exploit for CVE-2024-33911, a post-authenticated SQL injection vulnerability in The School Management WordPress plugin v10.3.4,…
 safe3s/cve-2022-21661
The first poc video presenting the sql injection test from ( WordPress Core 5.8.2-'WP_Query' / CVE-2022-21661)
 nu1l0/cve-2024-46636-sqli-modaps
SQL Injection vulnerability in NASA EOSDIS MODAPS due to improper input validation in the `category` parameter. This flaw allows attackers to…
 jjcjgo/cve-2026-38812-ruoyi-sql-injection
Proof-of-concept exploit for CVE-2026-38812, a SQL injection vulnerability in RuoYi v4.8.2 via the /tool/gen/createTable endpoint, enabling…
 xmyronn/cve-2026-7394-sqli
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 msd0pe-1/cve-2023-31714
Proof-of-concept exploit for CVE-2023-31714, a pre-authentication SQL injection in Chitor-CMS < 1.1.2. Automates database enumeration and credential…
 vighneshnair7/cve-2024-48427
Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…
 hamibubu/cve-2023-48084
Python program to dump all the databases, exploiting NagiosXI sqli vulnerability
 smarttfoxx/cve-2025-67261
Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…
 shubham03007/cve-2025-28346
Code-projects Ticket Booking 1.0 is vulnerable to SQL Injection via the > Email parameter
 0xdeku/cve-2021-42668
Proof-of-concept exploit for CVE-2021-42668, a SQL injection in Engineers Online Portal. Uses the vulnerable id parameter in my_classmates.php to…
 longwayhomie/cve-2022-27434
UNIT4 TETA Mobile Edition 29HF13 was discovered to contain a SQL injection vulnerability via the ProfileName parameter in the errorReporting page.
 r4x0r1337/-cve-2012-2661-activerecord-sql-injection-
Proof-of-concept exploit for CVE-2012-2661, an SQL injection vulnerability in Ruby on Rails ActiveRecord. Includes a write-up in Malay demonstrating…
 emad-almousa/cve-2025-24999
Proof-of-concept exploit for CVE-2025-24999, demonstrating privilege escalation in Microsoft SQL Server via the MS_DatabaseManager role.
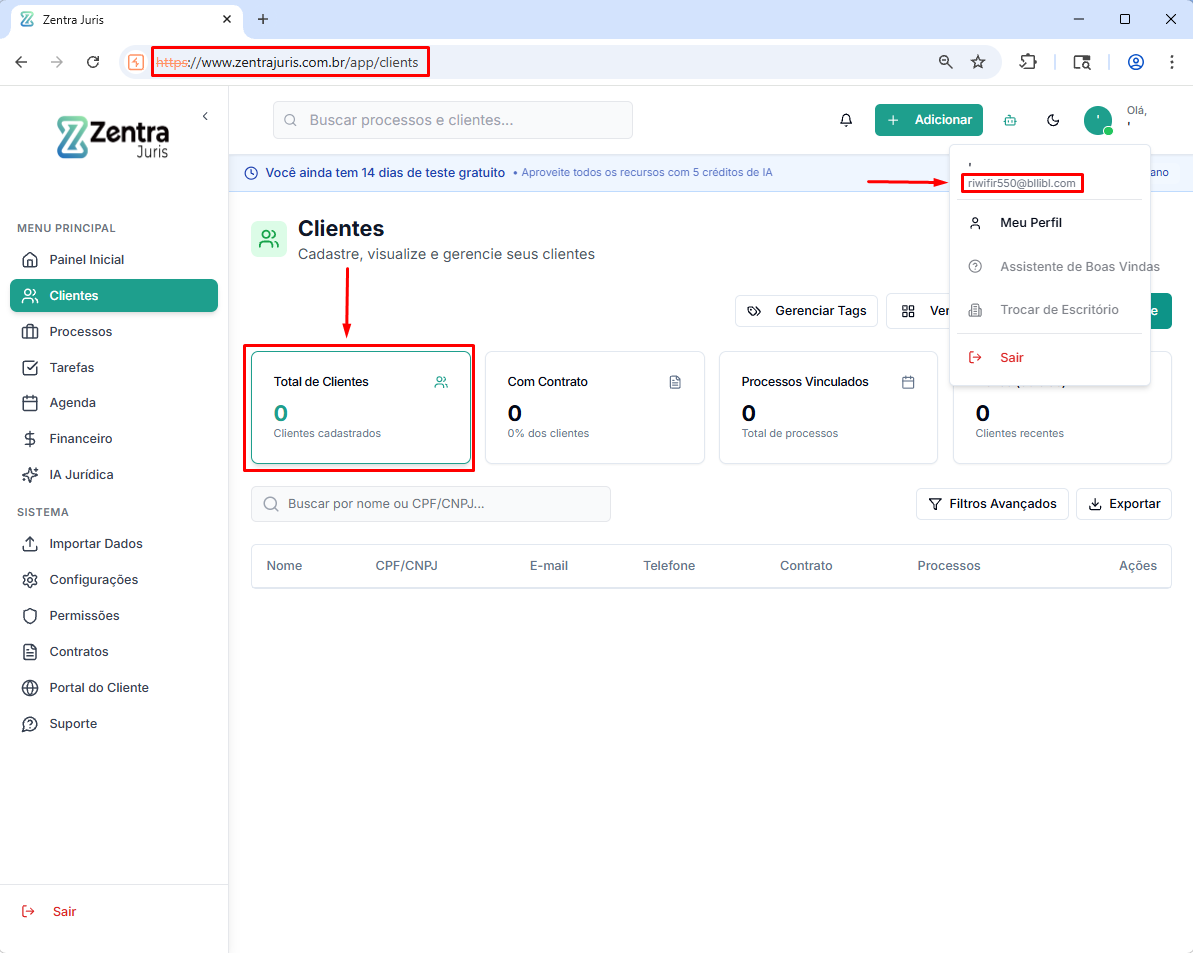 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 kgan0509/cve-2025-63585
Proof-of-concept for a blind time-based SQL injection vulnerability in OSSN's /action/rtcomments/status endpoint, demonstrating arbitrary SQL…