

CVE-2020-7471
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
database-securityeducationlabs-practice+2
1036 years ago
saferman/cve-2020-7471django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
 seccoder-security-lab/jdbc-sqlxml-xxe
h2-jdbc(https://github.com/h2database/h2database/issues/3195) & mysql-jdbc(CVE-2021-2471) SQLXML XXE vulnerability reproduction.
 probiusofficial/cve-2025-14847
poc for CVE-2025-14847
 deepingh0st/cve-2022-28346
Django QuerySet.annotate(), aggregate(), extra() SQL 注入
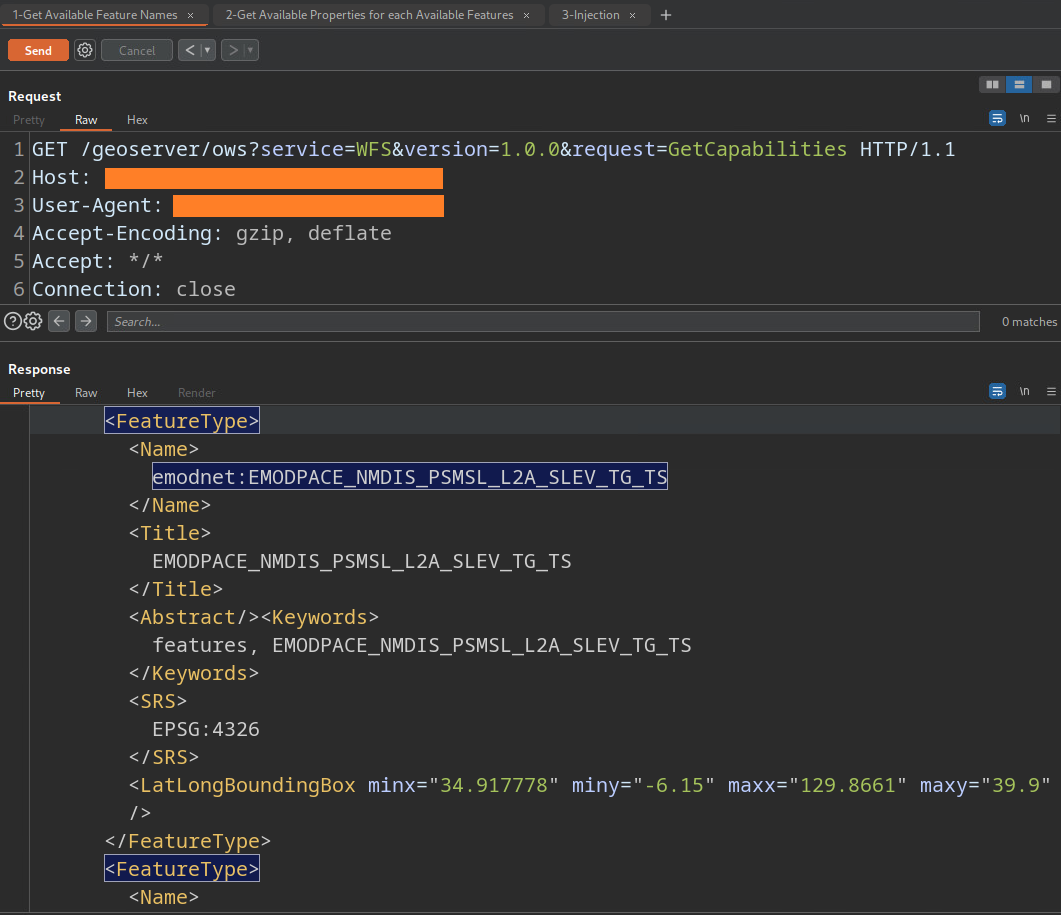 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
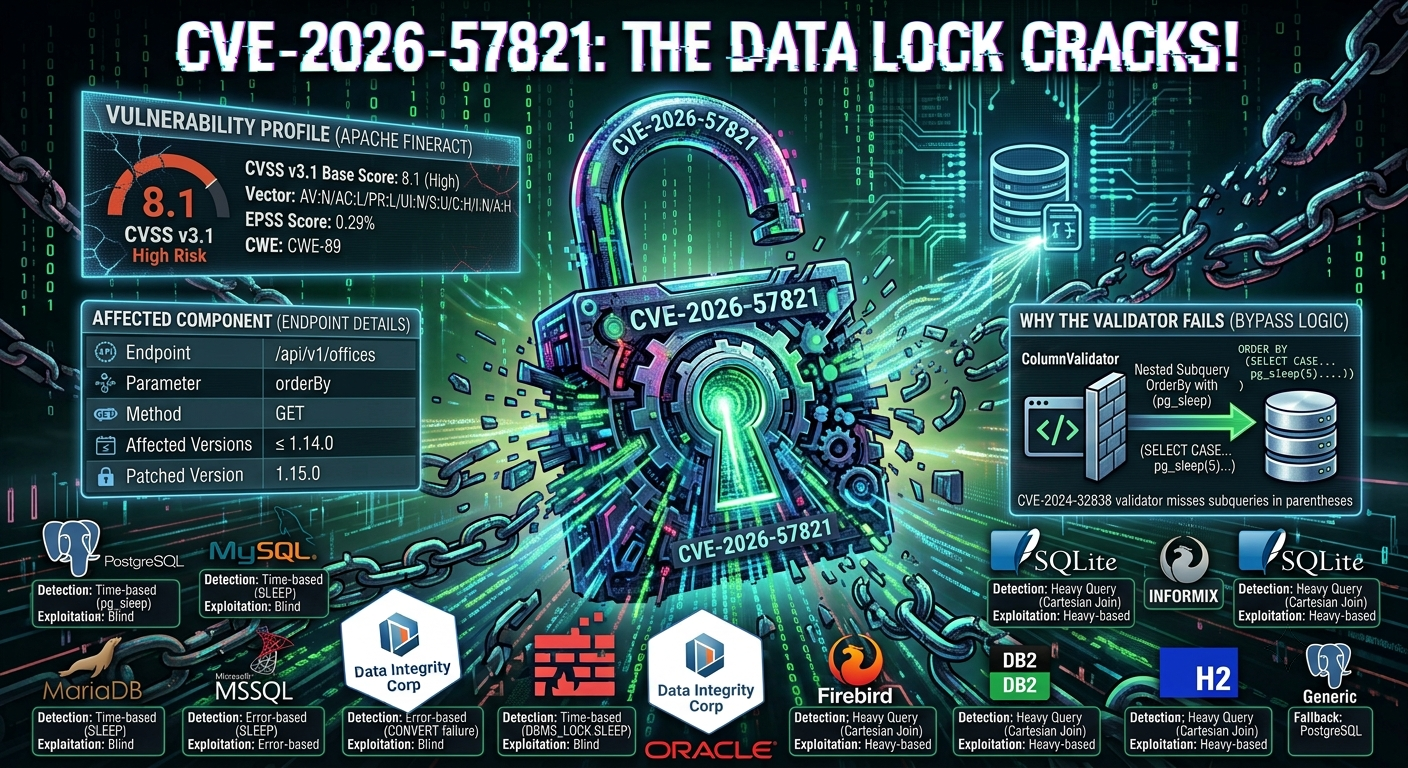 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 0xdaeras/cve-2024-51482-poc
Time-based SQL injection PoC for CVE-2024-51482 in ZoneMinder, with reproducible Docker lab and automated data extraction.
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 sw0rd1ight/cve-2025-57833
Analysis and reproduction of CVE-2025-57833
 george0papasotiriou/cve-2023-3163-sql-injection-prevention
A simple and quick way to check if your SQL Developer by Oracle is vulnerable to SQL Injection (CVE-2023-3163), most commonly occurs when SQL…
 hunt-benito/pgadmin-ai-assistant-sql-injection-cve-2026-17351-lexer-differential-bypass
Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…
 anusha-khan29/cve-2025-70149-sql-injection
Security research project — SQL Injection vulnerability exploitation and mitigation
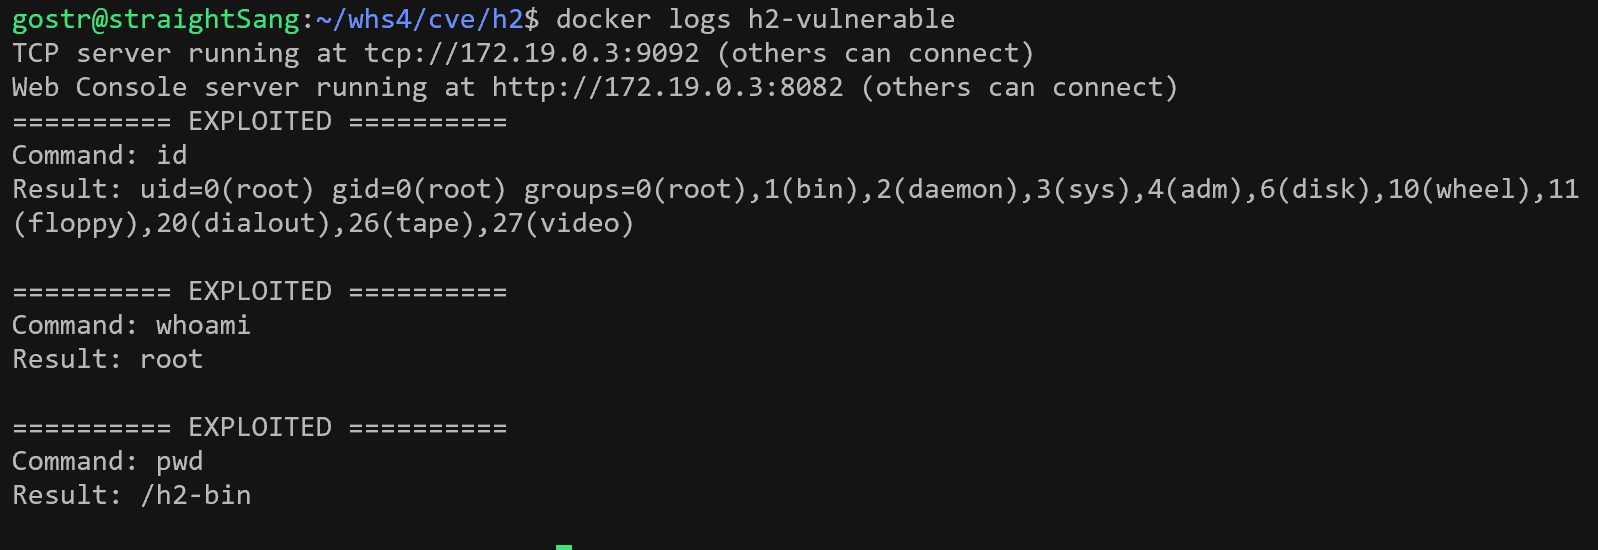 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221
 luckybool1020/cve-2018-8045
Joomla内核SQL注入漏洞原理、docker及poc[基于pocsuite框架]
 secoba/djvul_stringagg
Django StringAgg SQL Injection (CVE-2020-7471)
 sncker/cve-2020-7471
CVE-2020-7471 Potential SQL injection via StringAgg(delimiter)
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.