
ldapsdk
 pingidentity/ldapsdk
UnboundID LDAP SDK for Java
api-securityauthentication-authorizationdatabase-security+3
pingidentity/ldapsdkUnboundID LDAP SDK for Java
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 imbas007/poc-cve-2026-58048
Security research project
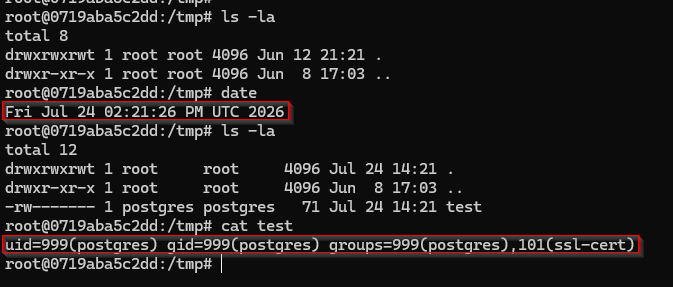 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 hakaioffsec/cve-2026-40083
Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
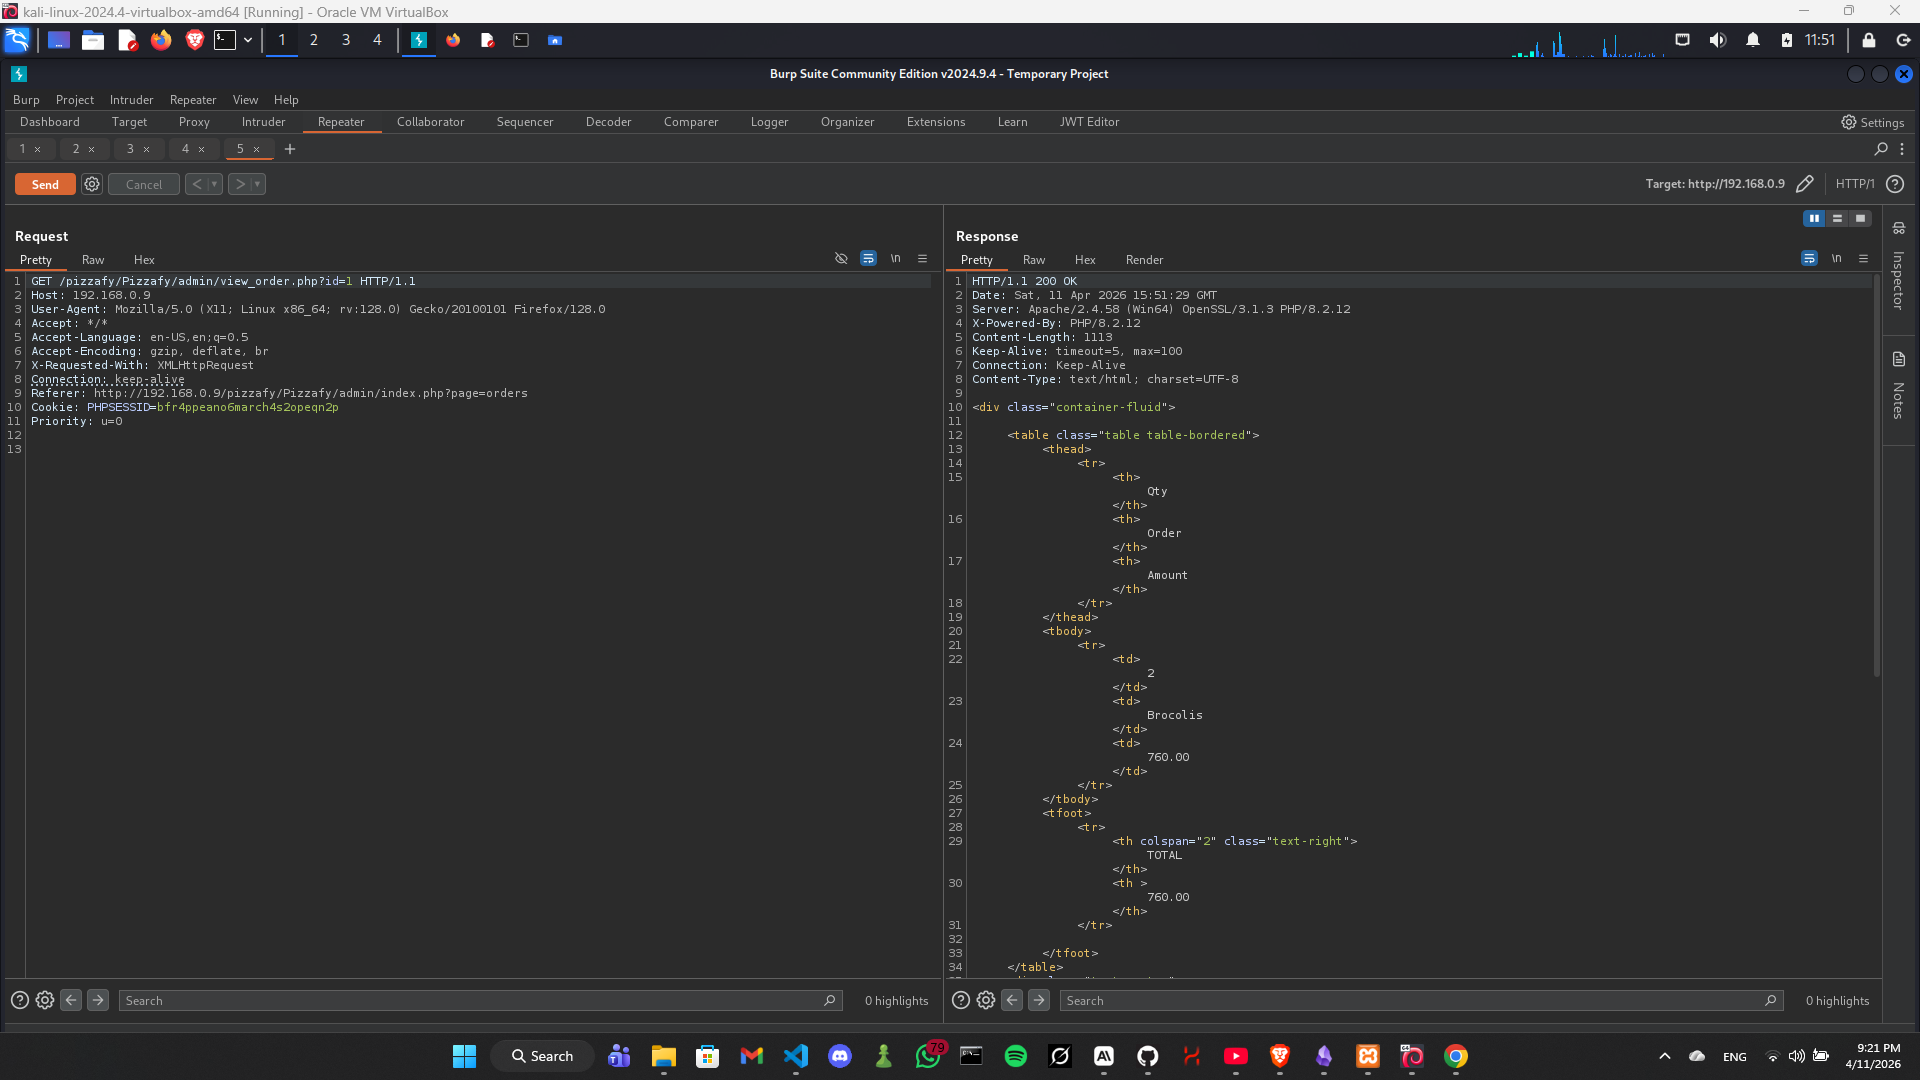 xmyronn/cve-2026-7394-sqli
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
 joakimbulow/cve-2026-1337
CVE-2026-1337 - Neo4j - Log Injection
 cybersrmutl/cve-2019-9193-postgresql-rce
Python exploit script for CVE-2019-9193, enabling remote code execution on vulnerable PostgreSQL databases via authenticated command injection.
 netw0rk7/cve-2019-9193-home-lab
This lab simulates CVE-2019-9193 - PostgreSQL COPY FROM PROGRAM RCE
 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 m0b1u3/cve-2025-50565
Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.
 abdullah4eb/cve-2025-50383
A low-privileged user can exploit this via a crafted order_by parameter, causing time-based blind SQL injection.
 oiyl/cve-2025-46171
Writeup of a Denial of Service vulnerability in the vBulletin 3.8.7 friends list.
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 randomrobbiebf/cve-2023-41652
RSVPMarker <= 10.6.6 - Unauthenticated SQL Injection
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…