NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.8k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
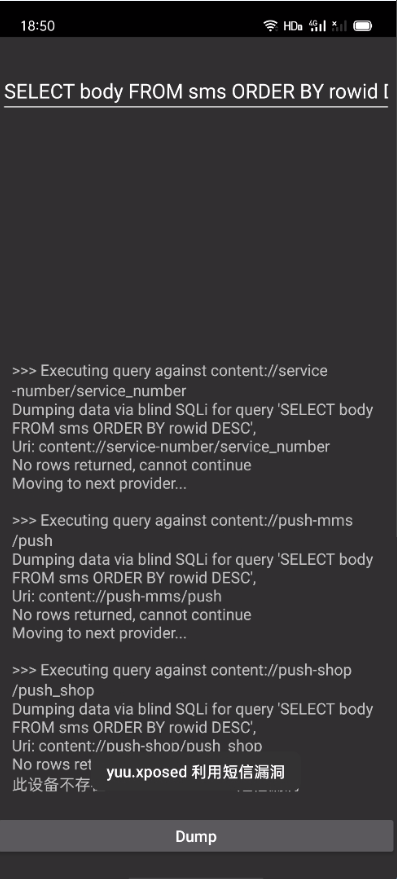 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
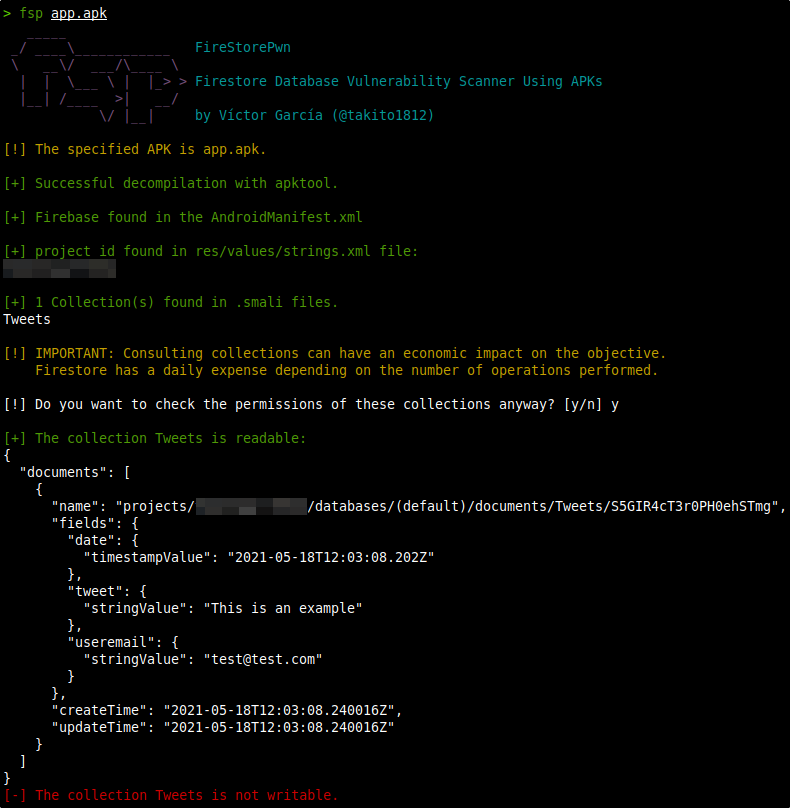 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
 secforce/cve-2008-1613
RedDot CMS versions 7.5 Build 7.5.0.48 and below full database enumeration exploit that takes advantage of a remote SQL injection vulnerability in…
 secforce/cve-2008-5416
Microsoft SQL Server sp_replwritetovarbin Memory Corruption via SQL Injection