CVE-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Security research project

CVE-2026-1337 - Neo4j - Log Injection

Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…

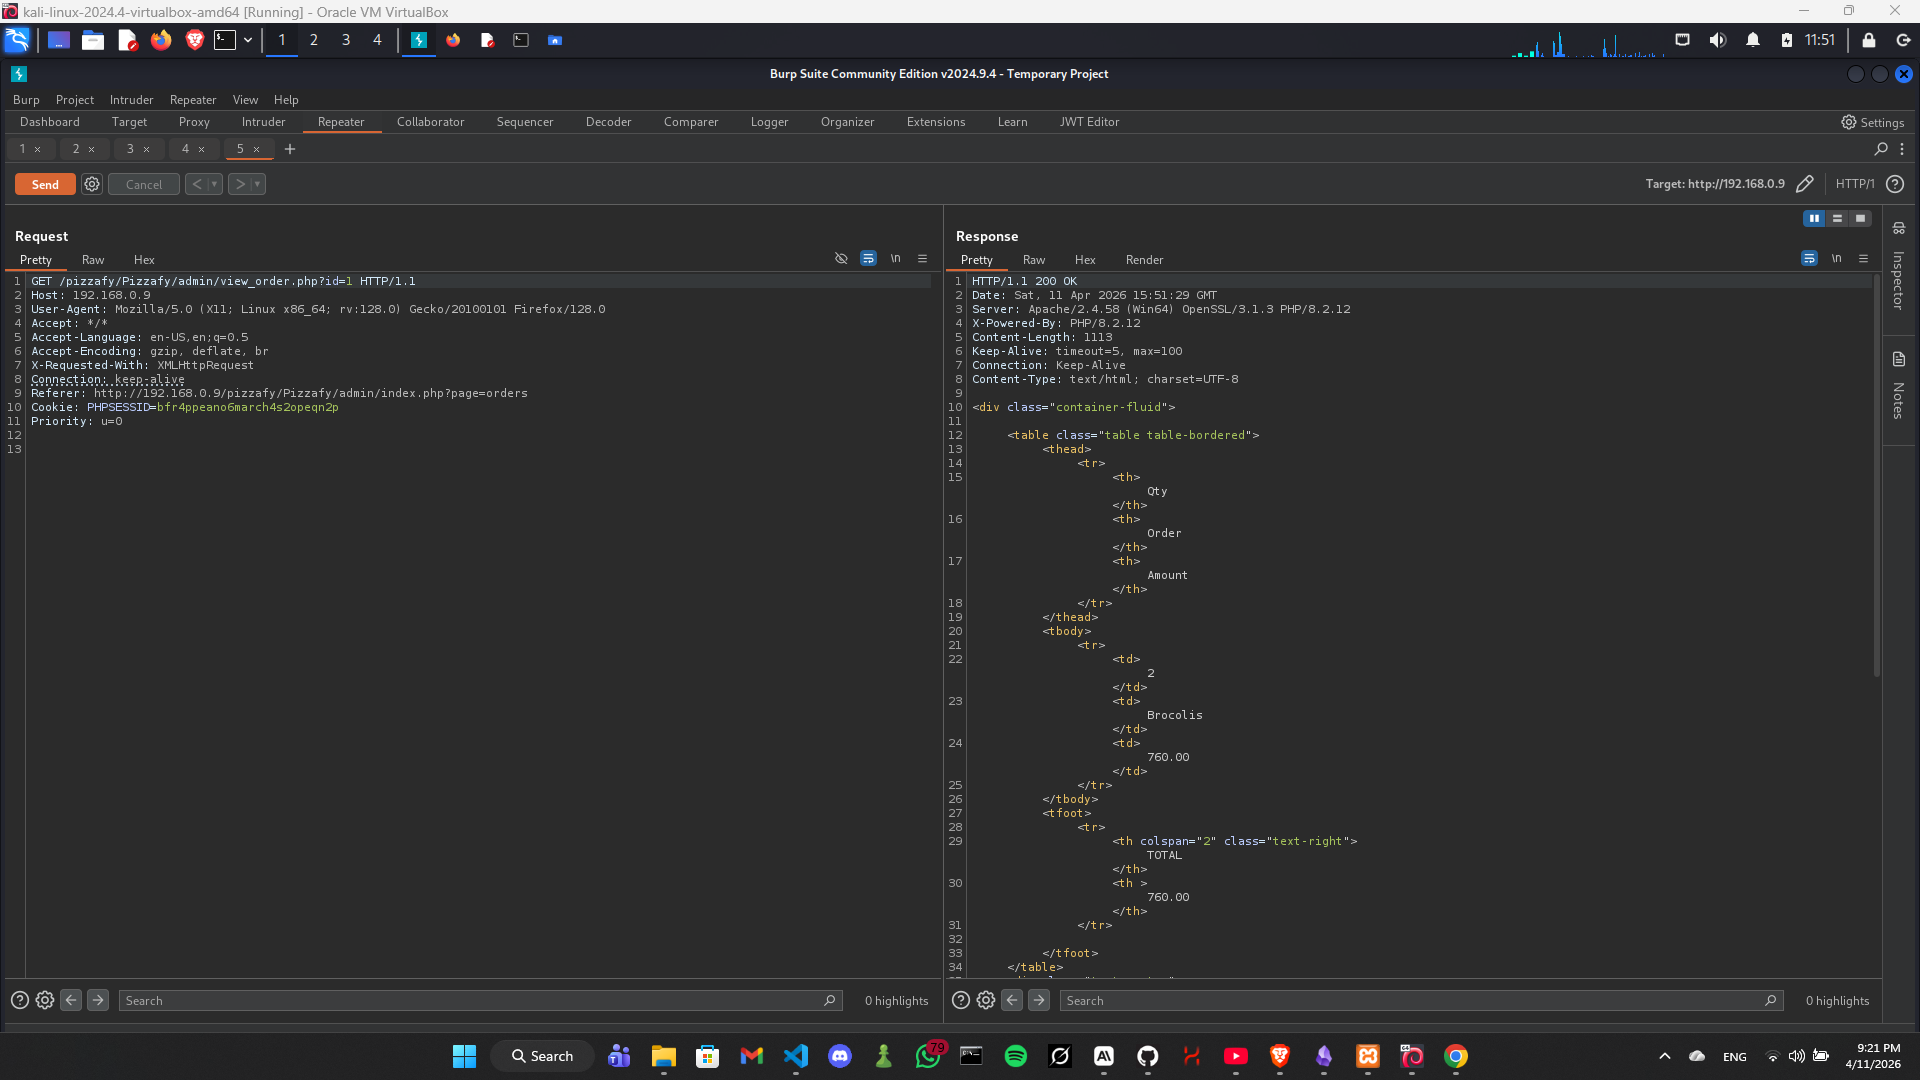
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…

MySQL 4.x/5.0 (Linux) - User-Defined Function (UDF) Dynamic Library (2) automation script.

Database authenticated code execution

UnboundID LDAP SDK for Java

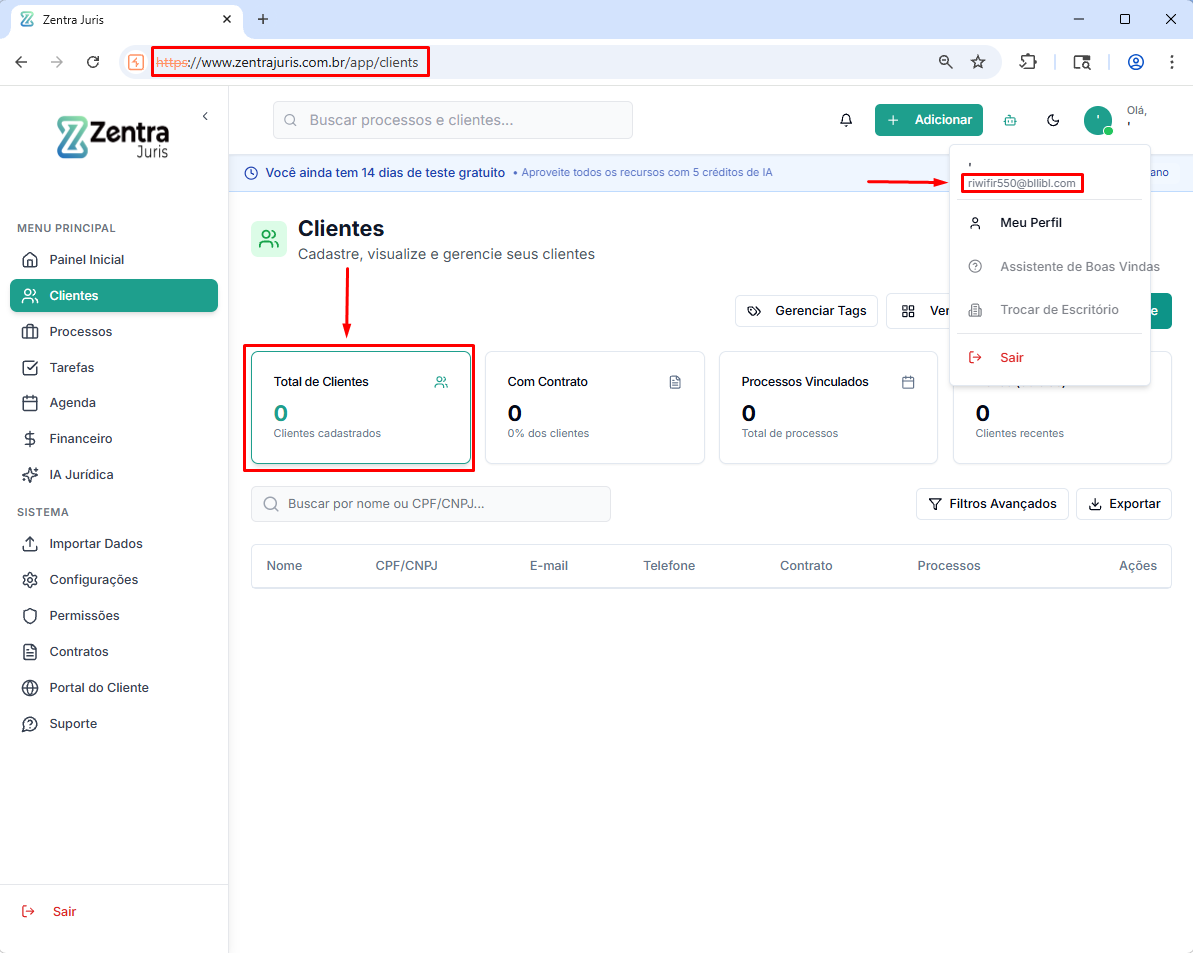
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…

Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.

Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…

Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…

Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…

RSVPMarker <= 10.6.6 - Unauthenticated SQL Injection

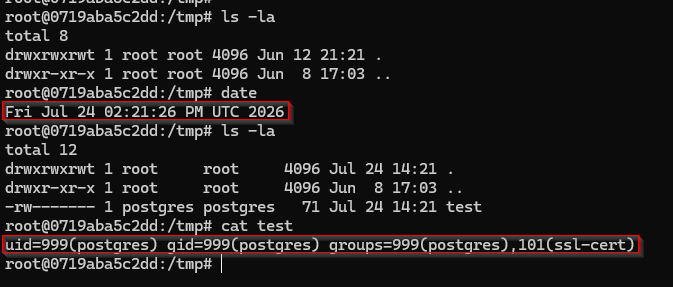
Python exploit script for CVE-2019-9193, enabling remote code execution on vulnerable PostgreSQL databases via authenticated command injection.

This lab simulates CVE-2019-9193 - PostgreSQL COPY FROM PROGRAM RCE

CVE-2023-45503 Reference

OpenEMR Security issue