
custom-oscp-tooling
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
wattocyber/custom-oscp-toolingOSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)

 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
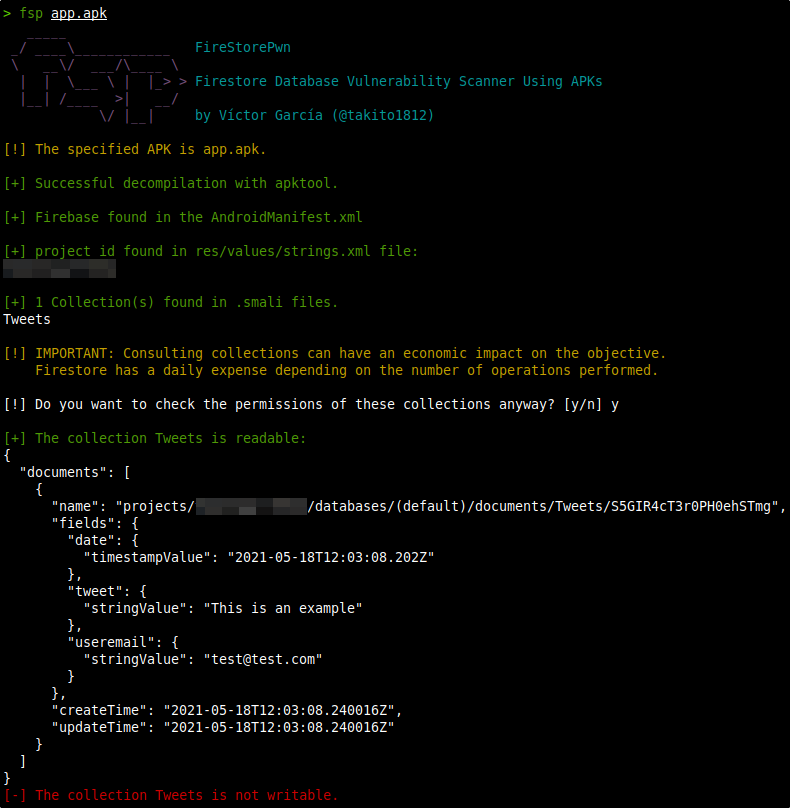 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
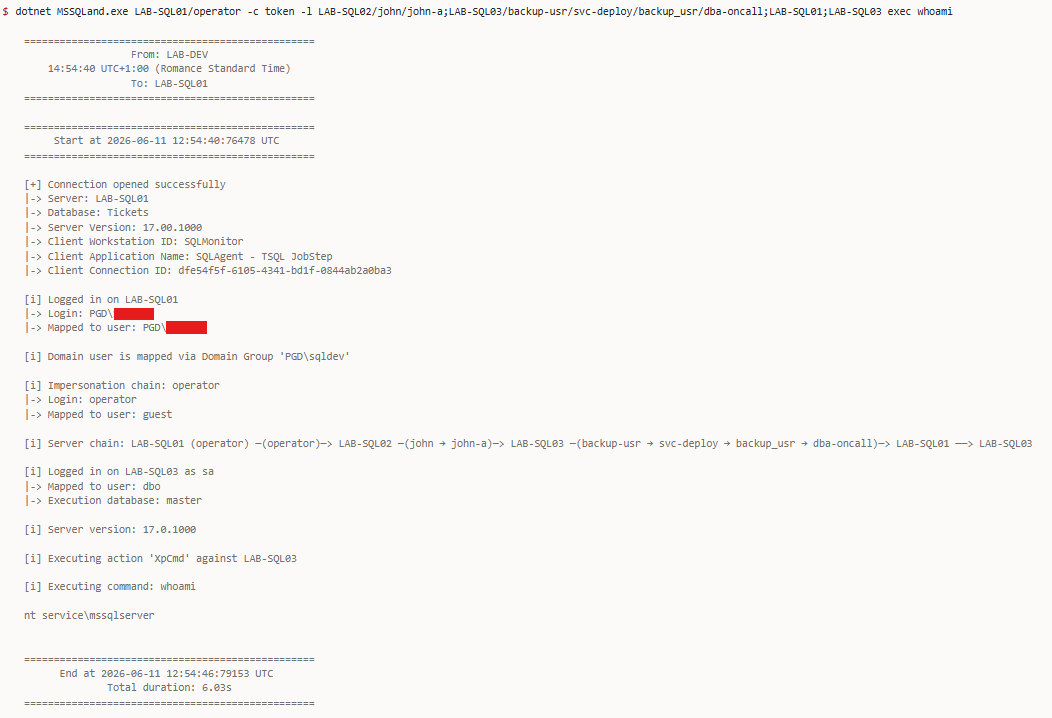 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
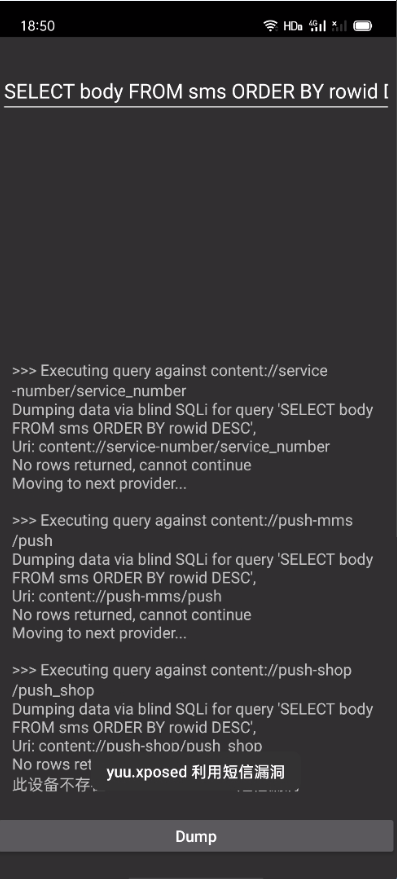 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案