
CVE-2026-0603
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
database-securityeducationexploitation+4
1
yym8538/cve-2026-0603Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
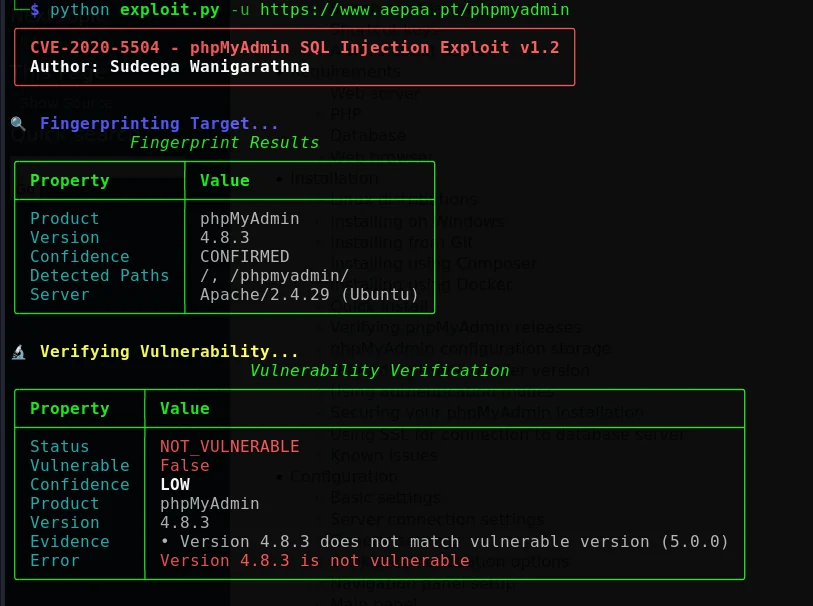 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 eqstlab/cve-2026-34220
SQL Injection vulnerability in MikroORM
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 eqstlab/cve-2026-0603
Hibernate ORM Second-Order SQL Injection
 sysdream/pysqli
Python SQL injection framework
 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference
 ivansmc/cve-2025-10351-poc
Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 torque59/nosql-exploitation-framework
A Python Framework For NoSQL Scanning and Exploitation
 torque59/nosqlpot
The NoSQL Honeypot Framework