
mysql-mysqldump-tab-path
 abraxas/mysql-mysqldump-tab-path
MySQL Community Server 26.7.0 - High - mysqldump --tab path leftover - client file write
database-securityexploitationinformation-gathering+4
abraxas/mysql-mysqldump-tab-pathMySQL Community Server 26.7.0 - High - mysqldump --tab path leftover - client file write
 abraxas/sqlite-wal-pagesize
SQLite 3.53.4 - High - Local - Info leak - WAL/DB page-size mismatch uninitialized page tail
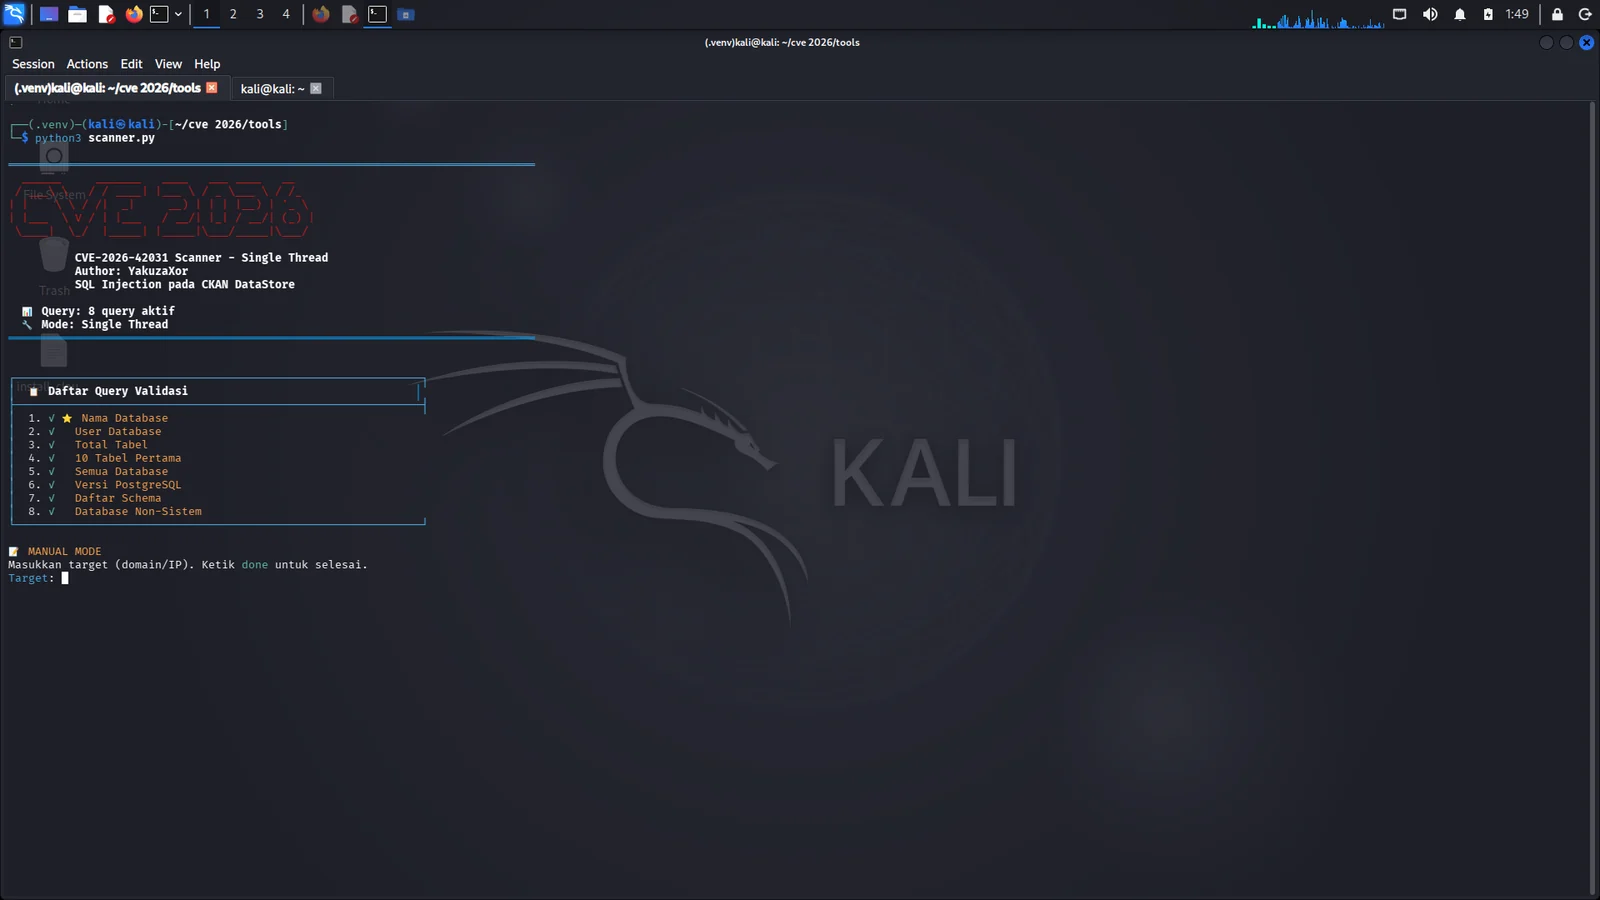 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 emad-almousa/cve-2021-2175
Proof-of-concept exploit for CVE-2021-2175, an Oracle Database Vault metadata exposure vulnerability, demonstrating unauthorized access to sensitive…
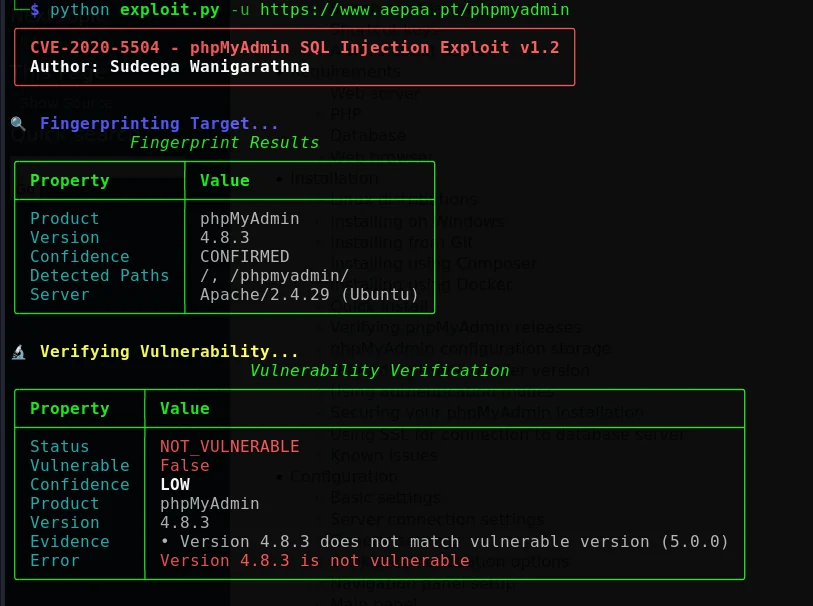 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 0xblackash/cve-2026-72898
CVE-2026-72898
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 0xdea/exploits
Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…
 randomrobbiebf/cve-2024-55978
Code Generator Pro <= 1.2 - Unauthenticated SQL Injection
 randomrobbiebf/cve-2024-12404
CF Internal Link Shortcode <= 1.1.0 - Unauthenticated SQL Injection
 randomrobbiebf/cve-2024-51818
Fancy Product Designer <= 6.4.3 - Unauthenticated SQL Injection