
cakephp-collate-sqli
 abraxas/cakephp-collate-sqli
CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
database-securityexploitationpenetration-testing+4
abraxas/cakephp-collate-sqliCakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 abraxas/phpmyadmin-auth-plugin-unquoted
phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
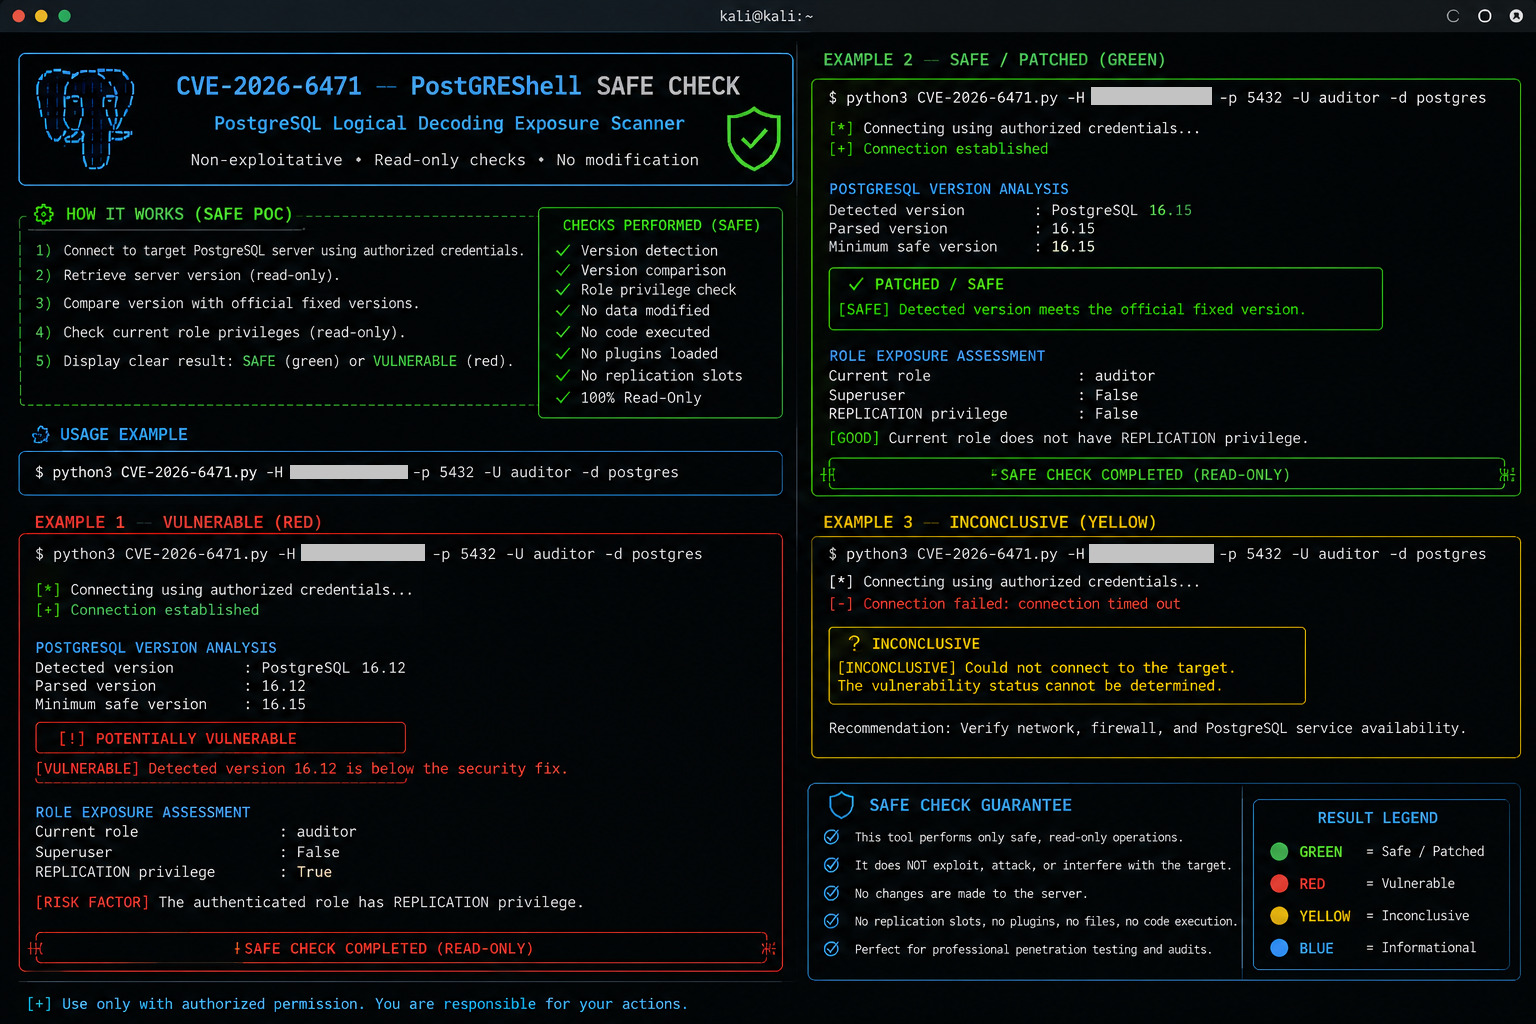 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
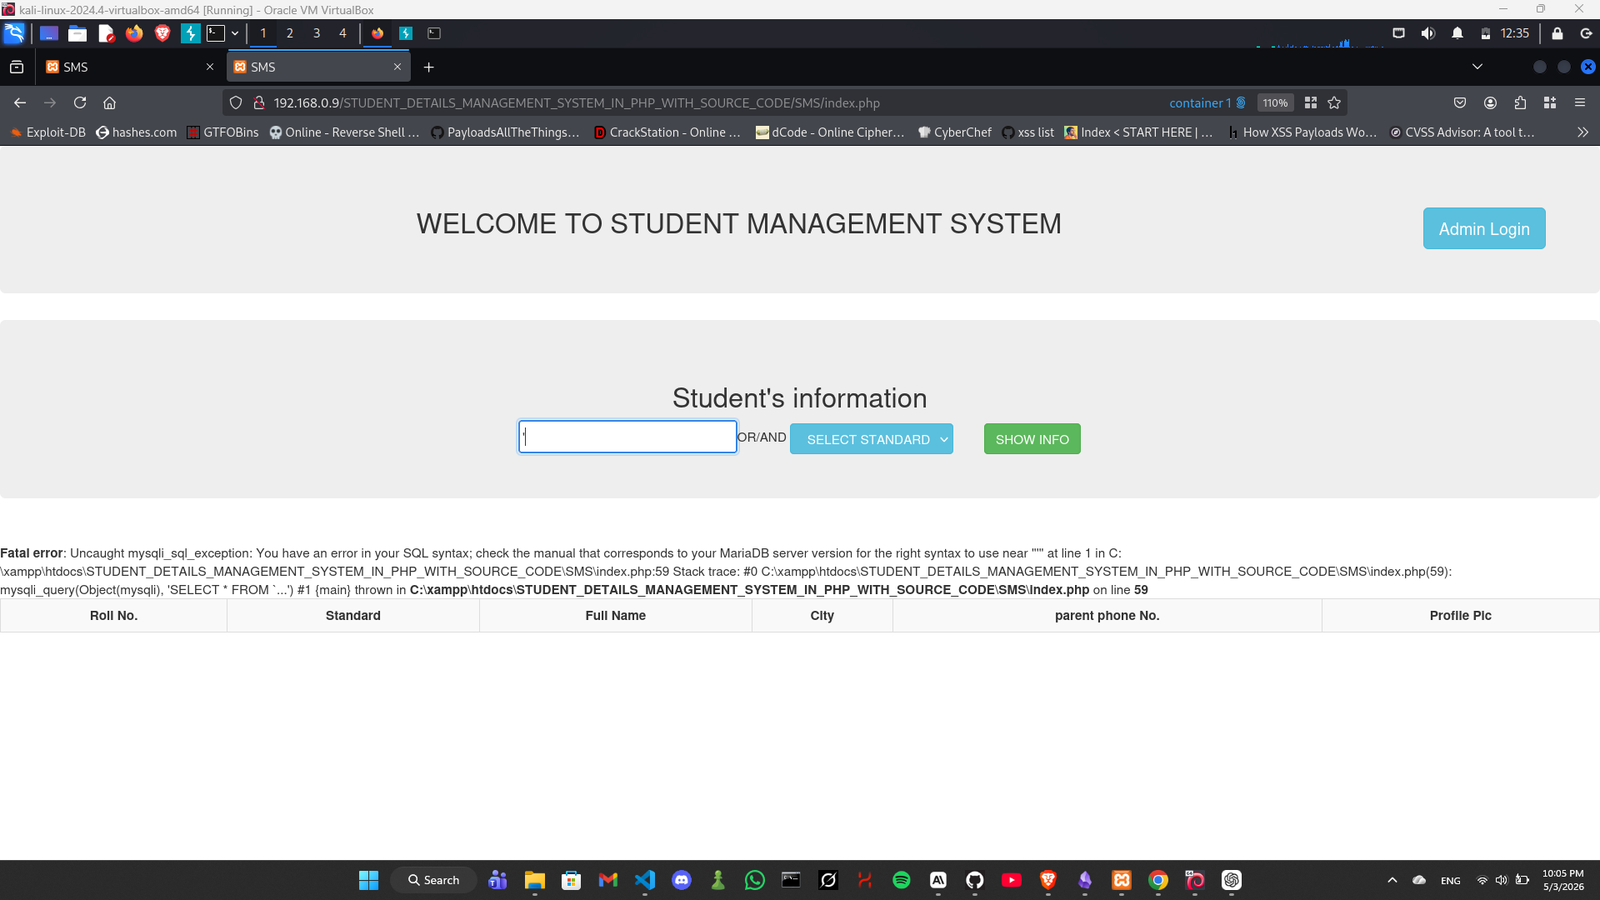 xmyronn/cve-2026-10110-sqli
Proof-of-concept for unauthenticated SQL injection in Student Details Management System 1.0, demonstrating UNION-based data extraction and credential…
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
 romain-deperne/cve-2026-32247
Cypher injection in Graphiti via unsanitized node_labels — CVE-2026-32247 / CVSS 8.1