

foremost
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
data-recoverydigital-forensicsdisk-forensics+2
380
korczis/foremostFile carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
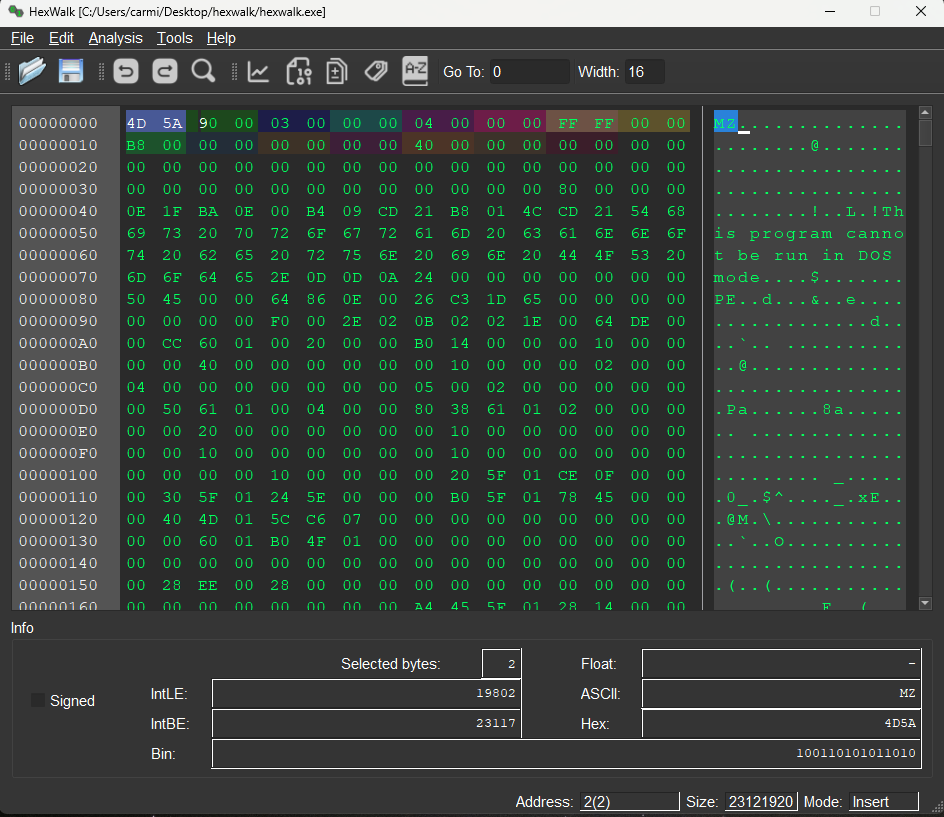 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 permanet/permanet
Cryptographically verifiable web archiving. Playwright capture → SHA-256 Merkle hash → Bitcoin-anchored OpenTimestamps → permanent Arweave storage.
 yuejd/ios_restriction_passcode_crack---python-version
Crack ios Restriction PassCode in Python
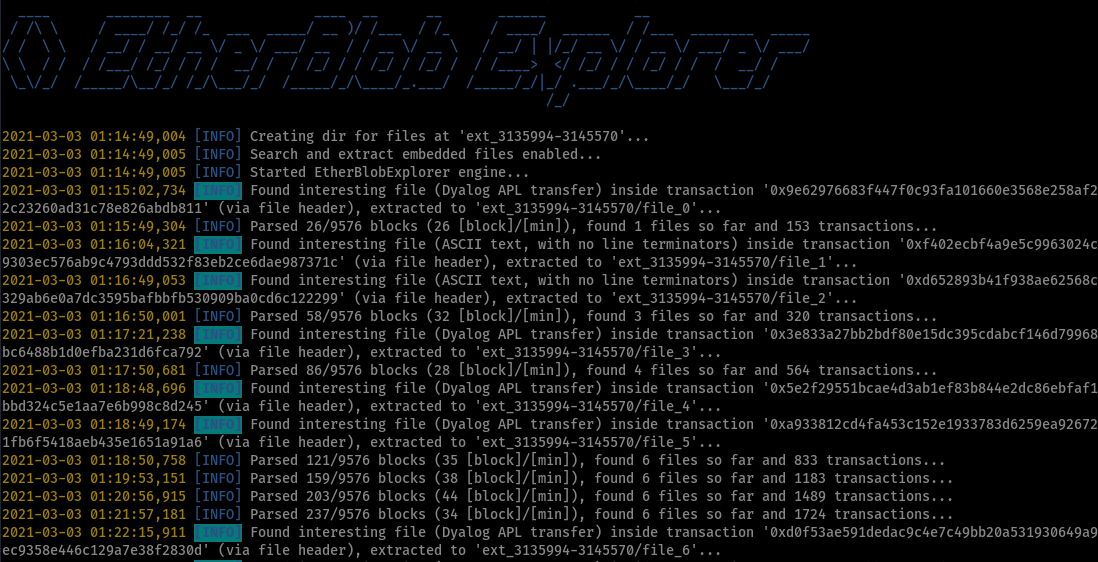 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
 jschicht/logfileparser
Parser for $LogFile on NTFS
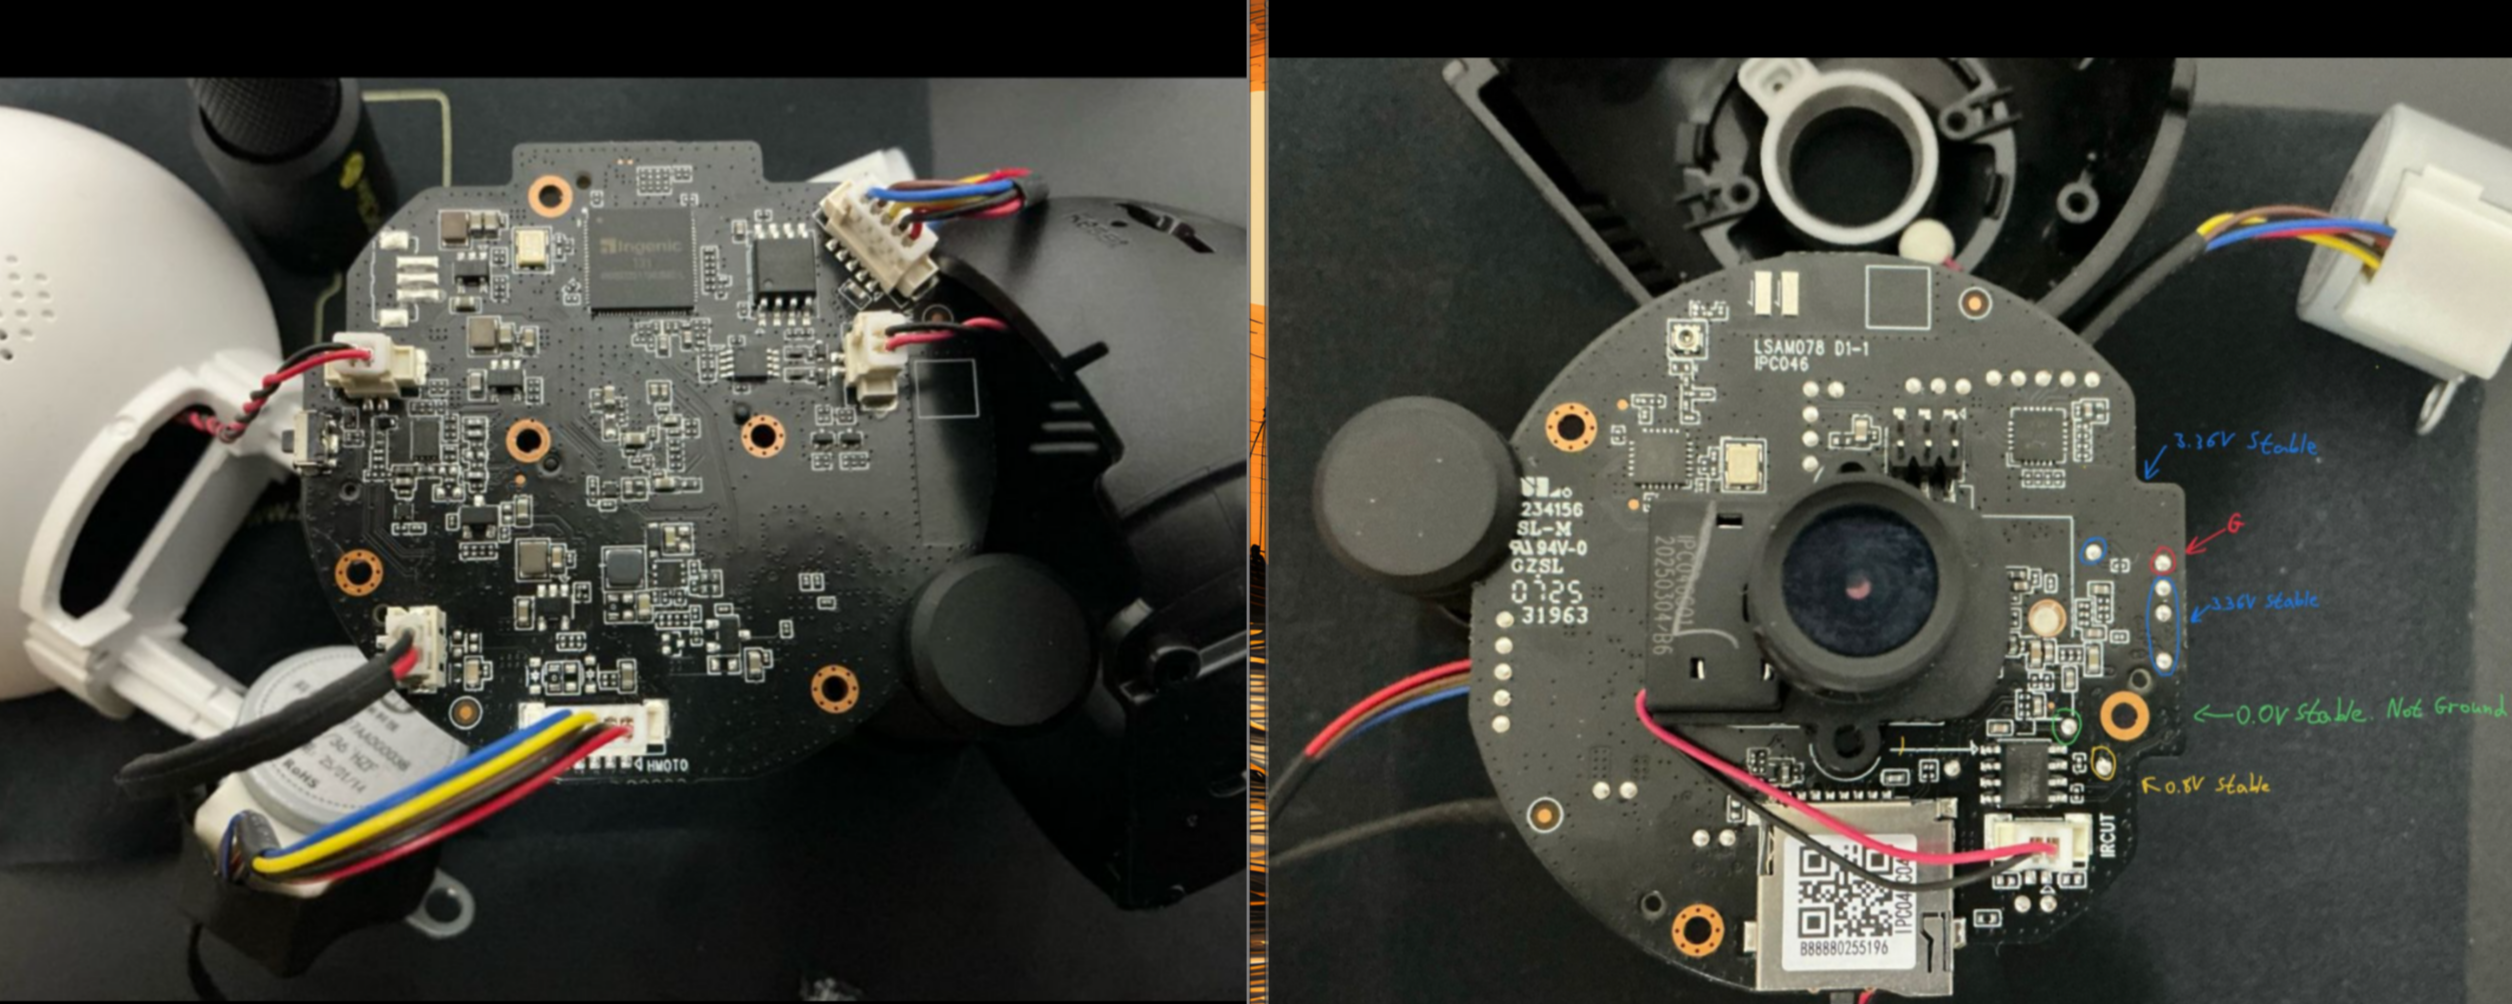 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
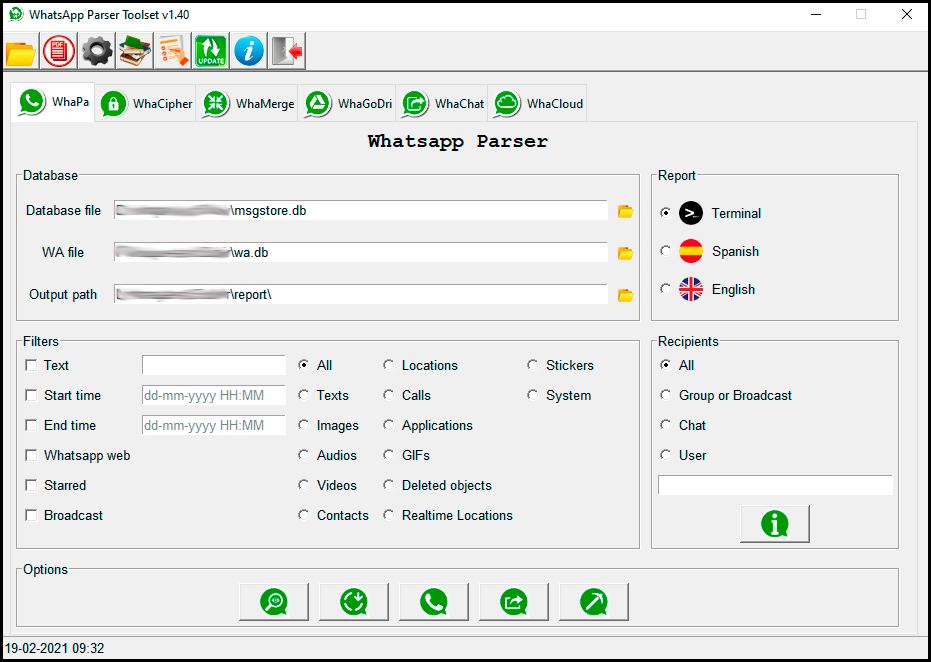 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 nowsecure/android-forensics
Open source Android Forensics app and framework
