
dwipe
 joedefen/dwipe
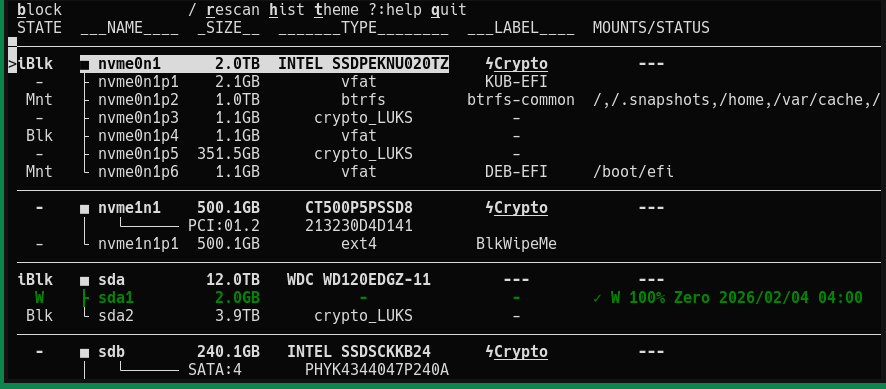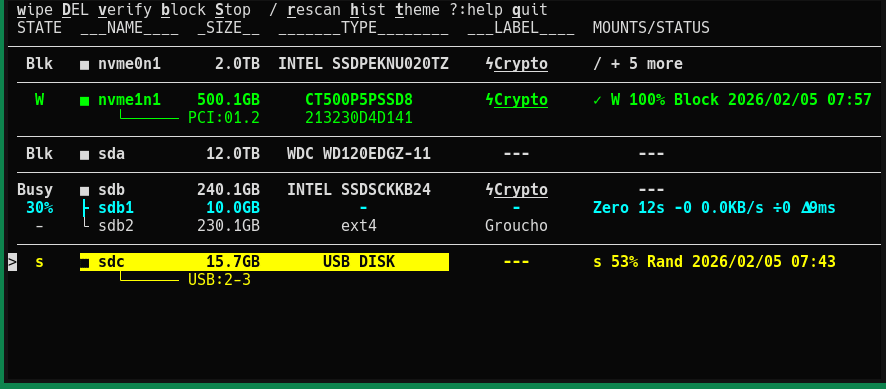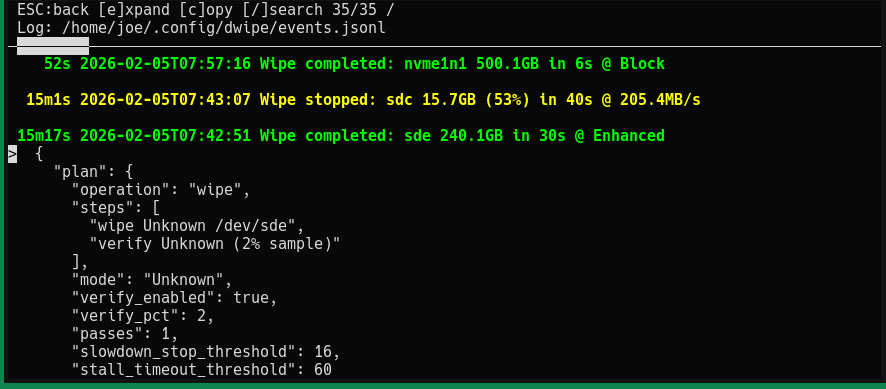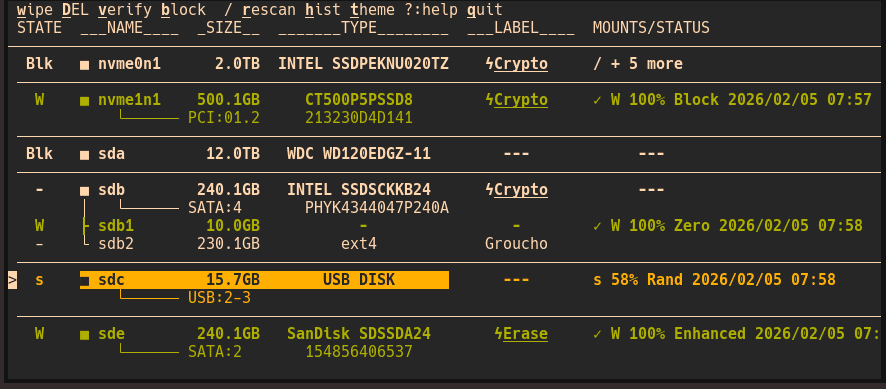
Tool to securely and efficiently wipe devices and partiitions for Linux
data-recoveryencryption-decryption-toolsforensics+3
joedefen/dwipeTool to securely and efficiently wipe devices and partiitions for Linux
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 jschicht/rawcopy
Commandline low level file extractor for NTFS
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
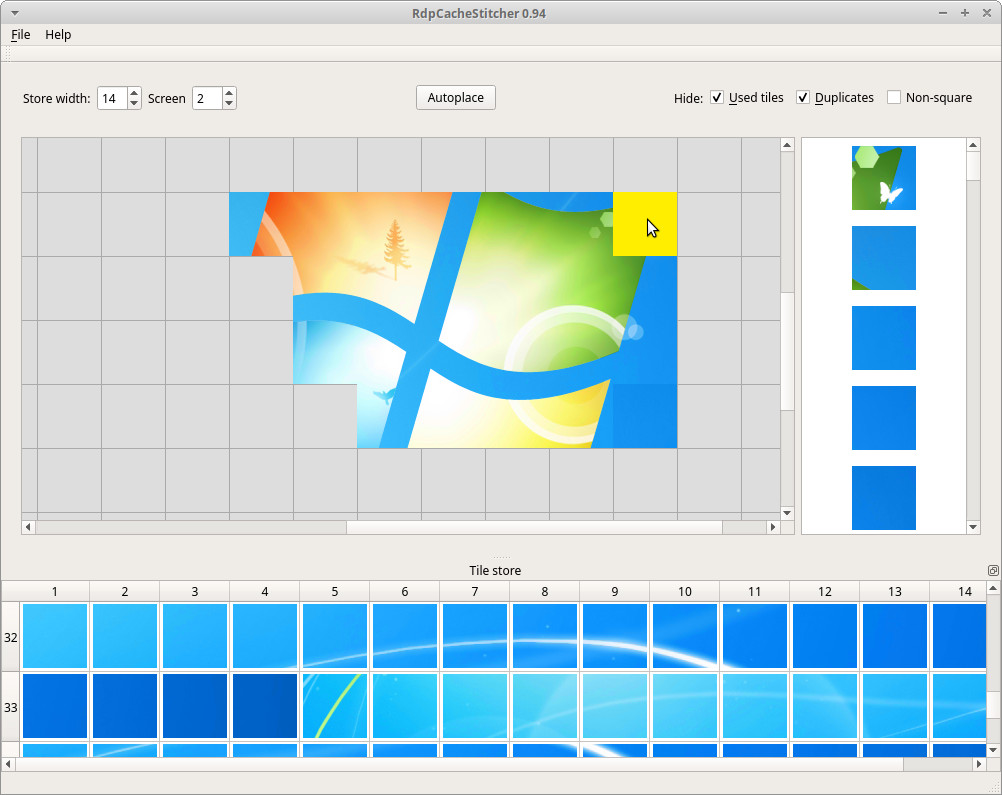 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
 jschicht/logfileparser
Parser for $LogFile on NTFS
 redrum0381/ataboy
ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 0xpoly/centry
Panic button for protection against cold boot attacks
 packetlss/android-locdump
android location service cache dumper
 libyal/libfwsi
Library to access the Windows Shell Item format
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.