

 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
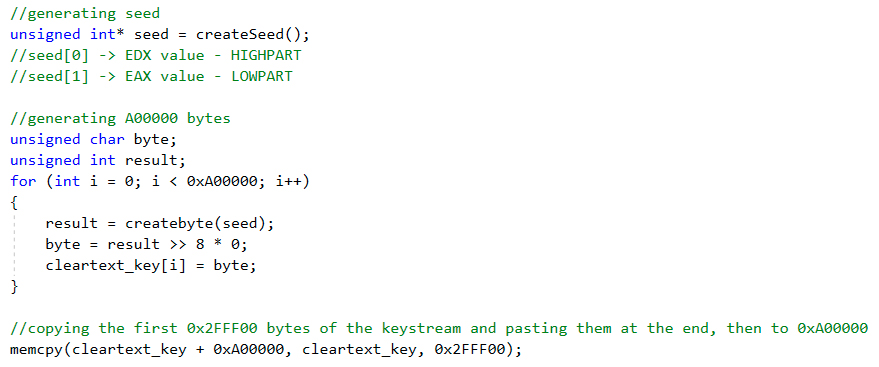 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
 politoinc/xwfacropalypse
X-Ways Acropalypse extension detects CVE-2023-21036 in common images
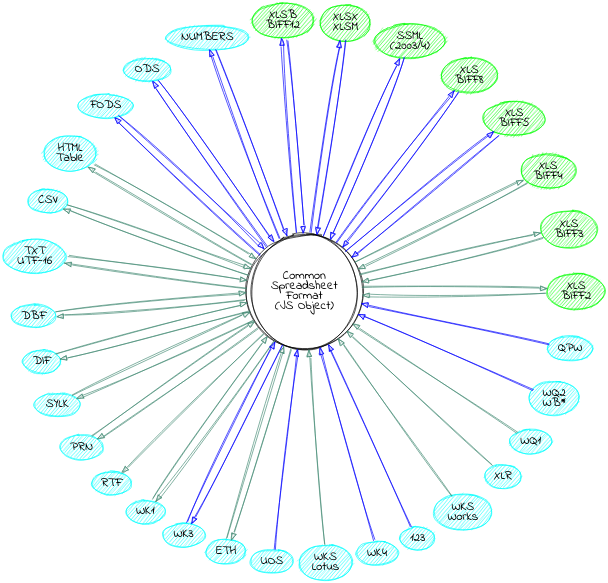 weareu/xlsx
SheetJS xlsx 0.18.5 fork with CVE-2023-30533 and CVE-2024-22363 fixes
 qixils/anticropalypse
Discord bot for mitigating the aCropalypse vulnerability (CVE-2023-21036, CVE-2023-28303) by retroactively deleting vulnerable images
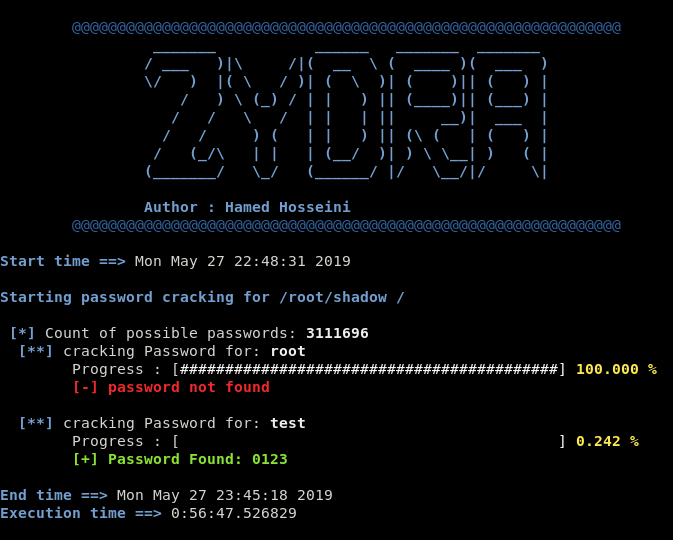 hameda2/zydra
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
 ustayready/physical-analyzer-scripts
Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality
 g4sp4rcs/cve-2023-32784-password-combinator-fixer
After using the KeePass password dumper maybe some character parsed as ● is incorrect and you want to know the real character