
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
146 results
hashdeep preview

hashdeep

GitHubjessek/hashdeep

Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
data-recoverydigital-forensicsforensics+1
788
9 years ago
filekey preview

filekey

GitHubrockwellshah/filekey

Offline, open-source web app for passkey-based file encryption and sharing. AES-256-GCM/HPKE, no cloud, no accounts; encrypt to recipients with…
authenticationcryptographydata-recovery+2
48427 days ago
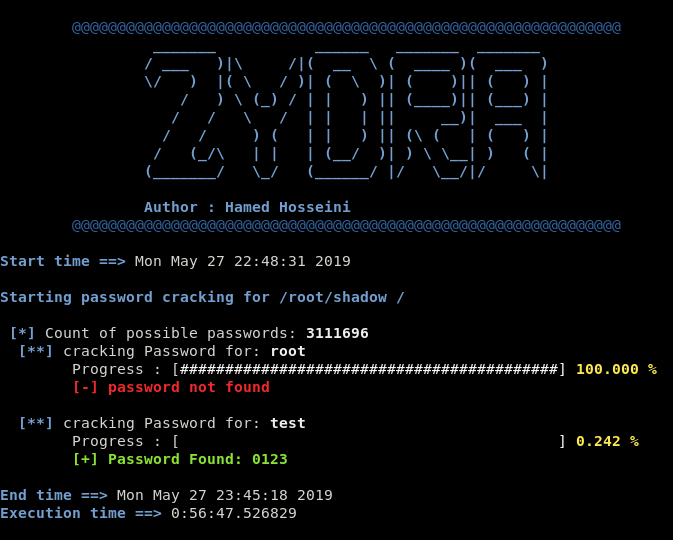
Zydra preview

Zydra

GitHubhameda2/zydra

Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
data-recoverypassword-attackspassword-cracking
4346 years ago
usbsas preview

usbsas

GitHubcea-sec/usbsas

Tool and framework for securely reading untrusted USB mass storage devices.
data-recoverydefensive-toolsdigital-forensics+1
3761 day ago
libewf preview

libewf

GitHublibyal/libewf

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
data-recoverydigital-forensicsdisk-forensics+1
3162 months ago
libfsntfs preview

libfsntfs

GitHublibyal/libfsntfs

Library and tools to access the Windows New Technology File System (NTFS)
data-recoverydigital-forensicsdisk-forensics+1
2371 day ago
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

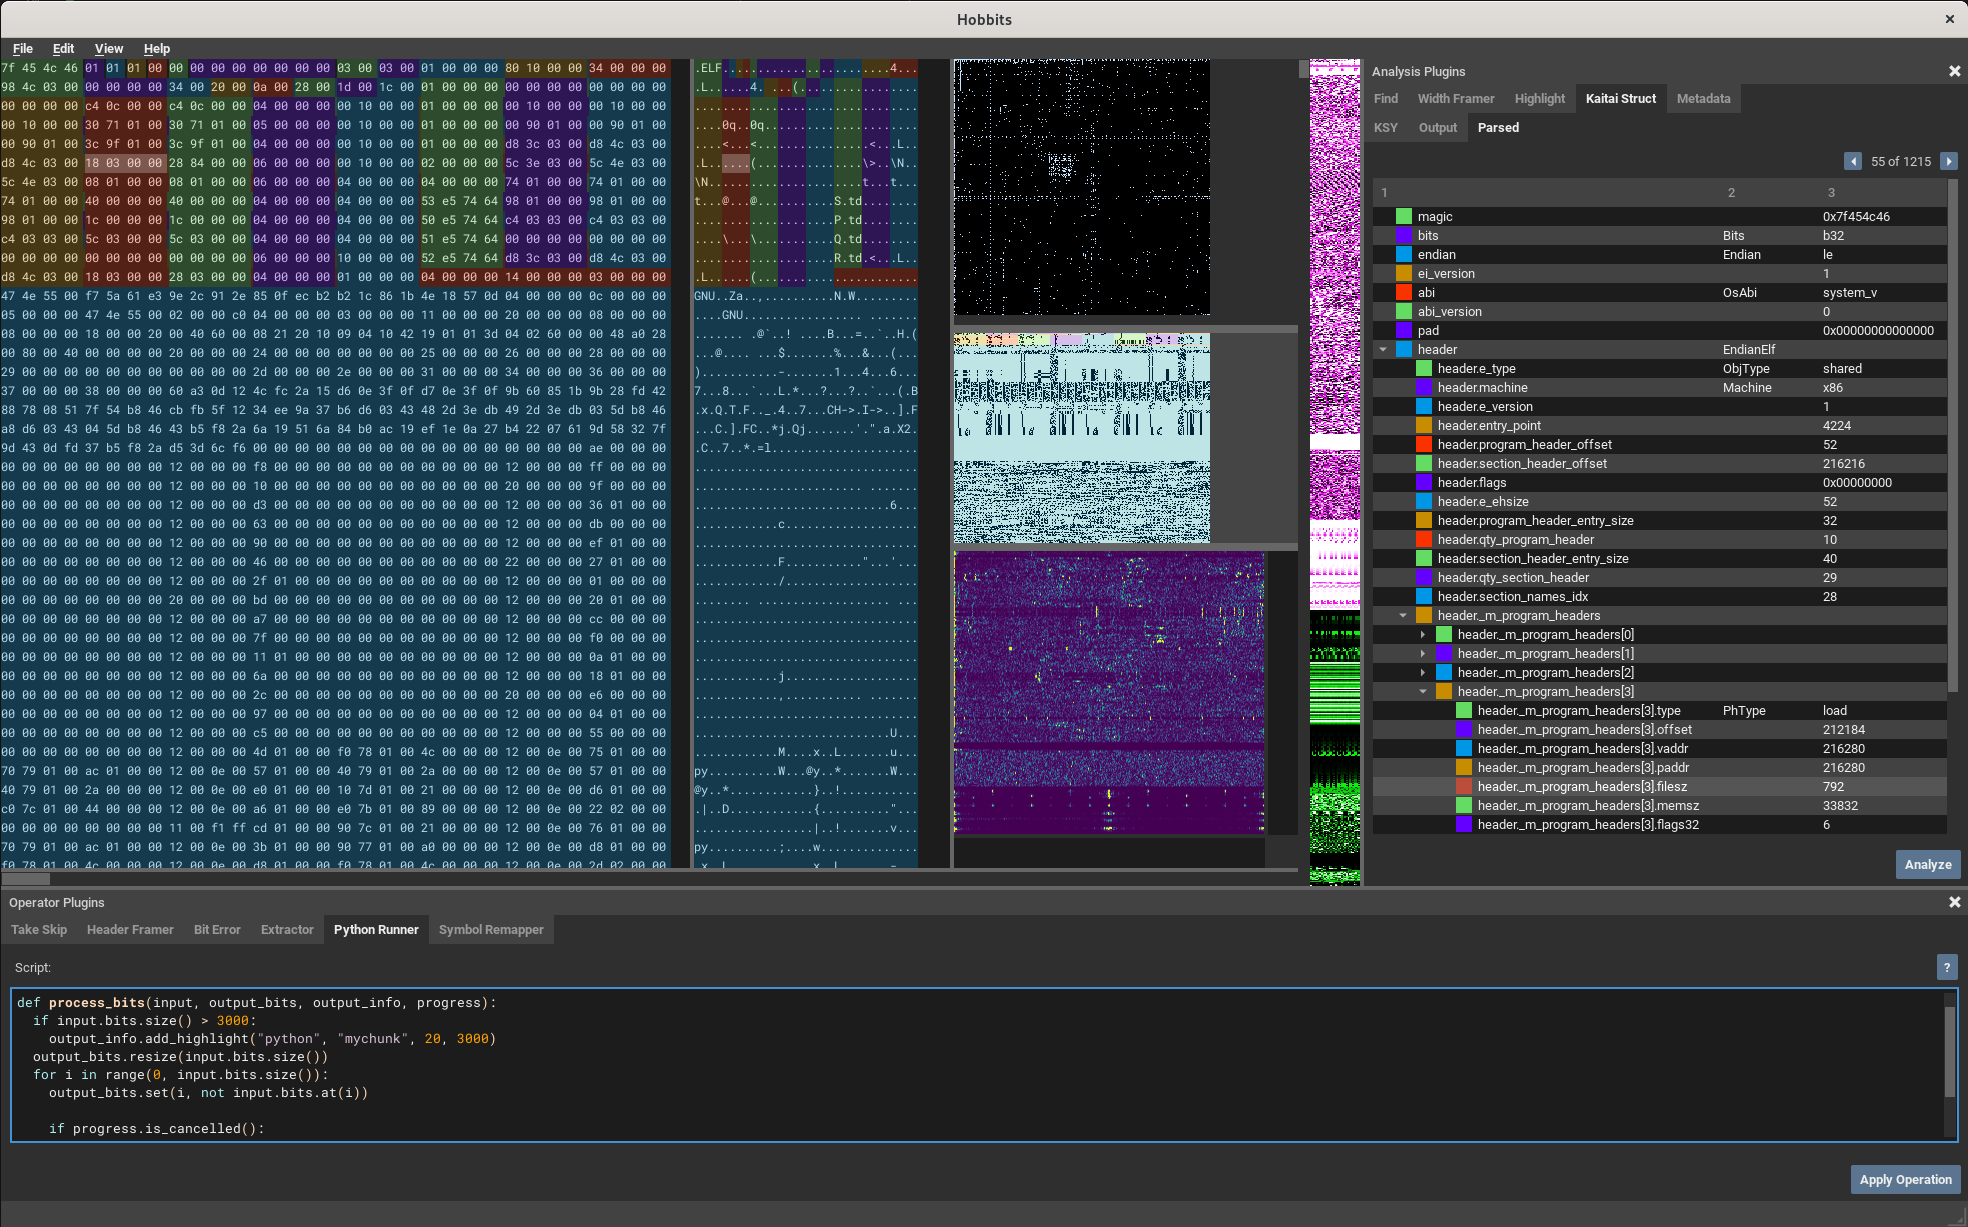
A multi-platform GUI for bit-based analysis, processing, and visualization

binary-analysisdata-recoveryforensics+1
7511 year ago
DroneXtract preview

DroneXtract

GitHubang13t/dronextract

Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
anomaly-detectiondata-recoverydigital-forensics+3
3693 years ago
libvmdk preview

libvmdk

GitHublibyal/libvmdk

Library and tools to access the VMware Virtual Disk (VMDK) format
data-recoverydigital-forensicsdisk-forensics
18611h 35m ago
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format
data-recoverydigital-forensicsdisk-forensics+1
14611h 48m ago
RawCopy preview

RawCopy

GitHubjschicht/rawcopy

Commandline low level file extractor for NTFS
data-recoverydigital-forensicsdisk-forensics+1
3247 years ago
libvshadow preview

libvshadow

GitHublibyal/libvshadow

Library and tools to access the Volume Shadow Snapshot (VSS) format
data-recoverydigital-forensicsdisk-forensics+2
1171 day ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
13225 days ago
LogFileParser preview

LogFileParser

GitHubjschicht/logfileparser

Parser for $LogFile on NTFS
binary-analysisdata-recoverydigital-forensics+3
2183 months ago
dwipe preview

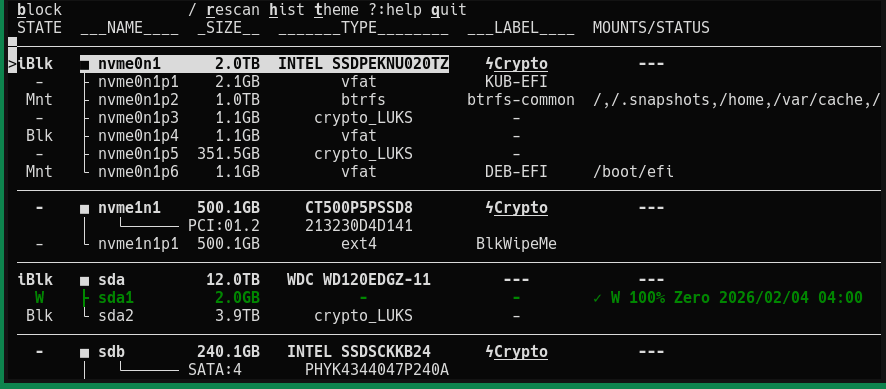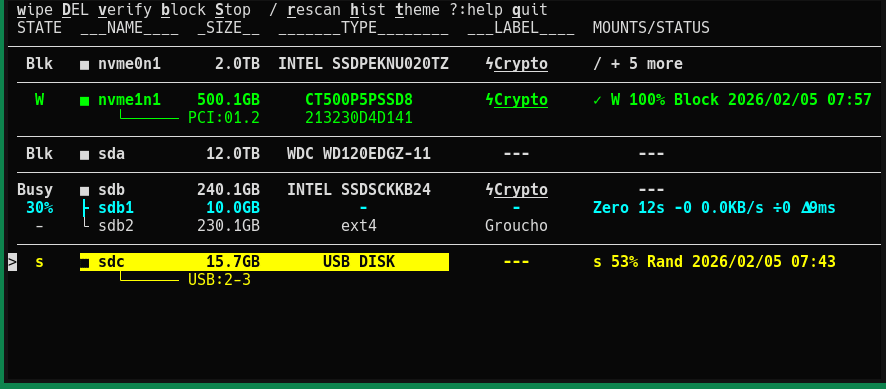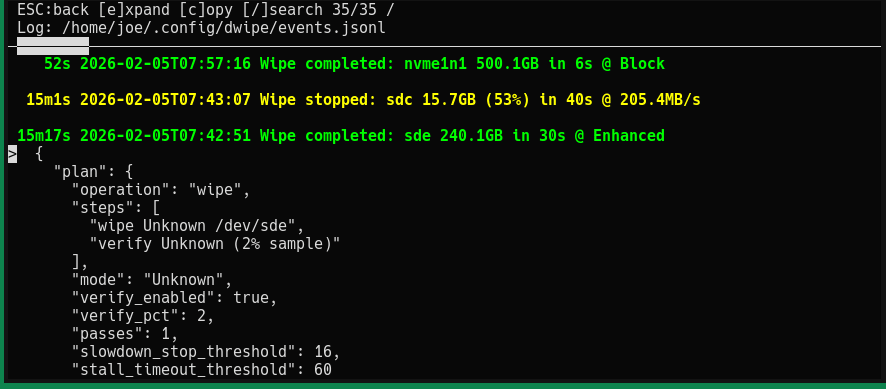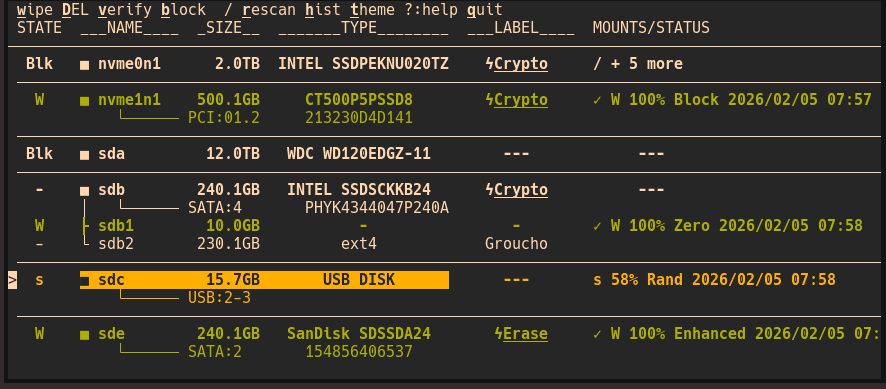
dwipe

GitHubjoedefen/dwipe

Tool to securely and efficiently wipe devices and partiitions for Linux
data-recoveryencryption-decryption-toolsforensics+3
1647 months ago
tscopy preview

tscopy

GitHubtrustedsec/tscopy

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

data-recoverydigital-forensicsdisk-forensics+2
1034 years ago
Centry preview

Centry

GitHub0xpoly/centry

Panic button for protection against cold boot attacks
data-recoverydefensive-toolsencryption-decryption-tools+3
1464 years ago
ParanoiDF preview

ParanoiDF

GitHubpatrickdw123/paranoidf

ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…

data-recoverydigital-forensicsencryption-decryption-tools+6
1123 years ago
Previous123…9Next