
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
149 results
Zydra preview

Zydra

GitHubhameda2/zydra

Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
data-recoverypassword-attackspassword-cracking
4346 years ago
usbsas preview

usbsas

GitHubcea-sec/usbsas

Tool and framework for securely reading untrusted USB mass storage devices.
data-recoverydefensive-toolsdigital-forensics+1
3773 days ago
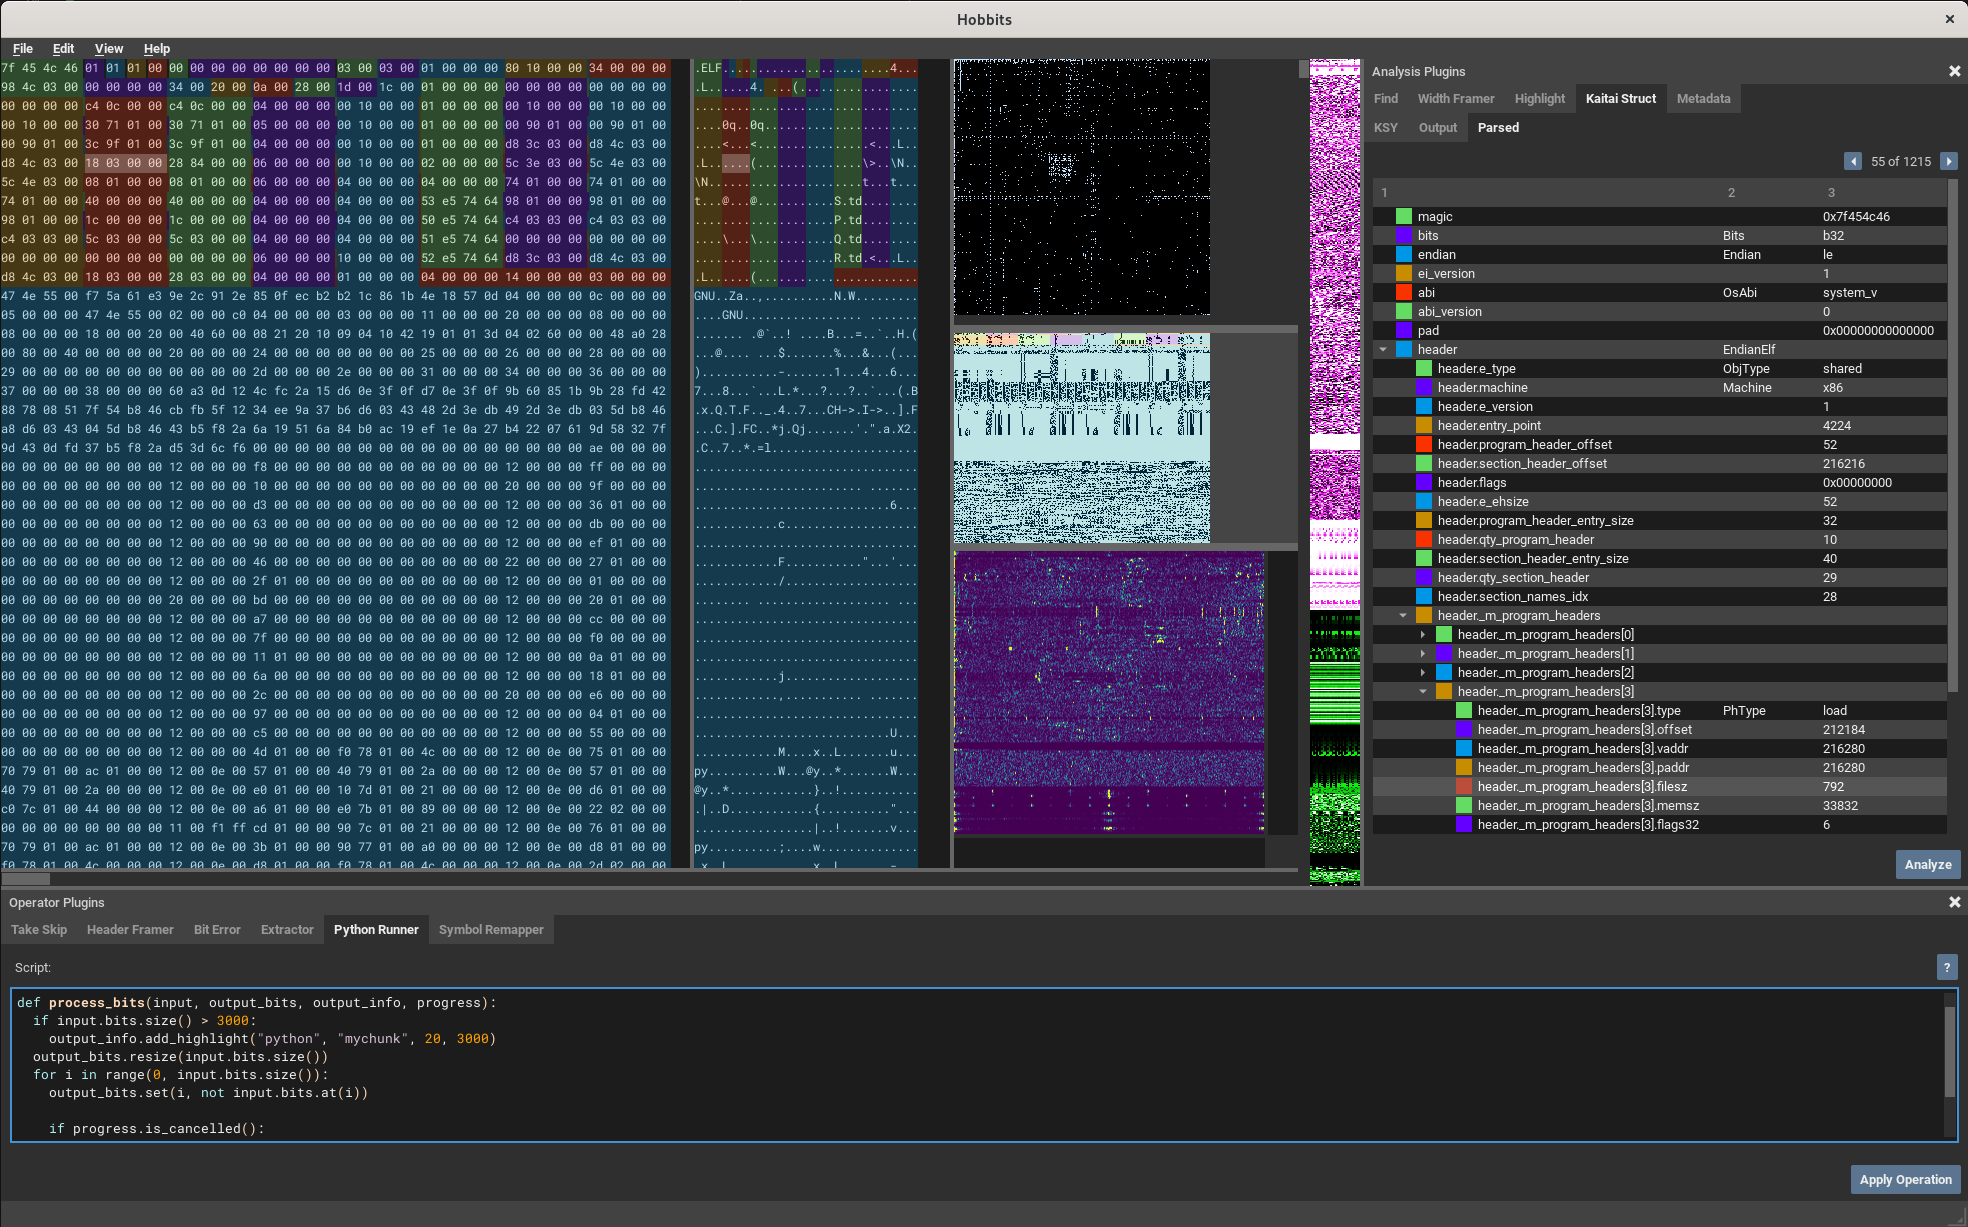
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

A multi-platform GUI for bit-based analysis, processing, and visualization
binary-analysisdata-recoveryforensics+1
7541 year ago
filekey preview

filekey

GitHubrockwellshah/filekey

Offline, open-source web app for passkey-based file encryption and sharing. AES-256-GCM/HPKE, no cloud, no accounts; encrypt to recipients with…
authenticationcryptographydata-recovery+2
4821 month ago
DroneXtract preview

DroneXtract

GitHubang13t/dronextract

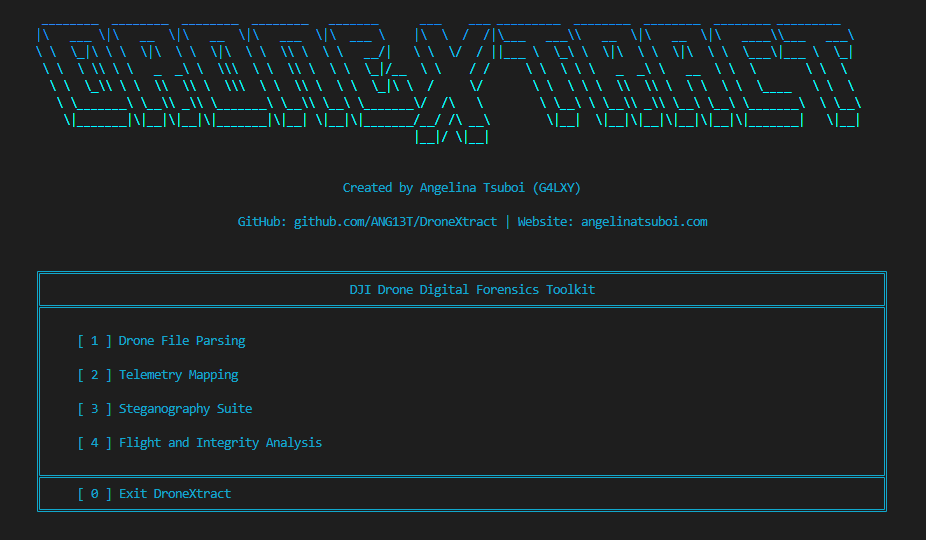
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
anomaly-detectiondata-recoverydigital-forensics+3
3693 years ago
RawCopy preview

RawCopy

GitHubjschicht/rawcopy

Commandline low level file extractor for NTFS
data-recoverydigital-forensicsdisk-forensics+1
3277 years ago
LogFileParser preview

LogFileParser

GitHubjschicht/logfileparser

Parser for $LogFile on NTFS
binary-analysisdata-recoverydigital-forensics+3
2204 months ago
tscopy preview

tscopy

GitHubtrustedsec/tscopy

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
data-recoverydigital-forensicsdisk-forensics+2
1034 years ago
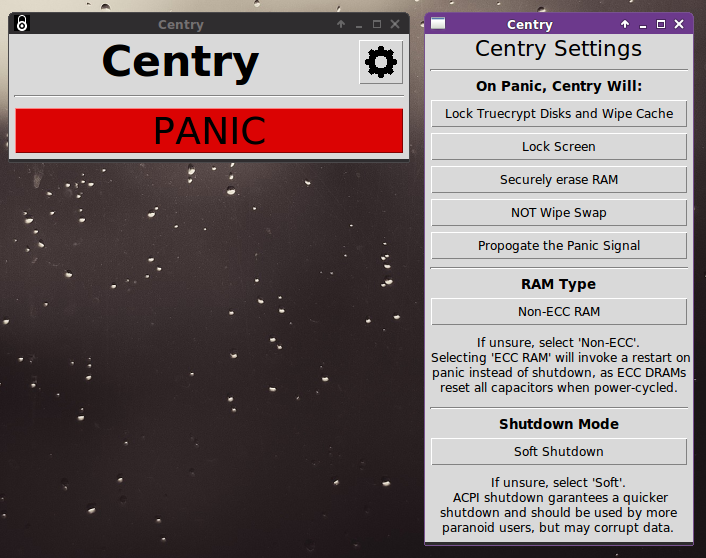
Centry preview

Centry

GitHub0xpoly/centry

Panic button for protection against cold boot attacks
data-recoverydefensive-toolsencryption-decryption-tools+3
1464 years ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1331 month ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
data-recoverydigital-forensicsexploitation+3
1042 months ago
interrogate preview

interrogate

GitHubcarmaa/interrogate

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
binary-analysiscryptographydata-recovery+4
787 years ago
CVE-2023-21036 preview

CVE-2023-21036

GitHubinfobyte/cve-2023-21036

Detection and sanitization for Acropalypse Now - CVE-2023-21036
data-recoverydigital-forensicsencryption-decryption-tools+3
803 years ago
mboxshell preview

mboxshell

GitHubdcarrero/mboxshell

mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
data-recoverydigital-forensicsemail-security+4
465 days ago
extundelete preview

extundelete

GitHubcherojeong/extundelete

Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…
data-recoverydigital-forensicsdisk-forensics
5410 years ago
dumper preview

dumper

GitHubelkirrs/dumper

CLI utility for creating encrypted database backups (PostgreSQL, MySQL, MongoDB) with support for multiple storage backends (SFTP, S3, Azure), SSH…
cloud-securitydata-recoveryencryption-decryption-tools+2
877 months ago
010-Editor-Template preview

010-Editor-Template

GitHubjas502n/010-editor-template

Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
binary-analysisdata-recoverydigital-forensics+4
445 years ago
Untrue preview

Untrue

GitHubnccgroup/untrue

Tool for checking passwords against TrueCrypt encrypted volumes and disks, and/or decrypting the data.

cryptographydata-recoverydigital-forensics+2
429 years ago
Previous123…9Next