
yellowkey-bitlocker
 desireeontrial76/yellowkey-bitlocker
Manage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.
data-recoveryeducationencryption-decryption-tools+2
desireeontrial76/yellowkey-bitlockerManage and recover BitLocker encrypted drives with this tool for Windows 11 recovery key management and educational study of CVE-2026-45585.

 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 libyal/libfwsi
Library to access the Windows Shell Item format
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 byte271/6cy
High-performance, streaming-first container format with per-block codec polymorphism and robust data recoverability. Reference implementation in Rust.
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
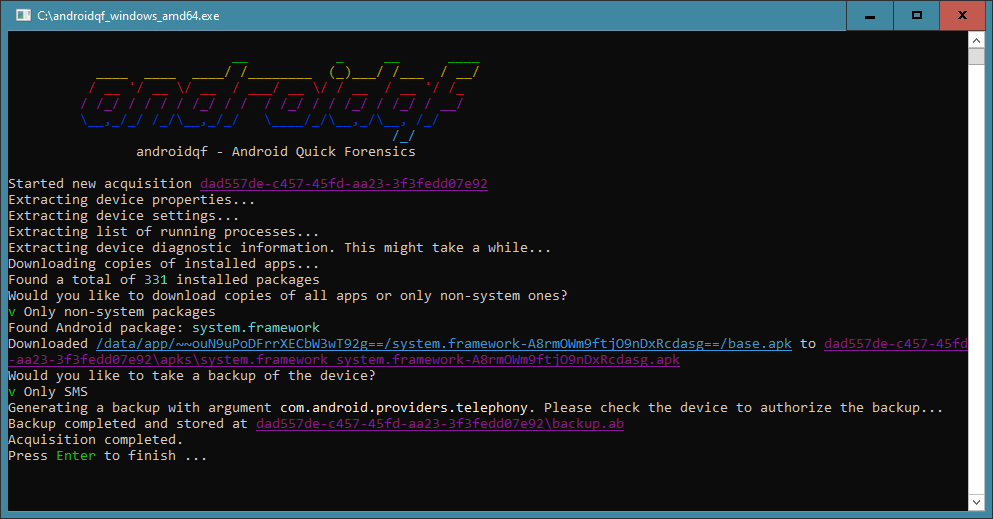 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.