nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.

Extract files from any kind of container formats

Steganographic storage & File encryption tool

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…

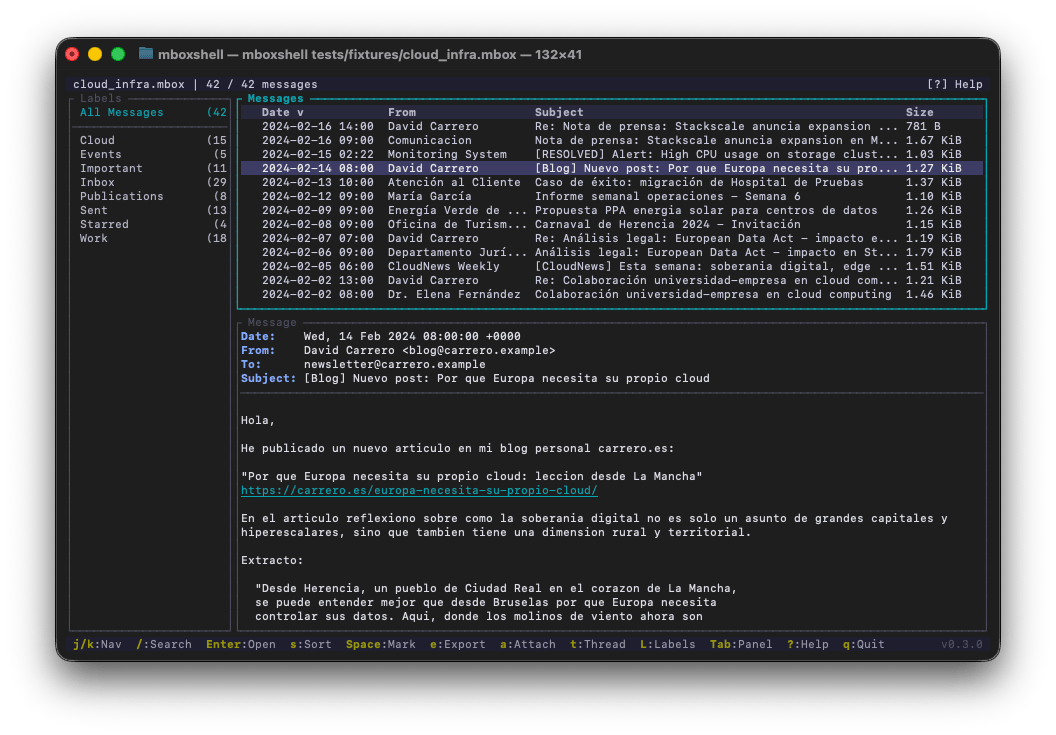
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

A tool for forensic file system reconstruction.

Offline, open-source web app for passkey-based file encryption and sharing. AES-256-GCM/HPKE, no cloud, no accounts; encrypt to recipients with…

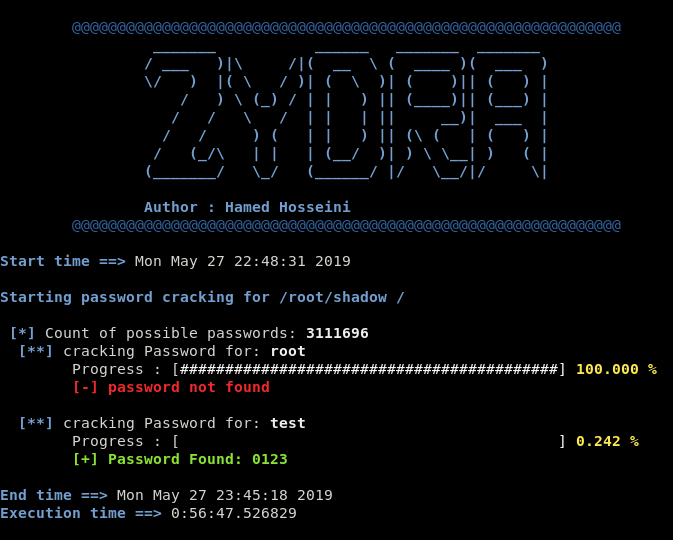
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…

Utility for recovering ES File Explorer encrypted files (.eslock)


F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files