StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.

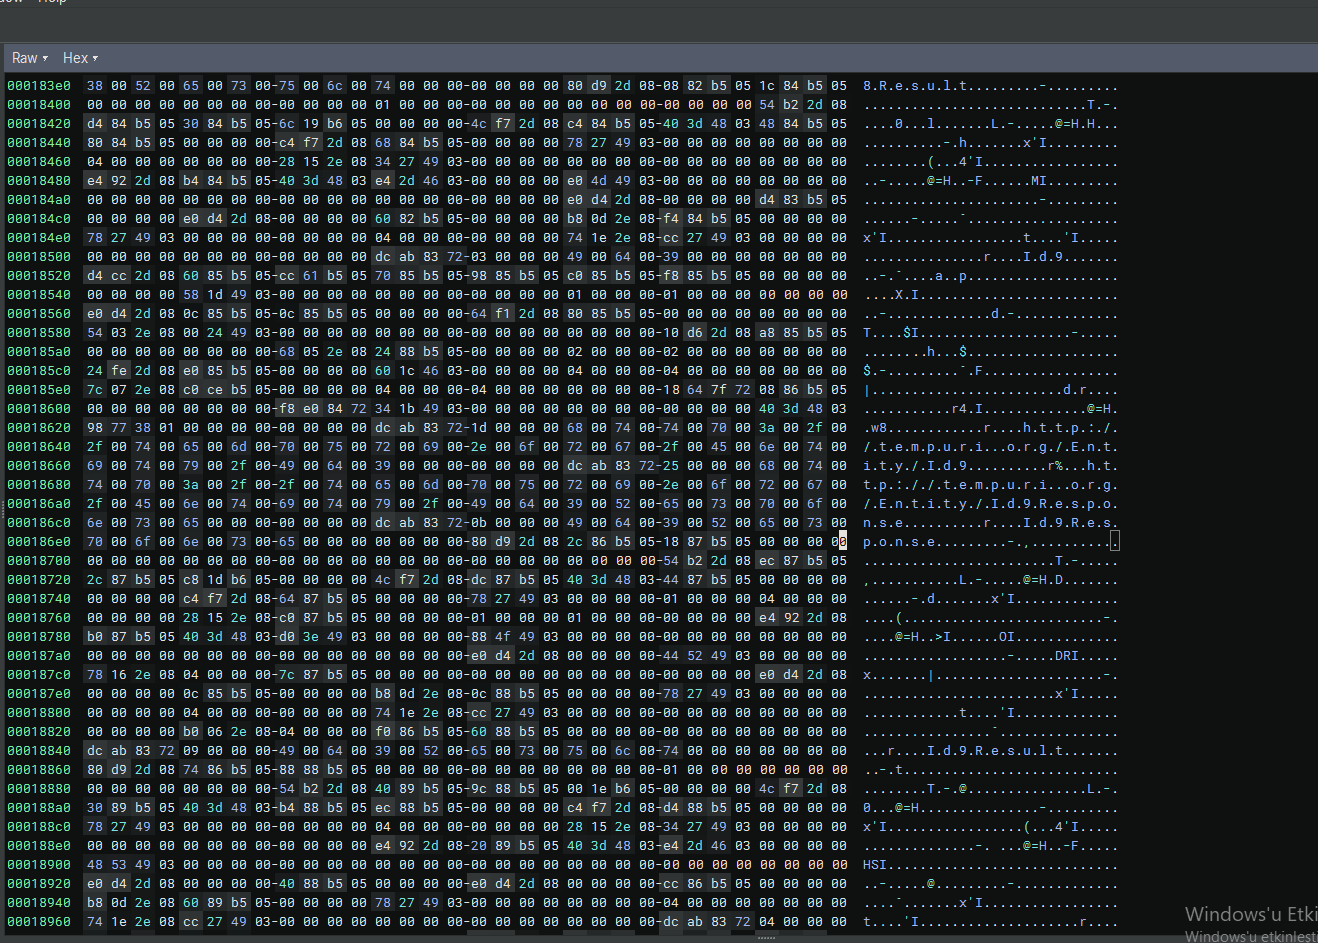
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

MxChat – AI Chatbot for WordPress <= 2.5.1 - Unauthenticated Information Exposure

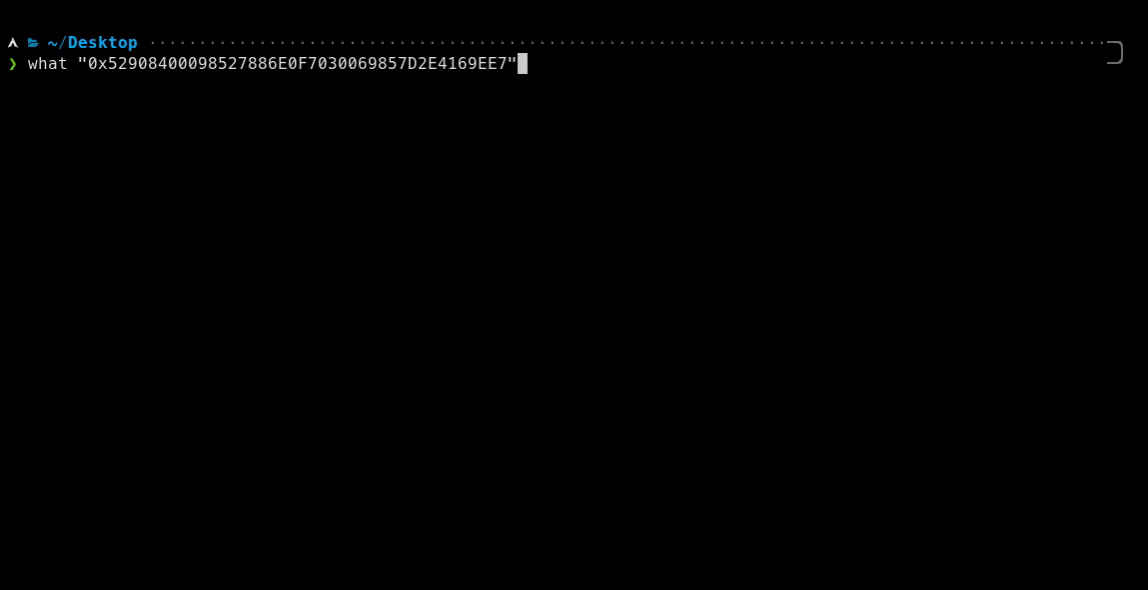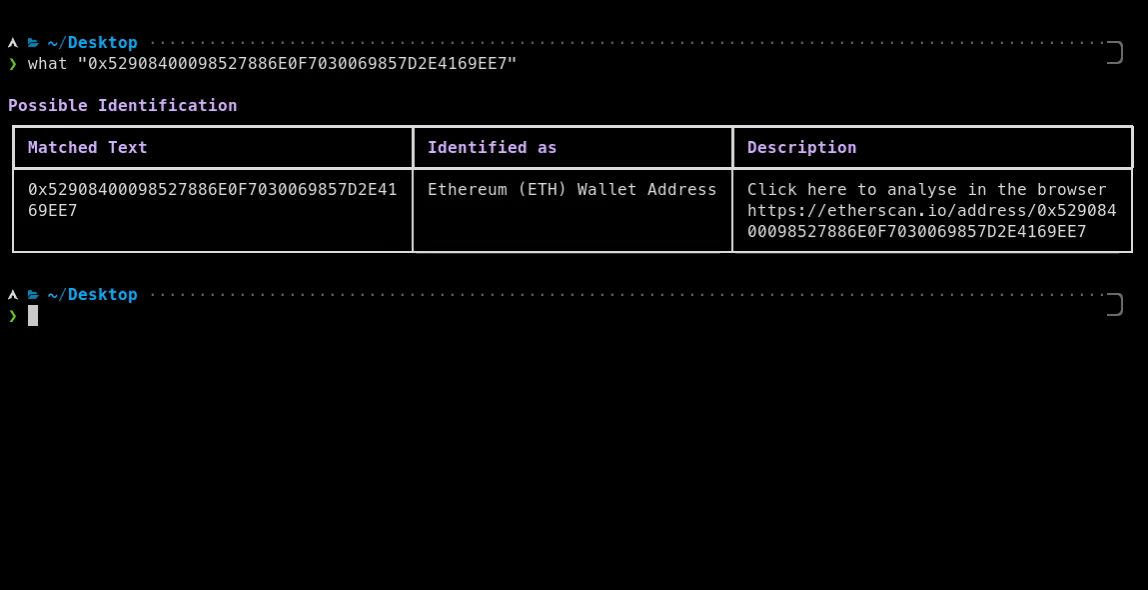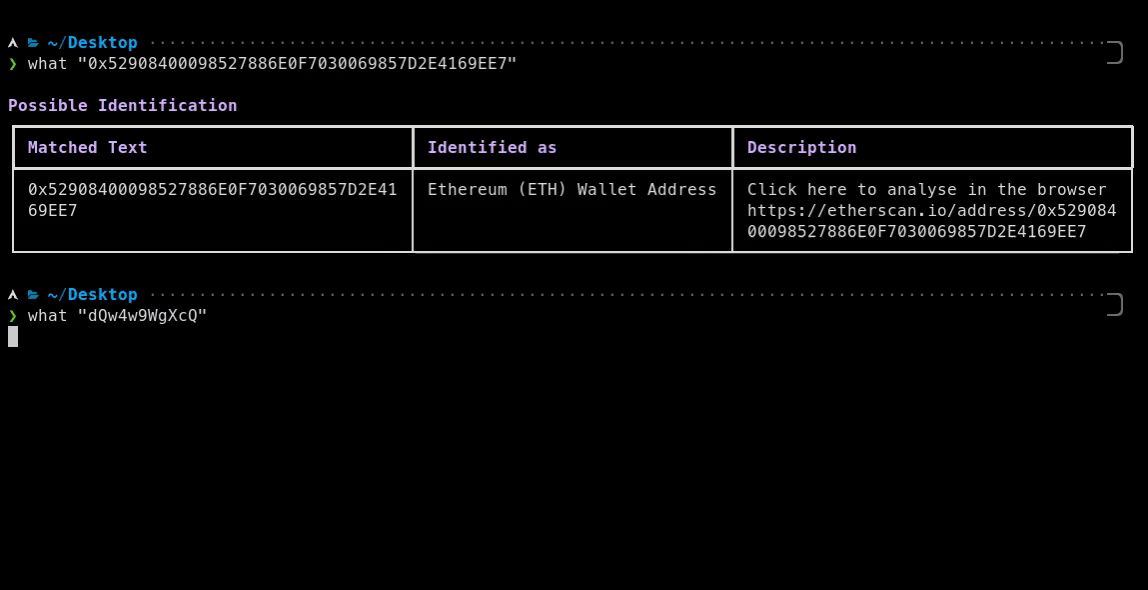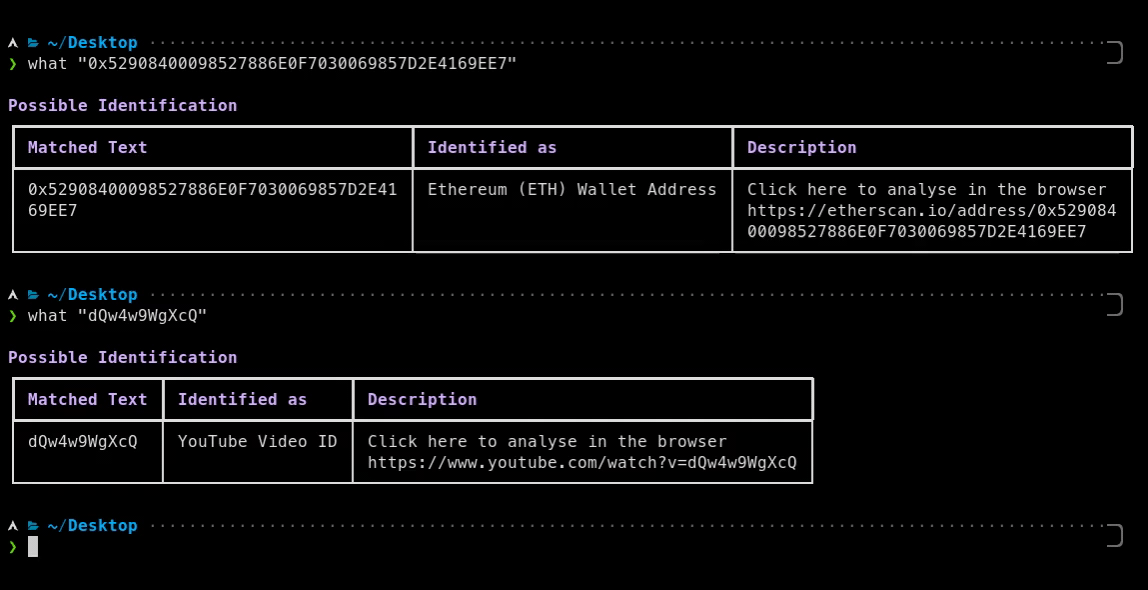
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…

[unmaintained] Post-exploitation tool

Code developed to steal certain browser config files (history, preferences, etc)