
memscan
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
data-exfiltrationfuzzinginformation-gathering+5
1285 years ago
nccgroup/memscanSearches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
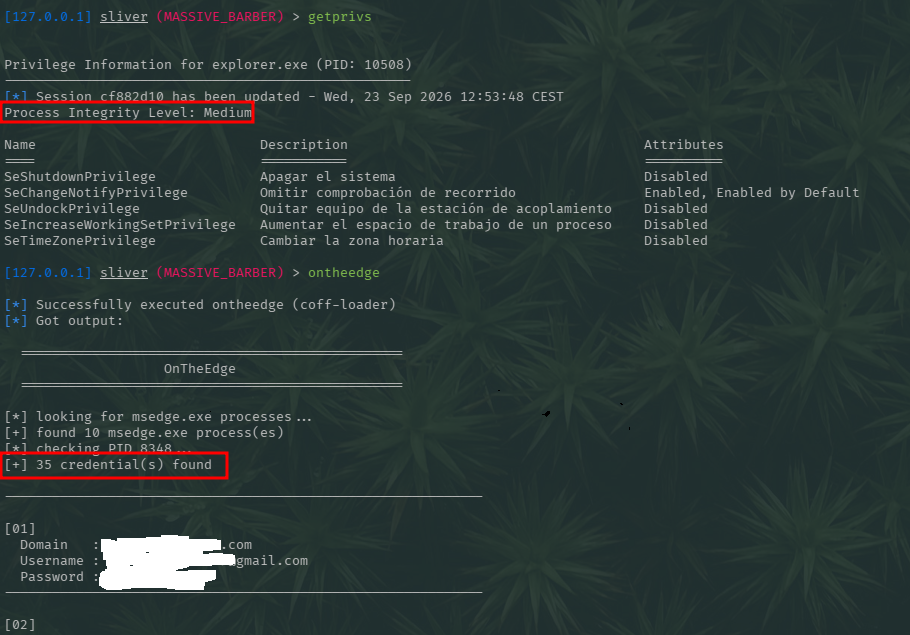 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
 kudaes/dumpy
Reuse open handles to dynamically dump LSASS.
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
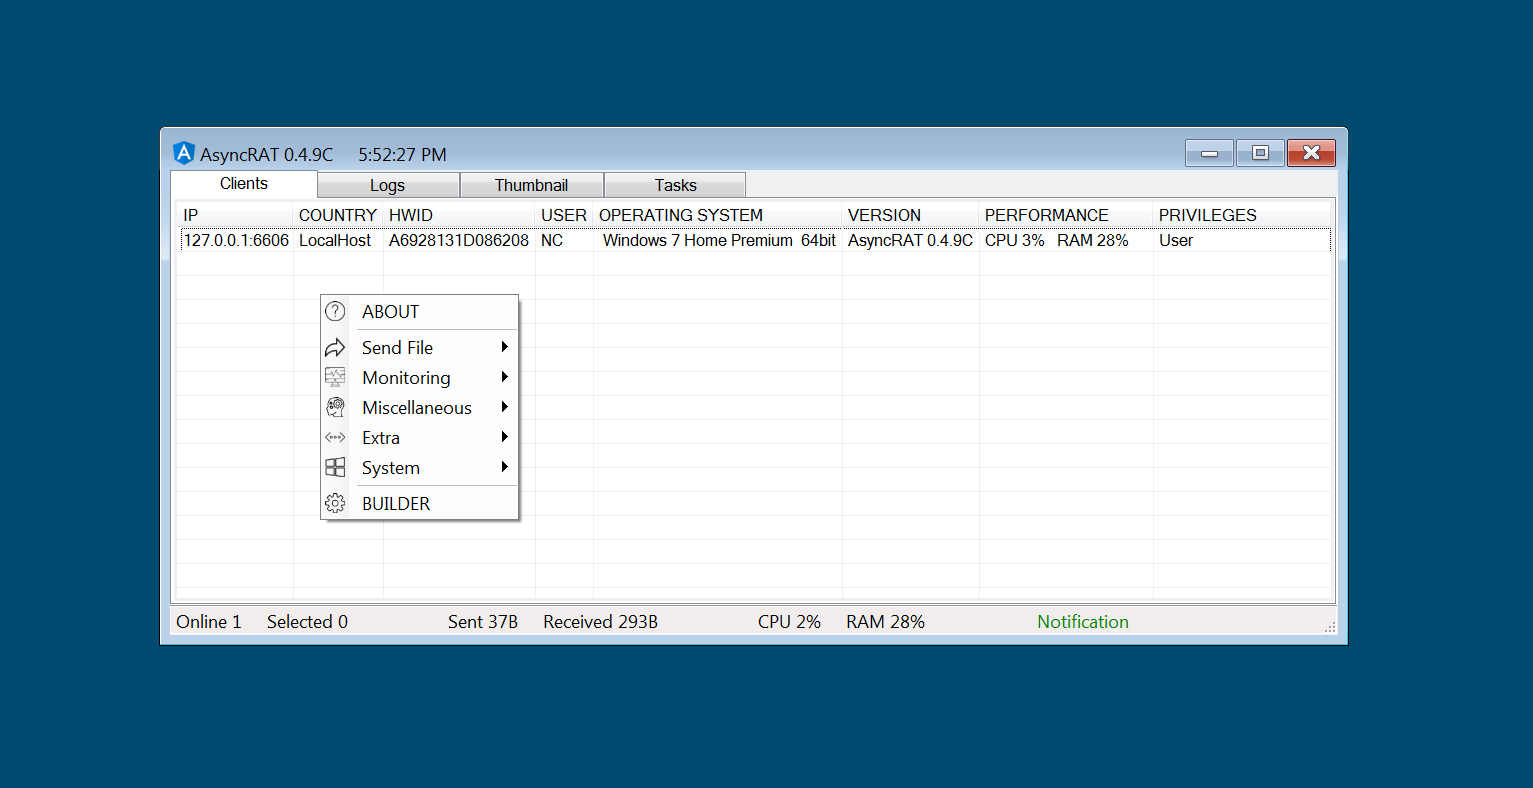 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 nathunandwani/cve-2020-24227
Playground Sessions - Storing User Credentials in Plaintext
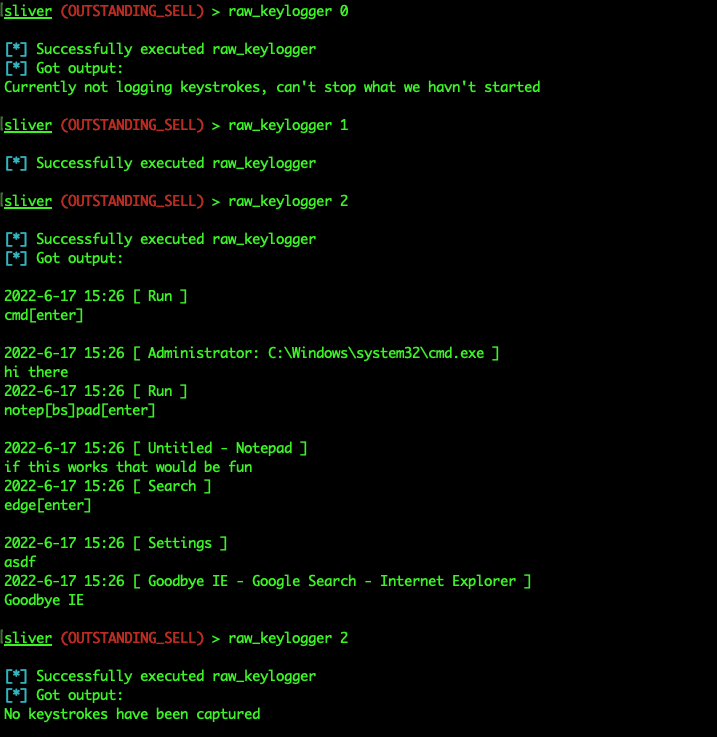 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…