kyocera-cve-2022-1026

An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords

An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords

a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…

CVE-2024-30056 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability

Android Data Stealing Vulnerability

CosmicSting: critical unauthenticated XXE vulnerability in Adobe Commerce and Magento (CVE-2024-34102)

Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…

Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…

Exploiting Android Vulnerability in ES File Explorer

Zero-day Vulnerability in ZKTEco biometric fingerprint reader.

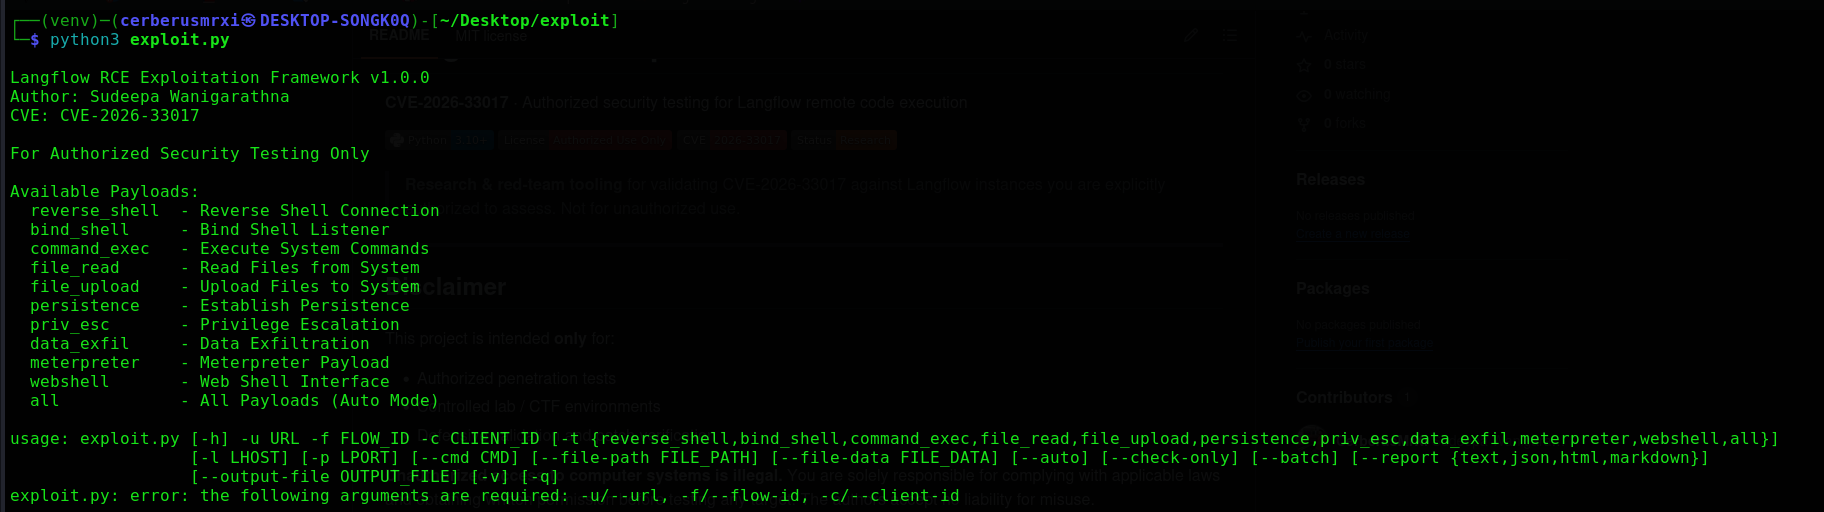
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…

CVE-2024-52317 - Apache Tomcat HTTP/2 Data Leakage Vulnerability

This script exploits a stored XSS vulnerability (CVE-2024-42009) in Roundcube Webmail version 1.6.7. It injects a malicious payload into the webmail…

Python implementation/PoC for CVE-2024-40422. Exploits a critical directory traversal vulnerability in Devika v1's /api/get-browser-snapshot endpoint…

PoC for CVE-2009-0229 "Print Spooler Read File Vulnerability" LPE AFR (related to CVE-2020-1048)

Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.

Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…

**CVE-2024-28987** is a critical vulnerability in SolarWinds Web Help Desk (WHD) that allows remote attackers to access sensitive ticket information…

Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7