
cve_2024_0044
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
android-securitydata-exfiltrationexploitation+5
1
hunter24x24/cve_2024_0044CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
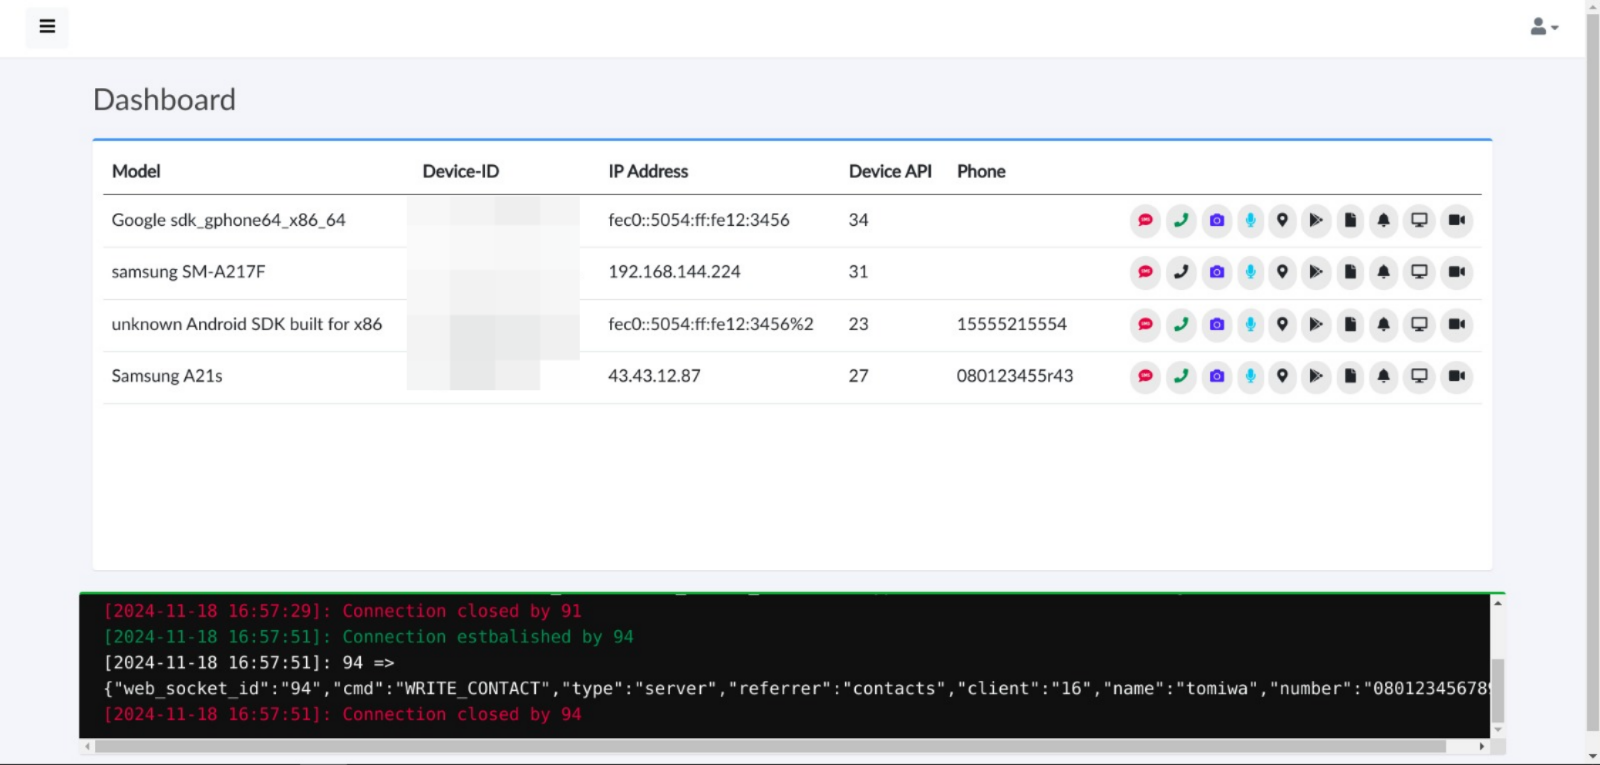 tomiwa-ot/moukthar
Android remote administration tool
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 007criptografia/c-cve-2024-0044
CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
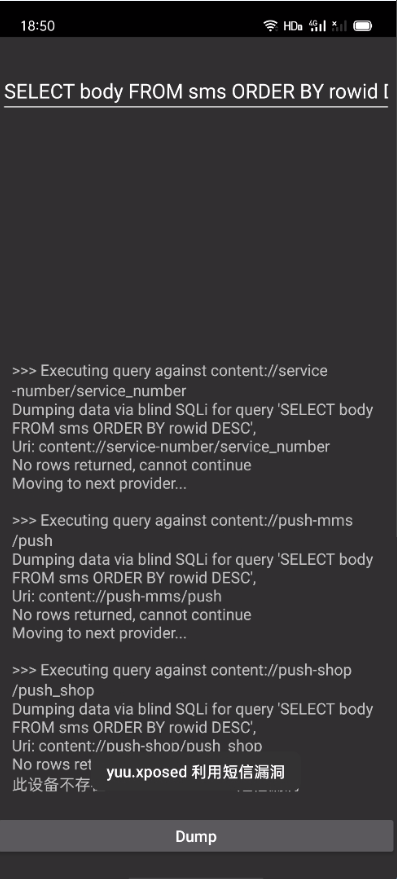 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
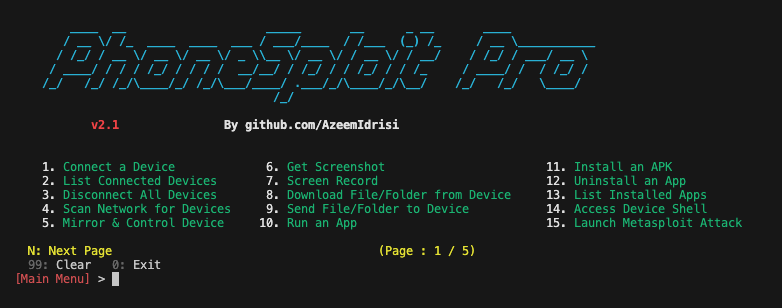 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
 mwsrc/betterandrorat
Android Remote Access Trojan
 huntoai/rdroid
[Android RAT] Remotely manage your android phone using PHP Interface
 ibrahimbalic/androidrat
Android RAT
 princessauroraj/chinese-cybercrime-research
Resources to learn more about Chinese-language cybercrime actors.
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.