

jupyter-notebooks
 vulncheck-oss/jupyter-notebooks
Example Jupyter notebooks that query VulnCheck APIs to chart exploitation timelines, Known Exploited Vulnerabilities, and botnet data for threat…
data-exfiltrationeducationexploitation+5
9
vulncheck-oss/jupyter-notebooksExample Jupyter notebooks that query VulnCheck APIs to chart exploitation timelines, Known Exploited Vulnerabilities, and botnet data for threat…
 qmf0c3uk/cve-2020-17518
Python exploit for CVE-2020-17518, allowing arbitrary file write via Apache Flink REST API. Supports single target and batch scanning from a file.
 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 hackzuoji/freeswitch-cve-2026-116779-poc
Detection and exploitation toolkit for the FreeSWITCH SIP MESSAGE command injection (CVE-2026-116779), with API execution, DNS OAST shell output,…
 jakabakos/cve-2024-34102-cosmicsting-xxe-in-adobe-commerce-and-magento
CosmicSting: critical unauthenticated XXE vulnerability in Adobe Commerce and Magento (CVE-2024-34102)
 datxzzz/cve-2026-93300
Python proof-of-concept for CVE-2026-93300, an unauthenticated SQL injection in the EventON Subscriber WordPress plugin; fingerprints the AJAX…
 0ggp4r1s/osint-pattern-analyzer
Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.
 agathanon/cve-2022-44268
Payload generator and extractor for CVE-2022-44268 written in Python.
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
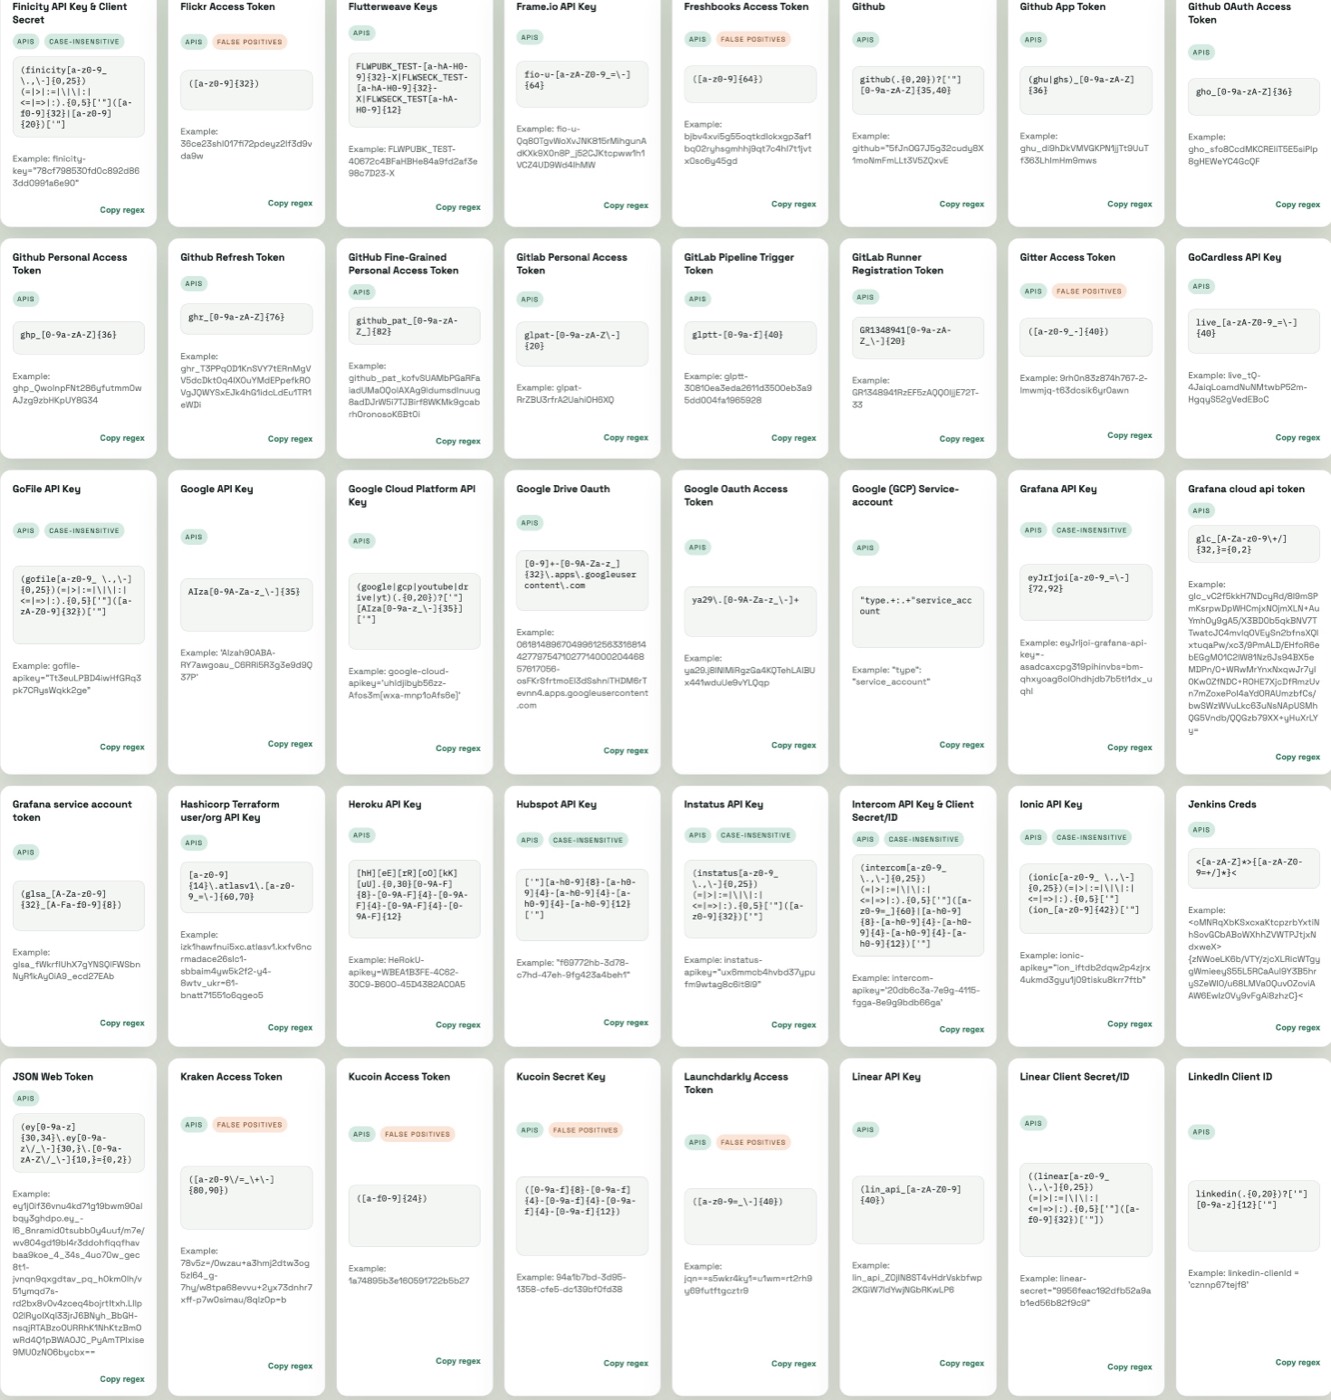 adversis/screenscrub
Find credentials in screenshots, save them to your secret manager, and irreversibly redact them from the image — local, offline, OCR-based.
 numanturle/cve-2025-25279
Proof-of-concept for CVE-2025-25279: path traversal in Mattermost Boards allows arbitrary file read via crafted import archive and board duplication.
 bitcoindatalabs/ln-upgrade-dynamics
Code, aggregate data and LaTeX source for 'Who Patches the Lightning Network? Evidence from Release Lines in Gossip, 2023-2026' (arXiv:2610.30350)
 emrekybs/tgsherlock
Telegram OSINT tool for user, group and message investigation
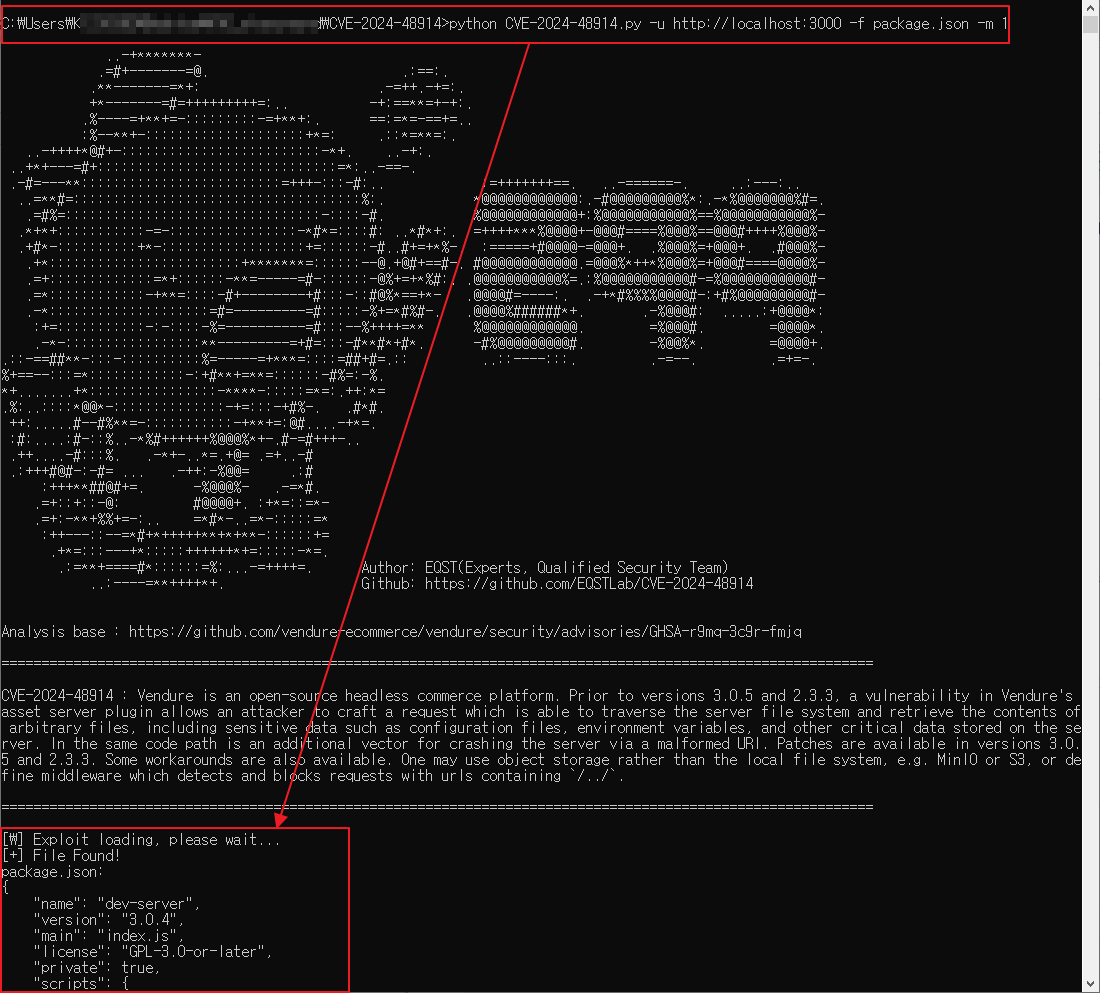 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
 l0lsec/cve-2021-26837
CVE-2021-26837 - SQL Injection in the SearchTextbox parameter of HelpSystems/Fortra DeliverNow. Payloads, annotated requests, and evidence. Fixed in…