

secret_handshake
 jconwell/secret_handshake
A prototype malware C2 channel using x509 certificates over mTLS
command-and-controldata-exfiltrationids-ips-evasion+1
153
jconwell/secret_handshakeA prototype malware C2 channel using x509 certificates over mTLS
 ariary/queensono
Golang binary for data exfiltration with ICMP protocol (+ ICMP bindshell, http over ICMP tunneling, ...)
 rwhitcroft/dnschan
A remote access trojan over DNS
 nccgroup/onelogicalmyth_shell
A HTA shell to assist with breakout assessments.
 d4vinci/wormy
some python3 functions to add spreading features to any python backdoor
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
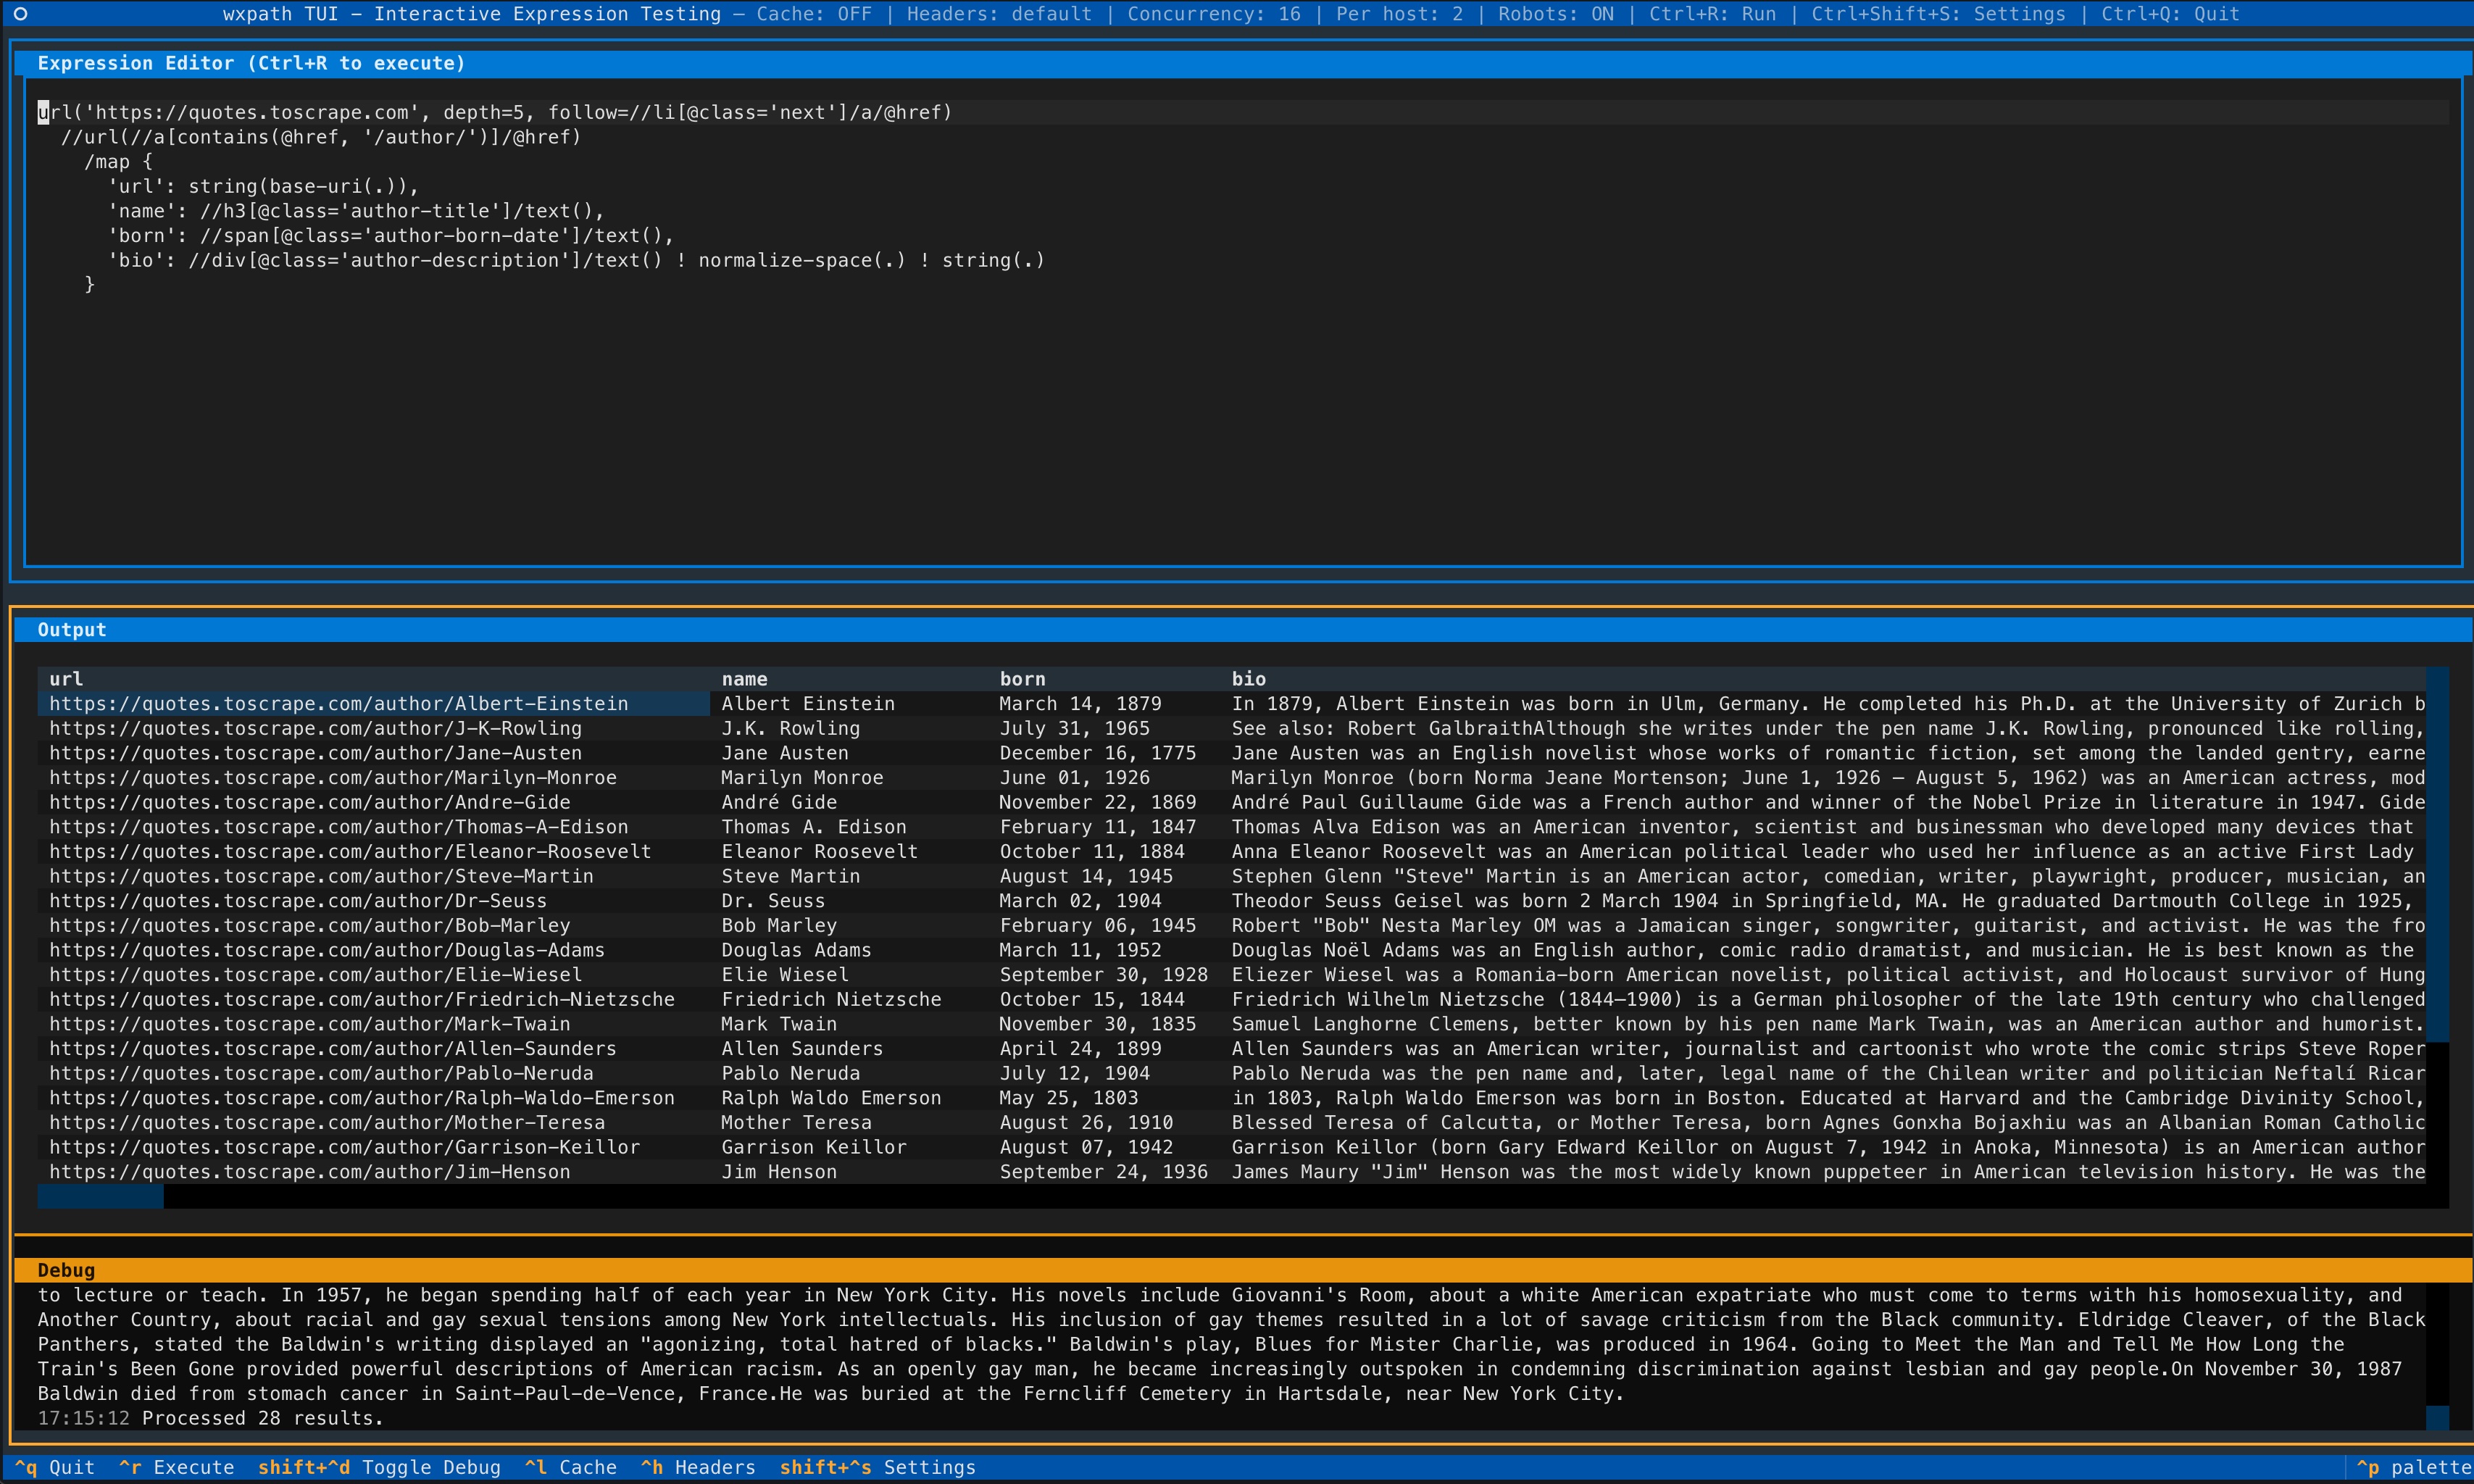 rodricios/wxpath
wxpath - declarative web crawling with XPath; a Web Query Language (WQL)
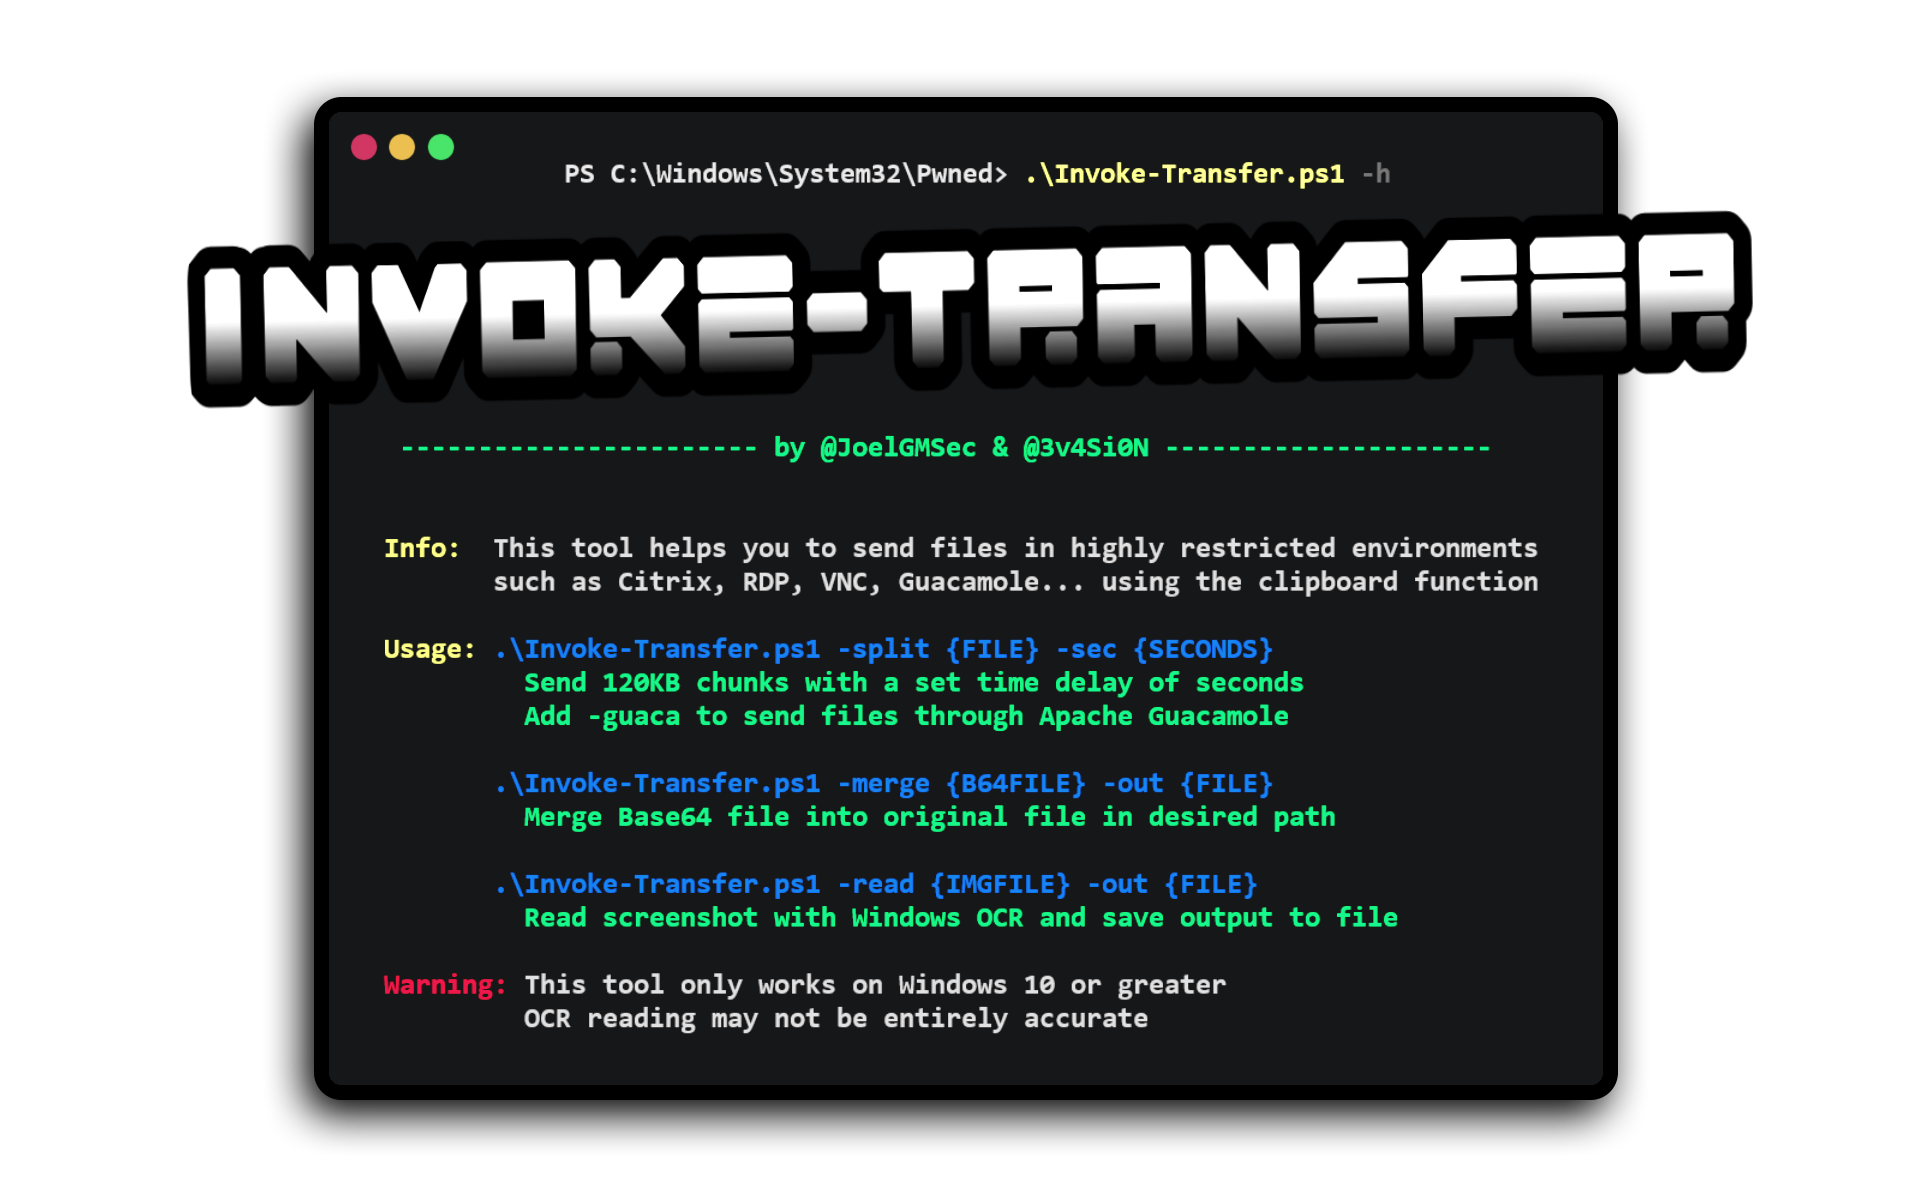 joelgmsec/invoke-transfer
PowerShell tool for transferring files in restricted environments (Citrix, RDP, VNC, Guacamole) via clipboard, Base64 chunks, keystrokes, or OCR…
 mwsrc/betterrat
Better Remote Access Trojan

 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 yschgroup/skyrat
SkyRAT - Powershell Remote Administration Tool
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 mwsrc/schwarze-sonne-rat
SS-RAT (Schwarze-Sonne-Remote-Access-Trojan)
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 shieldersec/cve-2020-11579
Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB