
react-cve-2025-55182
 stonelinks/react-cve-2025-55182
Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
command-and-controldata-exfiltrationforensics+6
stonelinks/react-cve-2025-55182Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
 zakaria-laouani/cve-2023-0669-simulation
Simulation environment for CVE-2023-0669 with Docker-based attacker, vulnerable server, and listener containers. Demonstrates deserialization exploit…
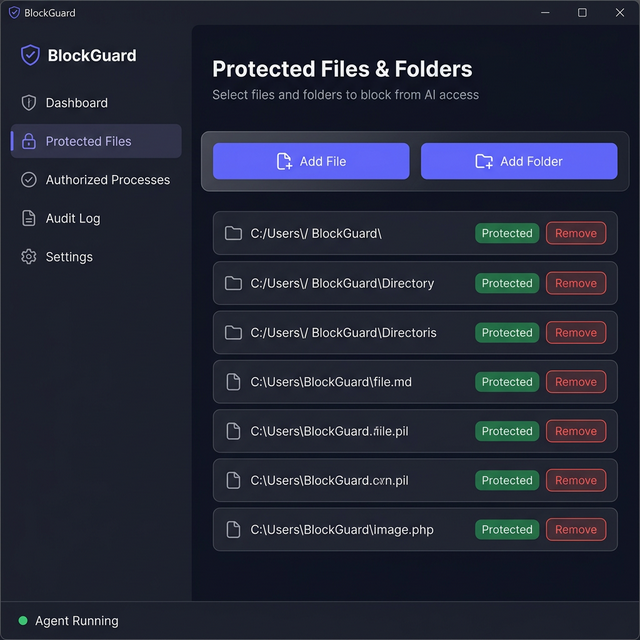 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
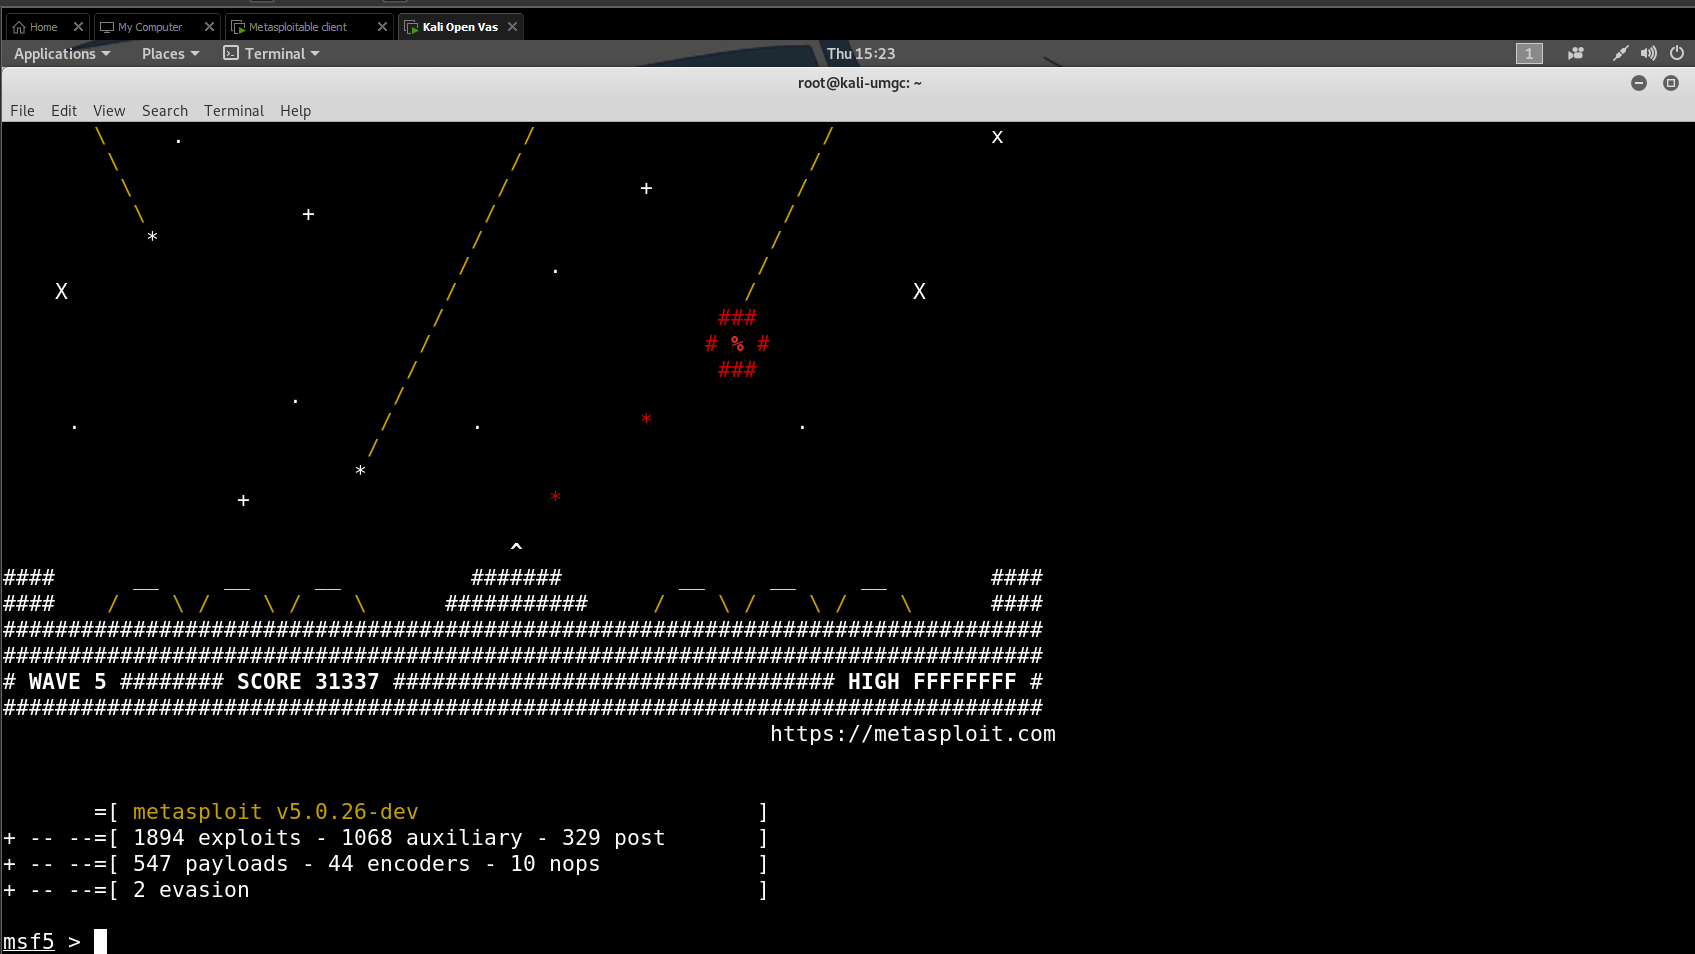 devinliggins14/smb-pentest-exploiting-cve-2007-2447-on-metasploitable-2
Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential…
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 h3x0v3rl0rd/cve-2019-6447
Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
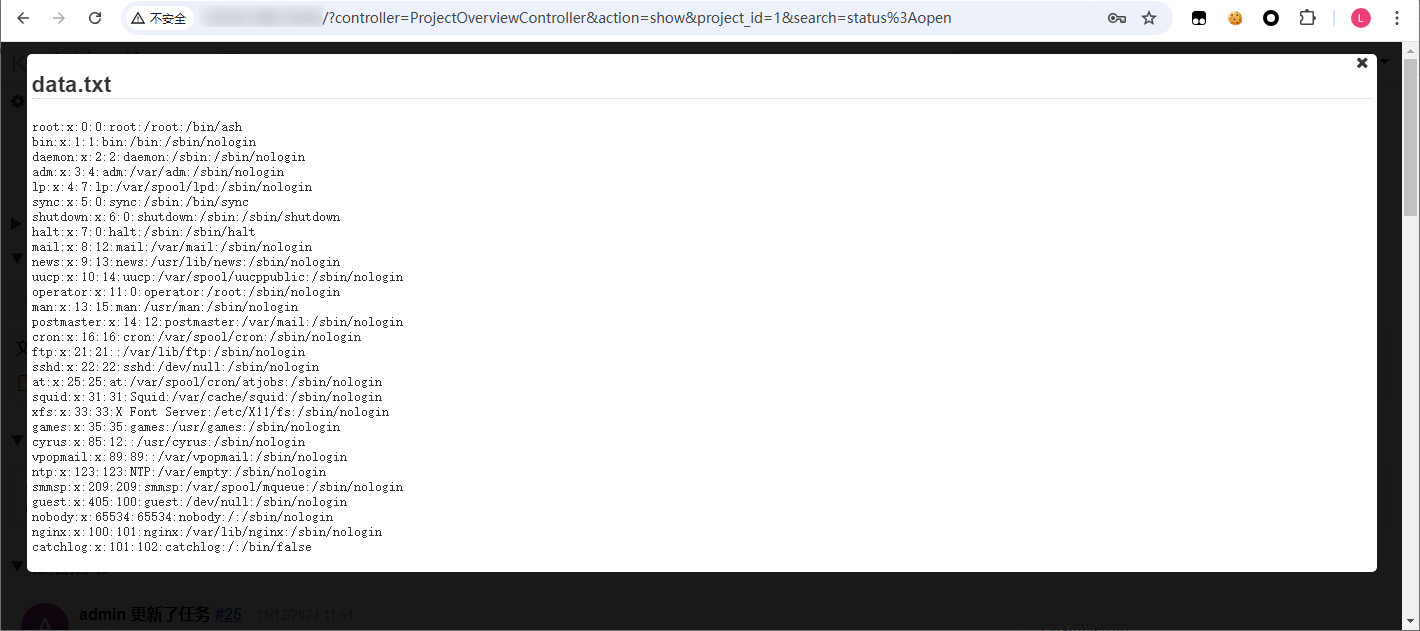 l20170217b/cve-2024-51747
Proof-of-concept exploit for CVE-2024-51747 enabling authenticated file read and deletion via SQLite database manipulation in a web application's…
 mksundaram69/cve-2024-34102
Proof-of-concept exploit for CVE-2024-34102, a critical XML entity injection in Magento, enabling exfiltration of sensitive files and unauthorized…
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 sromanhu/totalcms-arbitrary_file-upload--xss_steal_cookies---totaldepot
TotalCMS is affected by Arbitrary File Upload - XSS vulnerability which allows Cross-Site Scriting (XSS) Stored and also stealing session cookies
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…