metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…

A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

Paperweight scans your inbox to map your digital footprint, then helps you take back control and delete your data. Local-first and open source.

Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Python PoC exploiting CVE-2026-85706, an unauthenticated path traversal and arbitrary file read in GitLab CE/EE via the create-commit endpoint, with…

Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.

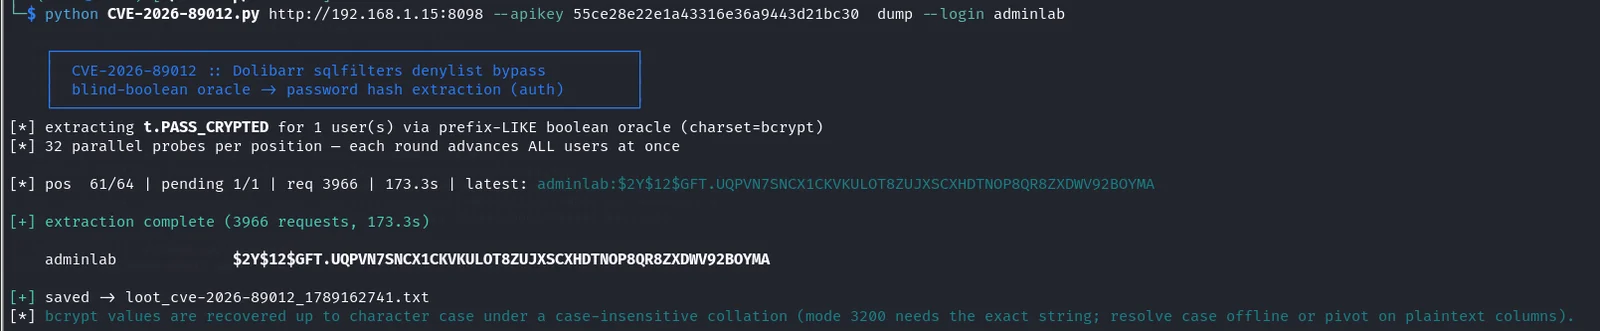
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read

Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Open-source IoT Platform - Device management, data collection, processing and visualization.

An all-in-one hacking tool to remotely take over Android devices.

Find and redact secrets in AI coding agent histories (Claude Code, and more).

USB Army Knife – the ultimate close access tool for penetration testers and red teamers.