
GraphSpy
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
authenticationcloud-securitydata-exfiltration+6
1.4k1 month ago
redbyte1337/graphspyInitial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 krishsharma0413/syncord
Syncord is a CLI-based file synchronization and storage tool that uses Discord as an encrypted file storage.
 infosecn1nja/veiltransfer
VeilTransfer is a data exfiltration utility designed to test and enhance the detection capabilities. This tool simulates real-world data exfiltration…
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
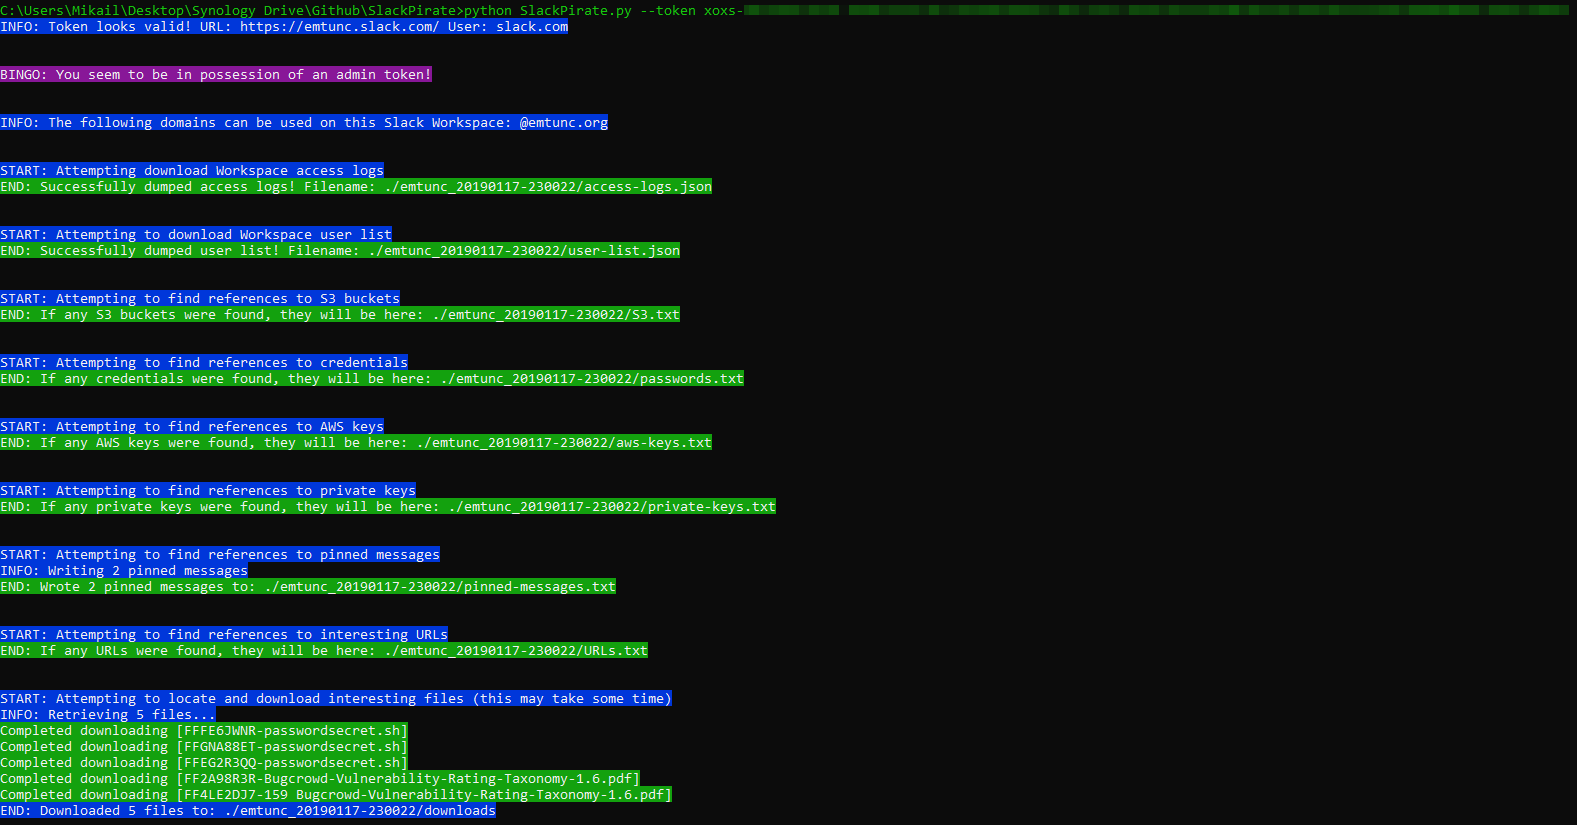 emtunc/slackpirate
Slack Enumeration and Extraction Tool - extract sensitive information from a Slack Workspace
 redsiege/egress-assess
Multi-protocol data exfiltration testing tool that simulates real-world egress scenarios over FTP, HTTP, HTTPS, DNS, ICMP, SMB, SMTP, and SFTP to…
 securing/dumpsterdiver
Tool to search secrets in various filetypes.
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 globalpolicy/phonemonitor
A Remote Administration Tool for Android devices
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 moloch--/leakdb
Web-Scale NoSQL Idempotent Cloud-Native Big-Data Serverless Plaintext Credential Search

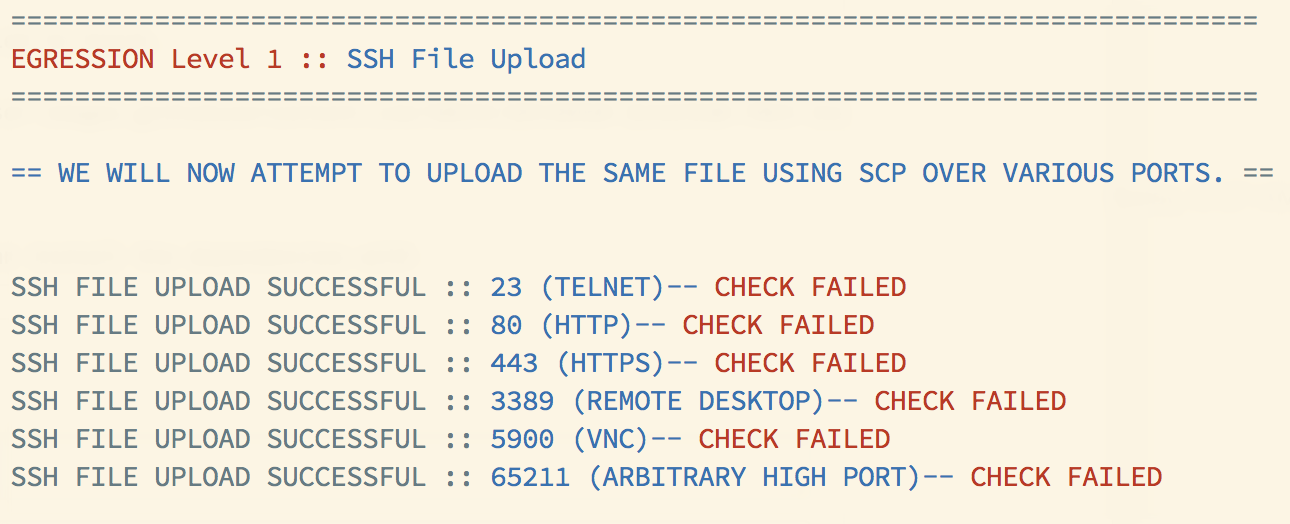 danielmiessler/egression
Test a network's egress controls with various levels of success and failure.
 designativedave/androrat
Remote Administration Tool for Android devices